We owe you an apology.
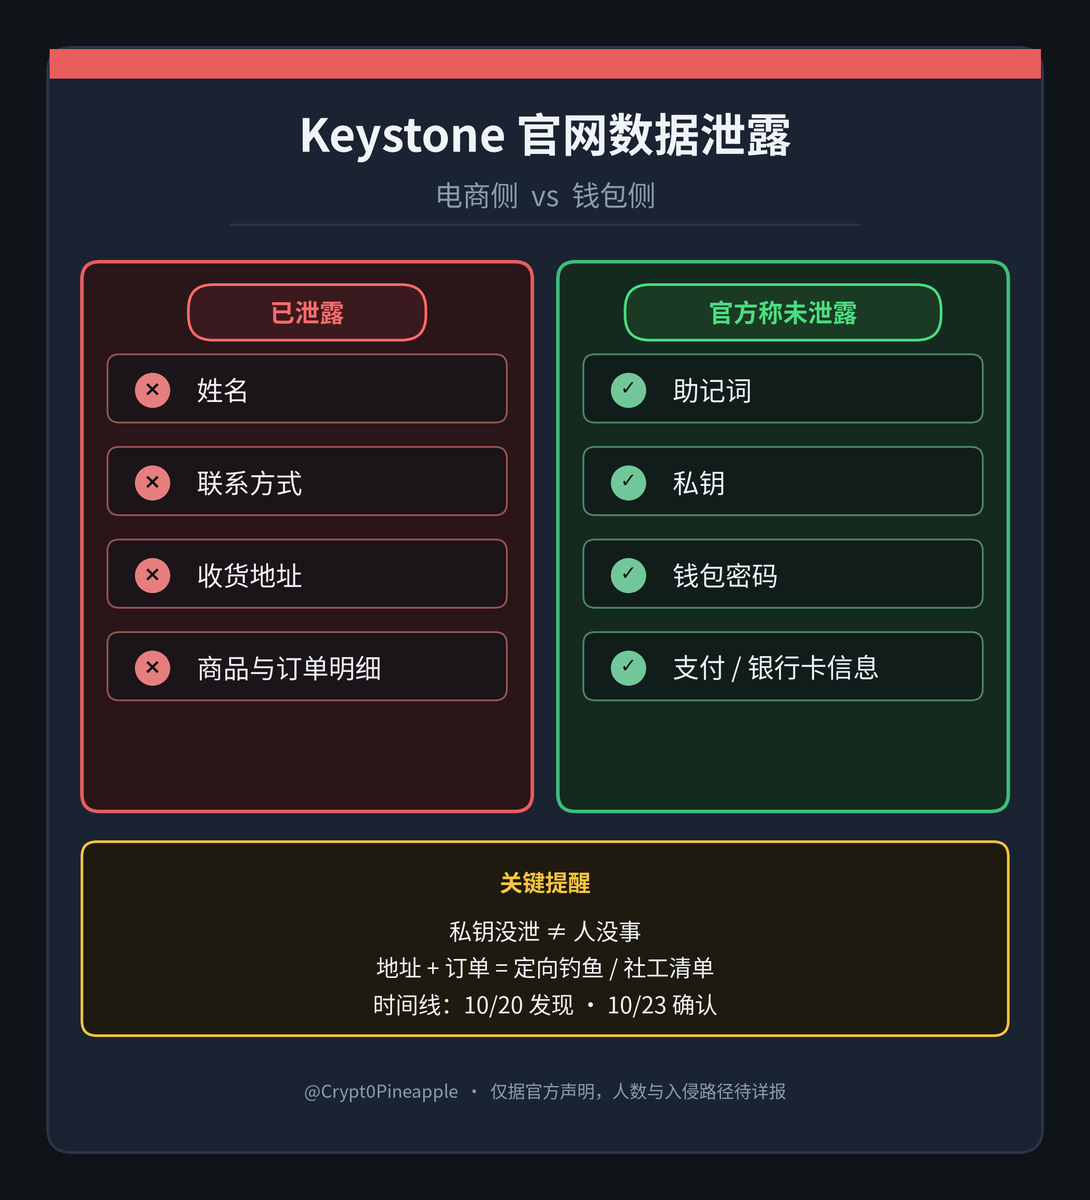
On October 20, we detected unauthorized access to our official website. After verifying API activity with Shopify, we confirmed on October 23 that a third party obtained customer shipping information. You trusted us with those details, and we're sorry we didn't keep them safe.
Exposed: names, contact details, shipping addresses, and order details (items and prices).
Not exposed: payment card or bank details, recovery phrases, private keys, or wallet passwords.
We've blocked access, fixed the vulnerability, opened an investigation, and are emailing affected customers.
Scammers may pose as Keystone by phone, text, email, or mail, offering refunds, replacement devices, or "fixes" for your order or address. None of it is from us.
NEVER share your recovery phrase or private keys, and NEVER enter your recovery phrase into a device you didn't order. We will never ask for them. Don't click links in unexpected messages. Type https://t.co/7km8AZM288 yourself.
A detailed report is coming soon.
Until then, trust only our official channels. If anything feels off, email [email protected]. We'd rather hear from you than have you take a chance.
Again, we're truly sorry to everyone affected.
As of Oct 23, 2026, 3:41:30 PM UTC, the Initia L1 and Rollups have been halted due to a security incident.
Our team is actively investigating the situation and working to establish the full scope of any impact with security teams, validators, and exchanges.
We will share verified information through our official channels as it becomes available.
Please remain cautious of unofficial links, messages, or claims circulating during this time.
‼️ BREAKING: Oracle Issues Emergency Java Update for Critical 9.1 HTTPS Trust Vulnerability
Details: https://t.co/XZV8KY0rPW
Oracle has released an emergency Java security update to address CVE-2026-91403, a critical vulnerability affecting how Java applications trust digital certificates. Published on October 21, 2026, the alert assigns the flaw a CVSS 3.1 score of 9.1 and covers Oracle Java SE and GraalVM.
The update blocks affected intermediate certificate authority certificates linked to eMudhra. According to Oracle’s security advisory, the issue affects the Java Secure Socket Extension, or JSSE, component.
Oracle rates exploitation as low complexity, with no authentication or user interaction required. Successful attacks can expose or change sensitive data, although the risk matrix lists no availability impact.
#cybersecuritynews #vulnerability
L’application de messagerie BitChat, chiffrée et indépendante du réseau mobile, est désormais numéro 1 sur l’App Store dans la catégorie « réseaux sociaux ».
Et dans le top 10 global.
Last month, we demonstrated high-rate alchemy: turning mercury into real, stable gold, beating CERN’s record by a factor of 10.
Last week, we enriched isotopes in the world’s most powerful plasma centrifuge, beating the Soviet record that stood for 40 years.
Now, we’re building a fusion reactor in San Francisco to achieve record power density.