@krishnsec@AnthropicAI Remove .cluade/* files/folders and start claude again it will start working again. (Make sure to copy your important files and paste again in .claude/ )
Me explaining why I rearchitected my RAG pipeline with hybrid dense sparse retrieval, a cross encoder reranker, and semantic chunking with recursive overlap to fix my context recall degradation
PRO TIP: Copy this article into Fable 5 and tell it...
"Read this article, review my current workflow, and tell me 5 things I can do to be more productive"
The best hackers I know aren't smarter than me.
They've just read more than me. Somewhere in their memory is the one obscure writeup that turns a dead end into a finding. Preview is that memory, on tap. For you, and for your agent.
-> https://t.co/JQKjIQGWFA
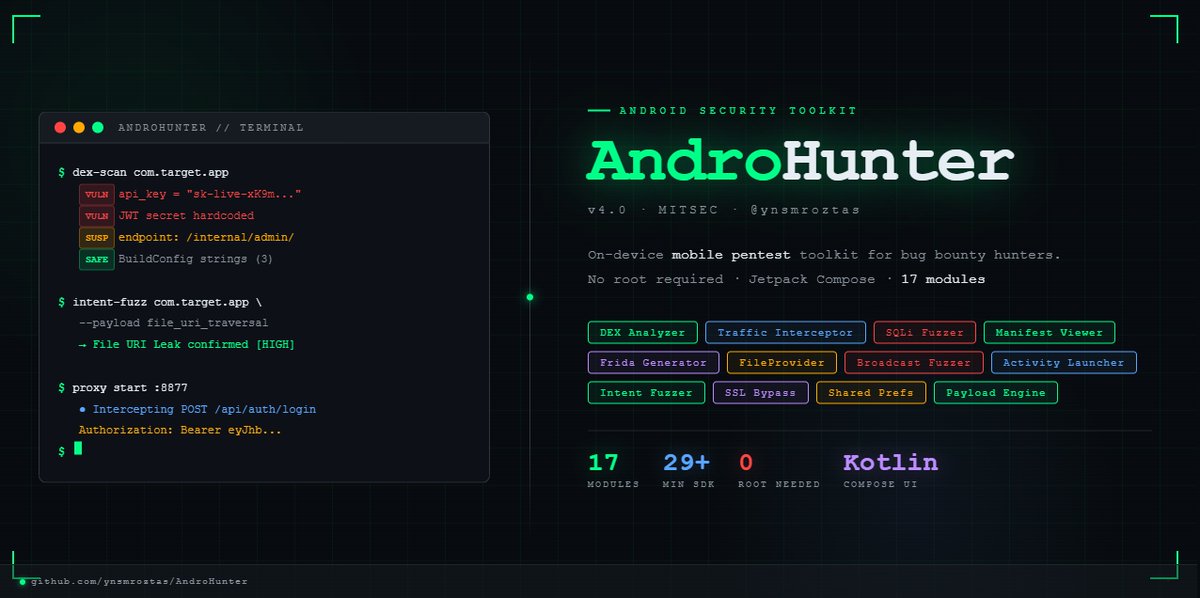
🚀 I'm releasing AndroHunter-v, my on-device Android security toolset developed for bug hunters.
17 modules. No root required. Works on Android 10+.
👉 https://t.co/saNETyZLaK
#bugbountytip#bugbountytips#infosec#recon#Android#PenTest
A new open-source project by @spaceraccoon monitors commit diffs and PR context in GitHub repos to find vulnerability patches before they're published into public CVEs.
For bug bounty hunters, this surfaces high-signal patch diffs where a real bug almost certainly existed. That makes it useful for finding variants and affected downstream projects before others do.
Repo 👇
https://t.co/OaWM4iJSBp
Site 👇
https://t.co/xlYBAuQrHg
#BugBounty
1 - Start by enumerating subdomains using any tool you like (subfinder or others) and save everything to domains.txt.
2 - Run dnsx on the list and see which subdomains actually resolve, and where they point.
3 - Use httpx to check which resolved hosts expose web services on common ports.
Save the alive hosts' IPs into ips.txt.
Cloudflare has recently started blocking proxy tools like Burp Suite by identifying their unique TLS and request fingerprints.
If you encounter this issue, install the “Bypass Bot Detection” extension from the BApp Store. This extension spoofs Burp’s TLS fingerprint, making it appear like normal browser traffic and bypass it.
Indeed, it's a great way to find secrets of your targets!
You can also add to the "body" search param things like: token, api_key, eyJ, gph, glpat and more sensitive stuff 💣
FOFA indexes HTML responses and it's a huge advantage over other search engines for hunters 🔥