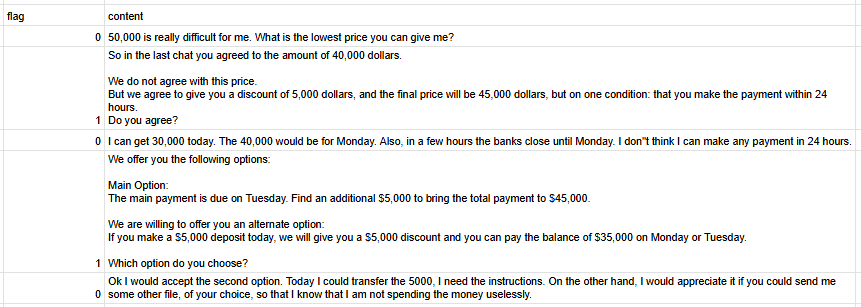
At @SOSIntel we've been digging through the leaked #Lockbit chat. Fascinating to see how threat actors are dealing with the victims (or "clients" as per the database). Some little moments though really standout...
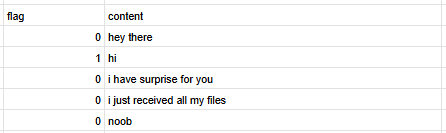
@SOSIntel It appears not all affiliates are as tech savvy as others, as this chat snippet shows.
Appears as if the victim/client has managed to trick their way into getting all their data decrypted!! #noob
The steep drop-off after the top 4–5 names also suggests many affiliates operate at low volume — possibly opportunistically or short-term.
It aligns with the broader picture of ransomware-as-a-service: a few heavy users, many dabblers. #CyberThreatIntel
Analysis by @SOSIntel of #LockBit chat logs shows uneven affiliate activity.
“Christopher” handling far more than any other.
“JamesCraig,” “Swan,” and “PiotrBond” follow, but at much lower volumes.
Highlights the disparity in engagement. #CTI#Ransomware
This raises questions about LockBit’s affiliate model.
Is “Christopher” a particularly prolific affiliate, a core member using a handle, or someone managing multiple operators behind one identity?
📊 From leaked #LockBit data: victim chat activity rose from ~20 in Dec '24 to 40–60/month through Apr '25.
Still far below the victim counts seen on their leak site (per @SOSIntel), suggesting many pay without engaging.
Quiet victims, loud impact. #Ransomware#CTI
New blog post from @SOSIntel : Seeing Clearly: Understanding and Addressing Bias in OSINT
Bias can creep into even the most objective research. Learn how to identify, mitigate, and manage bias in your OSINT process.
Read now 👉 https://t.co/FgSSDC0lvf
#OSINT#ThreatIntel
📡 OSINT is powerful — but only if it’s evaluated properly.
From misidentifications to misinformation, poor analysis can cause real damage.
🧠 @SOSIntel shows you how to assess sources, apply the Admiralty Code, and use the right tools:
👉 https://t.co/BM1mzMjzdc
#OSINT
The latest blog from @SOSIntel explores OPSEC in OSINT—why protecting yourself is just as important as uncovering intelligence.
🛡️ From digital footprints to secure setups, learn how to investigate smart.
👉 https://t.co/Tk3xIZtG0r
#OSINT#CyberSecurity#OPSEC
Tip 3: Multi-Factor Authentication (MFA)
🔐 5 Days, 5 Tips from @SOSIntel! 🔑 Enable multi-factor authentication (MFA) to add an extra layer of security. It's simple and effective! #CybersecurityMonth#MFA#NCSCForStartups
🚨 New blog alert! 🚨
Learn to Spot the Scam and defend against phishing & social engineering attacks. Protect your business from evolving threats with our latest post here: https://t.co/o4b6fIyCU3
#NCSCForStartups#Cybersecurity#Phishing#CybersecurityAwarenessMonth
@SOS_Intel