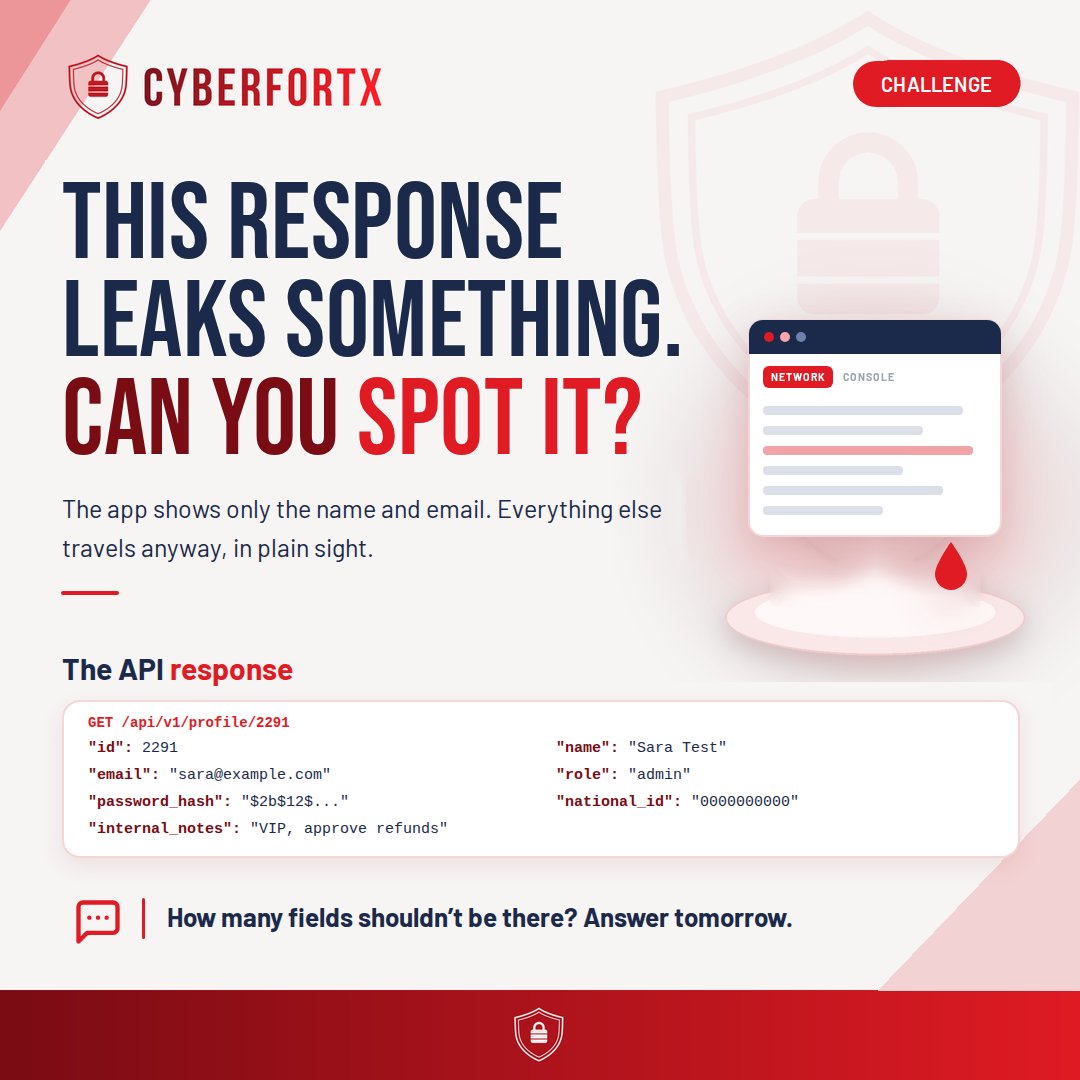
This API response leaks something.
The screen shows name and email. The response sends much more.
How many fields shouldn’t be there? Answer tomorrow.
#APISecurity#CyberFortX
Trusted yesterday. Verified today?
New device, new country, 3 AM. Zero Trust checks every request: who, from where, which device, which app.
#ZeroTrust#CyberFortX
Valid token. Wrong customer’s invoice.
The gateway checks who’s signed in. The service must check who owns the object. That’s #1 on the OWASP API Top 10.
#APISecurity#CyberFortX
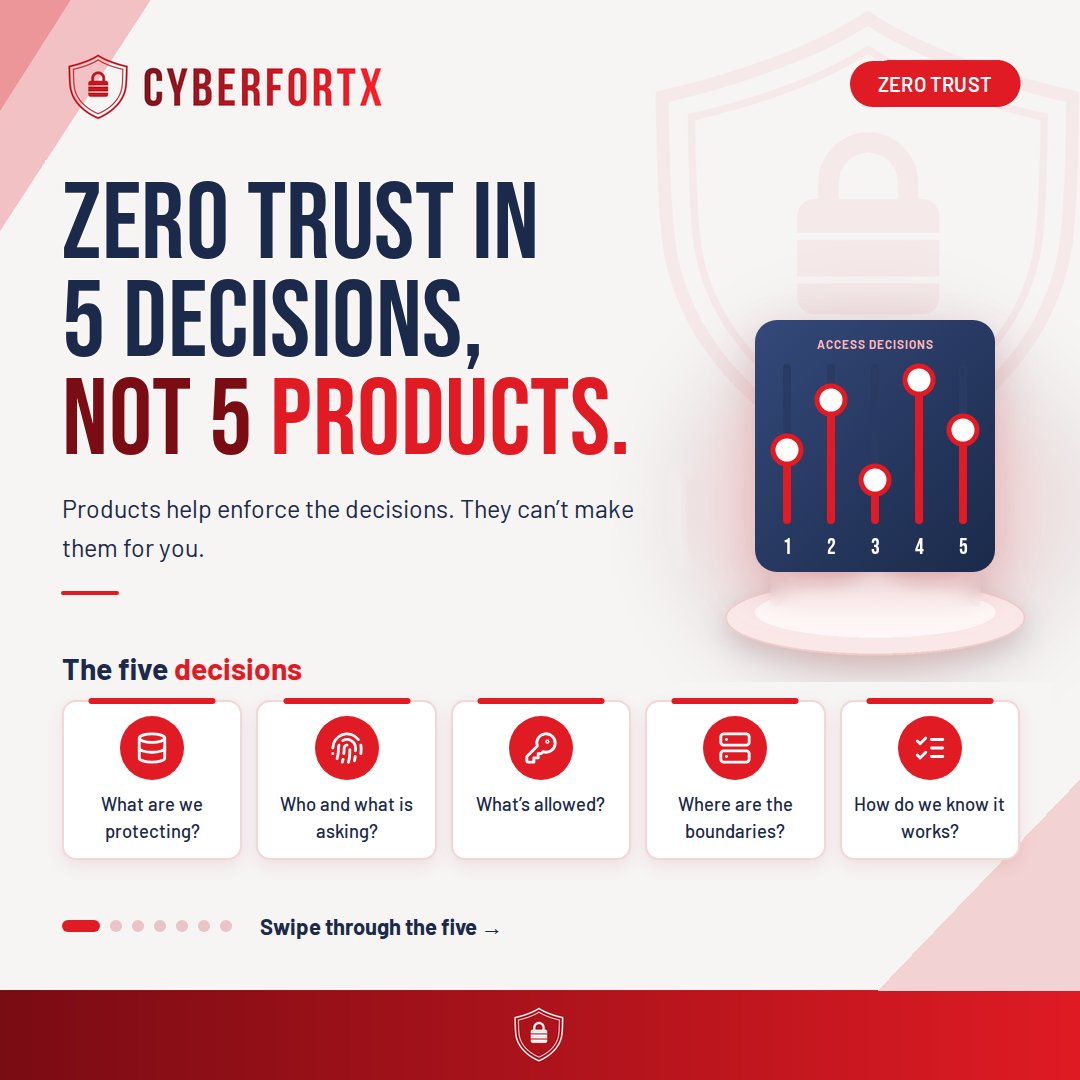
You can’t buy Zero Trust. You decide your way into it.
5 decisions: what to protect, who’s asking, what’s allowed, where the boundaries are, how you know it works.
Which one has your team made?
#ZeroTrust#CyberFortX
Change one number in the link. See another customer’s invoice.
Logged in is not the same as allowed. Inventory your APIs, check ownership in the service, test by swapping IDs.
#APISecurity#OWASP#CyberFortX
7:40 AM. Locked screens, a ransom note. You decide.
A. Pay fast
B. Shut everything down
C. Isolate, activate the plan, check backups
A, B or C? We’ll explain each tomorrow.
#IncidentResponse#Ransomware#CyberFortX
The backups were there. They were encrypted too.
Attackers go after backups first. Keep one copy immutable or offline, use separate backup credentials, and test your restores.
#Ransomware#ImmutableBackups#CyberFortX
Your RTO says 4 hours. Has anyone timed it?
Reality adds: finding a clean backup, rebuilding identity first, restoring in dependency order.
An RTO is real only after a timed full restore.
#DisasterRecovery#RTO#CyberFortX
Your RTO says 4 hours. Has anyone timed it?
Reality adds: finding a clean backup, rebuilding identity first, restoring in dependency order.
An RTO is real only after a timed full restore.
#DisasterRecovery#RTO#CyberFortX
Backups that report “success” every night tell you data was copied, not that the business can come back. Only a real, timed restore does.
When did you last restore from backup, for real?
#BusinessContinuity#DisasterRecovery#CyberFortX
Most access risks aren't a missing tool. They're accounts nobody owns.
What we find first in identity reviews:
• Service accounts with no owner
• Admin rights from finished projects
• Ex-employees still active in SaaS apps
Which would you find first? #IAM#CyberSecurity
Myth: one login = one lock.
SSO is one key to every door. Apps outside it keep their own passwords, and a stolen session skips the login altogether.
Fix: phishing-resistant MFA, every app behind SSO, short sessions.
#IdentitySecurity#CyberFortX
MFA is not the finish line.
20 push requests at 2 AM. One tired tap on Approve.
Fix it in the configuration: number matching, phishing-resistant keys for admins, a limit on push attempts.
Does your MFA ask for a tap or a number?
#MFA#CyberFortX
Access is granted by request and removed by memory.
It piles up at 3 moments: joining, moving, leaving.
The fix: HR as the source of truth, role-based packages, review on every move, automatic removal.
Which stage leaks most for you?
#IdentityGovernance#CyberFortX
He left 3 months ago. His account didn’t.
The directory was disabled. The SaaS apps weren’t.
Fix: HR as the trigger, automatic removal everywhere, a monthly ownerless-account review.
How long does removal take for you?
#IdentityGovernance#CyberFortX
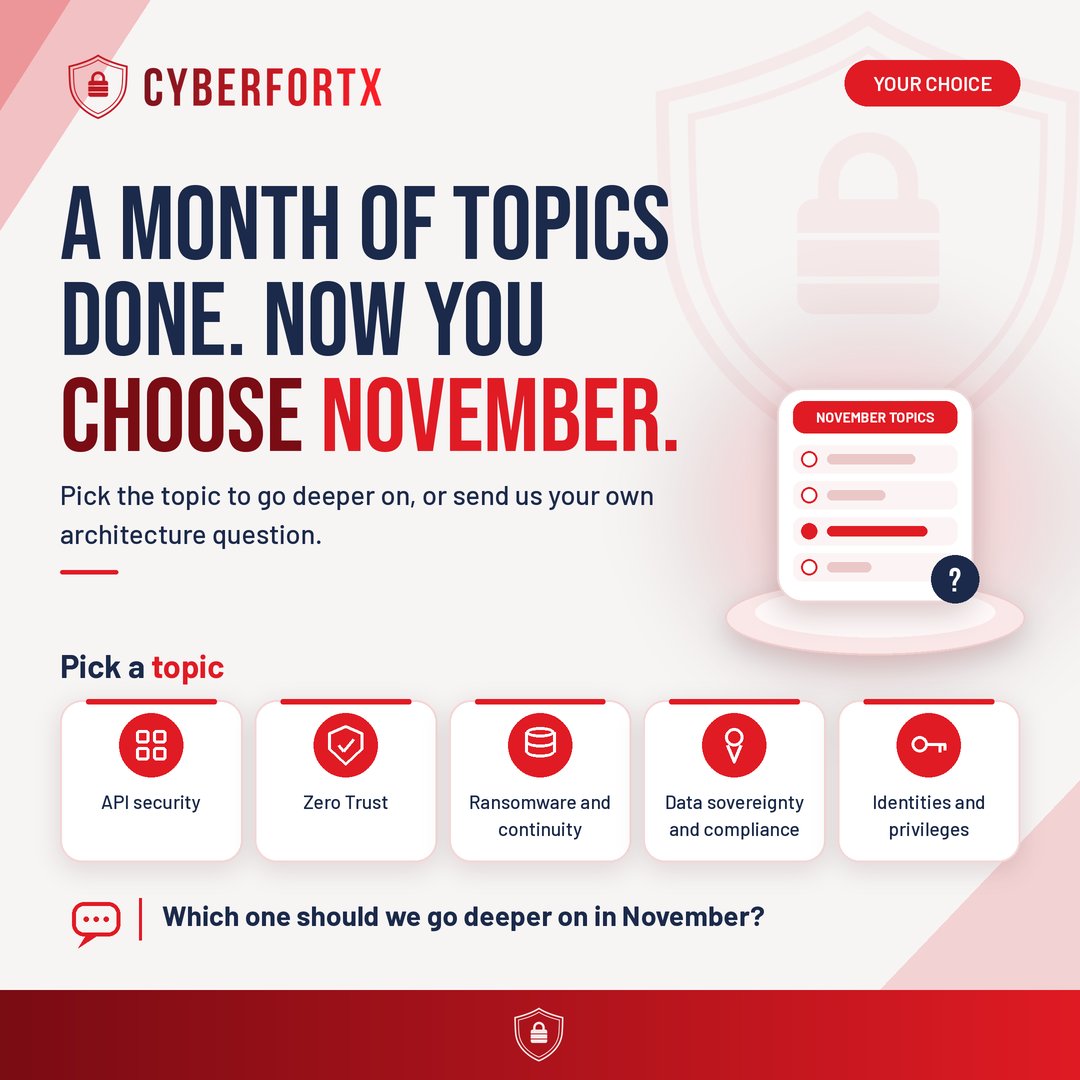
A month of topics is done. Which one should we go deeper on in November?
API security, Zero Trust, ransomware and continuity, data sovereignty, or privileges and identities?
Tell us your pick.
#Cybersecurity#CyberFortX
The month in one question per topic: APIs, admin access, machine identities, vendors, recovery, data sovereignty, independent assessment.
Any question you can't answer clearly is your next meeting's agenda.
#Cybersecurity#CyberFortX
People say multi-cloud cures vendor lock-in. Often it multiplies complexity without guaranteeing an exit.
What protects you: a written exit path, data exportable in open formats, and infrastructure defined as code.
Do you have an exit strategy?
#CloudSecurity#CyberFortX
A hypothetical: 7:40 AM, billing systems are down. Who decides to isolate? Who talks to customers?
A tabletop exercise tests decisions, not devices, and puts leadership, legal and comms in one room.
When did senior leadership last take part in one?
#Readiness#CyberFortX