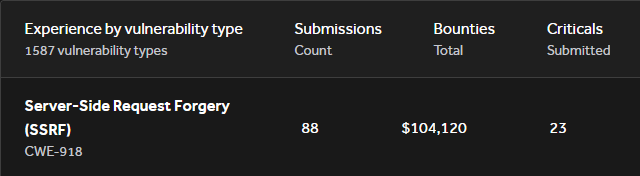
I've made over 100k on SSRF vulnerabilities.
They aren't always as simple as pointing it at localhost or AWS Metadata service.
Here are some tricks I've picked up over the past 5 years of web app testing:
this course has been a real wealth of knowledge explaining the concepts of advanced evasion techniques and most effective Active Directory breaches in depth, highly recommend it to anyone who want to advance their evasion techniques and/or Active Directory skills @offsectraining
@shreyacasmalert this has been a subject for discussion on multiple occasions, how it affects one strongly depends on the type of person you are, for some it tends to be beneficial while for others it could be degrading. Humans are social creatures by nature and I consider RW is kind of unnatural
Researchers at @proofpoint have tracked a financially motivated cyberthreat actor, TA558, as it targets hotel and travel organizations in Latin America. The group has drawn from at least 15 different malware families since 2018: https://t.co/gGHVetDBT2
Just wrote a short write-up on my latest research at #BHUSA and #DEFCON! You can check the slides and video there!
Let's Dance in the Cache - Destabilizing Hash Table on Microsoft IIS! https://t.co/hdZEvntxlW
How to exploit CSPP (on our early adopter channel)
1) Go to the proxy tab
2) Click Open Browser
3) Pin the extension
4) Enable prototype pollution
5) Visit https://t.co/Y29Hiyc8T8
6) Open devtools > DOM Invader
7) Scan for gadgets
8) Open devtools > DOM Invader
9) Click exploit
Since Microsoft plans to disable macros by default, I have decided to release a proof of concept that I use on my engagements by leveraging the document properties built in Microsoft Office.
Here is the link to the article: https://t.co/ZvgDxeuIJG
"Abusing HTTP hop-by-hop request headers" by @nj_dav was nominated as a top web hacking technique back in 2019, and has just blossomed into an F5 BIG-IP unauth RCE!
https://t.co/8WYT6JNOhh
https://t.co/tdQzM1OG5L
https://t.co/ZPVrMVxDkr
Hunting evasive vulnerabilities: finding flaws that others miss - from @albinowax - premiered at Nullcon Berlin. If you didn't catch the live event, it's now available on YouTube.
https://t.co/WwEIjEBnyO
I’ve been doing web security research for many years now and what I’ve noticed is results depend on a combination of luck, skill, knowledge and persistence. That’s why persistence is so important because an element of luck is required. This is why some knowledgable people don’t -
4/8/22 #bugbountydiary#bugbountytips
Everyone is sick in the house but I had some running scans I needed to check up on.
I found a SQL injection bug on a blog.
Here's how I did it, so you can learn...
👇
🚨Like, retweet, & follow for more hacker tips!🚨
1/x
#WAF#Bypass
(Akamai's Kona)
<a href="javas%09cript:[1].map(top['ale'+'rt'])">
Built with tricks you find in https://t.co/1TfS9CHeJX!
PoC Vector:
https://t.co/3bmIxEaHlx
PoC Bypass: