A beginner's guide to bypassing BIOS passwords on laptops. Dives into identifying vulnerable chips, executing bypass methods, and exploring the reasons behind this attack and its prevention.
🔗 https://t.co/Hq4BJzU3hz
#HardwareHacking#BIOSBypass#LenovoLaptops#CyberSecurity
On #WorldPasswordDay, CyberCX's @jlaundry explores why we're gearing up to say goodbye to passwords, and projections for the future as we prepare for a shift towards passkeys.
Read the blog here: https://t.co/iziLuhqgN6
In January 2024, while examining a Netcomm NL1901ACV VDSL Modem, CyberCX discovered an input sanitisation vulnerability leading to remote code execution.
Learn about the team's findings and potential impact in our latest technical series blog: https://t.co/iwLKCHdIHY
Introducing Efflanrs - a Python tool, written in-house and released by CyberCX for open source, designed to enhance the usability of Snaffler.
Read our latest technical blog by @dajnewin to find out how you can start using the streamlining tool today: https://t.co/IhdsrMZNYm
My writeup on how to protect your Evilginx server from the dreaded 'Deceptive site ahead' warning when conducting Red Team and Social Engineering engagements 🎣 https://t.co/gqcw3jeMcg
Today, CyberCX has released an advisory about a vulnerability that existed in Adobe #ColdFusion, where an unauthenticated attacker could obtain remote code execution with 20,000+ vulnerable hosts directly exposed to the Internet.
Read more details here: https://t.co/oAYnUDiIAF
Our latest tech blog explores h ow CyberCX's Daniel Jensen developed an extension to popular web application testing tool #BurpSuite, widely used by members of the #cybersecurity community to conduct research & penetration testing.
Read more in the blog: https://t.co/h4GqFFilja
In our latest Technical Series blog, Senior Security Consultant Aakash Gyawali explains what Cross-Site Leaks (XS-Leaks or XSLeaks) are, providing an example attack, along with mitigation options for application developers and systems administrators 🧑🏾💻
https://t.co/Xr29UsDwYN
Really well written article, backed up with Shofe Miraz presentation at AppSec 2023. On top of all that he's released tooling for other pentesters as well!
https://t.co/4oLNgFz576
In our latest Technical Series blog, CyberCX's Shofe Miraz attempts to bypass restrictions in #Flutter that protect apps from malicious activity, but are also an obstacle for mobile application penetration testing.
Read the detailed article here: https://t.co/0A3cK6d1V9
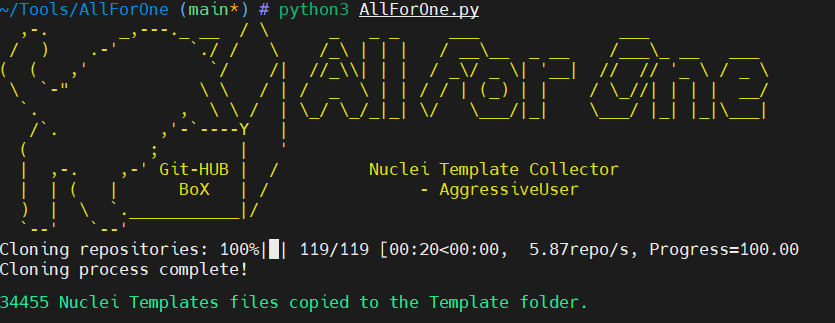
🔍 There have been hundreds of thousands of FOSS vuln check rules created.
👍 While @pdnuclei (by default) has a great many, there exists a project to gather over 119 repos of Nuclei checks/templates.
➕ That's over 30,000 additional checks.
https://t.co/85EC7DDfTq
The first blog in our new Technical Series explores #Azure SSRF Metadata 👨💻
Find out how Azure-hosted services can be exploited through Server-Side Request Forgery attacks, and what developers & system administrators can do to minimise these risks: https://t.co/IVDGWdXPjB
Registration for #OWASP New Zealand Day is open! Join us for this 2-day web and application security conference, emphasizing secure architecture and development techniques to help Kiwi developers build more secure applications! REGISTER TODAY: https://t.co/mtA4L8Ar1v
#appsec