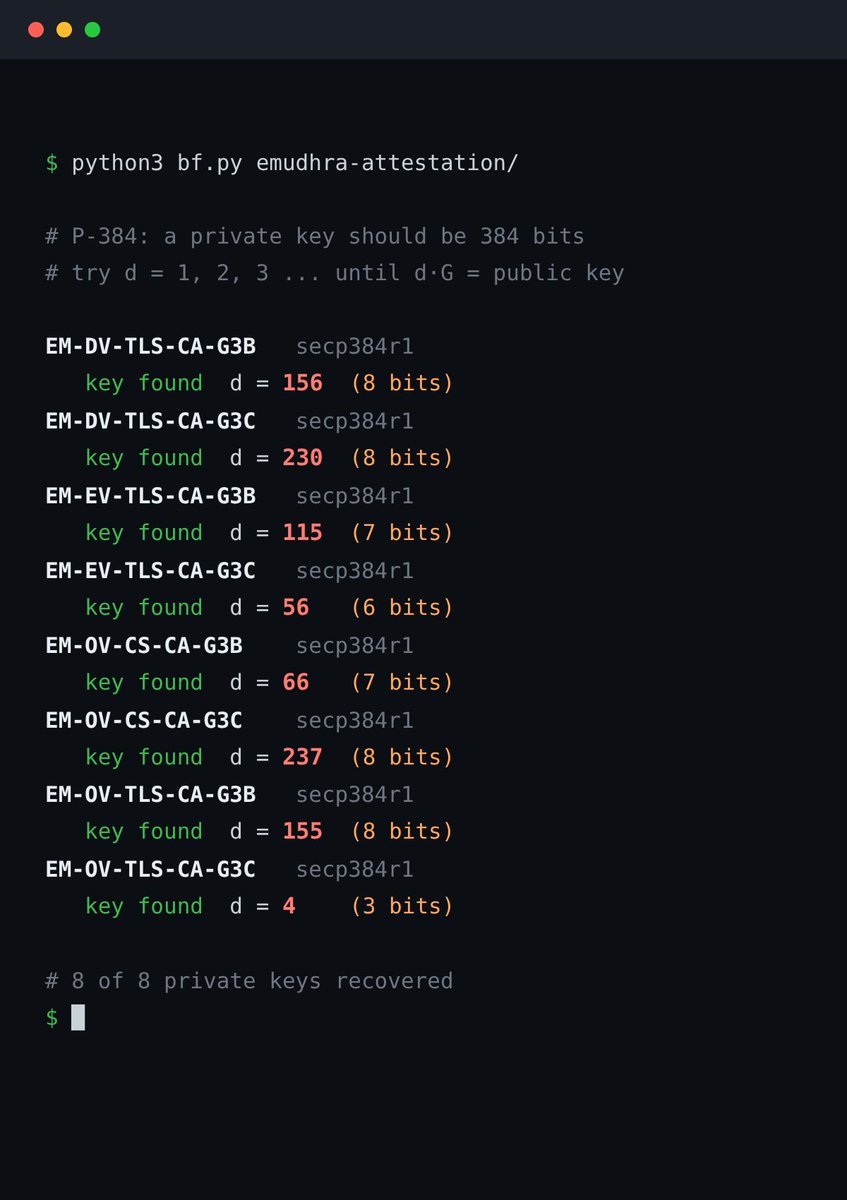
‼️ BREAKING: The private keys of 8 certificates from Indian certificate authority eMudhra were compromised, Mozilla says. Firefox blocked them within 3 hours.
Each key should be a 116-digit number, but one was just 4.
Anyone can guess them and forge HTTPS certs for any website.
but the higher capacity parts get cost cutted
- 1TB : Now use BC8Q-1T as the main supplied drive, which is a QLC NAND from SKHynix. But Apple also have Samsung 3DV8 1TB TLC as a rare alternative. Imagine buying an iPhone 18 Pro/Max 1TB and getting a slower drive, oh god.
2/3
For my first post, I’m sharing a letter @NVIDIA signed on why open models matter.
AI will transform every industry, power every company, and be built by every country.
Open models strengthen safety and cybersecurity, accelerate innovation and diffusion, and enable sovereignty.
The world needs both frontier closed models and frontier open models.
https://t.co/AUKzoQ5Ikb
Instagram decided to roll out a new “Muse AI” feature, that lets users create AI images based on people’s Instagram photos.
Then they opted in EVERYONE with a public account
To opt out:
Click your profile picture
3 bars in the top right
scroll down to "Sharing and reuse"
Toggle off for both Posts and for Reels
Introducing Sakana Fugu: A full multi-agent orchestration system accessible via a single model API.
Our ‘Fugu Ultra’ model matches the performance of Fable and Mythos, delivering frontier capability without the risk of export controls.
Try it: https://t.co/hhO6qTawgb 🐡
Update 5:05 PT: The attack has now expanded well beyond @TanStack and @Mistral.
373 malicious package-version entries across 169 npm package names, including @uipath, @squawk, @tallyui, @beproduct, and more.
The malware propagates by stealing your CI credentials and using them to publish new compromised versions.
Full IOCs, affected package list, and detection steps: https://t.co/jWG9DUCu3x
🚨 BREAKING: cPanel and WHM, the control panels behind an estimated 70+ million websites, have a critical security flaw that lets anyone become root admin without a password. CVE-2026-41940 affects every supported version. It’s already being exploited in the wild.
watchTowr Labs published the full attack today, after the hosting company KnownHost confirmed the bug was already being used to break into a significant chunk of the internet.
If you've never heard of cPanel: it's the dashboard that hosting providers and millions of website owners use to manage their servers, domains, email accounts, databases, and SSL certificates. WHM is the admin version that controls the entire server. If someone gets root access to WHM, they get the keys to the kingdom and to every apartment inside it.
How the attack works, in plain English:
🔴 Step 1: The attacker sends a deliberately wrong login. cPanel still creates a temporary "you tried to log in" record on disk and gives the attacker a cookie tied to it.
🔴 Step 2: The attacker tweaks the cookie to disable cPanel's password encryption. Normally cPanel encrypts the password field on disk. With one small change to the cookie, cPanel just stores it as plain text instead.
🔴 Step 3: The attacker sends a fake login attempt where the password field secretly contains hidden line breaks. cPanel does not strip these line breaks out, so they get written straight to the session file. Each line break creates a brand new fake record. The attacker uses this to inject lines that say "this user is root" and "this user already authenticated successfully."
🔴 Step 4: The attacker visits one more random page on the site to nudge cPanel into re-reading the file. cPanel then promotes the injected fake lines into its main session memory.
🔴 Step 5: On the next request, cPanel sees a flag that says "this user already passed the password check." cPanel trusts that flag, skips checking the actual password, and lets the attacker in as root.
From start to finish, the attack takes a handful of HTTP requests.
If you run cPanel or WHM, the patched versions are:
🔴 cPanel/WHM 110.0.x → 11.110.0.97
🔴 cPanel/WHM 118.0.x → 11.118.0.63
🔴 cPanel/WHM 126.0.x → 11.126.0.54
🔴 cPanel/WHM 132.0.x → 11.132.0.29
🔴 cPanel/WHM 134.0.x → 11.134.0.20
🔴 cPanel/WHM 136.0.x → 11.136.0.5
If your version is older than these, assume someone has already broken in and act accordingly. Patch right now, then rotate every password and key the server touched: root passwords, API tokens, SSL private keys, SSH keys, mail passwords, and database passwords.
@HarmeenSoch Right? 😅 same here. And the previous intersection’s just as bad—random cars jumping in even on red.
Nice to see someone else actually noticing this stuff.
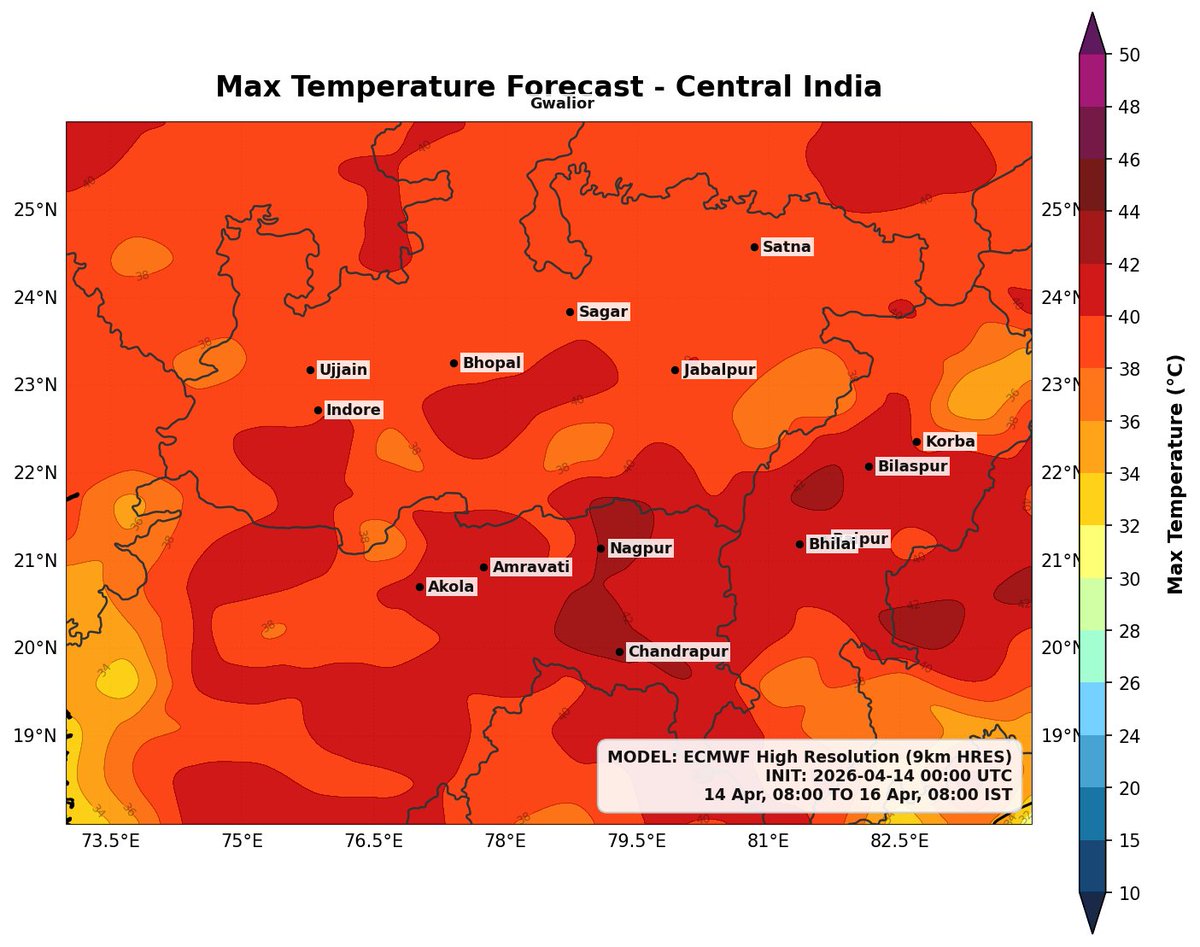
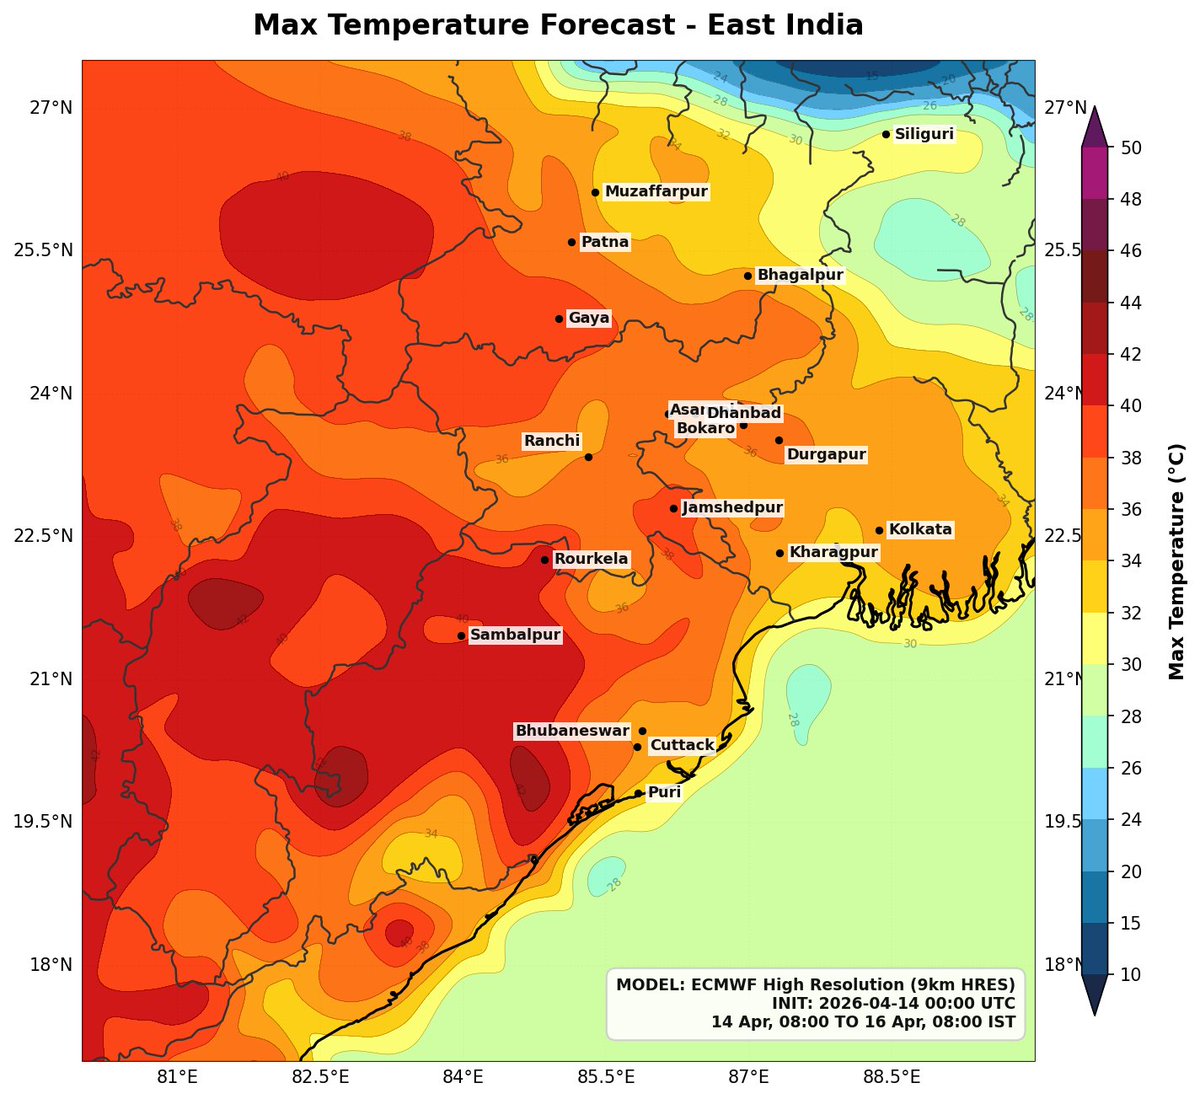
Over the period of next 48 hours #Heatwave to intensify in #India with expected maximum temperature in the range of 42 to 45°c in the interiors of #Maharashtra#MadhyaPradesh#Chhattisgarh#Odisha.
#Delhi NCR to cross 40°c mark for the first time in this season, #UttarPradesh & #Rajasthan brace for 42-43°c.
No respite anytime soon, temperatures will keep on rising gradually over the period of next 2-3 weeks.
#Summers #Summers2026