That moment in a conversation when you realised that neither of you was wrong,
but you just both saw things from different perspectives. That's what real communication is about;
understanding, instead of being right.
Be a good person. No amount of money, titles, or status can hide who a person truly is. Sooner or later character speaks, intentions show, and the way you treat others tell the story.
At the end of the day, a pure heart, honesty, humility & good character will always win.
this ai scares you for real.
you paste your website link. Explee works out who needs the product. the replies and booked calls land on your calendar.
it runs the entire process. i did not sign up for this scare.
ok. testing it: $30 free
https://t.co/BBHKdjP8vC
‼️ Hackers broke into Polish payment operator Autopay with no malware and no phishing. The company says it was an attack of "a completely new type", run with mass use of AI tools.
Its security manager told Polish security site Sekurak the attackers used valid logins and admin tools to move through its monitoring, deployment and password-management systems. Each step looked like routine admin work and didn't trip the usual alarms.
They reached part of the payment data Autopay processes. It says it can't rule out that the data was copied, and is contacting everyone who may be affected.
The sea has always ruled us. For centuries we've been slaves on a ship, registered at birth like cargo, following a current we call currency, and today that ship has to sink so we'll beg to board the next one. The old financial system goes under while the only thing they launch is a rocket, the symbol of the digital money that will own you instead of the other way around. Nothing is organic, nothing is random, every sinking is a ritual planned long before us. Learn to read the code. Watch my series See in the Dark at https://t.co/VvDf4qP8aJ
🛡️ Claude Gets VirusTotal TI Capabilities for AI-Assisted Malware and URL Analysis
Details: https://t.co/Z3Mtwhq0qe
Claude users can connect VirusTotal threat intelligence to their investigations, bringing file, URL, domain, and IP reports into an AI workflow. The connection lets analysts review detection findings, analysis dates, coverage, and source links without treating an AI answer as a security verdict.
The integration uses Model Context Protocol, or MCP, to connect Claude with VirusTotal AI, known as VTAI. Users authenticate through browser OAuth without providing a personal VirusTotal API key. Organization rules may require an owner to approve the connector before employees can use it.
#cybersecuritynews #claude
🛑 Google warns hackers are using autonomous AI agents to turn security patches into working exploits.
Attackers are deploying multi-agent frameworks to automate hacking, weaponize known flaws, and speed up intrusions.
Here's what Google uncovered: https://t.co/4LYuPonBzW
🛑 Google warns hackers are using autonomous AI agents to turn security patches into working exploits.
Attackers are deploying multi-agent frameworks to automate hacking, weaponize known flaws, and speed up intrusions.
Here's what Google uncovered: https://t.co/4LYuPonBzW
🚨 Amazon uncovers AI agents hunting API keys across LiteLLM, Dify, and other AI apps.
Captured logs reveal the playbook: exploit weak spots → steal API keys → use those keys to power more attacks.
The campaign's reported results remain unverified.
Full story: https://t.co/k7y80PiRnl
‼️ Japan's cyber response team has found about 1,000 servers it suspects are bases for AI-run attacks on websites worldwide.
Most run AI pentest tools such as ARTEX. They appear to scan sites for flaws and try to steal config files.
One held traces of an Anthropic coding tool.
I hear about ARTEX all day, but there are so many other AI pentesting frameworks out there like CyberStrikeAI, HexStrike, PentAGI... Some people talk about these tools like they can do magic and we won't be able to stop them. AI gives TAs speed, and speed comes with a cost…. it can be noisy. Don't just detect on user agents, they are very inconsistent, look into the behaviors. I mean, at the end of the day they just behave like any other pentest tools
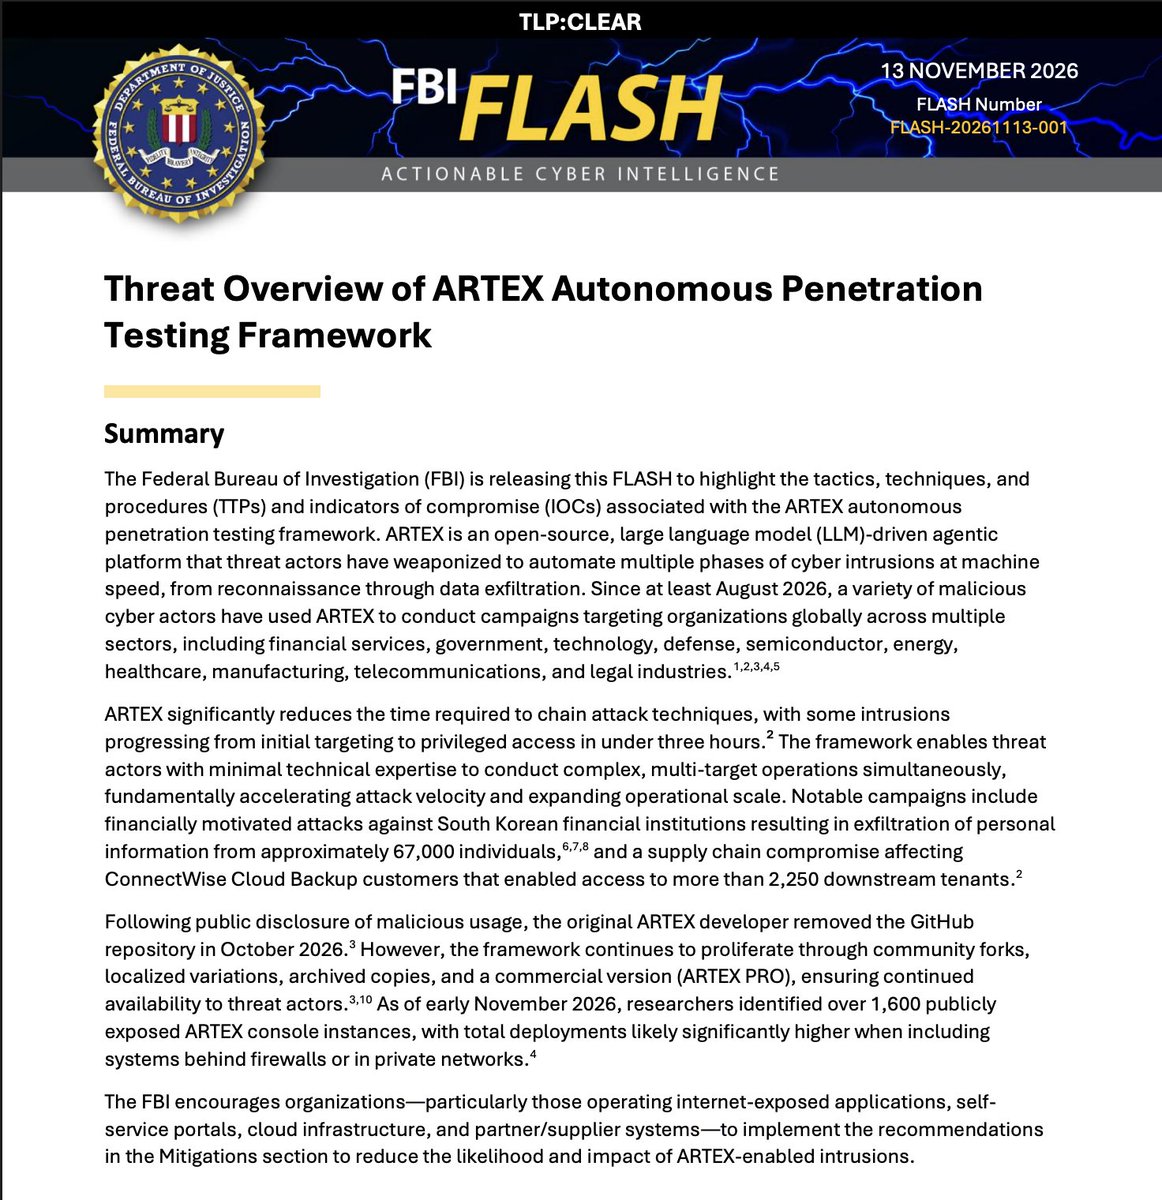
The FBI just issued a warning about AI agents being used to hack companies.
Some attacks reached privileged access in under 3 HOURS.
67,000 people's data exposed. 2,250+ downstream tenants affected in a separate campaign.
The tool behind it? ARTEX.
Here's how the attacks work. 🧵
We are all tools
In this world,
If you are’
honest they
use it against us,
If you lie’
They call you
a betrayal,
The world isn’t’
Friendly to good people.
Sentiment aside, Picazo gave us the hottest before fame freestyle, guy was on fire🔥
I don't know what happened, bro's rap ability just reduced as soon as he blew
someone is trying to take down the internet's biggest privacy network and they're adapting faster than the fixes
tor, the network people use to browse the internet anonymously, is under a massive attack
hackers are flooding its servers with so much fake traffic that the whole system is slowing down
the tor team rushed out an emergency fix. within 10 minutes the attackers switched to a completely different method
whoever is behind this is watching the defense team in real time and adjusting on the fly
tor says this is far from over and more emergency updates are coming
the network that millions of people depend on to stay anonymous online is in a live fight right now, and the attackers are keeping up
The same operator says the attack on their relay stopped the moment it lost its HSDir flag, the role that stores the lookup records for onion services.
Source: https://t.co/0jJVBVgS1F
Don't miss out on any news, join our newsletter: https://t.co/wCLSRPDvs1
Be sure to join our TG channel: https://t.co/tXwFKv6wzn
Tor Project just issued a rapid-response security release with key DoS defenses amid the ongoing sustained DDoS attack on the network.
https://t.co/zDLyRrWi2V
*that explains why things barely worked today: crazy slow, and I couldn’t connect for a while
h/t https://t.co/BTrpQDYgFr
Başarılı bir veri güvenliği mimarisi için DLP'de şunları kesinlikle yapmalısın:
▸ Data Classification uygulamalıs��n. Yoksa DLP her dosyayı taramaya çalışır; devasa bir CPU yükü oluşturur ve yapısal olmayan veride bypass edilebilir.
▹ Belirli bir olgunluk seviyesine geldikten sonra DLP'yi agresif şekilde blok modunda kullanmalısın. Sadece monitoring yaptığın DLP ile sadece CPU harcarsın.
▸ Mutlaka CASB konulmandırmalısın. Dışarı çıkan verinin şirketin kurumsal cloud depolamasına mı yoksa kullanıcının kişisel cloud depolama hesabına mı gittiğini ancak bu sayede görüp engelleyebilirsin.
▹ Gelen her talebe exception vermemelisin. Öbür türlü DLP değil Data Pool kurmuş olursun. "Dosya, upload edilen web sitesinden daha sonra download edilebiliyor mu" sorusunu sorgulamalısın.
▸ Alarm geldiğinde "O, veri çıkarmaz tanıyorum." önyargısını bırakmalısın. Bu durum "Insider Threat" ile el sıkışmaktır.
▹ Net bir Incident Response planı oluşturmalısın. Planın yoksa o alarmlar sadece okunmayan bildirimlere dönüşür.
▸ Bloklanan kullanıcıya "justification" ekranı sunmalısın. Kullanıcıyı sürece katmadan güvenlik kültürü yaratamazsın.
▹ 6 ayda bir Policy Review yapmalısın. Bunu aksatırsan eski hatalarını sonsuza kadar yaşarsın.
▸ Mobil cihazları DLP'yi entegre etmelisin. Yoksa yönetilmeyen kişisel cihazlarda veri sızıntısını engelleyemezsin.
▹ Politikalarında threshold ve kademeli aksiyonlar tanımlamalısın. Örneğin threshold 10 için justification, 50 için yönetici onayı, 100 block tetikleyebilirsin.
▸ VPN öncesinde mutlaka HIP kontrolü yaptırmalısın. Cihazda bir DLP ajanı yoksa kurumsal ağa erişimi engellemelisin.