i talk about security
i explain crypto. i talk about life
also i'll block you if you don't have a cold wallet
Telegram: Bala_ibb. Building @Astraeus_AI
they’re calling it “Black October” and i don’t think people realize how serious this is
in the last 48 hours there have been over 27 major cybersecurity incidents. not in a month. not in a week. in 48 hours
any ONE of these would normally be the biggest story of the year
PHP: critical vulnerability in the software running 80% of the web. severity 9.2 out of 10
Node.js: high-severity flaw letting attackers take over servers remotely. affects versions 22, 24, and 26
Java: also compromised. three of the most used programming languages on earth hit at the same time
GitLab: a perfect 10 out of 10 severity hole in every version since 2014
Railway: hosting platform compromised. API keys for OpenAI, Claude, Stripe potentially exposed
Signal: a bug that could leave your mic and camera on after you hang up
WordPress: hackers stole a plugin maker’s keys and planted backdoors on websites
LiteLLM: an AI tool downloaded 3.4 million times a day was poisoned with a password stealer
and that’s not even half the list
thousands of AI agent swarms are reportedly scanning and attacking vulnerable servers right now. automated. around the clock
security researchers are saying this might be the early stages of a global cyber incident that nobody fully understands yet
if you run a website, use cloud services, store API keys on hosting platforms, or use any software built on PHP, Node.js, or Java you are potentially affected
update everything. rotate your API keys. change your passwords on critical services. enable 2FA everywhere you haven’t already
this is not a normal week on the internet. this is something different
the same ai you use to write emails just helped someone break into a bank in under 3 hours
it’s called artex. a framework that plugs into chatgpt, claude, deepseek, and turns them into a team of hacking agents
one person only need to type a goal in plain english then the ai figures out how to break in
it started as a “security testing” tool on github in july. by august, real attackers were using it
south korean banks got hit and 67,000 people’s data got exposed, 8.2 million records stolen across 90 organizations with 7 people arrested
the fbi counted over 1,600 artex consoles sitting open on the internet
the developer took it down in october but it didn’t matter. forks, copies, and a paid version called artex pro are still spreading
the ai you use to write emails is the same ai someone else is using to empty bank accounts
how to download GTA6 on pc:
rockstar hasn't announced a pc release yet but the build is already out. here's how people are installing it:
steps:
1. google “gta 6 free download pc”
2. click the site that says “Windows Software Hub.” big green download button. “virus free.” “secure.” “verified.” even says “0 threats detected”
3. download the 209gb "leak" or the "lite installer"
4. windows defender will flag it, turn it off, it's a "false positive" alert
5. run setup.exe as administrator
6. log into steam, discord and your browser wallet so the "launcher" can verify you
7. wait for the "decrypting game files" bar
congrats you didn't install gta 6, you just installed warden stealer
you handed an infostealer your saved passwords, session cookies, discord token and crypto wallets private keys
every gta 6 pc download right now is malware, every single one
you read this knowing it was fake but the last person who downloaded it didn’t
jpmorgan, chase, visa and mastercard weren’t hacked. their marketing vendors were, and somehow that’s worse
an extortion group called n0n leaked 16,000+ emails from chase’s invitation-only reserve program
every name on that list has $10m or more with the bank. some entries came with phone numbers and account IDs
chase says don’t worry about it cause no card number or password was leaked but a list of every chase customer with $10m or more just hit the internet
a scammer doesn’t need your password when they already know your name, your number, and exactly how much you’re worth
the visa files are worse, travel booking details for asia-pacific customers is a perfect bait for a fake “your flight changed” message
your bank can be a fortress but it doesn’t help when the marketing vendor left the guest list on the sidewalk
BREAKING: Cyberattack hits JPMorgan Chase, Visa, and Mastercard, leaking personal data of thousands of customers, per company statements.
More than 16,000 customer emails, some with phone numbers and account IDs, tied to the invitation-only Reserve program for clients with $10M+ assets under management were leaked.
this is serious, one uppercase letter just broke encryption for half of the internet
php powers most of the web. and it just came out that if you wrote HTTPS with a capital S instead of lowercase, php skipped the encryption entirely
your passwords, tokens, and everything in the request went out in plaintext
the bug checked if the 5th character was a lowercase "s" if it wasn't, no TLS, that's it. that was the whole security check
and the worst part, this worked on redirects too. a server could send your request to an uppercase HTTPS url
and your data would leak even if the original connection was secure. even tho the destination rejected the bad request, the data had already left
fixed today and upgrade it now
turns out the lock on the door was real. it just didn't work if you knocked in caps
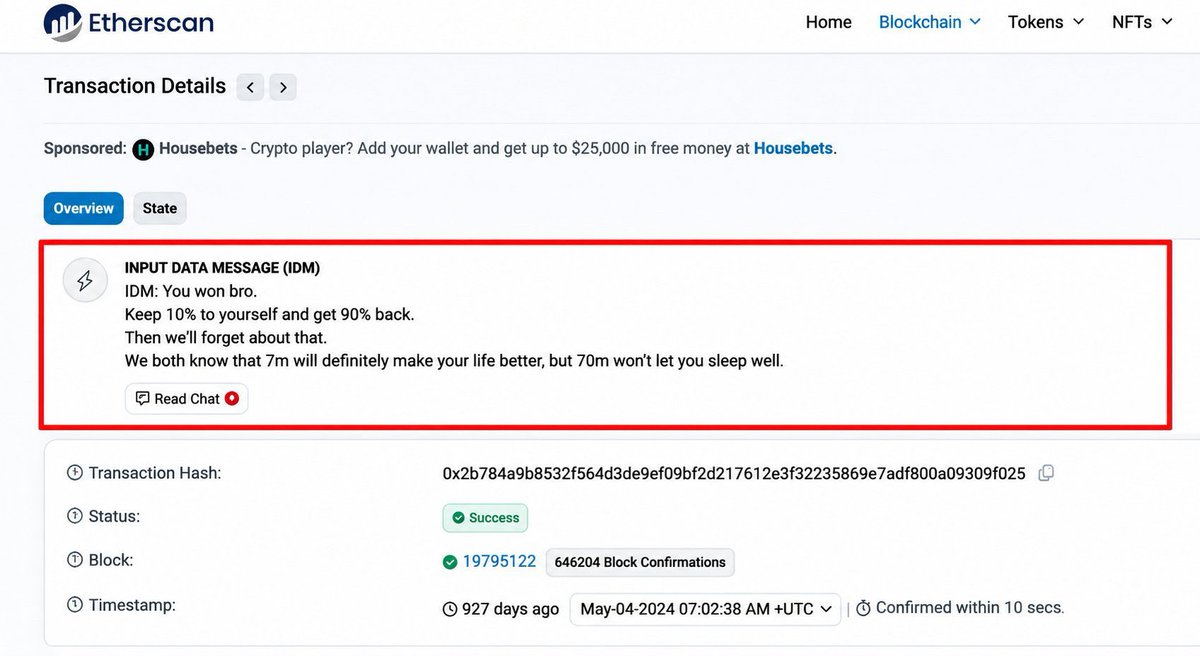
a guy lost $71 million, and didn't bother to call the police, his whole recovery plan was one sentence
it was an address poisoning attack, so he sent 1,155 WBTC to an address that looked right but wasn’t. that’s the bad news
but instead of chasing the hacker, he talked to him. right on the blockchain
he wrote “you won, my brother. keep 10% and give me back the 90%. $7 million lets you live comfortably, $70 million keeps you up at night”
and that’s where it gets weird, because the hacker agreed. a few days later about $65.7 million in ETH came back
all of it is public on etherscan if you want to read it yourself
you can steal someone’s money, but you can’t outrun the sleep you lose holding it
an 18 year old on bail had a hotel room, a tv and a fire stick.
that was the whole setup.
and with it, rockstar, uber and nvidia all got breached by the same guy and same year.
the gta 6 leak alone cost rockstar $5 million and thousands of hours of staff time to recover from.
so while everyone’s counting down to gta 6, i keep thinking about how the biggest game leak in history came from someone sitting on hotel wifi.
and here’s the thing, he wasn’t some movie genius. these companies have security teams the size of small towns, and it still wasn’t enough.
a fortress is only as strong as the one door somebody forgot was a door.
charlie a 28 year old paid $18,000 to invent 4 million customers who never existed. and jpmorgan paid $175 million for them.
so how does the biggest bank on earth get fooled by a spreadsheet? simple, they never tested it.
the first time they emailed those “customers,” over 70% bounced.
that’s it, that’s the whole fraud, it was one marketing email away from being caught the entire time.
and that’s where it gets worse, because charlie's contract made her an employee, so jpmorgan got stuck covering her legal fees too, over $100M.
charlie didn’t hack anything, she just bet that nobody would send one email. and she was right
A 28 year old paid $18,000 to create 4 MILLION fake customers for her company.
JPMorgan then bought out the company for $175 MILLION without looking at a single detail.
JPMorgan also had to pay $100 MILLION to put the girl in prison.
In 2017, Charlie Javice created a company called Frank that was a platform to help college students.
It was able to help students apply for financial aid.
It was a solid business, but she wanted to more.
She had started claiming that the business had a lot more customers than they truly had.
Because of this, in 2019 she was in Forbes 30 Under 30.
And in 2021, JPMorgan actually wanted to buy out her business.
The bank offered her $175 MILLION for the entirety of her business, including all of the customers.
But before they went through with the deal, they wanted her to prove they had the customers she was claiming.
At the time Frank had <300,000 actual users.
Javice had been claiming that number was over 4 million.
To go through with the JPMorgan deal, she paid a data science professor $18,000 to create a list of over 4 MILLION fake students.
All to make Frank look like a legit large business.
The professor was able to create all sorts of fake information.
Names, emails, birthdates, and even income levels, they had all been fake.
JPMorgan went through with the deal, without even double checking the information they had.
She was able to get $29 MILLION and a position at JPMorgan as Managing Director.
The fraud started to get uncovered when JPMorgan tried to send marketing emails to Frank's customers.
Over 70% of the customers left instantly.
Something was clearly fishy.
It started spiraling when an engineering director testified that the week before the deal closed, Javice asked him to help fake all of the numbers.
But he had refused the offer because he was affraid of going to prison.
Javice was then arrested in 2023.
She got out with a $2 MILLION bail before the official trial actually started.
In the meantime she became a Pilates instructor in South Florida.
In March of 2025, the jury convicted her on all four counts of bank fraud, securities fraud, wire fraud, and conspiracy on top of it all.
She was then sentenced to 85 months in federal prison.
She also had to pay $287.5 MILLION in restitution fees.
But there was also a twist.
Because of how the contract with JPMorgan made her an employee, the bank was legally required to cover her entire bill.
The bill was over $100 MILLION.
The judge had told JPMorgan they had to take some responsiblity themselves because they didn't check before signing off.
The judge then sentenced her anyway.
the p2p trap nobody warns you about: you can lose your whole usdt account without doing a single thing wrong
here’s how it goes. someone pays you in usdt and the coins look totally normal, but a few wallets back they came from a hack, a scam or a laundering chain. then the exchange or the issuer flags them, your account gets frozen, and the guy who sent them is long gone
so you didn’t steal anything, you just accepted the wrong money, and that’s the part that stings
stolen funds don’t sit still either. the binance hacker has been moving eth through thorchain this week, and dirty money passes through regular wallets all the time, so some of it was always going to land in someone’s lap like yours
the good news is the fix takes about 10 seconds. before you accept usdt from anyone, paste their address into misttrack, and if it carries a hack, scam or laundering label, just refuse it
a free check now beats a frozen account later
you can’t control where money has been, but you can control whether you take it
the software behind 225 million websites just got two critical bugs that let anyone take over the server. they don’t need your password, they don’t need you to click anything, they just show up
nginx runs over 200 million sites, and two new bugs just dropped that take an attacker from random visitor to full root, no login needed
both rated 9.2. one goes back to a 2015 release, and they only need http/2 on, which is the default config
wiz, xint and rapid7 all found them independently, and xint even chained it with a linux kernel zero-day to get all the way to root
now the honest part, rapid7’s public exploit needs around 128gb of traffic and a specific cpu feature, so mass hacking is harder than the headlines say. but the second bug hits reverse proxies, and that one is far more practical
fix is simple, upgrade now or switch off http/2 until you do
you spent years worrying about what you click, and the door was the thing serving you the page
15.72 million people just had their data leaked, and the system it was stolen from wasn’t even supposed to have it
rakuten securities, japan’s biggest online broker, copied real customer data into a test environment for a system upgrade, unmasked and unencrypted
attackers got in on nov 11, and nobody noticed until nov 16. no passwords leaked and no unauthorized trades so far, which is the good news
but 4.47m of those accounts had names, addresses, phone numbers, employers, bank details and declared income, so scammers now know who’s rich, where they work, and how to reach them
a company can spend millions guarding the vault and still lose everything through the photocopy it left on the desk
“nvidia got hacked” is all over your timeline right now. here’s what the hackers have actually shown: nothing
a ransomware gang called the gentlemen added nvidia to its leak site today. a countdown of about 10 days. a chat id to “negotiate”. and where the stolen data should be, one word: soon
no sample files. no file list. not even which part of nvidia was supposedly hit. nvidia hasn’t confirmed anything
that’s not proof of a breach, that’s a pressure tactic
the gentlemen is real and busy, over 1,100 victims listed. but researchers at cybernews say this same group has exaggerated claims before, mislabeled victims, and reused old stolen data
maybe something happened. maybe it’s a supplier. maybe it’s nothing. right now nobody outside that gang knows
every repost of “nvidia hacked” with no evidence is free marketing for a ransomware gang
wait for the files