Everything that blocks bfcache, including Cache-Control: no-store and open connections, plus how to refresh stale data after a restore: https://t.co/41FAtNnO9M
Back button reloading the whole page? It probably missed bfcache.
Usual culprit:
addEventListener("unload", ...)
Desktop Firefox won't cache pages that use it, and Chrome deprecated it. Use pagehide instead.
Then run DevTools > Application > Back-forward Cache.
Tried it?
@ArthurLiu0725 Ideally on a schedule, since waiting for a near-miss means you're rehearsing under pressure. Even a quick drill each quarter against a staging project keeps the steps fresh.
Between Oct 20 and 22 an attacker escalated privileges in Railway's build systems and decrypted some customer env vars. At most 1.85% of workspaces were hit. If you deploy there, rotate database passwords first, then AI keys. How fast could you rotate yours today?
@_itsmeavinash Fair point. Pinning one zone only works when the audience is mostly in one place. For a wider audience I'd do what you said: send the ISO string and format it after mount, so both renders match and every visitor sees their own time.
toLocaleString() in a server-rendered component is a hydration error waiting to happen.
Server runs in UTC. Your visitor doesn't. Two different times, two different HTMLs.
Pin it:
Intl.DateTimeFormat("en-IN", { timeZone: "Asia/Kolkata" })
Seen this one before?
@ArthurLiu0725 Honestly, a written checklist beats a wiki page nobody has tried, but a rehearsed one beats both. A dry run before you actually need it is usually where you find the keys everyone forgot existed.
Up to 26,739 https://t.co/8gqRtrd4PK Desktop Cloud servers may be affected. Malware was planted on them, and customers reported unauthorized trades. If you used it, change passwords from another device and turn on 2FA. Do you keep logins saved on your servers?
PHP2Shell is a pair of critical PHP bugs that let attackers run code without logging in. Update to 8.5.12, 8.4.27, 8.3.36 or 8.2.35 and restart your workers. Can't yet? Set session.upload_progress.enabled to 0 as a stopgap. Which PHP version are you on? #PHP
@telemetrytrkr Good call. If it has to be the visitor's own timezone, formatting after mount is the cleaner route. And nice point on suppressHydrationWarning only going one level deep, that's easy to miss and it's exactly why I'd keep it on the single <time> tag.
The full list of hydration error causes in React and Next.js, with the fix I use for each, including localStorage, typeof window and bad HTML nesting: https://t.co/ovWIvD37cQ
@JD_eth@vercel@Shopify Yeah, it's wild how small that fix is compared to how often it's missing. A few lines of JSON-LD on the product page and an agent suddenly knows the real shipping cost and return rules.
@equalworld_ai Yep, B is the one. Drag-only reordering trips 2.5.7, and a simple pair of up/down buttons fixes it without touching the drag UX. Good call on the inline link exemption too, that one surprises a lot of people.
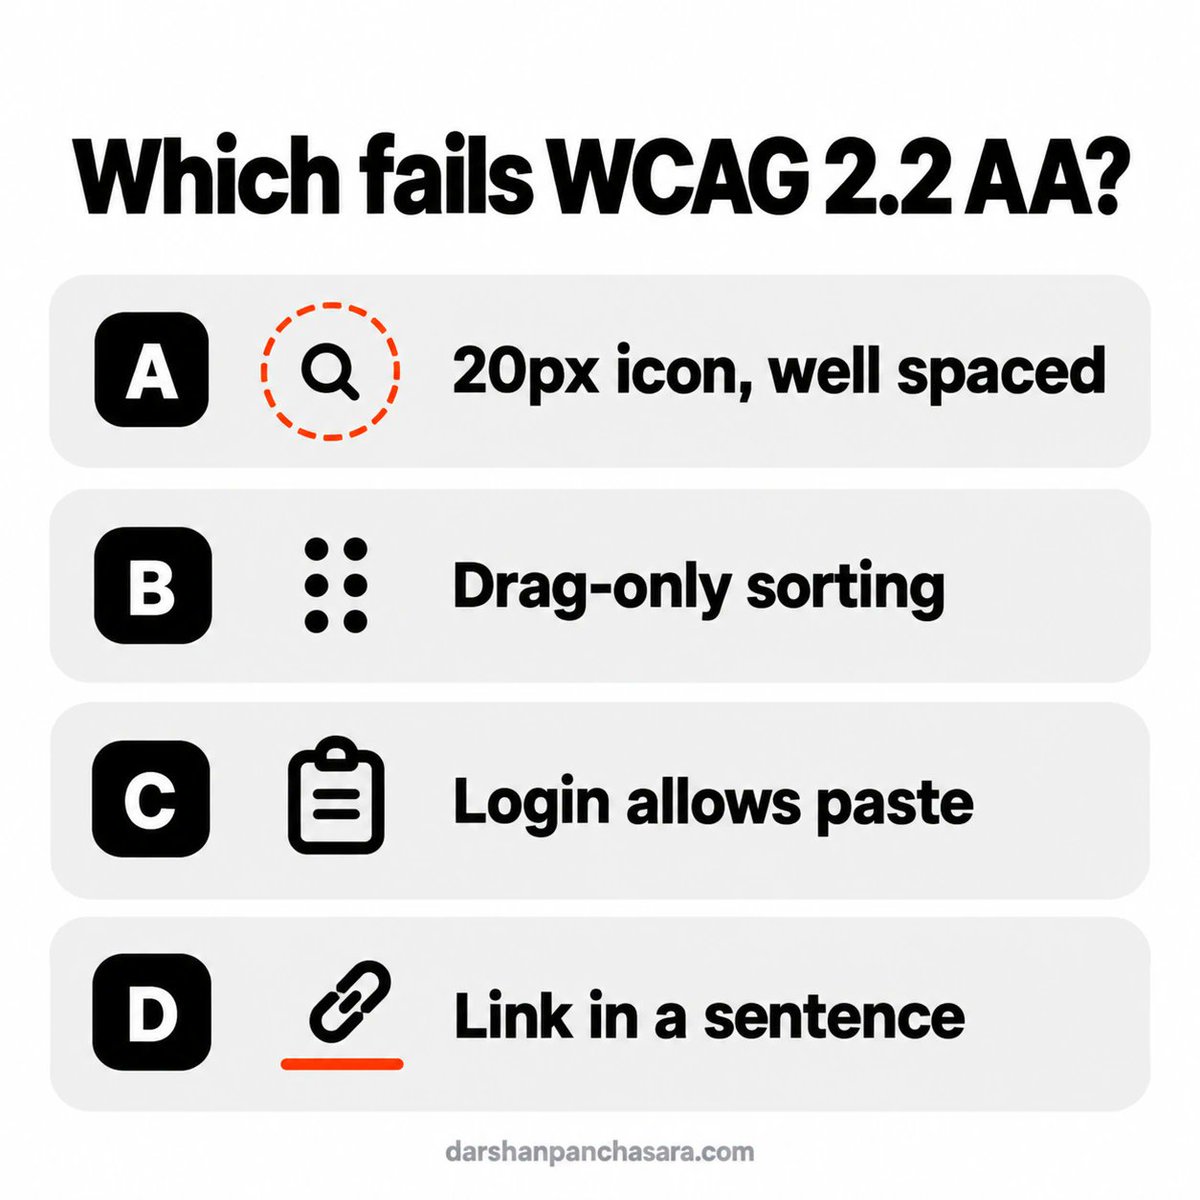
Quick WCAG 2.2 quiz. Which one fails AA?
A) 20x20 icon button, no other target within 12px of its center
B) A list you can only reorder by dragging
C) A login form that allows paste
D) A small link inside a sentence
Your answer?
@JD_eth@vercel@Shopify That tracks. A policy page behind a footer link is basically invisible to anything reading only the product page. Putting shipping and return details in structured data on the product itself feels like the cheapest fix most stores are skipping.
z.coerce.number() turns an empty string into 0.
So ?page= with nothing in it passes validation as page 0.
Add a range check after coercing:
z.coerce.number().int().min(1)
Now empty values fail instead of slipping through. Has coercion ever bitten you?