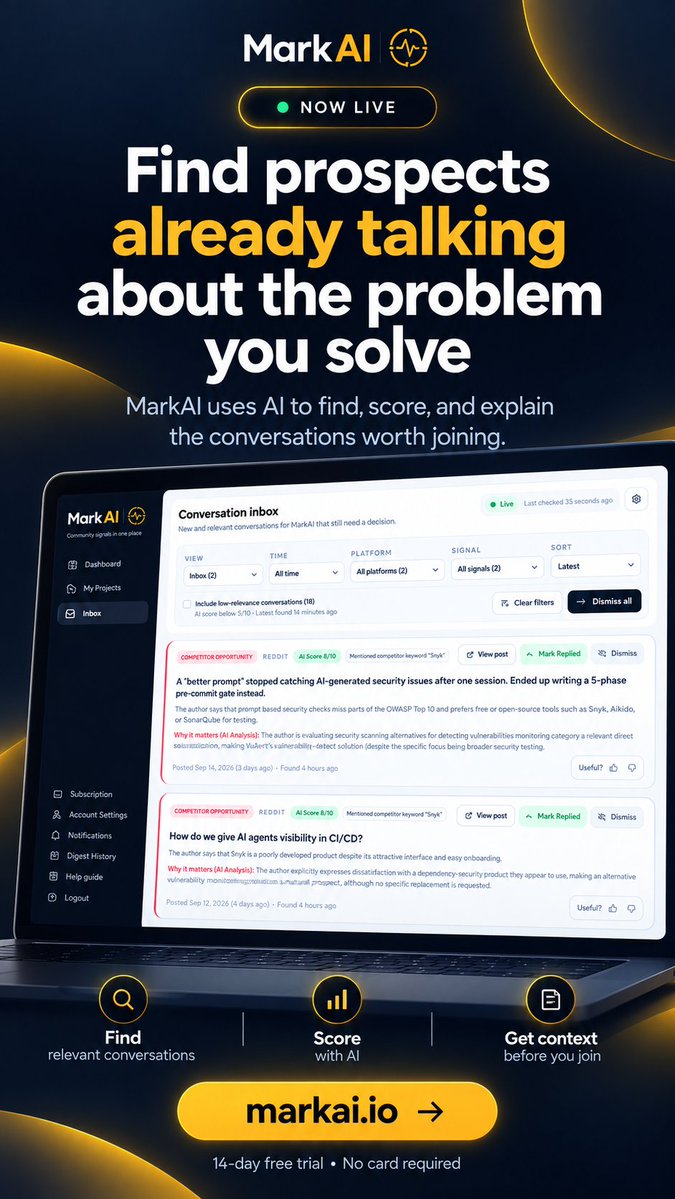
@lightsilver323 MarkAI uses AI to help you find qualified prospects already talking about the problem you solve across Reddit, Hacker News, GitHub, and other communities.
https://t.co/kfYU4YlxhR
MarkAI is live 🚀Your potential customers are already talking online about the problems your product solves.
MarkAI uses AI to find and score the conversations worth joining across Reddit, Hacker News, GitHub and more.
visit now: https://t.co/LnLI48hsFi
#startup#launch#ai#b2b
Found this hiding in Claude’s public artifacts 👀
A TOP SECRET briefing.
Redacted files.
A declassification sequence.
Nine slides.
I clicked through to see what was being hidden.
The final reveal was not what I expected
🔗 https://t.co/f2Q6xRE6qb
#ClaudeAI#AIArtifacts
The current version of Done Day is already available on iPhone and Android. This new experience is still being prepared, and I’ll share more as we get closer to release.
Android: https://t.co/qMlOxbIfI2
iPhone: https://t.co/l2BR2AxhDs
Been quiet here for a while. Recently, I’ve been working on the next evolution of Done Day.
The habit tracker will stay simple—but something new is about to make consistency feel much more personal. 🥚
Any guesses what’s inside?
#BuildInPublic#IndieDev#productivity
🚨 Exciting News! 🚨 We're now sharing the hottest vulnerability updates on our Telegram channel! Stay ahead with insights on current vulnerabilities and trends. Don't miss out – follow us here: https://t.co/MV162jm8zv
#CyberSecurity#VulnerabilityUpdates#StaySafe#TechNews
🔥🔥🔥 Attention Laravel developers: The Laravel RCE vulnerability in the cookie session driver exposes the encryption keys, allowing attackers to execute remote code on affected systems.
https://t.co/k7TtgHksMI
#laravel#php#vulnerability#opensource#sharingIsCaring#bugbounty
US Senate now mandates SBOMs for software. But how do you monitor vulnerabilities in these open-source components?
With Vulert: Monitor SBOMs, Get instant vulnerability alerts and many more.
Try our no-signup playground: https://t.co/SVcpV1bYuz
Stay safe with #Vulert#SBOM🛡️🔒
🚨After NPM, hackers have now set their sights on #Ruby Packages😱. Check out the recent identified package with malicious code: https://t.co/bS7XgAJ7IM
Visit https://t.co/SVcpV1bYuz to check if your organization might be affected, no signup required.
#Rubygem#sca#vulnerability
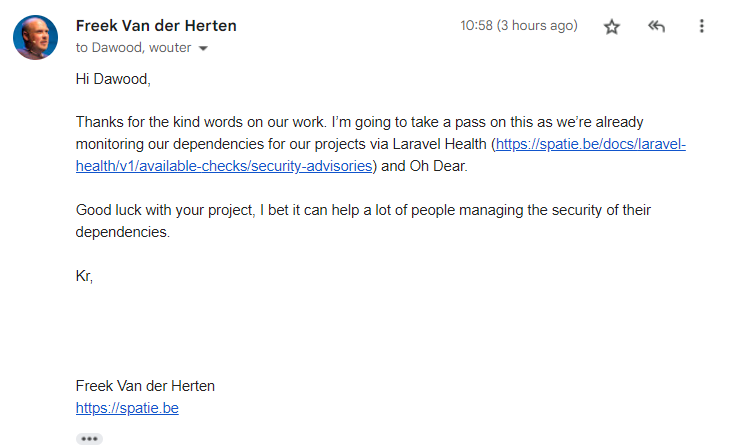
Thrilled to see @freekmurze, a pillar in the #laravel community, endorse our project, Vulert 🎉. For those unaware, Vulert monitors & alerts about #opensource#vulnerabilities in real-time, using only a lock file! 👏
Thanks Freek, for your encouraging words. 🙏 It's validation.
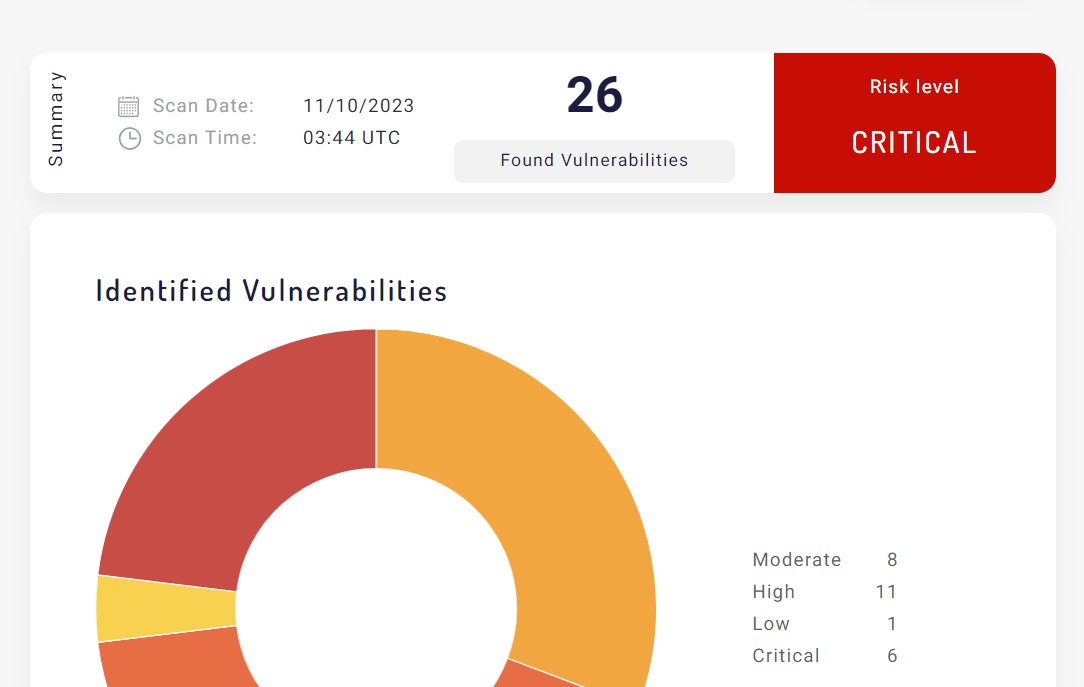
🚨Attention!🚨 Vulert discovered over 30 vulnerable dependencies in enzyme-to-json npm package with 840k+ weekly downloads. Secure your code by reviewing the vulnerabilities here: https://t.co/pjZ2zZ6zyE #cybersecurity#npm#vulnerability#opensource#bugbounty#javascript