before mainnet, we tried to break our own solana program.
3 scans with @CertiK AI Auditor, fixes shipped between every run:
25 findings, 1 critical
24 findings, 0 critical
19 findings, 0 critical
here's what it caught and what we changed 👇
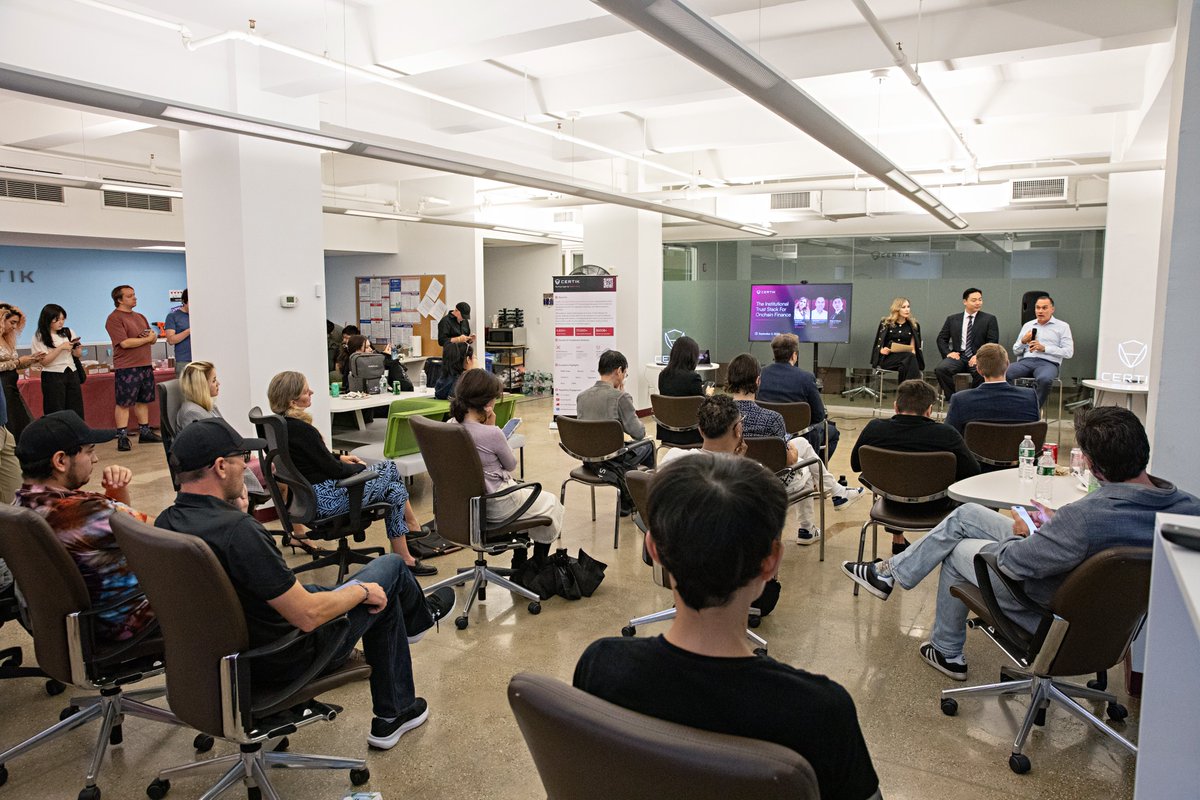
We're only a week away from the best event in NYC! This time, we are bringing @IBM and @midnightfdn to join us on the panel together with @CertiK's CEO @RonghuiGu.
Don't miss your chance to meet the most interesting people in real life, enjoy some delicious food & drinks, and take home some of the coolest CertiK swag!
RSVP now: https://t.co/csu7rwmFLX
Aptos is rebuilding its Move execution engine with MonoMove.
An initial note about a few things worth comparing with the existing VM: how it executes bytecode, represents values, enforces checks, and charges gas. (According to Oct 6, 2026 source snapshot.)
https://t.co/MoHX7BC6VB
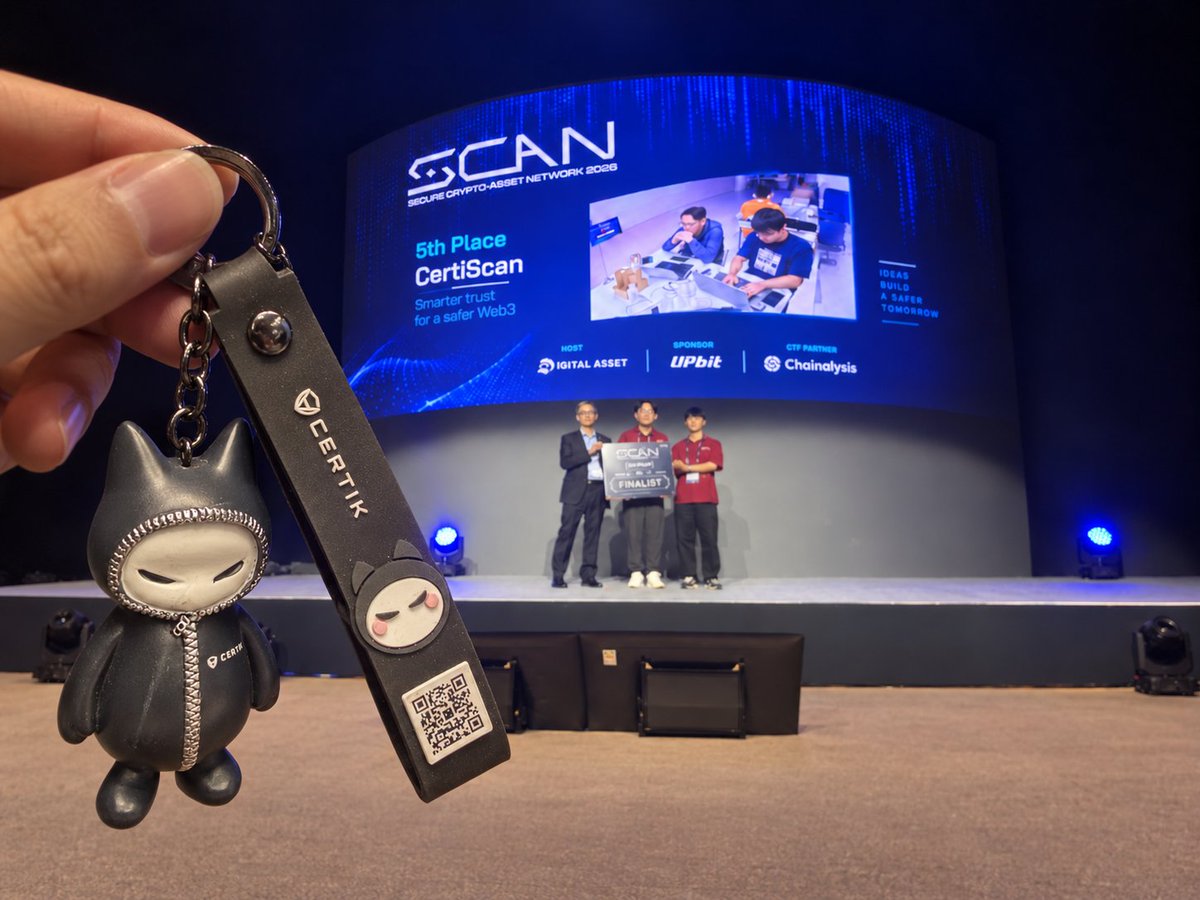
Proud to share that our team, CertiScan, representing @CertiK , finished in 5th place🏆
Thanks to the organizers, fellow participants, and our teammates for making this a great experience
Huge thanks to the codex, gpt 6 sol, gpt 5.6 sol, claude opus and Tibo reset🤣🤣
no thanks to the deepseek😭
#SCAN2026
web3.js 3.0.0 keeps the familiar API, but two changes matter when upgrading from V1(like 1.98.4):
1. Default commitment. With none set, v3 sends confirmed where v1 omits it.
2. Response checks. Of six injected malformed replies, v1 rejected all six; v3 returned four.
Repro below.
Proud to have discovered and responsibly disclosed this bug in Zcash using our Chain Scan tool.
Thank you to the Zcash Foundation for the recognition.
Always great to see security research turn into real-world impact. 🛡️
If a protocol has been audited, how does it still get hacked? That’s the billion dollar question we’re asking @CertiK tomorrow.
We’ll dive deep into how attackers find opportunities, where protocols remain exposed after deployment, and what real security looks like today.
Join us 🎙️ https://t.co/9cz8ARwTlU
A big reason I joined @CertiK is the chance to work more closely with fellow security researchers I respect.
We’re already working on initiatives to get more involved in the security community AND bring more of the community into what we’re cooking up.
If you care about web3 security and don’t mind a little alpha on the side 😉 drop a comment and I’ll shoot you a DM.
Really excited about what we’ve got coming.
We’re excited to welcome Alejandro Munoz (@unsafe_call) to CertiK! 🛡️
Alejandro brings deep expertise in smart contract security, vulnerability research, and incident response, with extensive experience tackling some of Web3’s most complex security challenges.
Welcome to the team, Alejandro! 👋
@abdoulrauf_jn@CertiK@CertiKCommunity Much love bro ❤️ You’ve been part of the AI Auditor journey every step of the way. Your feedback keeps pushing us to build better. We keep shipping
Thank you to everyone who joined us at @CertiK’s NYC headquarters! And a huge thank you to @XDC_USA and @TravisJohn for joining @magnusweb3 and me for a great panel discussion.
I’m already looking forward to bringing everyone together again for more events like this 😎
Sorry for being quiet recently. I have been head down in CTO mode in the last month - writing both code and whitepapers. I think I figured something out. Hope to share more broadly in the near future.
Sad to see Full Sail sunset. After reviewing the on-chain transactions and deployed code, the likely root cause appears to be in Switchboard’s Move implementation.
Anyone could create Oracle objects inside the production guardian queue. During attestation, the contract checked the target oracle’s expiry instead of the guardian’s, while an empty guardian public key caused the signature comparison to pass vacuously.
The attacker created three fake guardians, satisfied the quorum, and installed a signer they controlled on a production oracle. They then submitted prices roughly 100× below market, deposited into the affected vaults, restored the prices, and withdrew more than they contributed.
Switchboard appears to be the upstream technical root cause, but downstream controls amplified the impact: FullSail’s vault deviation check failed open after shares had already been created, while Virtue lacked independent price-magnitude and source-diversity checks.
If you integrate Switchboard’s Move deployments, this is a good time to reassess your assumptions, add independent oracle bounds, and verify the deployed contracts—not just the SDK. #SuiNetwork
Audit 101 – this Thursday!
This Thursday at 5PM (UTC+3), we’re running a Space with @CertiK as part of our Acceleraptor program
@LCecconn, BD Lead for LATAM at CertiK, and @de3p4c1to, Audit Partner at CertiK, will break down everything you need to know about smart contract audits
We’ll cover:
• Who needs an audit and at what stage
• What auditors actually check
• How to prepare your product and code
• What an audit costs
• How to choose a solid auditor
• Alternatives for projects with smaller budgets
• Custom CertiK packages for Ukrainian developers
Join us this Thursday for Audit 101!
Register via link below 👇
The CertiK Hunt community is growing. 🎯
Meet the latest security researchers invited to CertiK Hunt, bringing new expertise and experience to the platform.
More Hunters. More programs. More to come.
Stay tuned.
BootROM → root → lock-screen PIN.
We enter BROM mode, load a patched preloader, gain root, extract the lock credential, recover the 6-digit PIN offline, and use it to unlock the phone.
Full PoC ↓