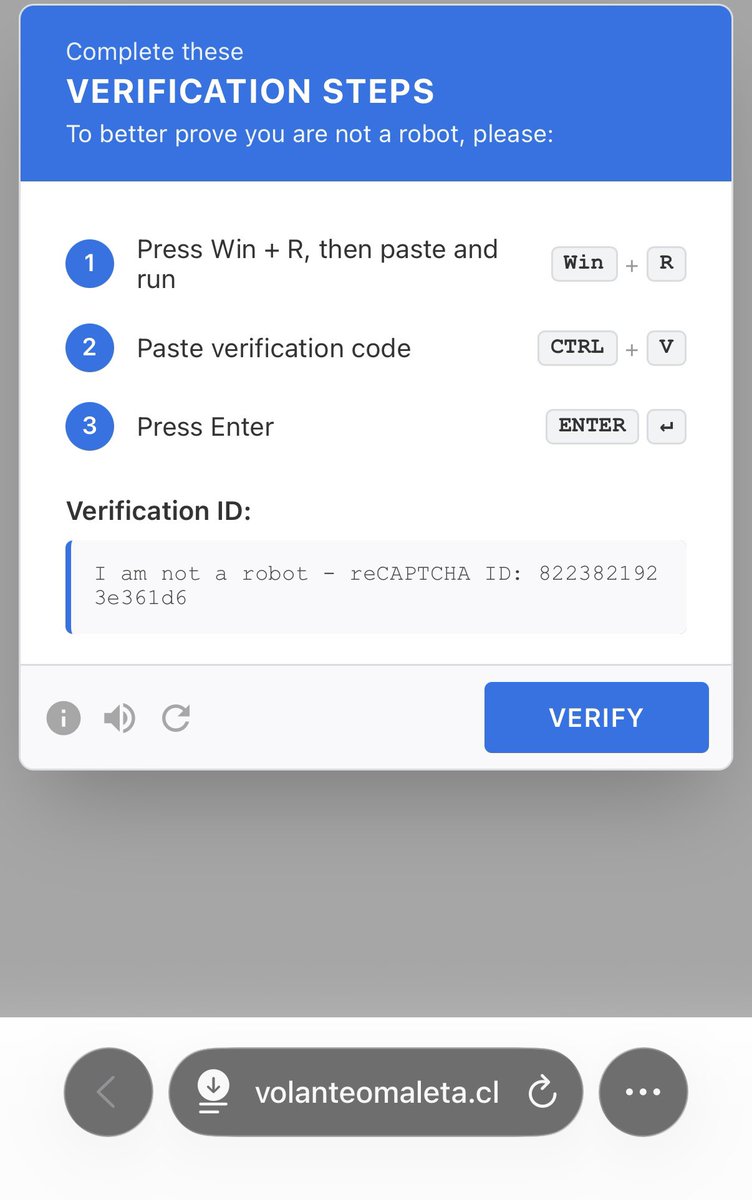
@LaGrevia E se vi dicessi che io, nato analogico, nell’era dei nativi digitali mi ritrovo ancora a spiegare a ragazzi e adolescenti come funziona Internet?
E non parliamo nemmeno di cybersecurity, privacy e rischi della rete…
Per dire, eh. 🙃
@ShitSecure This bug reminds me of a “sensitive” web application I found about 20 years ago: authorization enforced entirely on the client side.
if (isAdmin === true) { doDirtyThings(); }
Some things really never change. 😄
In July, Microsoft fixed CVE-2026-50343, a Windows privilege escalation bug reported by Calif and 9 others, dubbed “Dark Elevator”.
But was it really fixed?
Ask @tiraniddo
https://t.co/4YgBY2N2KZ
Been digging deep into the Windows Endpoint Security Platform (WESP) in Win11 25H2, definitely one of the most fascinating security features Microsoft has built in a while.
The concept is neat: compile rules to decision graphs in user mode, hand them to wesp.sys, and let the kernel evaluate them in-path while telemetry streams asynchronously in the background.
I did an AI-assisted reverse engineering dive into the whole stack (wesp.sys, espclient.dll, and wesp_elam.sys), documented the wire protocols, disposition tables, and the enforcement gate, and built esptool, a research harness with 118 XML rule docs so anyone can test live telemetry and in-kernel blocking.
Repo: https://t.co/ZPYPHfmCP4
Tech doc: https://t.co/P2s4geHEsI
Thanks to @yarden_shafir for putting this on my radar
@lastknight@Revolut Resta valido anche il metodo più “arcaico”: davanti anche al minimo dubbio, si alza il telefono, si chiama direttamente l’ente o l’ufficio interessato usando un contatto verificato e si chiede conferma 😅
AI may eventually become the new Cold War: everyone keeps building more powerful systems because they can’t afford to let the other side get ahead. Chip manufacturers may become the equivalent of uranium supplier controlling access to the resource that makes the race possible
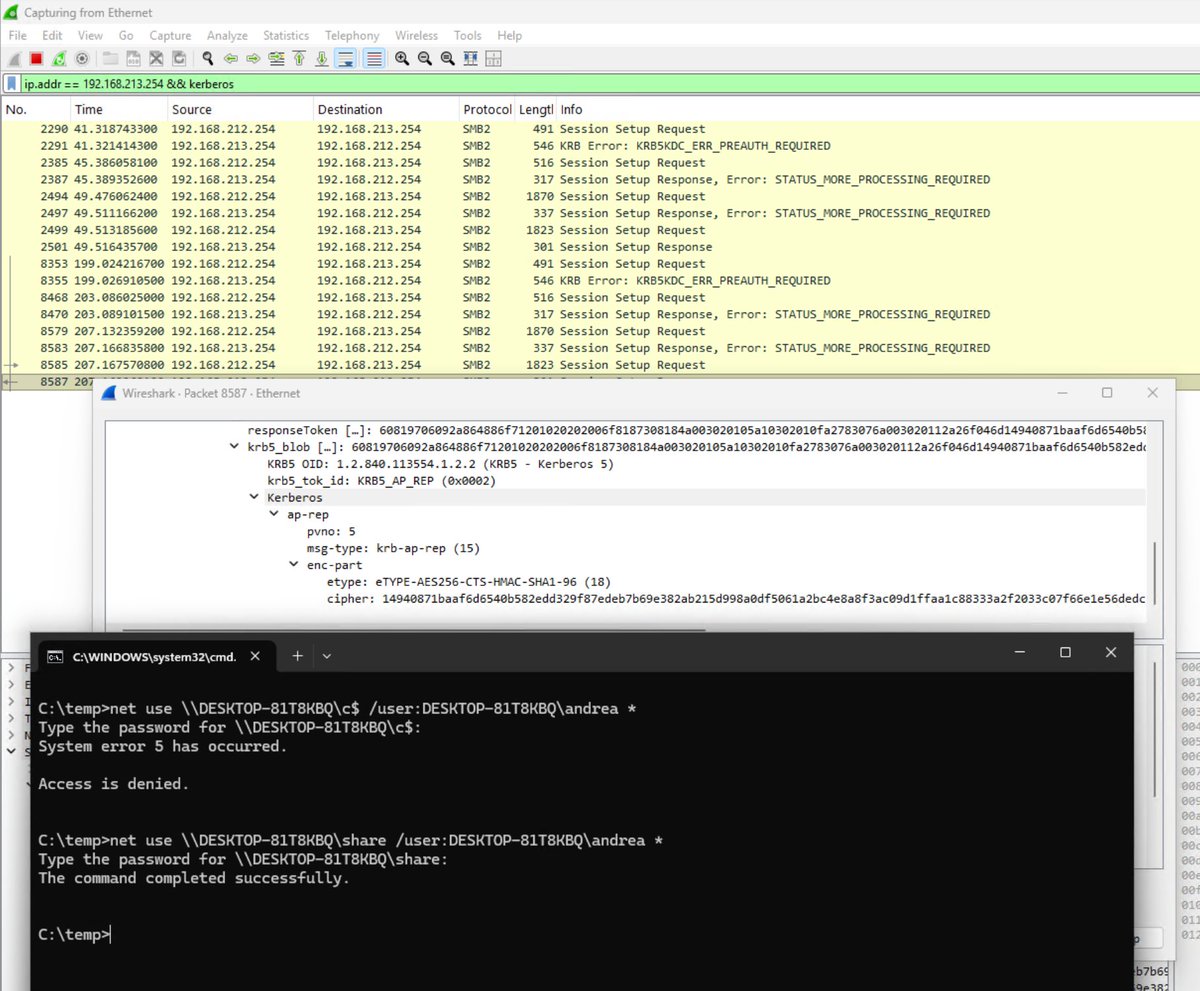
@merill Agreed on moving toward modern auth, but “modern” doesn’t automatically mean “more secure.” The right approach is migration and secure configuration of all protocols , also of the legacy protocols (yes it is possible) that are still widely used.