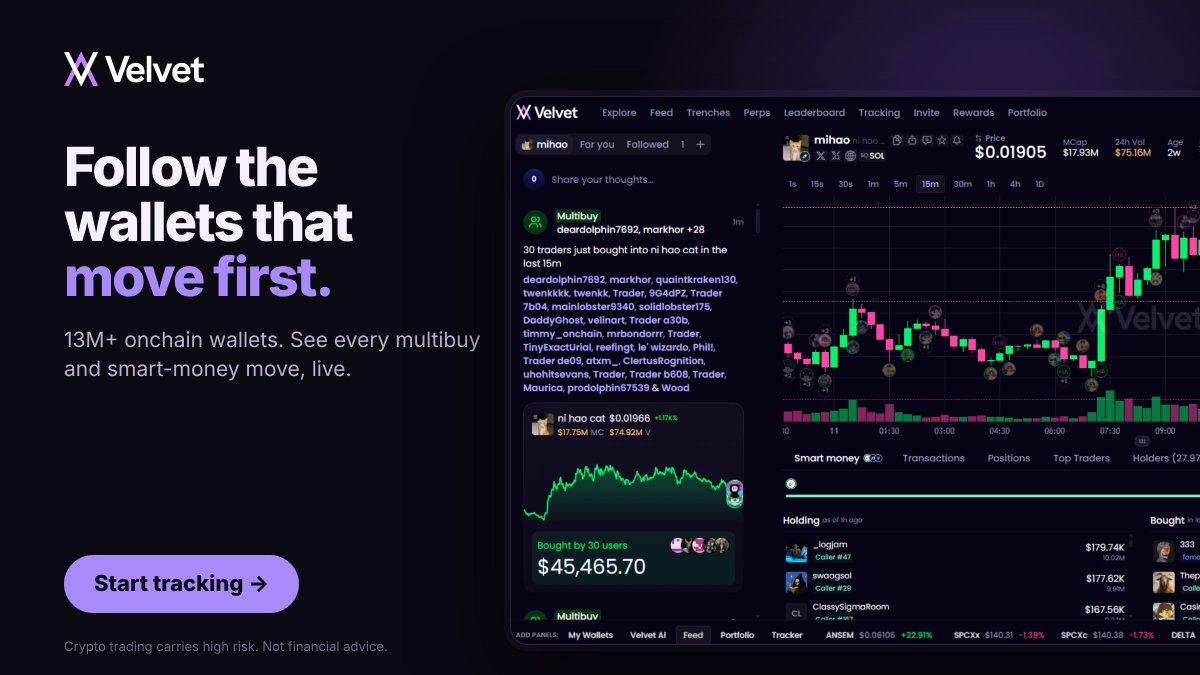
Smart money doesn't tweet first... it buys first
Velvet X shows you which trending tokens the top wallets are buying with data from over 10m wallets (including all on FOMO and Pump) and then lets you trade it in one click
Smart money doesn't tweet first... it buys first
Velvet X shows you which trending tokens the top wallets are buying with data from over 10m wallets (including all on FOMO and Pump) and then lets you trade it in one click
If a token doesn't even have a Twitter or website, why is it on your screen?
VelvetX now lets you filter the Trenches by X account, Telegram, and website
Flip the toggles and the zero-effort launches disappear
Avoid the rugs... before they rug
London, we’re coming
Velvet will be at Solana Breakpoint, and we’re opening the doors to the Velvet Traders House for top traders & KOLs, right near the main venue
📅 Nov 14–17
Comment if you’ll be in town and want an invite👇
London, we’re coming
Velvet will be at Solana Breakpoint, and we’re opening the doors to the Velvet Traders House for top traders & KOLs, right near the main venue
📅 Nov 14–17
Comment if you’ll be in town and want an invite👇
Trade a memecoin with its own Trading Bot & earn rewards
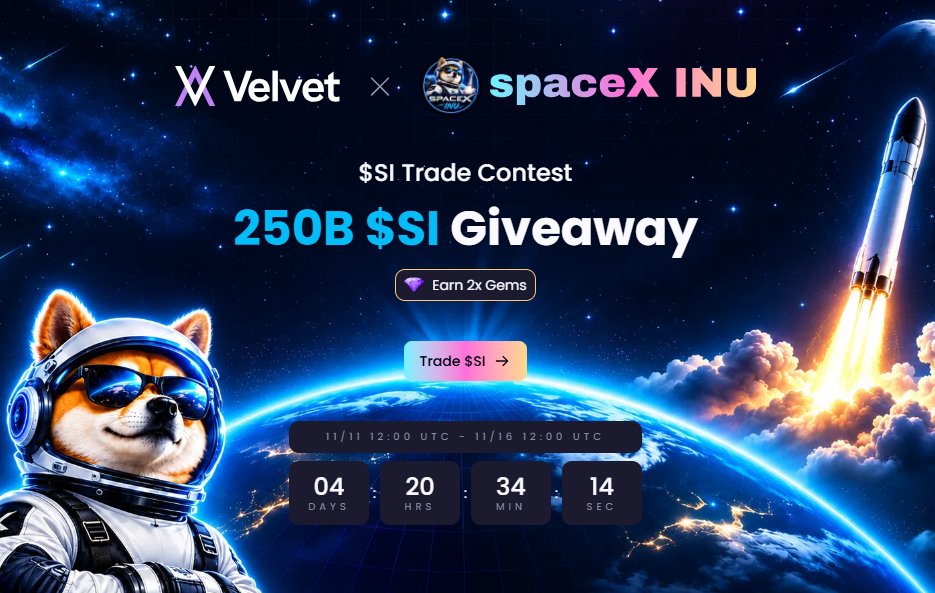
The $SI @FanSpaceXInu Trading Competition is LIVE on VelvetX
With 250 BILLION tokens up for grabs on BNB Chain:
- 225B $SI tokens distributed based on Trading Volume
- 25B $SI tokens distributed to the top 50 veVELVET stakers
Starts: November 11 at 12:00 UTC
Ends: November 16 at 12:00 UTC
Trade $SI. Climb the leaderboard. Compete for your share.
🚨 SlowMist TI Alert: iOS sandbox escape 0day PoC “worse_query” disclosed 🚨
A public PoC for a sandbox escape 0day, worse_query, targets iOS 26.0–26.7.2 and iOS 27.2. It is the successor to bad_query. 📱
⚠️ This is a container sandbox escape, not a jailbreak. It breaks the assumption that apps can’t see each other: a malicious app that successfully exploits it can reach system paths and read or modify other apps’ data.
💸 The bug does not steal assets by itself. The real risk starts when a user installs an app from an untrusted source, such as a sideloaded IPA. If a wallet stores its seed phrase, keystore or WebView cache in plaintext locally, a malicious app could read it.
🛡️ Recommendations:
🔸 Don’t install IPAs or apps from unknown sources
🔸 Keep iOS up to date and install Apple’s fix as soon as one is released
🔸 Wallet developers: don’t store sensitive data in plaintext locally
🔸 If you installed an untrusted app on a device holding wallets, treat it as risky and consider moving assets to a new wallet created on a clean device
🔗 https://t.co/sIP4hX85TR