The flaws can allow unauthenticated remote code execution on vulnerable systems. That means an attacker may be able to run malicious code without first logging in.
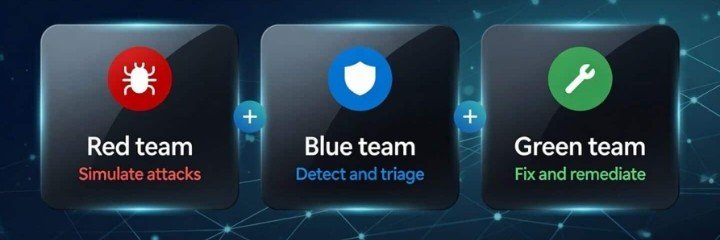
The discovery involved AI-assisted security research. The PHP Foundation and collaborating security researchers coordinated the fixes, and the Foundation acknowledged that a delay in addressing an earlier indication of one flaw represented a structural failure