I have joined @spearbit as a Full time Security Researcher !
My journey started with Spearbit, so it always made sense to get more involved with the company!
I will continue with public security contributions, as much as I can
Anon, you are gonna see a flurry of security content from me !
Let's secure web3 ☺️
Devcon 9 is coming to Lisbon! 🇵🇹
October 11–13, 2027
Building on Mumbai, we're bringing Ethereum's builders together with more friends and allies working toward a freer, more open internet.
I'll be speaking at DSS alongside @Sabanaku77!
We'll be talking about Web3 Security Monitoring Internals, from on-chain threat detection to incident response.
See you all at DSS and Devcon!
How do you guys offramp your stablecoins?
Are you still doing VDA sales, P2P, CDM or cash settlements? Your bank account could get lien/freeze or heavy penalties due to illegal money trails.
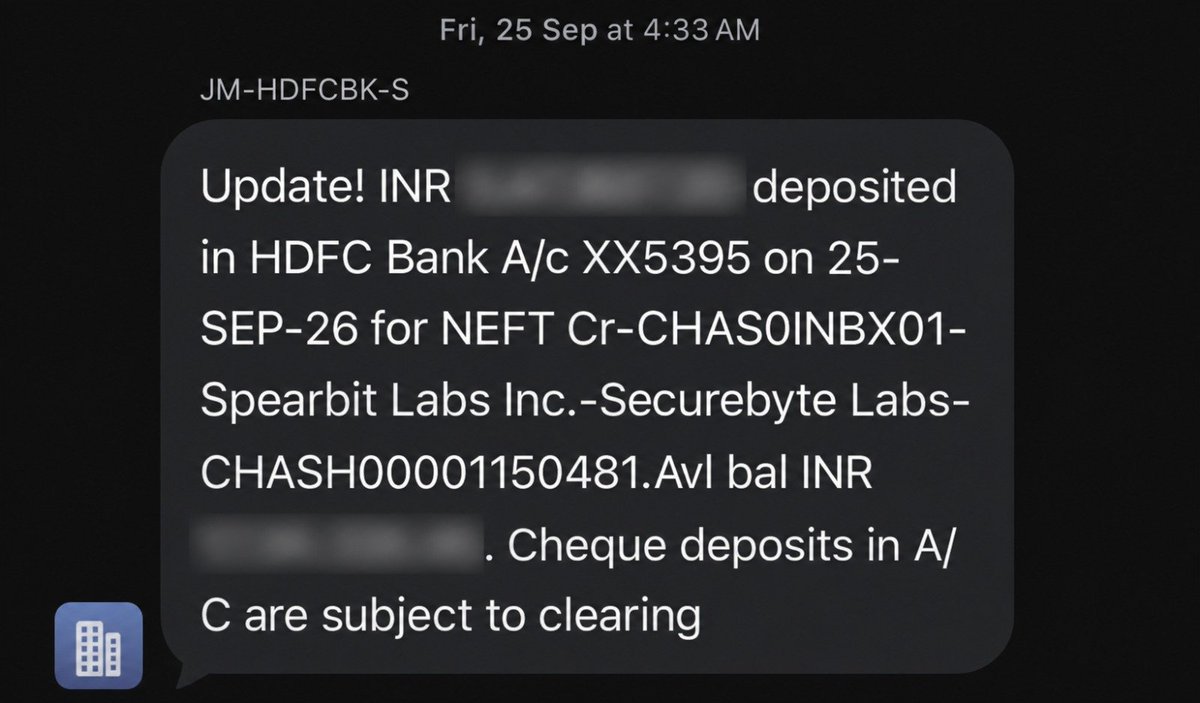
I’ve been using @PayZoll for the past 2 months to offramp my stablecoin salary in INR along with a FIRA certificate through JP Morgan Chase and my bank statement reflects my company name, Spearbit Labs Inc.
Really like what the @PayZoll team has built. Tried other platforms, but getting the right purpose codes and my company name on the bank statement was always a challenge. PayZoll solved these pain points.
I’d recommend checking out https://t.co/Y2ugJrC0bK , if you receive stablecoins/fiat through salaries, bug bounties, or anywhere
DM @ItachiOnChain or @PayZoll if you need help getting started
This Dussehra, a better way to turn stablecoins into INR is here. 🇮🇳
USDC to INR settlements are now live on PayZoll.
Get started → https://t.co/MRhD61FS2y
We're all fine if Jio gets the first-mover advantage in satellite internet.
The data stack must be in India. There shouldn’t be any question around that.
After the H-1B issues, it's better we have our own backs. A capitalist from our country is better than an outsider any day.
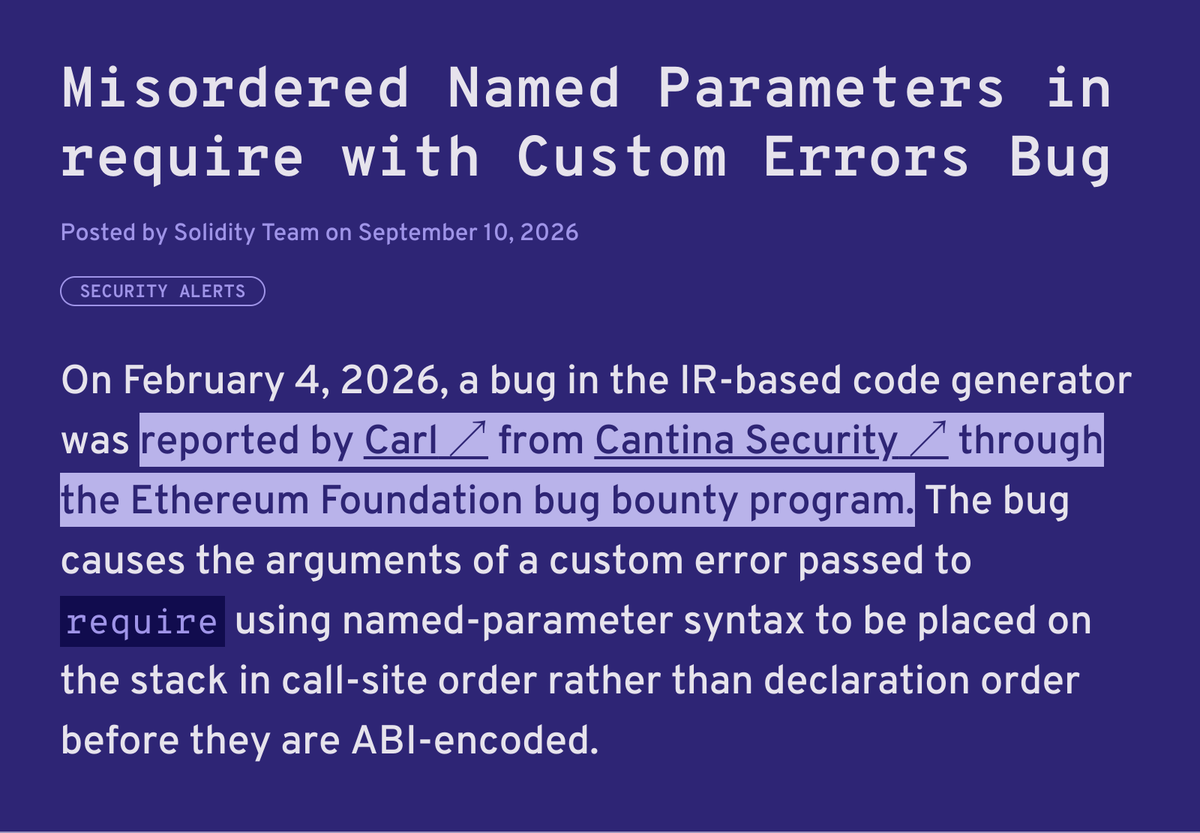
Apex, our autonomous bug hunter, found a bug in the Solidity compiler that got fixed in this release.
Congrats to @popular_12345, who is building Apex and reported the bug through the @ethereum bug bounty program.
We constantly test new recipes and improvements on real software. Finds like this help us make Apex better.
We spent years finding vulnerabilities before attackers did. That was the easy part.
Teams already know what's broken. Nobody has the bandwidth to close it.
Today we raised $16.5M to make Cantina the security workforce for your security workforce. https://t.co/GWF2OICZsr