Blockchain consultant & full-stack builder | Founder @KochainTech | Co-Founder @RTindex | Ethereum • Solana | Building in Public 🛠️ | Tweets are personal
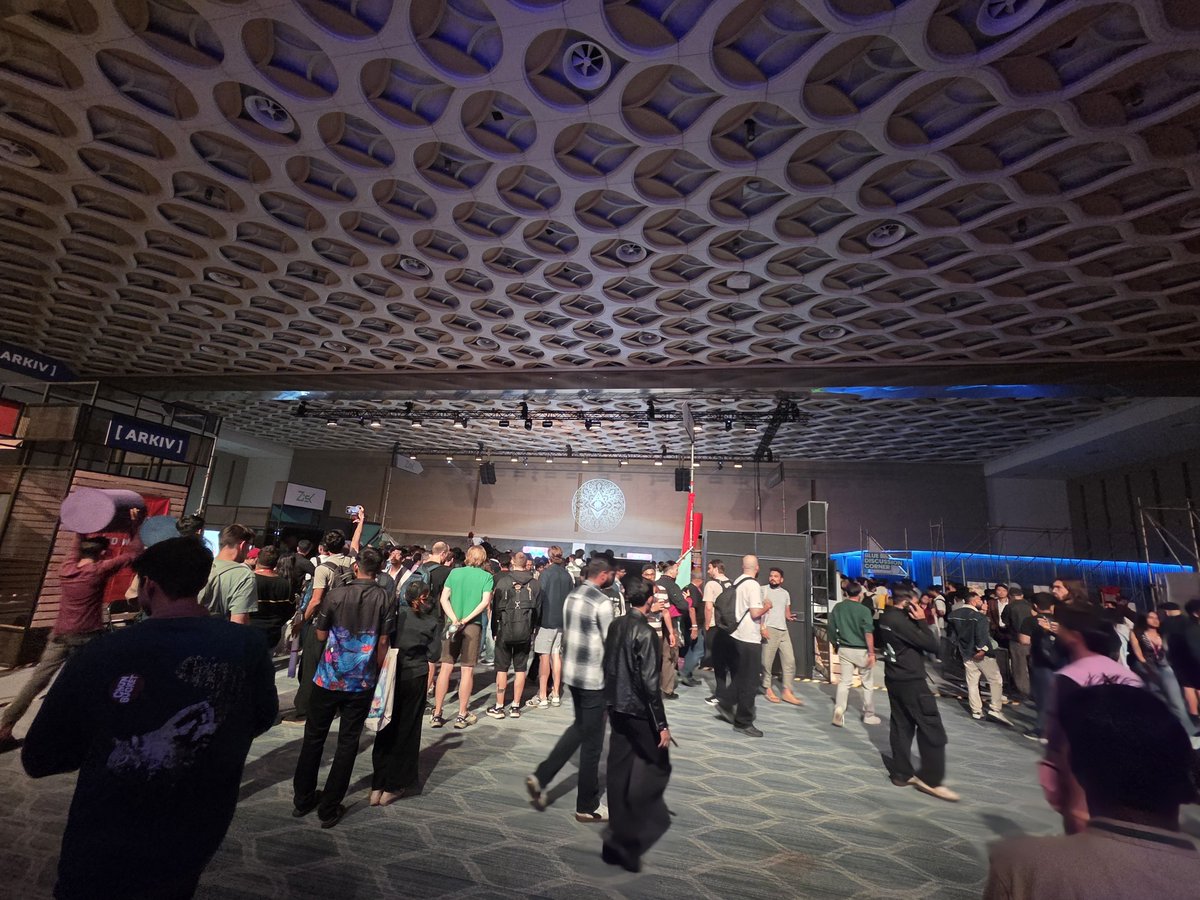
That's a wrap on @EFDevcon 🇮🇳
Binance's post-mortem says its $6.3B hack began with a fake job interview and a coding assignment on a work laptop.
At Devcon, security and agent builders said it too: attacks are moving from code to people.
More soon from @RTindex and @Payaion .
Final day at #Devcon8@EFDevcon 🇮🇳
4 days with security teams, agent builders and Base. Clear signal: agents need to pay for files, devs need to check code before running it.
RTIdx → https://t.co/rOUG25OrSc
Payaion → https://t.co/ZFl7u2evgO
Still here today. DM to meet.
Day 3 at #Devcon8@EFDevcon@ethereumfndn 🇮🇳
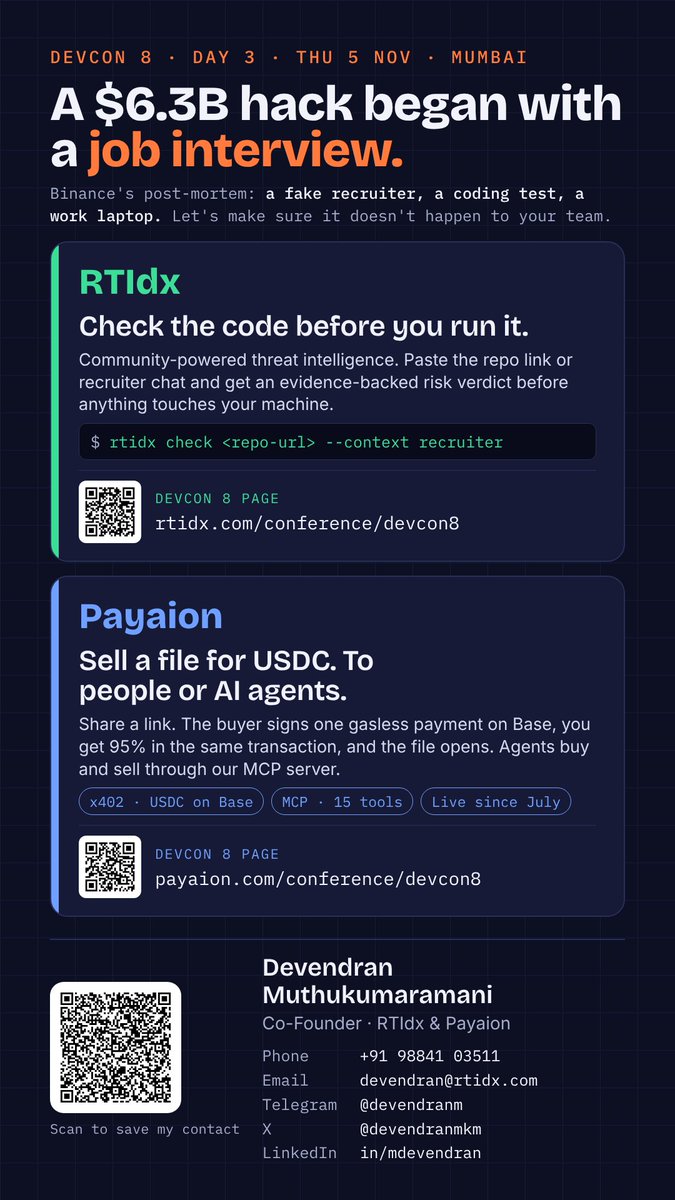
A $6.3B hack began with a job interview. Check the code before you run it → https://t.co/rOUG25OrSc
Sell files for USDC on Base, to people or agents. One gasless signature, 95% to the seller → https://t.co/ZFl7u2evgO
DM to meet.
Day 2 at #Devcon8.
@Payaion : send a file, get paid, only the right person can open it. USDC on Base, for people and AI agents.
@RTindex: check the code before you run it. Stops fake-recruiter attacks on devs.
At Devcon? Let's talk. Links below.
Day 1 at Devcon 8, Mumbai. That's a wrap.
An afternoon at the Security Hub with people working on incident response, threat intel and security funding. One idea kept coming up: catch attacks on developers before they land. That's what we're building with @RTindex .
Good to catch up with old friends from the ecosystem too.
Tomorrow: agent payments and private file sharing with @Payaion . At Devcon? DM and we would love to connect with you.
#Devcon8 #Ethereum #Web3Security #AIAgents
Heading to #Devcon8 in Mumbai, 3–6 Nov, for @RTindex and @Payaion .
RTIdx: check a recruiter's repo or take-home test before you run it.
Payaion: files only your recipients can open, or sell them for USDC on Base, to people or AI agents.
If you're building in developer security, threat intel, agent payments, identity or private file sharing, or funding work like this, let's meet. Message me here or on Telegram (@devendranm).
#Devcon8 #Ethereum #Web3Security #AIAgents
@ProgrammerSmart I faced two of these myself, so I know the feeling. If you still have the DM or recruiter profile, please log it at https://t.co/wwZB7MZ2tF (I’m part of the team there). We track these personas so the next dev can check before the call. Happy to help, details stay anonymised.
Try these recovery steps;
1. Move funds from any wallet that was on that laptop to a fresh wallet, from another device
2. Rotate GitHub, npm, cloud keys and revoke tokens
3. Log out all sessions, change browser-saved passwords
4. Wipe the machine, deleting the folder is not enough
The file vanishing is normal. They clean up after.
@cz_binance@mikebelshe The fake profiles are the bigger risk for job seekers. A “Binance recruiter” with a take-home task is how many devs get hit. Would Binance consider a simple way for candidates to verify if a recruiter really works there?
@mikebelshe Feel for him. For devops folks the risk is even bigger, because your laptop holds the keys to production. One simple rule: no interview task or “quick test repo” should ever run on a machine with prod access. Throwaway VM, every time.
@mikebelshe@LinkedIn Agree. And it’s not only the org chart. The payload usually arrives as a take-home repo in a fake interview. Got one myself: real code ended at line 46, backdoor at line 258. Hiding profiles protects the company. Devs still need to check repos before running them.
🚨 THE INTERNET BROKE TODAY 🚨
Oct 21, 2026 will go down in history
1. eMudhra : Private key was literally "4". 8 keys forged ANY website for 17 months. 60M+ certs at risk.
2. SBI CONFIRMED. 3,897 customers' mobile, DOB, address + loan data found on dark web.
3. Rajasthan Police 🇮🇳ALLEGED hack. Group claims 70,000 identity records + 59,460 numbers for sale. Unverified.
4. php2shell [9.2] Unauth RCE in PHP. 70% of the web. WordPress, Drupal, Laravel. CISA: Patch or GO OFFLINE.
5. GitLab [10.0/10] PERFECT SCORE. Unauth RCE, no login needed.
6. Node.js [CVE-2026-111497] Brotli decoder RCE + TLS bypass. 10 CVEs patched today. Also blocked eMudhra.
7. Railway BREACHED TODAY. Env variables decrypted. Your API keys & DB passwords exposed. Rotate all.
8. OpenCode BREACHED. OpenAI, Anthropic, Google API keys exposed for Console users. Distillation attack. Bills run up in $$$$.
9. LiteLLM PyPI v1.107.0 was MALWARE today morning. Steals credentials + backdoor.
10. Plex2Shell ACTIVELY EXPLOITED. Hackers installing cryptominers LIVE. CISA KEV, deadline Oct 23.
AI found the bugs. AI is exploiting them. Humans can't patch fast enough.
Patch. Rotate. Revoke. Update.
RT to save someone's server ♻️
#CyberSecurity #DataBreach #India #php2shell
Real talk — I almost lost my wallet to a fake "Blockchain PM" interview a while back. Stolen identity, a cloned GitHub, a MetaMask connect request mid-call. Got lucky — empty wallet, and I happened to check the console.
Since then I've been part of the team behind @RTindex , built within @thedefdone . This week we shipped a free CLI that checks a recruiter's repo before you run it.
Anyone else been targeted by one of these? Tell us about it.
“Your files are encrypted.” Every transfer service says it.
Ask who holds the key and the room goes quiet. This week we made it so we can’t answer that question either.
Private Link locks your file in your browser. What reaches us is encrypted message - not the file, not even its name. We couldn’t open it if a judge asked nicely.
Then it leaves us too, onto @WalrusProtocol : decentralized storage on @SuiNetwork . Not our bucket, not one company’s terms that change on a Tuesday. The nodes holding your file are in the same boat we are.
They’ve got encrypted content. No account. No email. No wallet. Nobody can ask us who sent a file, because we never asked.
Free: 100 MB, no signup. Wallet: 500 MB. Pro: 1 GB a file and 20 GB of storage, $10/month through September - half price, because nobody has bought it yet and we’d rather find out what it’s worth than guess. (Private links cap at 500 MB whatever you’re on. Browsers have opinions.)
We’re small, we ship weekly, and what we build next is decided by whoever tells us something worth building. Right now we’re staring at agents. So, a real question: if you run agents - what’s the one thing you’d want an agent to do with a file that nothing does properly today? Reply. We read all of them