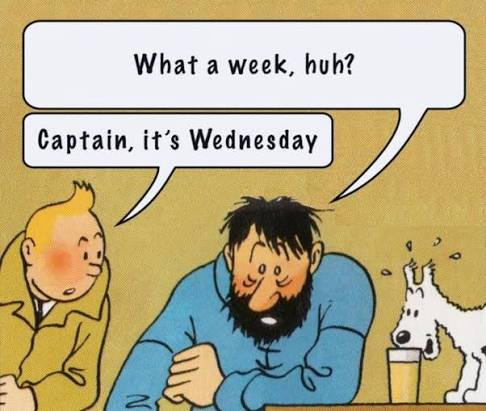
working in cybersecurity nowadays:
> wake up
> read "new critical vuln just dropped"
> summon dev and SRE in the incident channel
> patch, scan, rotate secrets, redeploy
> check logs to make sure you are not already cooked
> take a deep breath and go to sleep
> wake up
> read "new critical vuln just dropped"...
WELCOME TO THE AI ERA
Introducing nginx-poolslip, a fresh RCE for the the latest nginx release 1.31.0.
nginx-rift has been patched, but our security agent Vega has found a new 0 day.
We will release the full technical writeup with ASLR bypass 30 days after the patch on https://t.co/LAhOC5UHrp.
El año pasado quedamos 29 de 34. Este año, 39 de 42.
Quizá va siendo hora de dejar de encargar el entrenamiento del equipo a macroempresas o al influencer de turno, y de empezar a elegir a los participantes con criterios claros y a preparar la competición en serio, no un mes antes. Si queréis buenos resultados, tenéis que dejar de depender del talento individual que os carrileó años atrás y empezar a competir de verdad. ¿No habéis aprendido nada de cómo lo hacen otros países?
Un poco de amor propio, por favor.
🏁 Finaliza la participación de la Selección Española en el #ECSC2026.
Gracias a los diez integrantes por su esfuerzo, dedicación y compromiso durante toda la competición, y por representar a España en #Bochum . 🇪🇸
En español me ha quedado gratamente sorprendido con el contenido de @gorkaelbochi. Y sin duda, aunque no esté directamente relacionado con seguridad, no puedo dejar sin mencionar aquí a mi camarada @achetronic.
Being technically great and being a great communicator rarely come together.
Most people are strong in one and weak in the other, which makes people who nail both genuinely rare.
That's why I rate @LiveOverflow and @NahamSec so much. Real depth, explained in a way that actually sticks. That combo is way harder to find than people think.
@juanca_mnz Na, si hoy día o tienes un patrimonio inicial grande, o está difícil. Pero como antiguamente te daban hipotecas de regalos con los bollicaos y los pisos valían 2 duros... Pues eso.
today we're releasing apex-flash-1, our first open-weights model for security research post-trained on real vulnerabilities we found and got paid for.
we are also releasing the abliterated variant for researchers who want fewer refusals in their own authorized workflows.
how we built it: https://t.co/sSIV6qKFGt
"La ciberseguridad es uno de esos trabajos que solo se hacen visibles cuando algo falla".
Gracias a Manuel Collado y a La Vanguardia por la entrevista.
https://t.co/IMomkclWmV
This finding takes 10 seconds to spot and can pay out hundreds of dollars.
An exposed Google Gemini API key. Used to be "informative, no impact." Not anymore.
The reason: that same key can run Gemini prompts on someone else's bill. It's not just exposed data anymore. It's free AI spend for whoever finds it. Programs are paying for that now.