langflow. bun. ant-design. nuxt. vue. mermaid. pnpm. trpc.
Over 600,000 GitHub stars between them, and CodeRabbit reviews it all, for free.
Next stop: more than $10M into OSS over the next year, counted at what it costs us.
Heres how and why 👇
🚨 A public Telerik UI PoC chains a padding oracle into unauthenticated RCE.
TantoSec’s exploit for RadAsyncUpload forges encrypted state and loads a DLL, but only on specific non-default configurations.
Inside the chain → https://t.co/tmvIIbR3Ns
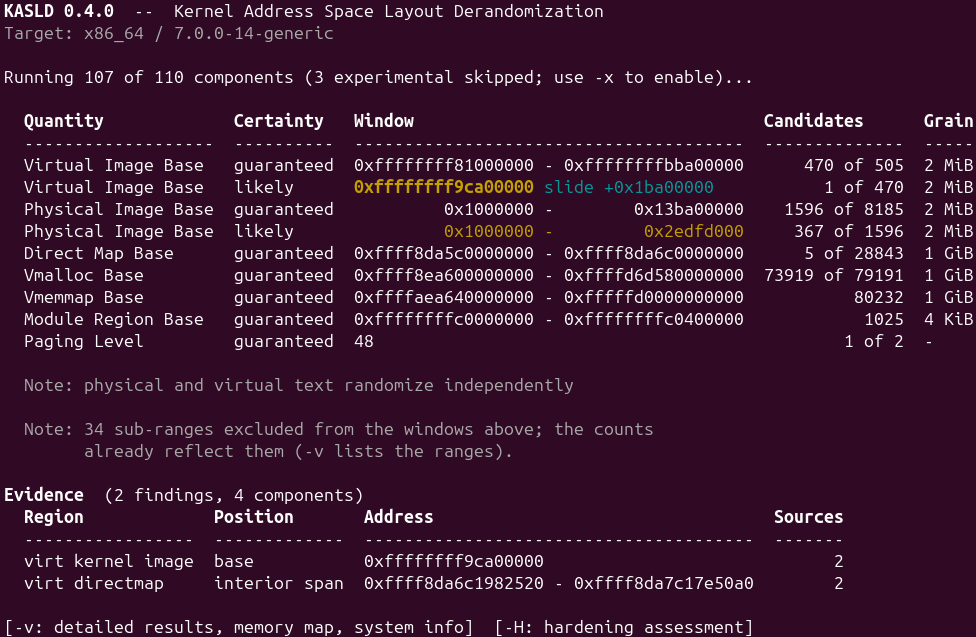
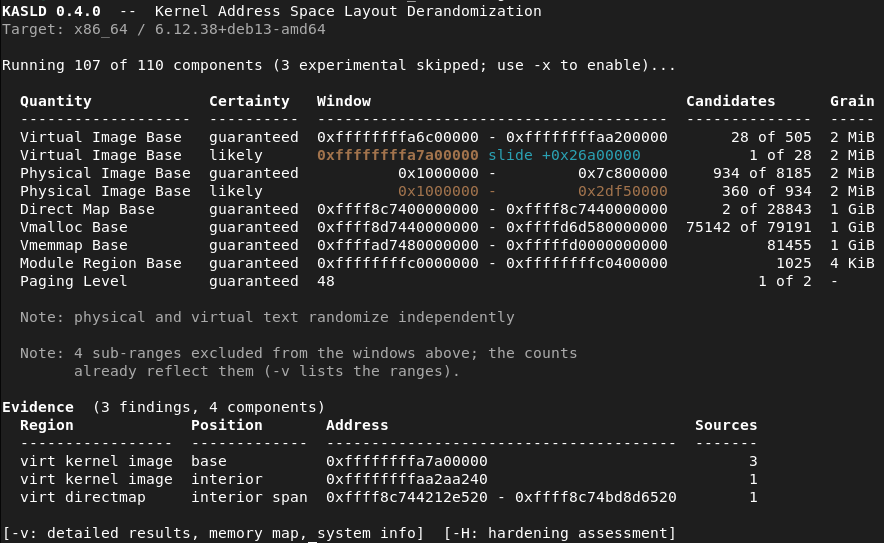
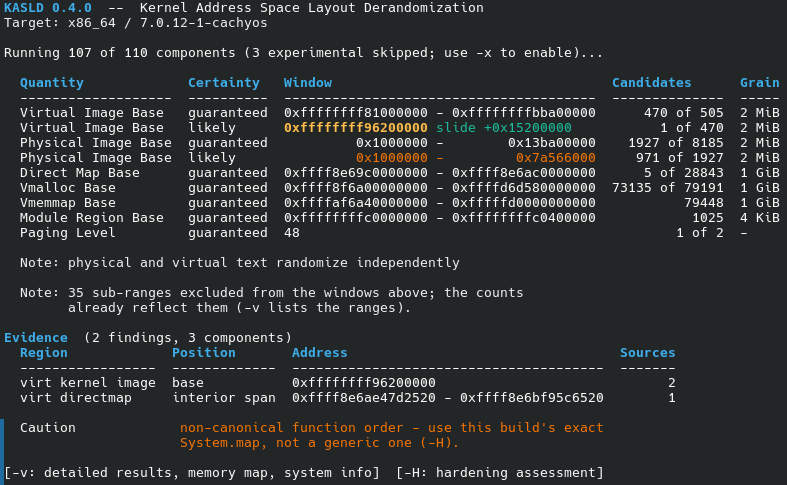
KASLD v0.4.0 released.
Linux #KASLR derandomization tool.
Memory regions now carry a certainty rating: "guaranteed" proven values/ranges, and "likely" narrower guesses that can be wrong (from heuristics/side-channels).
+18 leak components (120 total).
https://t.co/NDUxBpgqE5
🛑 A critical VMware flaw can turn local VM admin access into host code execution.
Broadcom fixed CVE-2026-59346 and an HGFS flaw in Workstation and Fusion 26H1u1. Both affect 25H2 and 26H1, with no workarounds or known exploitation.
How the code execution paths work: https://t.co/dCuVR33NuP
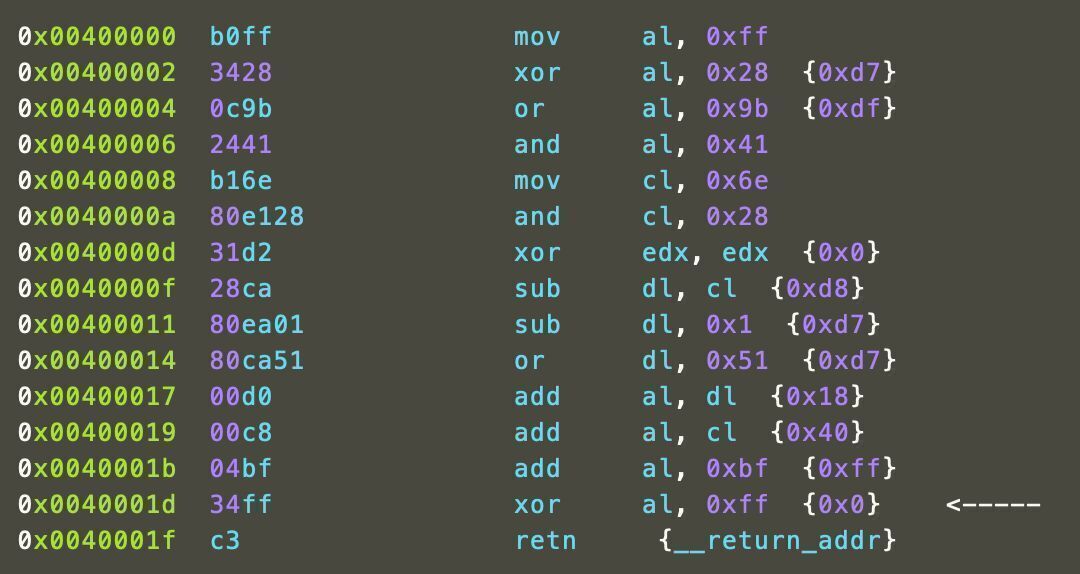
LLVM based analysis of the relationship between compilers, obfuscation, and de-obfuscation
https://t.co/7rfwhEczcz
Credits Robert Yates (@quarkslab)
#infosec
🛑 A BGP hijack delivered a malicious Virtualizor update that established persistent root access.
A valid certificate prevented connection warnings. One provider found 5 of 34 checked hypervisors compromised.
Virtualizor says check every server.
Read: https://t.co/UKTxcwrBDT
‼️ A public PoC shows how CrowdStrike Falcon’s macro remediation can be abused for privilege escalation.
FalconFlank works on fully updated Windows 11 25H2 and Windows Server 2025. CrowdStrike has not yet commented.
Read: https://t.co/yN3FInp26x