SCOM's Operations console is still a Windows app. The web console can't deploy agents. Mac users know the jump box tax.
We shipped SCOM Pulse: the everyday SCOM console, in a browser. Alerts, Health Explorer, agent deploy, maintenance, dashboards.
One MSI. 30-day trial. No key.
🚨STEVE JOBS FUE DESPEDIDO DE APPLE
Después se presentó en el MIT y soltó la masterclass de negocios más cruda y sin filtros de 60 minutos jamás grabada.
Cero mentiras de relaciones públicas. Cero imagen que proteger.
Solo pura y brutal honestidad del hombre que construyó Apple una vez y estaba a punto de reconstruirlo aún más grande.
Deja de scrollear.
Mira esto esta noche en lugar de Netflix.
Guárdalo y regresa cuando lo necesites 🔖
Are you doing Autopilot Hybrid join? If answer is Yes, you need to update the Intune Connector! The old connector will be blocked starting July.1, 2025 #msintune
https://t.co/EqtlB0rNnB
What's new in Microsoft Intune July 2024: The days in my part of the world have been long and hot. Often my emails are met with out-of-office replies as my colleagues and friends are taking time to recharge outside of work. It reminds me… https://t.co/zOy8x7VoiL #MSIntune#SCCM
SECURITY: ACTIVE DIRECTORY and GROUP POLICY: Stress Reduction Tip - Structure and Simplicity
There are a few key elements to reducing overall stress managing Group Policy:
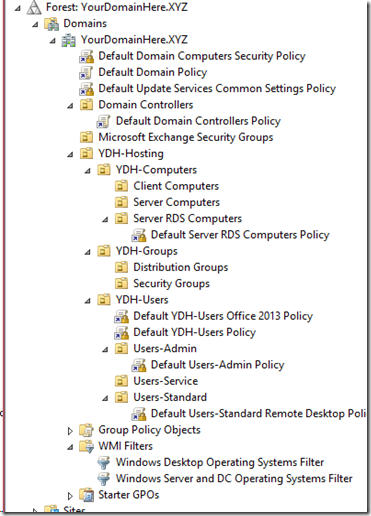
1: A proper Sites & Organization Unit structure
2: GPOs that are User _or_ Computer specific linked to their respective OU
3: Limit the use of Loopback
4: Never, ever, edit the Default Domain Policy or the Default Domain Controllers Policy. Ever
In the image, any GPO linked to a Computer specific OU would have the Users component disabled. Any GPO linked to a User specific OU would have the Computer component disabled.
Never the twain shall mix.
In larger organizations, the OU structure should mimic the Sites structure.
A root OU for each site then the pictured OU structure for each keeping the Computer and User AD Objects separate.
The simpler we keep things, the simpler it is to troubleshoot if something behaves in an unexpected manner.
The simpler we keep things, the more _secure_ our Active Directory will be.
Plus, keeping the number of GPOs linked closer to the root or at the root limited helps reduce overlap and possible settings collisions that can be painful to troubleshoot.
TIP: Think of OU structure and how the GPOs apply as being similar to CSS. The closer the GPO is to the intended AD Object the more weight it has. And, the last GPO closest to the AD Object _always_ wins. Well, _almost_ always! ;0)
Acronyms
AD = Active Directory
GPO = Group Policy Object
OU = Organizational Unit
CSS = Cascading Style Sheets
Tags
.@WindowsServer
#ActiveDirectory #GroupPolicy #NetworkSecurity
#OnPremises #Hybrid
#Troubleshooting
Not sure which #Azure compute service to choose for your application? Let this article be your guide! From Azure #AppService to Azure #Kubernetes Service, find the perfect fit for your needs. Read more here: https://t.co/yvBDXHAVdd
¿Tienes una deuda reportada en DataCrédito?
Ahora podrás negociar con diferentes entidades desde Midatacrédito 🤝
¡Conoce el paso a paso y las entidades aquí! ⏩ https://t.co/RP4VIzQE0W
#PrimeroLoPrimero
*Aplican Términos y condiciones
¡Hoy gané mi badge "Configuración de Microsoft Entra ID"! ¡Me llena de orgullo celebrar este logro y espero que esto te inspire a comenzar tu propio viaje de @MicrosoftLearn!
https://t.co/1pzSFKgrmO #MSLearnBadge
“We love #configmgr, it’s not going anywhere, there’s more people coding on it than ever” - #msinunte CVP Steve @dispensa
I feel a need to amplify Steve’s quote - as indubitably people always finishing a conf like this taking away that it is dying.