1/ We are thrilled to announce the industry-leading transaction pre-execution service - Mopsus. Mopsus aims to help users understand transactions before signing.
https://t.co/D6pRUJmOe2
🦅Phalcon Update!
* Transaction Simulation supports #BSC@BNBCHAIN
* Supports #Polygon@0xPolygon. The data after block 34165312 is available. Old data is currently being imported.
Click this link for the Polygon transaction:
https://t.co/3VNhxb97nb
Fly with Phalcon!
Carrot on BSC was attacked.
https://t.co/BLueNa8jK9 (Thanks @bbbb for sharing this tx hash).
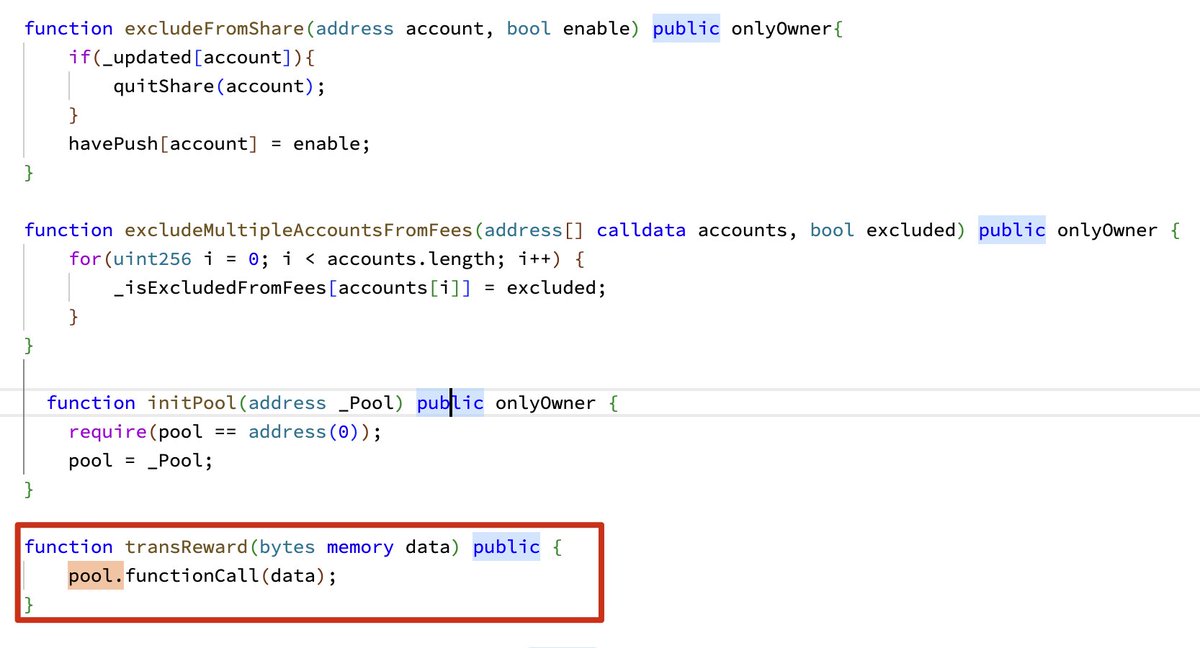
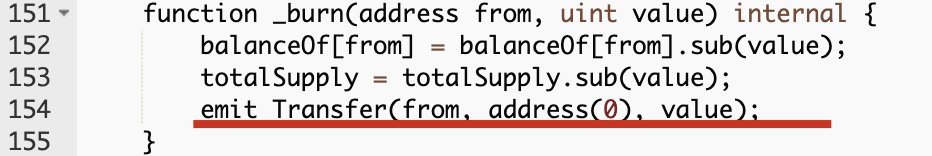
We have seen public burn, public transfer. Now we have public functionCall.
What's next?
Update: How we recover the stolen funds for TransitSwap
@TransitFinance (and BabySwap @babyswap_bsc)
Because the bot that front-runs the attack is vulnerable to profanity vulnerability. We recovered its private key and rescued the funds.
Full Story: https://t.co/T7z39R5b3p
🎉 Phalcon Dark Mode Launched!
We have fixed the bugs and made some optimizations (https://t.co/bjqqOfXo3U).
#Ethereum#BSC#Cronos
Note: Try this transaction 0xc18ec2eb7d41638d9982281e766945d0428aaeda6211b4ccb6626ea7cff31f4a
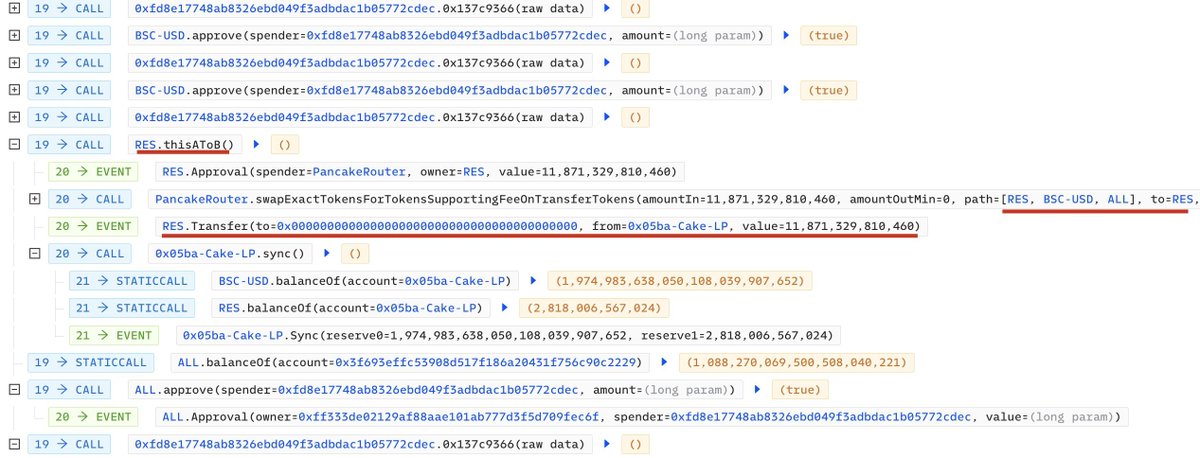
2/2 Specifically, the thisAtoB function allows to swap RES tokens in the contract to ALL tokens through the RES-BSCUSD-ALL path. By using flashloans, the attacker successfully made the pools unbalanced to manipulate the prices, and then swapped the tokens back to make profits.
1/2 Our system detected that RES token on BSC was attacked with $290,671 loss. The attack transactions are as follows:
https://t.co/4SdXxc66oL https://t.co/TOgnvSGxsS
It is a price manipulation attack, and the root cause is due to the controllable external function (thisAtoB).
1/ We are thrilled to launch a powerful transaction explorer: Phalcon (https://t.co/HkL4ls6IwX), which aims to provide comprehensive data on invocation flow, balance changes, and fund flows. Currently, it supports #Ethereum, #BSC, and #Cronos.
Our experience shows that this can-be done within one hour on a server (500g memory and 64 cores). Should be faster if gpu cluster is used.
Actually the vulnerability is being widely exploited. We are actively monitoring and will release a detailed report sometime next month.
Our short analysis of the Accusation of the Wintermute Project: https://t.co/6Lw6FjUrLp
@wintermute_t@evgenygaevoy@librehash@WuBlockchain@banteg
Our analysis shows that the report is not convincing enough to accuse the Wintermute project.
We found similar scams on #BSC earlier. The scammer teaches users how to develop a Front-run bot to make money. But the contract it provides has a backdoor. After being deployed, all the victim's tokens will be transferred to the attacker's address.
https://t.co/yzwNzUpx33
3/ Steps
1) Borrow USDT via flashloan
2) Partially swap USDT for RADT-DAO token in the Pancake pool
3) Trigger the fallback function of the RADT-DAO contract to transfer the remaining RADT-DAO in the Pancake pool
4) Swap RADT-DAO (from Step 2) for USDT
5) Return the flashloan
2/ There are three front-running transactions and a failed "original" transaction (https://t.co/OKzh9pums0). Through the investigation, we find that the attack is made possible due to the price manipulation of the RADT-DAO - USDT pair in the Pancake pool. Below is the detail:
1/ Our easy-to-understand version of the vulnerability in the Profanity tool, which caused Wintermute @wintermute_t to lose 160M.
https://t.co/ZNRgHmtDMm
BlockSec Academy | We have compiled a variety of security articles on #DeFi and #NFTs, including Attack Analysis, Secure Contract Development, and related misc.
📘 You can contact us if you have any questions while browsing the articles.
https://t.co/qoEm47AX8Z