ported @dotenvx to Go, and all my Go projects now use the port.
for those of u using Go and haven’t tried dotenvx yet, there’s no better time to try it.
- the encrypted .env is in git, so *every worktree/sandbox just works* and there will be no more .env.example drift
- //go:embed it: one binary, one env var (DOTENV_PRIVATE_KEY)
- no Node, no extra process: 5ms startup, ~73MB less RAM than `dotenvx run`
ty @motdotla for the blessing
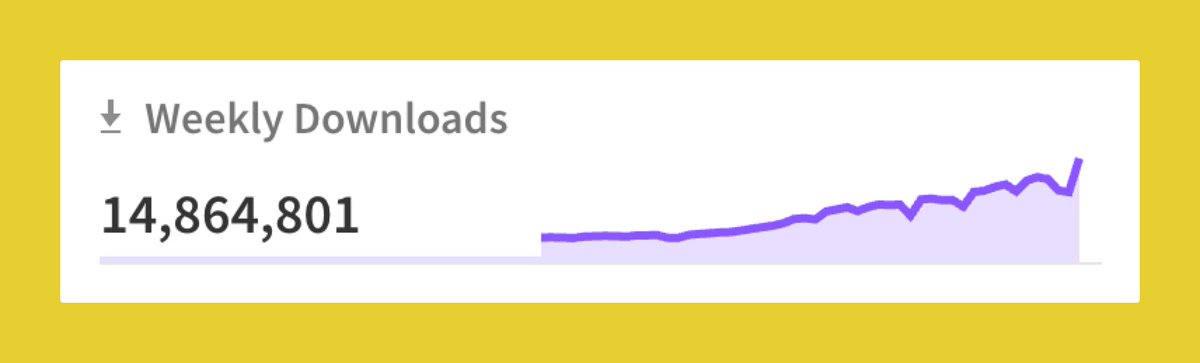
20 mil everyone. thanks for your support.
despite the download count we're prob the quietest biggest secrets solution still. no big hundred mil valuation, just an elegant cryptographic secret-splitting solution that makes you sovereign over your secrets.
thank you kings. 👑
One person can accomplish what once required many. And more code is being written than ever because of it.
Dotenv is somewhat of a yardstick for this. In December ’25 it was doing 300 million installs a month. Today, 750 million. That’s insane growth for a mature fully-distributed project.
Maybe you feel like me - excited but also unsettled, like the whole engineering discipline is completely changing. Where do you set your feet? What do you hold fast to? Every week a new model, new tool, new way to build.. it’s kind of a lot right now.
There’s never been more opportunity, there’s never been more uncertainty.
https://t.co/Fefbo58Fi4
Yes, so the decryption key is taken, but the attacker also needs access to your encrypted .env.production file (which doesn't look like was accessed here). That private key then becomes useless to the attacker.
You should still rotate all your underlying keys but this buys you way more time of a worse case of your secrets immediately being put to use by the attacker.
It is tough these days to build secure software - especially if you are under a major attack like OpenCode. So I feel for them and they build great product.
But this is another example of why you should use a model like Dotenvx or SOPS. Split your secrets cryptographically so that an attacker has to attack both the providers secret store (in this case that is what was attacked) AND the encrypted secret in your code (which was not attacked or even reachable here).
This is why we wrote our whitepaper. Meanwhile, every other provider retweeting OpenCode and saying 'use our secrets store' is repeating the same systematic problem - centralizing your secrets to their secrets store yet again.
Dotenvx or solutions like SOPS are the only way to solve this for your organization.
https://t.co/rhXRG54PCp
Indeed. Competing projects seem to get all the attention here on twitter, but the cool-handed devs, they choose @dotenvx.
Thank you to all the other cool-hand devs like Chris here using dotenvx!
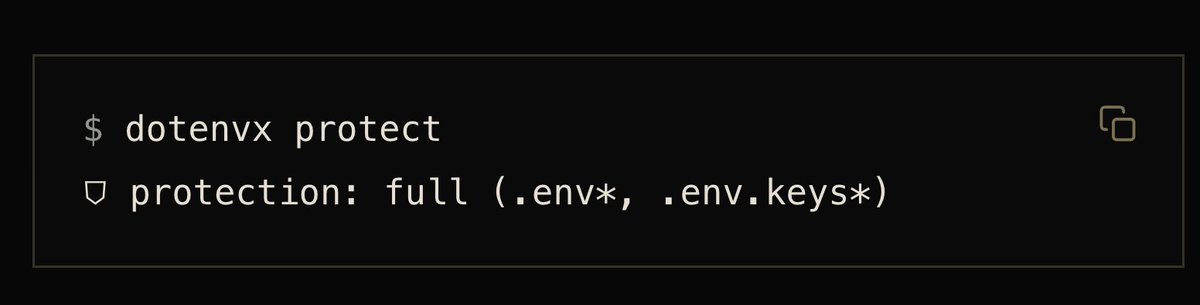
Man @dotenvx is such an underrated piece of technology. We use it for all our clients and our SaaS. Now you can run dotenvx protect once, and it protects you from agents accidentally committing unencrypted env vars 🔥
New in Dotenvx: One-click custody! 🔑
> With .env.keys now an option and not a default
> we've made it one-click easy for you to
> custody your private key
>
> to @1Password, @Bitwarden, or keychain.
All the benefits of encrypted .env files + the custodian you trust. 🔐❤️