#SANSTip: if you're not using Bluetooth on your phone or computer, turn it off. It's more secure AND it saves battery life. It's a win-win!
For more tips like this, check out the @SANSAwareness #OUCH newsletter: https://t.co/5ks8RTzTlY
The SANS Institute is so excited to announce the second edition of the SANS-HBCU Cyber Range competition. Save the date and spread the world. Stay tuned for a follow up announcement on some valuable prizes. https://t.co/gZUXuDwboH
We decided that each area needs its own curriculum with specialized attention. Offensive Operations is the umbrella name to encompass them. My goal is to ensure we cover every attack vector across the entire threat landscape & the operations in which we perform to defend our orgs
If you've been tasked with implementing, managing, or protecting web applications, then #SEC522 is the course for you!
Take it with @johullrich at #SANSCDI: https://t.co/yCZQOWhAJd
Enumerate Contents of Storage | Upload & Download Files from Storage | Encrypt Data | Alternative Cryptography Commands for Azure | AND MORE! Get your free copy of this #multicloud cheat sheet here: https://t.co/e8sTcGaUhk
What does a #SANSCloudAce represent? The best of the best.
Join the flight to the future.
Learn more about #cloudsecuritytraining here: https://t.co/bsFPB0dRs1
CLI Version Details | Filtering & Query | Authentication | SSH to a Public Cloud Virtual Machine - this is just one side of the new #multicloud cheat sheet by @brandonmaxevans. Get your copy here: https://t.co/EKtKjgPklO
This course is a deep dive into the native services in #AWS to gather, analyze, & detect threats. You'll learn about common attack techniques used against cloud infrastructure and investigate how to detect them. @TheCybergoof | #SEC541
Learn more: https://t.co/mkGO6Jd2wG
“I thought the slides and diagrams were phenomenal. It really helps to introduce and step into containers/docker/kubernetes and related principles.” – Kyle V. #SEC584 | @sublimino | @emjohn20 Come take the class with us! https://t.co/r8kwOtgEOK
In this talk @BrandonMaxEvans explains how a compromised serverless function can be used to exfiltrate sensitive data, persist malware, gain powerful credentials, and pivot to other cloud services.
https://t.co/xvtGzItFOv
#multicloud#multicloudsecurity
Curious about the all NEW #SEC510 Multicloud Security Assessment & Defense? Course co-author @BrandonMaxEvans wrote this blog post exploring the need for such a course.
Read it now: https://t.co/oGcv4Y3iYP
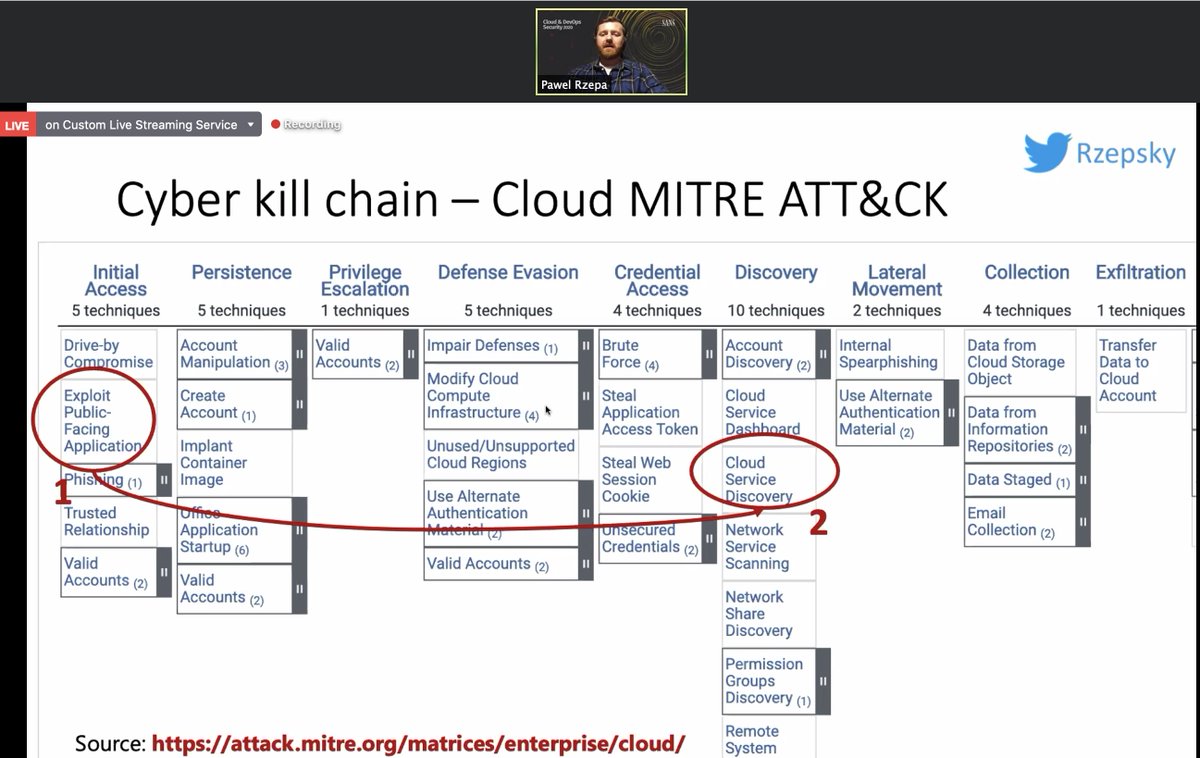
.@NightmareJS is sharing an overview of what constitutes privilege in GCP and how movement between accounts can occur to obtain privilege at #SANSCloudDevOps | #SANSCloudAce