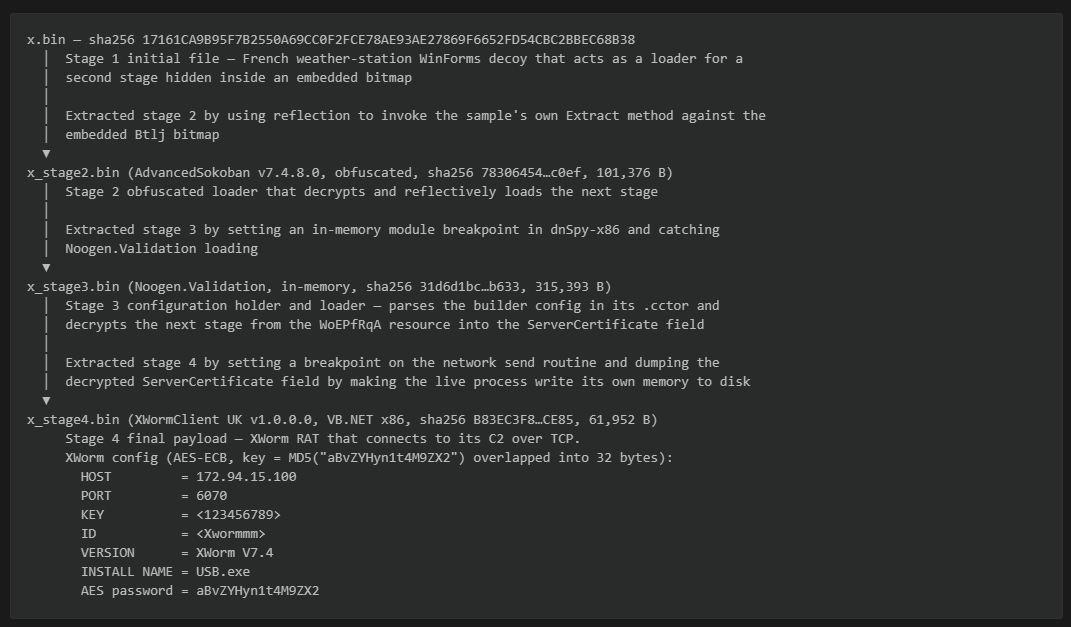
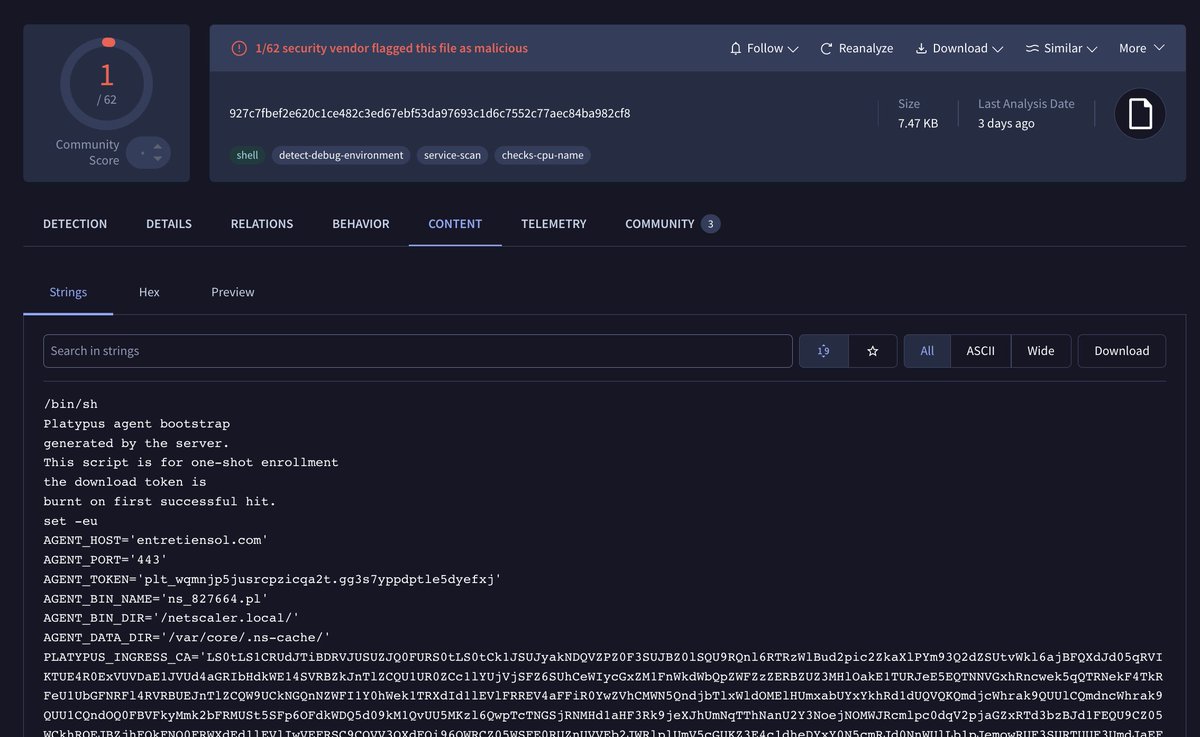
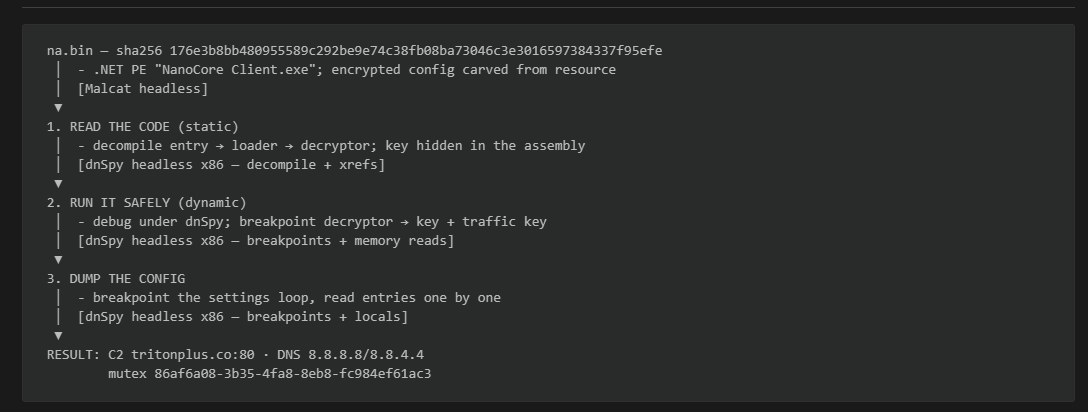
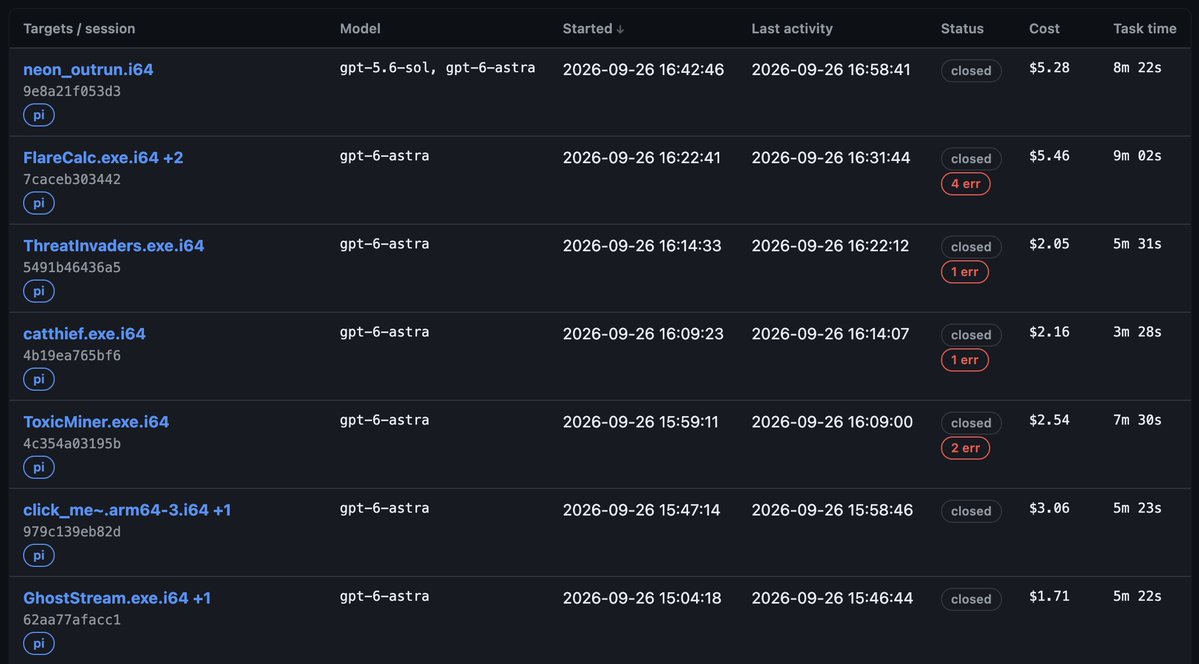
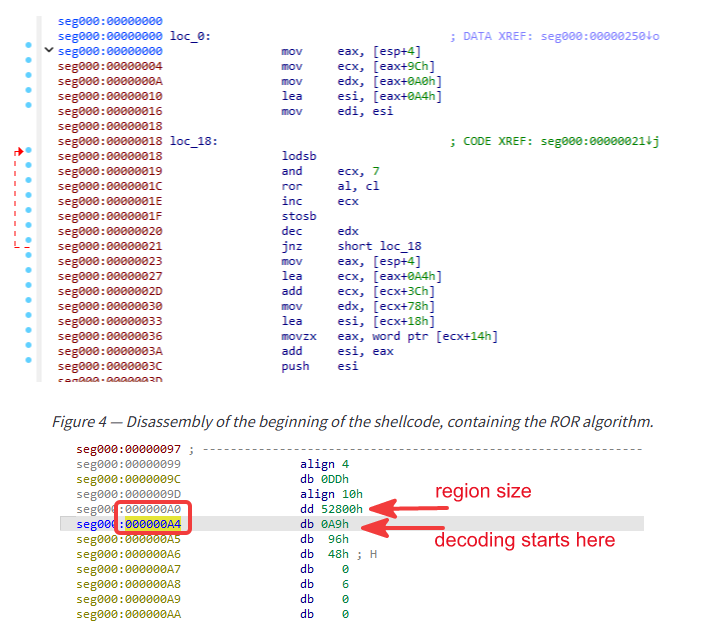
These two #malware configs came entirely from a local LLM setup with no internet access.
- GLM5.3-Flash (Tensorfold, EXL3)
- Pi harness
- Driving a windows 10 VM over MCP.
The heavy hitter today was DnSpy, vibe modded to have a headless mode + debugger over MCP.
If you are a threat hunter or Detection engineer -
Baseline your wscript usage. The numbers will be staggering and then take it up the chain to get wscript, mshta, cscript blocked globally.
“ … it copies a size-matching cache entry to %LOCALAPPDATA%\Temp\t.vbs, giving the cached payload a VBScript extension, then executes it with wscript.exe. “
The more we continue to allow the basics to execute, the longer clickfix continues.
Good luck out there friends. ⚔️
I was informed of this specific ClickFix command being spotted in the wild yesterday, and was scratching my head trying to figure out what the hell it's doing
This is an incredibly weird, fragile but creative technique
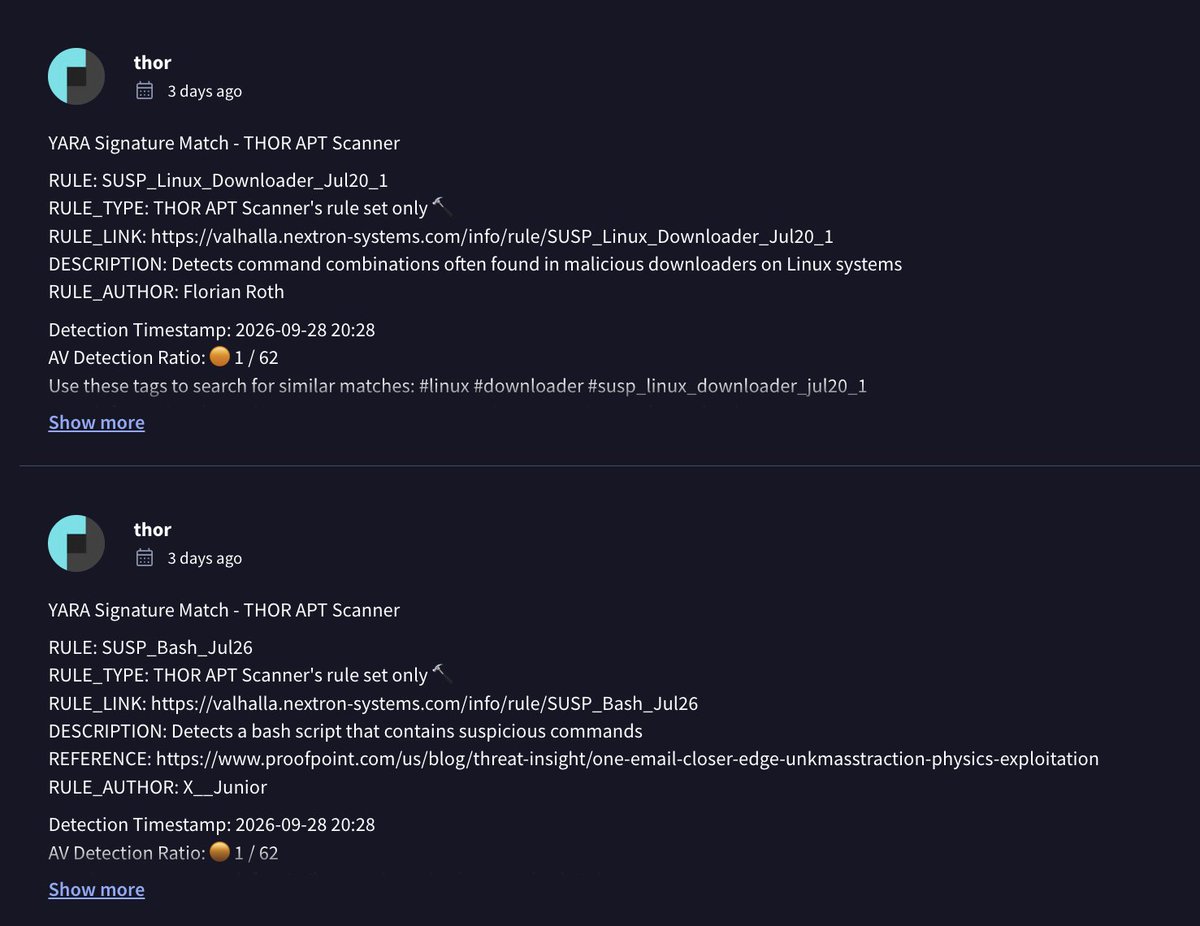
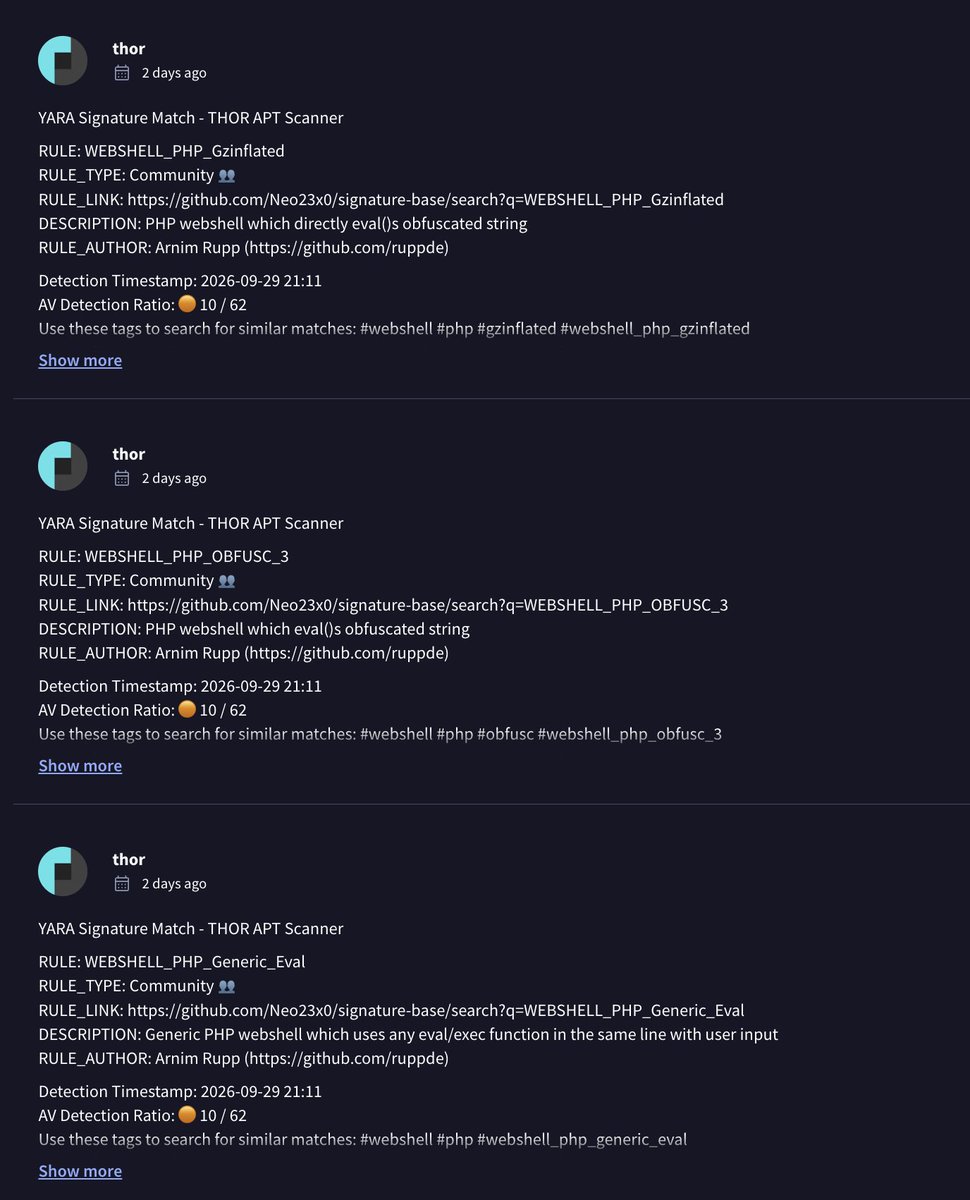
We examined artifacts left behind by attackers during the recent Citrix #NetScaler compromises. Many were already covered by existing generic THOR rules, including rules we've shipped for years.
One script matched SUSP_Linux_Downloader_Jul20_1. That rule dates back to 2020, more than six years ago(!). The script also matched SUSP_Bash_Jul26.
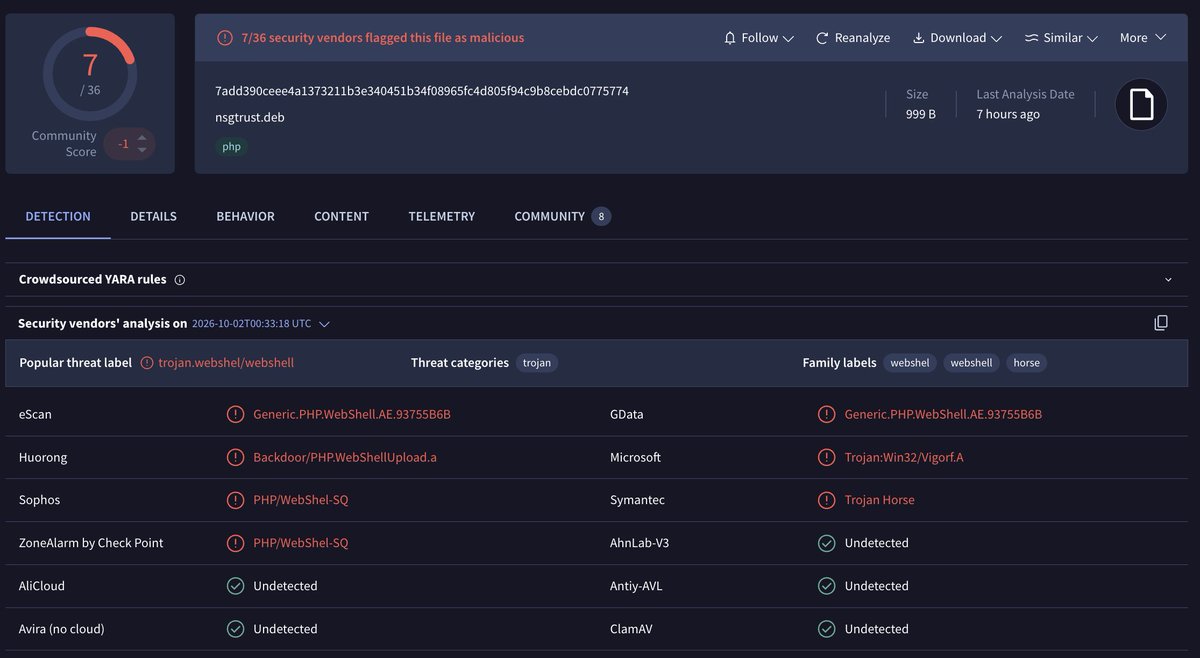
The recovered webshells matched these existing generic rules:
- SUSP_WEBSHELL_PHP_Encoded_Jun21_1
- SUSP_Eval_Base64_Indicators_Feb22_1
- EXT_WEBSHELL_PHP_Generic_Eval
- EXT_WEBSHELL_PHP_OBFUSC_3
- EXT_WEBSHELL_PHP_Generic
- EXT_WEBSHELL_PHP_Gzinflated
- EXT_WEBSHELL_PHP_Dynamic_Big
Some of those webshell rules are in THOR Lite, too (EXT_*)
This is POST-EXPLOITATION DETECTION. We didn't need to know which zero-day got the attacker in to recognize what they left behind.
A scan could have flagged these artifacts from day one, before the exploited vulnerabilities were public. The rules were already there.
Scan your edge devices regularly. Daily, where practical. Use THOR via SSHFS or scheduled file collection for THOR Thunderstorm.
Don't wait for the next advisory to start looking
Why THOR detects what others miss
https://t.co/EbtVt3al8E
🗿:Kaela, do you have any summer memories?
🔨: I- *laughs* I talked about mine yesterday
🗿:You HAVE to tell me yours
🔨:My summer memories is about Kronii...
It so funny how on the very next day Biboo did the SAME exact thing that Raora did
#LIVEseki#kaelaif
The official IDA MCP Server is here. It's free, open source, and works with any LLM.
Your agent writes IDAPython, uses ~20% fewer tokens, and can share an IDB with you in real time.
𝚞𝚟𝚡 𝚒𝚍𝚊-𝚑𝚌𝚕𝚒 𝚖𝚌𝚙 𝚒𝚗𝚜𝚝𝚊𝚕𝚕
https://t.co/jXPiF6Wyvk
(copy-paste: uvx ida-hcli mcp install)
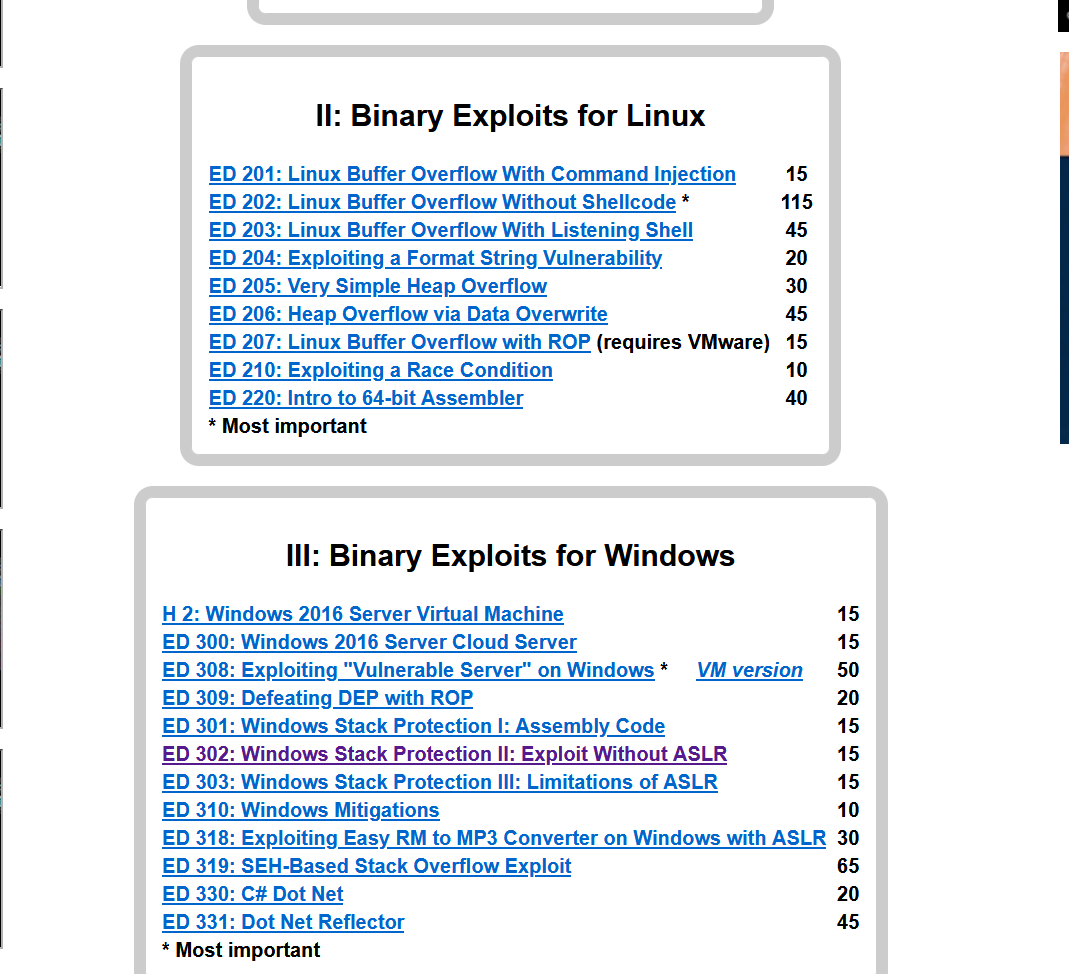
If you're learning exploit development, bookmark this.
A FREE collection of hands-on exploit development tutorials covering:
Linux + Windows buffer overflows
ROP + defeating DEP
ASLR + Windows mitigations
Heap overflows
Format string vulnerabilities
Race conditions
SEH exploitation
x64 assembly
ARM shellcode
iPhone exploitation
Created by @sambowne with @djhardb, @KaitlynGuru and @infosecirvin.
Start here: https://t.co/dpFck4hnwz
Excellent free resource for anyone getting into exploit development, binary exploitation and reverse engineering.
#ExploitDevelopment #ReverseEngineering #Infosec
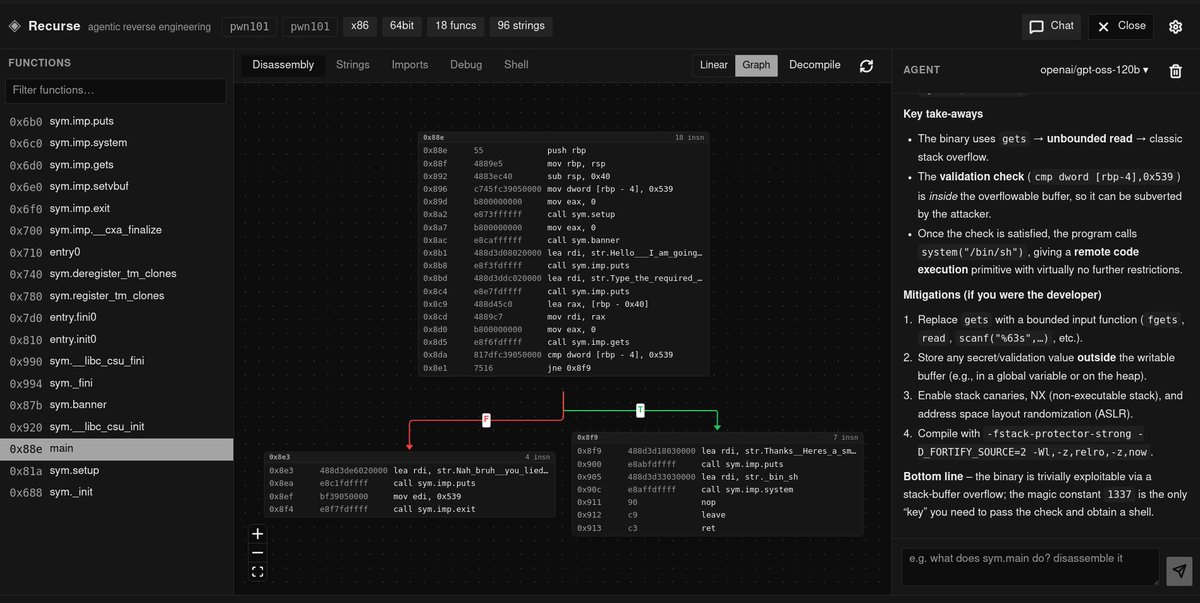
Recurse: Agentic reverse engineering environment with Ghidra-class desktop app. Built with Tauri 2 on top of an existing RE toolchain: radare2 does all parsing, analysis, disassembly, xrefs, strings and imports; r2ghidra (optional) provides decompilation.
Github:- https://t.co/nyk5FmEx0i
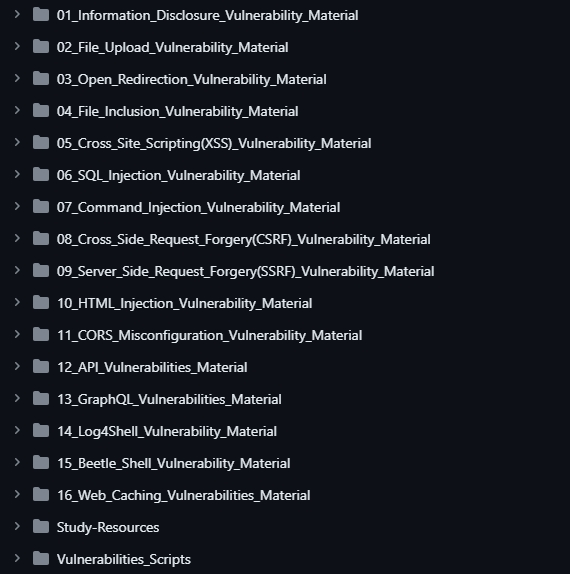
Digital Forensics - Memory Analysis Guide, Part 1
We made a guide showing how to use Volatility 2 and 3 for different tasks.
Handy cheat sheet
https://t.co/urogtnhWlr