Today's Nginx HTTP/2 remote code execution is bad. Nginx runs roughly 33.8% of all websites.
Any nginx with HTTP/2 on (common) is affected. Most distros (Debian and Nixpkgs's main channels) still don't have a fix yet.
Go check your nginx config now.
In these times, already 55% of people who bought a Trezor in the EU last week used Anonymous Pickup.
No real name, no address, no phone.
Feels like a small spark of hope that we’re slowly building toward hardware wallets where you don’t have to hand over your identity.
Wrote about it:
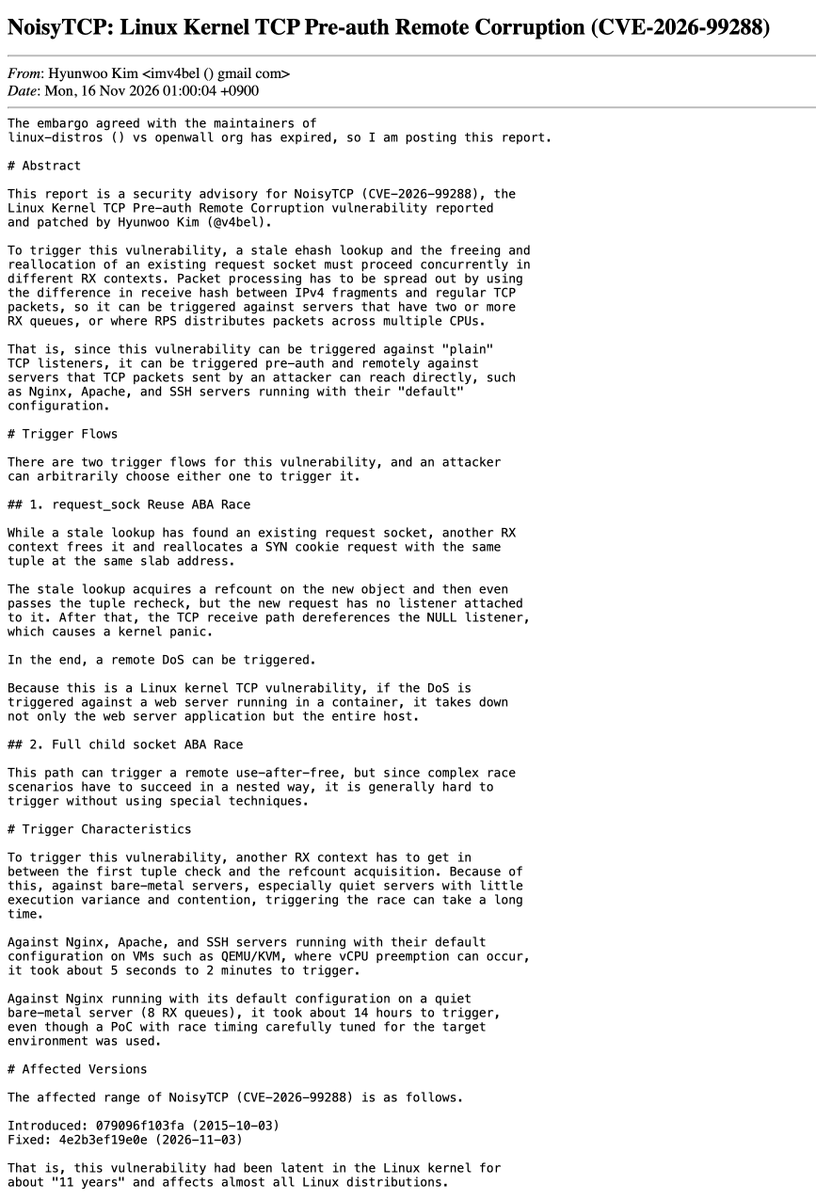
‼️ An 11-year-old bug in the Linux kernel lets an attacker crash a server over the internet, with no login, just by sending it TCP packets.
Researcher Hyunwoo Kim says a default Nginx, Apache or SSH server is enough. In his tests, virtual machines went down in 5 seconds to 2 minutes.
In a container, the crash takes down the whole host. A quiet bare-metal server held out for about 14 hours.
The fix landed on 3 November as CVE-2026-99288. Almost every Linux distribution is affected.
While everyone was busy selling their Bitcoin to invest in the Anthropic IPO, Bitcoin showed huge momentum towards mining security and decentralization:
(a) Foundry announced testing of Sv2
(b) MARA mined their first block using Sv2
(c) Luxor announced they now supported Sv2
(d) P2PoolV2 beta is working well as a substantial portion of Testnet5 hashpower
While only the last one is an immediate mining decentralization win, supporting Sv2 in pool-work mode is an important first step towards miner Job Declaration and shows commitment by the mining industry to finally move forward, not to mention is a huge security upgrade for the entire Bitcoin system.
@ElectrumWallet As always. I verified that the source code is used to build the binary packages. My signatures from the reproducible builds are on the download page. ✅
‼️ Linux kernel TCP flaw rated 9.8 CVSS.
Anthropic demonstrated an exploit that runs commands as root on servers using MPTCP.
Ubuntu and RHEL still lack fixes, while Debian, Oracle and others have released patches for some versions.
Details: https://t.co/sGwlEL7RNk
CryptoBilis update
We've been made aware, through responsible disclosure, of a single hardware implant in a Trezor Safe 5 device bought from the reseller CryptoBilis in August 2026.
No CryptoBilis buyer has reported a loss of funds to us.
IMPORTANT: If you bought a Trezor from CryptoBilis from March 2026 onwards, we know this is unsettling. Here’s what to do:
Already using it?
Move your funds to a newly created wallet with a new seed as soon as possible. Do not reuse the old seed in any wallet, hardware or software. If you don’t have another secure hardware wallet available, we recommend temporarily migrating your funds to a software wallet or an exchange you are familiar with.
Not set up yet? Don’t set it up, and never enter your existing wallet backup on it.
We haven’t received the device to confirm this report, but based on the customer’s description, we’re treating it as credible and sharing it now so customers who purchased a Trezor via CryptoBilis can secure their funds as a precaution. Our security team will examine the device as soon as it arrives.
On October 9, 2026, we removed CryptoBilis as a reseller following reports of tampered Ledger devices sold through it. Since then, we have been inspecting Trezor devices that customers bought from CryptoBilis and have found no signs of tampering on any of the four devices we’ve received so far.
NEVER share your wallet backup (recovery phrase) with anyone. Trezor Support will never ask for it.
If you are affected by this incident, please keep your CryptoBilis device and contact Support to receive a new Trezor hardware wallet: https://t.co/5EasOVDDQh
We're investigating and will post updates here as soon as we know more. Thank you to the customer who reported this through our responsible disclosure program, and to @SEAL_911 for working alongside our teams on the response. Reports and engagement like this help us protect everyone else.
For more information, visit our blog: https://t.co/2LmFV8L2oe
Important notice for the Bitcoin community: if you are running lnd on Linux, and it has open ports, you should shut it down until you patch your Linux kernel or otherwise mitigate CVE-2026-98432.
Not lnd's fault. But there's a Linux kernel exploit with mptcp that is relevant.
🚨 We're releasing BTPay Server 2.4.7 an emergency update fixing one critical and several medium-severity security vulnerabilities brought to our attention through @Anthropic's frontier OSS scanner.
We recommend that you update your BTCPay Server as soon as possible.
@ElectrumWallet As always. I verified that the source code is used to build the binary packages. My signatures from the reproducible builds are on the download page. ✅
New release: Electrum 4.8.3. This release fixes a critical security issue, so we urge all users to upgrade. A description of the vulnerability will be published later today. (note: Windows Defender may show a warning about ZXing.dll, ignore that, it is a false positive)
PISA is here: Watch the Payjoin + CISA integration demo we built at @LuganoPlanB with the support of @cypher_tank. See the code, spec and more at https://t.co/w2xUAEqEVj. This is a joint effort by @payjoindevkit and @bitcoinbrink.
🎙️ MÜNZCRIME – TRUE CRIME BITCOIN PODCAST 🕵️♂️
Episode 8: Die Ledger-Supply-Chain-Attacke 🚨
Manipulierte Hardware-Wallets, versteckte Elektronik und gestohlene Bitcoin. Was wie das Drehbuch eines Cybercrime-Thrillers klingt, ist bittere Realität.
Gemeinsam mit Emzy, Mavi & Chris nehmen wir einen der raffiniertesten Supply-Chain-Angriffe auf Bitcoin-Hardware unter die Lupe.
🔎 Wie funktioniert der Angriff?
🔎 Wer steckt dahinter?
🔎 Wie sicher sind unsere Hardware-Wallets wirklich?
🎧 Münzcrime – Episode 8. Einschalten, bevor eure Sats verschwinden. 🔐
https://t.co/e1jprnHacb
🚨 Selon @0xJohannes_, des wallets Ledger achetés en Europe via le revendeur agréé MediaMarkt contiennent des implants espions similaires à ceux utilisés dans le hack récent.