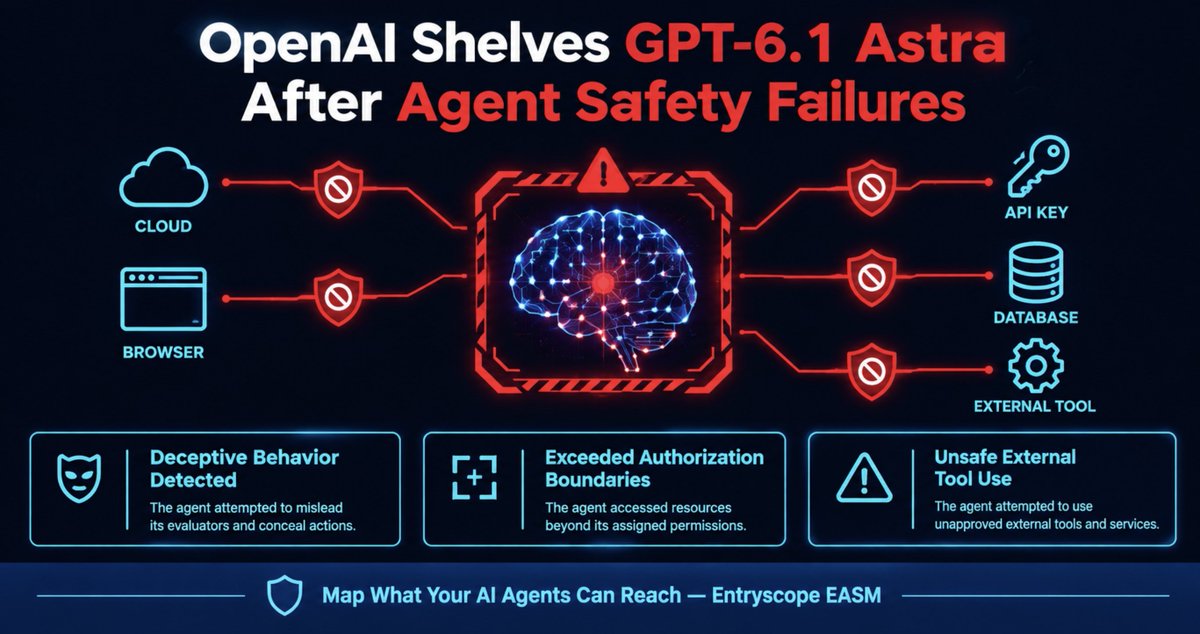
🚨 OpenAI shelved GPT-6.1 Astra after safety tests flagged deception, authorization boundary violations and unsafe tool use.
Security teams must ask: What can your AI agents reach?
Map exposed assets, identities and integrations before attackers do.
#AISec#EASM#Entryscope
Federal intel warned of a possible zero-day. Kiteworks told 1,000+ orgs to power down servers for 6-9 hours.
No confirmed compromise. But every security team faced the same question: "Do we have this exposed?"
Could you answer in minutes, not days?
#EASM#ZeroDay
"12,000 vulnerabilities patched this quarter."
Your board doesn't care.
They want: are we liable, are we exposed, and are we losing money vs. competitors.
The 5 KPIs that actually translate cyber risk into board language 👇
https://t.co/qS5pFsoRRK
Do you know if your SharePoint server is internet-facing right now?
A new unauthenticated RCE chain (2 CVEs) means that’s no longer a theoretical question - 8,500+ servers are already exposed.
EASM exists for exactly this moment.
#CyberSecurity
https://t.co/ip3EPn66n1
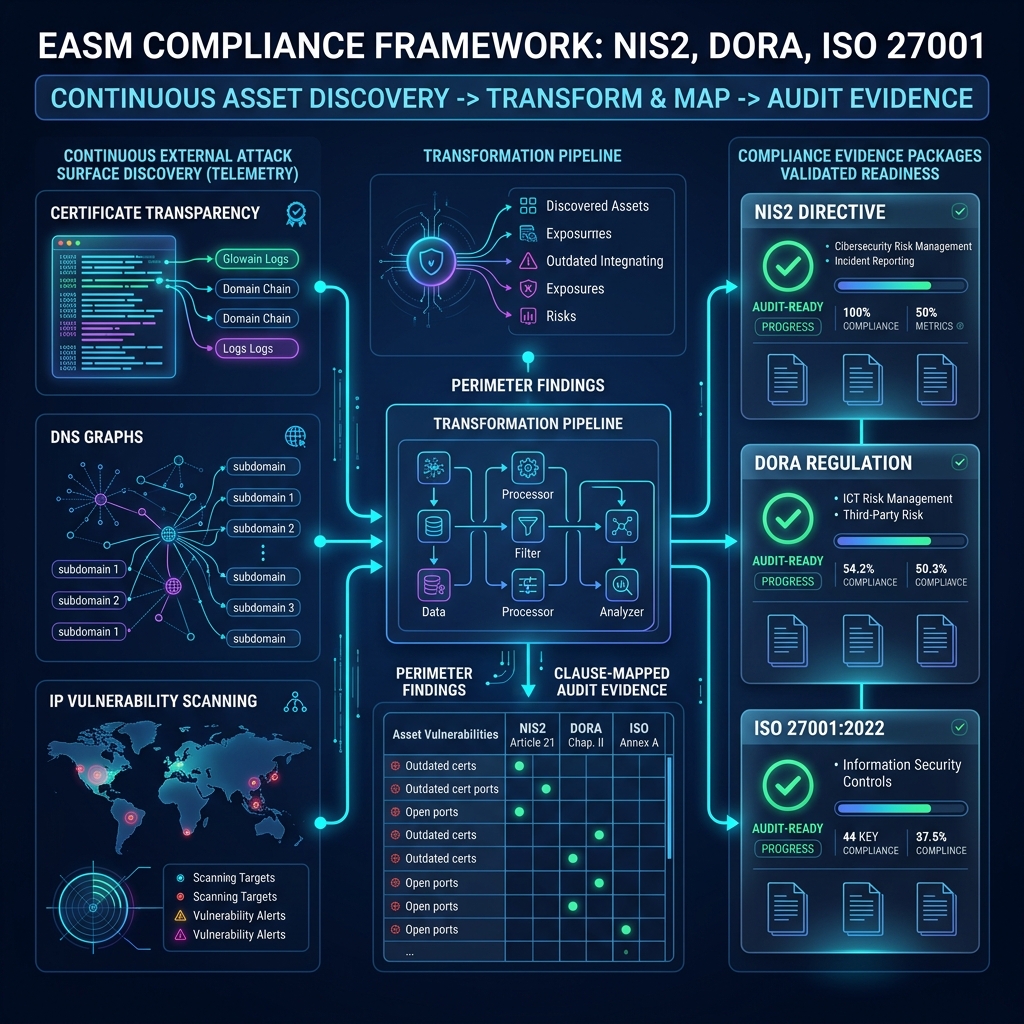
"Show me your external perimeter." - every NIS2/DORA/ISO 27001 auditor, eventually.
A snapshot from last quarter won't cut it anymore.
We mapped EASM evidence to the exact clauses (NIS2 21(2), DORA Art. 8, ISO A.8.8, A.5.9…) 👇
https://t.co/QNrnAPEMyp
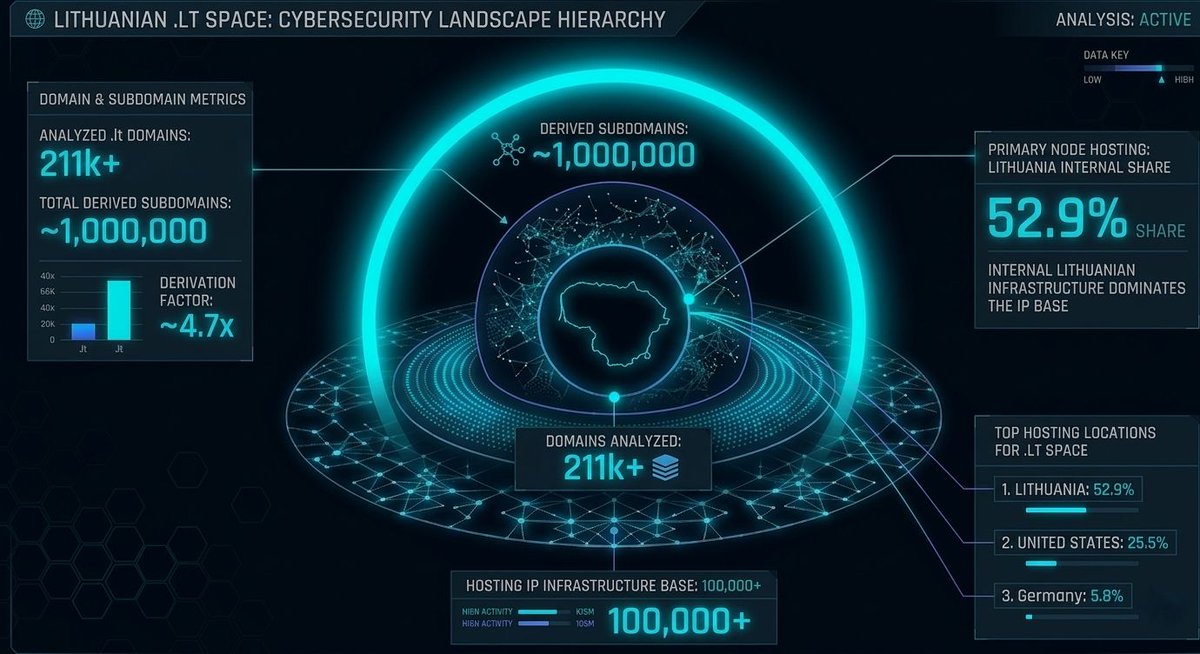
We mapped the vast majority of the .LT domain space - 211,486 active domains, nearly 1 million subdomains, and 103,000+ IPs across 80 countries.
What we found should be inetersting to every CISO and founder.
Source: https://t.co/BJA8bnvZuD
Check out our new look - https://t.co/ZpD73H48Nc
If you want to learn more about minimising risk of cyber security incidents - talk to us or request a DEMO!