PHP released fixes today for #PHP2Shell (CVE-2026-109618, CVE-2026-109619), two critical RCE vulnerabilities in PHP.
Update to 8.5.12, 8.4.27, 8.3.36, or 8.2.35 and restart PHP-FPM or your web server.
How the details leaked and why a version check isn’t enough 👇
🚀 Equixly August 2026 update is here!
🧭 Attack Trace: see how the agent reached each vuln
🤖 AI Red Teaming: now configurable in the UI
⚡ Faster pentest scans, clearer scan checks
🏷️ Discovery tags, better filters, bulk actions
🔗 Simpler MCP server URL
#AppSec#APISecurity
🚀 Equixly July 2026 update is here!
🕸️ Service Overview: your full attack surface on one radial map
🔗 Qualys integration: push findings to VMDR, pull asset inventory
🔍 Smarter Discovery: rate-limit awareness + exponential backoff
#API#AppSec#CyberSecurity#WAF
🚀 Equixly June 2026 update is here!
🧠 AI Red Teaming for your LLM
🕸️ Attack Surface graph
🔍 Discovery: scheduled scans, MCP detection, technology tagging & natural-language auth
📋 Three tailored reports per scan
#API#AppSec#CyberSecurity#AIRedTeaming
🚀 Equixly May 2026 update is here!
🧠 Knowledge settings for app-aware testing
🔍 Faster API and web app discovery
📋 Restyled compliance section
⚡ Multi-service creation from one upload
📥 API spec export
🤖 MCP Server coming soon
#API#AppSec#CyberSecurity
🚀 Equixly join WIN, to bring continuous API penetration testing to the @wiz_io ecosystem.
Wiz provide the visibility, while Equixly proves what can be exploited.
Wiz customer? Discuss adding it to your environment: https://t.co/o8CLxW24x5
Announcement: https://t.co/U5rEp68Jri
Next week we're in Birmingham for @NCSS_Cyber 📍.
Visit us at 5/M32 to see how traditional penetration tests are leaving your APIs exposed between tests.
Don't miss our talk at the show - The Case for Attacking Yourself: https://t.co/7UI8g8UFGZ
#APIsecurity#OffensiveSecurity
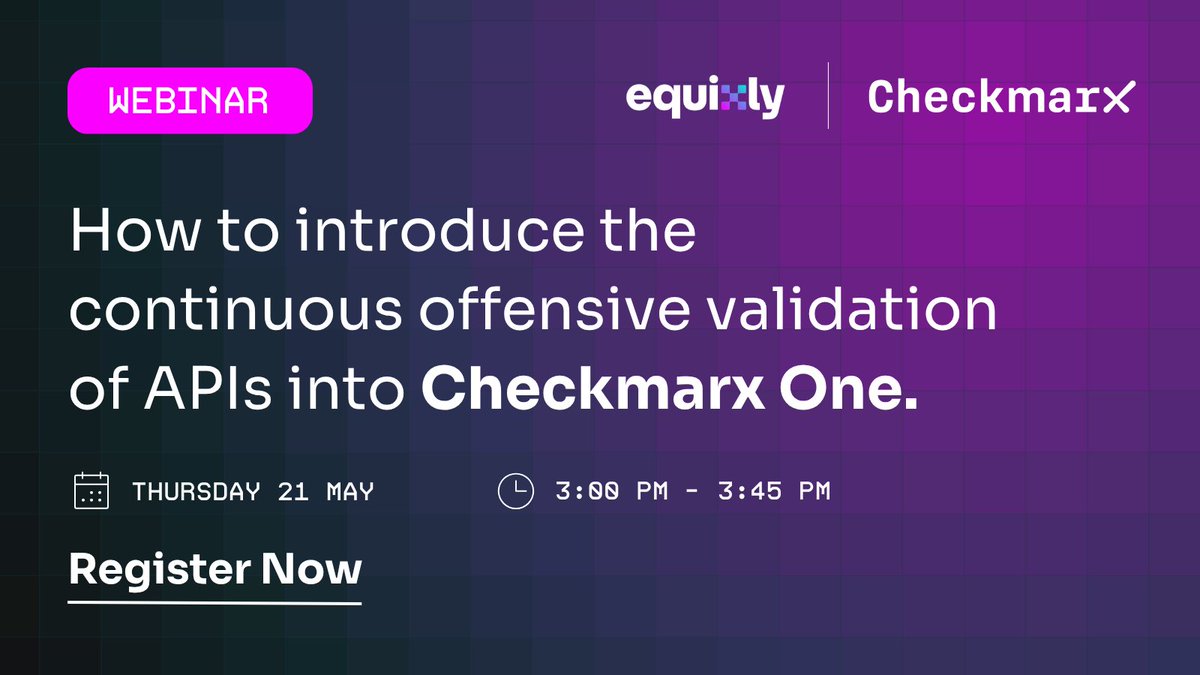
Join us and @Checkmarx as we discuss why modern appsec requires continuous security and how we empower Checkmarx customers with offensive validation of their APIs and application logic.
Register here: https://t.co/p9r7GwQMKD
#APIsecurity#ApplicationSecurity#Checkmarx
Replace periodic penetration tests with an always-on AI adversary.
Why only test your apps once a year, when you can shift to continuous pentesting?
Discover, attack, and validate your applications and APIs as they evolve.
See how it works: https://t.co/hZ9wD8OyPv
Modern APIs change daily, meaning that your previous pentest likely describes a past version, not the one running today.
Traditional, point-in-time penetration tests are no longer enough for API architectures.
Discover continuous testing with Equixly.
https://t.co/aL4EHX7soa
🚀 April 2026 Equixly Update!
🔍 Discovery: Auto-find & test APIs without specs.
🌐 DAST: Dynamic App Security Testing for SPAs & web apps!
🔗 Integrations: Native Jira, GitHub & ServiceNow syncing.
🛠 MCP Security: Dedicated testing for AI infrastructure.
#api#security
✨ Equixly’s February Product Update is here!
🎨 Redesigned UI for simpler navigation
🍪 Advanced cookie management for complex auth flows
⚡ Faster workflows and improved performance
Built to make API security testing easier, faster, and more reliable.
#API#security
📢 The January Equixly Update is live:
⭐ Polaris (upgraded AI assistant) for guided setup + scanning
🛡️ Vulnerability Assessment to spot CVEs + prioritize exploitable risk
📥 Import Burp history → create services from exports (great for undocumented APIs)
#api#security
📢 The December Equixly Update is live! 🚀 Focus: Saving your time. ⏳
✨ AI Assistant: Auto-repair API syntax errors
🔐 Auth Matrix: Bulk actions & advanced filters
📂 HAR Support: Import directly from traffic
✅ Pre-Scan: Verify auth settings instantly
#api#security
🚨 November 2025 Product Update! 🚨
🛠️ Repeater & Debug Section: Effortlessly test scripts within your scan environment.
🚀 Efficiency Boosts: Smarter scan management with bulk actions + scan archiving.
⏱️ Scan Speed: Enjoy fast scans with optimized startup.
#security#API
Check out the October 2025 product update!
✨ Automated authorization matrix to eliminate BOLA vulnerabilities.
🕒 Real-time scan insights.
🗂️ Enhanced project lifecycle management with unarchive and delete capabilities.
#security#API
Check out the September 2025 product update!
🚀 Webhooks for seamless integration with your workflows.
🔑 Authentication-specific dictionaries.
📊 Path rules for targeted and flexible scan scoping.
✅ Pre-scan authentication validation for faster, test setup.
#security#API