The Australian government poured billions into the NBN, and somehow we're still paying $85/month for 25 Mbps internet.
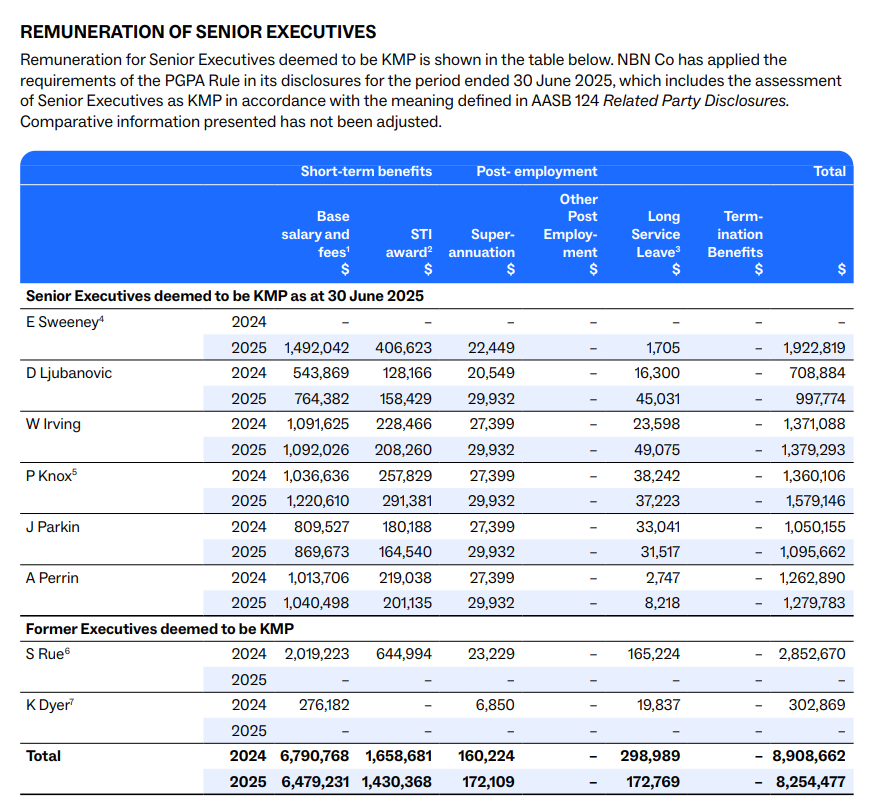
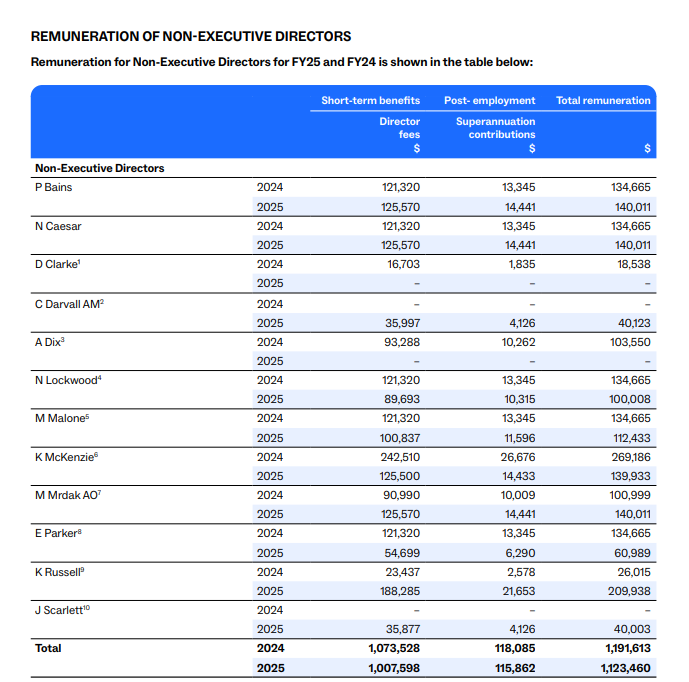
Meanwhile, executives at this 100% government-owned company received $8.25 MILLION in total remuneration in FY2025. Not to mention the ridiculous amount of double dipping non executing directors.
The economics of this entire operation deserve serious scrutiny.
https://t.co/JNQxVPJeTY
@RileyRalmuto Nice, you figured out the best memory layer ;) we run something eerily similar inhouse to what you've made and we even called our system Engram. Infinite monkeys with typewritters going strong.
Binance lost about $6.4B on Oct 29. Biggest crypto theft on record.
On Ethereum the attacker brought 50 presigned permissions for one hot wallet, one per possible nonce. One matched.
The wallet ran their code for 3h49m after that. Six more pulls after the first sweep.
Sorry to say,
Lazarus Group might be the hardest working security researchers in Web3.
Other security auditors charge $70K+ to find vulnerabilities.
Lazarus finds them for free by compromising the people, keys, multisigs and interfaces around the contracts.
Their Resume:
• Bybit: $1.5B
• Drift: $285M
• Bitget: $350M
• WazirX: $235M
• KelpDAO: $292M
• Ronin Bridge: $625M
• DMM Bitcoin: $308M
And many more.
Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
MEMBER HIGHLIGHT: @sigintzero_ 🇦🇺
Sydney security crew led by @ErrToCompile and @alteredlad. Creators of Tripwire, a circuit breaker for smart contracts
☑️ Rust and Solana audits
☑️ Sentinel AI code scans
☑️ Exploit write-ups: Drift, BonkDAO, DefiTuna
Read before you ship 👇
Real-time smart contract monitoring is useful, but having to rely on third-party infrastructure isn't always ideal.
Tripwire being free and self-hosted makes it a lot more interesting. Teams can run their own monitoring without adding another paid service to their stack.
Pretty useful for anyone building onchain.
@tarunchitra@zachxbt The next big wave will be self hosted security tools. If everyone is a full stack engineer, then their AI needs all the tooling available to fulfil that role
https://t.co/nNKXdRlopB
so about the $86m ledger drain. everyone’s screaming “ledger got hacked” again. i spent the evening digging and it’s dumber and scarier than that
there’s a shop in malaysia called cryptobilis that sells hardware wallets. ledger has it listed as an official authorized reseller since at least 2022, for malaysia, indonesia and the philippines. legit shop, real devices, years of normal customers
this spring the founders sell it. the deal comes with an NDA: they can’t tell anyone about the sale until october 19
by august the company registry shows one owner with 100%. some guy from heilongjiang, china
the shop keeps running like nothing happened. the site, the name and the “authorized by ledger” badge all stay up
then on oct 8 @MagicalTux posts photos of a ledger he cracked open. hidden under the screen there’s an extra little board with an LTE modem and an eSIM. it just watches the display. you set up your wallet, your 24 words show up, and they get sent out over mobile data. ledger’s genuine check doesn’t catch it because the actual ledger chip is real. his device came from malaysia
https://t.co/vRuBM0xIfR
that post does 120k views
22 hours later someone sweeps everything. 203 BTC hits two addresses in literally one block. ~$58m USDT moves on tron in the same hour. i added up all the wallets: ~$91m
about 7 hours after that ledger says “we’re investigating” and asks cryptobilis to pause sales
cryptobilis is still on ledger’s site as an authorized reseller
to be fair, nobody has officially tied the new owner to the bugged devices yet, and ledger hasn’t confirmed how it happened. but read it as a business plan:
get authorized, sell real stuff for years, quietly sell the company under an NDA, keep the badge, ship devices that phone home, then drain everything the second someone notices
and was ledger even told the shop got sold? nobody’s said so
“authorized reseller” means ledger trusted whoever ran the shop back in 2022. says nothing about who runs it today
bought your hardware wallet anywhere but the manufacturer? open it up today, ledger literally has a guide for that. then move to a fresh seed on a device bought direct
wonder who’s going to answer for this: the chinese frontman from heilongjiang, the shop’s previous owners, or ledger itself
@Ledger clearly needs to keep a much closer eye on who they call official resellers, and take way more responsibility for who sells their devices and how
A few things here: first, this is a game of chicken, like an actual game of chicken.
Abstract is scheduled to close on December 15. Minters will receive an egg on abstract, and on December 8th, one week before scheduled closure, you'll be able to "flee the coop".
Mint is 0.01 ETH. The first to flee will receive half of the mint price (0.005 ETH) on ETH, along with their Abstract Chicken.
0.003 ETH will remain in the coop.
Later exits receive bigger payouts. Anybody who does not exit before the chain closes forfeits both their NFT and ETH to the coop.
The last chicken to successfully exit gets half of that forfeited pot, the other half is distributed to everybody that successfully exited (weighted by exit order).
Some disclaimers: anything that remains on Abstract when the chain halts is unrecoverable FOREVER. That includes your egg, any ETH you hold, and anything else that you have on Abstract.
The abstract the team actually reached out yesterday and asked me not to do this (bring more liquidity ONTO the chain), but fuck it we ride.
After mint, you will be directed to the migration portal to make sure that you remove everything that you own from the chain. I'd recommend leaving $2 or so, just enough to trigger your exit when the time comes.
The "whiteboard defense:" I should be able to pull you aside at any moment and ask you to explain any customer-facing system you've shipped. You should be able to clearly explain how it works and defend the decisions you made. This is my benchmark for responsible AI usage.
I don't expect line-level familiarity with the code. I don't care if you remember the exact function name or implementation detail. You may not even know it. I don't care.
But if I ask "why did you do X instead of Y?", "what happens if this actor behaves maliciously?", "what data structure did you use here and why?", or "where does this fail?" you should be able to answer confidently.
For PoCs, demos, experiments, whatever: I don't care. Generate 100% of it and understand none of it. Speed over quality every time in those specific scenarios.
But if you're shipping customer-facing work, you can't be shipping things you don't understand at a high level.