UPDATE: Palo Alto Networks Unit 42 has retracted its earlier assessment linking the European government agency attack to PHP2Shell exploitation.
The attack involved a vulnerable PHP application, but Unit 42 says it cannot confirm initial access was tied to the specific PHP2Shell CVEs.
We've updated our report ↓
A breath of fresh air? Something other than PHP2Shell...
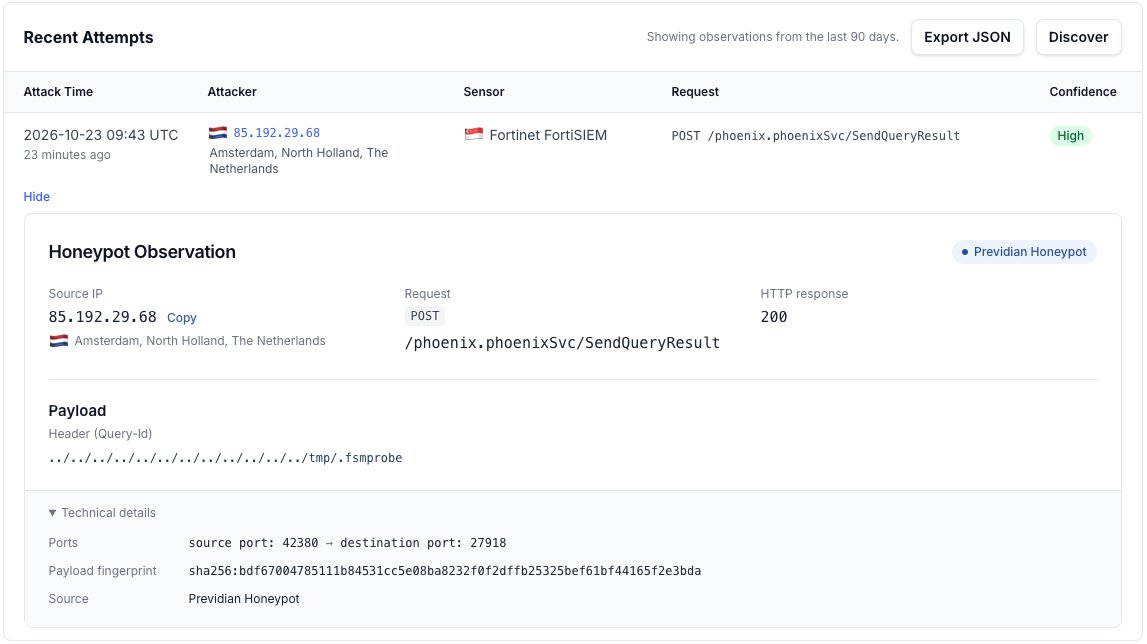
We detected an exploitation attempt against our FortiSIEM honeypot decoy, targeting CVE-2026-106173, Fortinet FortiSIEM’s path traversal vulnerability.
The request matches the file overwrite mode in @Horizon3ai PoC, published on 20 October 2026.
Observed on 23 October at 09:43:32 UTC: one request from one source IP (85.192.29[.]68).
• POST /phoenix.phoenixSvc/SendQueryResult
• HTTP/2 over TLS on TCP port 27918
• Twelve ../ sequences in the query-id header, targeting /tmp/.fsmprobe
• A 7-byte gRPC body carrying empty file contents
The request attempted to overwrite /tmp/.fsmprobe with an empty file. It contained no shell commands. This capture does not confirm a successful file write or code execution.
Upgrade to FortiSIEM 7.5.1 or later, following Fortinet’s advisory.
Restrict access to TCP 27918 and investigate unexpected /tmp/.fsmprobe artifacts.
Details and updates 👇
We're now seeing upload progress probes for PHP’s critical RCE vulnerability, CVE-2026-109618.
Our honeypots captured three HTTP requests from two source IPs, including PHP test code embedded in upload filenames.
Timeline (UTC):
• 20 Oct, 19:45: Previdian early-warning email sent.
• 21 Oct, 13:05: First attempt captured by our sensors.
• 21 Oct, 13:27: Follow-up warning emailed.
• 21 Oct, 13:30: PHP security fixes released.
• 21 Oct, 15:15: Previdian’s temporary virtual patch available.
Our initial warning preceded our first sensor observation by approximately 17 hours 21 minutes.
The evidence and IoCs:
• Observed source IPs: 166.1.90[.]109 & 43.134.82[.]85
• Multipart POST requests to /
• Fields: PHPSESSID and PHP_SESSION_UPLOAD_PROGRESS
• Two requests used the upload filename: <?php echo 1;?>.txt
Attackers did not manage to execute PHP or upload files in these first instances.
Update to PHP 8.2.35, 8.3.36, 8.4.27 or 8.5.12, or your vendor’s patched package.
Rumours of 2 Critical CVSS 10 PHP >= 5 RCE vulnerabilities to be released on October 22nd are starting to circulate 👀
No further details at this time, other than the Hacker News post.
RAPID RESPONSE: Huntress has become aware of a widespread security incident involving ConnectWise Cloud Backup (formerly SkyKick).
We’ve confirmed that an unknown threat actor abused the access they obtained in SkyKick to pivot to access customers' Microsoft 365 environments. 🧵