𝐓𝐇𝐄 𝐄𝐀𝐒𝐘 𝐖𝐀𝐘 𝐈𝐍 | 𝐒𝐢𝐭𝐮𝐚𝐭𝐢𝐨𝐧 𝟎𝟑: 𝐓𝐡𝐞 𝐨𝐫𝐠𝐚𝐧𝐢𝐬𝐚𝐭𝐢𝐨𝐧𝐚𝐥 𝐯𝐢𝐞𝐰
“Don’t use AI” sounds simple. But is it enough?
Employees are already using AI to summarise documents, prepare for meetings and speed up everyday tasks. The challenge for organisations is to make sure they can do this without exposing sensitive information.
That starts with clear, practical guidance.
🔹 𝐀𝐩𝐩𝐫𝐨𝐯𝐞𝐝 𝐭𝐨𝐨𝐥𝐬: Which AI tools can employees use for work?
🔹 𝐃𝐚𝐭𝐚-𝐬𝐡𝐚𝐫𝐢𝐧𝐠 𝐫𝐮𝐥𝐞𝐬: What information can be shared, and what must stay within approved systems?
🔹 𝐂𝐥𝐞𝐚𝐫 𝐫𝐞𝐩𝐨𝐫𝐭𝐢𝐧𝐠: What should employees do if they accidentally share sensitive information?
Policies alone aren’t enough. Employees also need appropriate access controls, visibility into AI use and a clear process for reporting mistakes.
𝐓𝐡𝐞 𝐪𝐮𝐞𝐬𝐭𝐢𝐨𝐧 𝐟𝐨𝐫 𝐬𝐞𝐜𝐮𝐫𝐢𝐭𝐲 𝐥𝐞𝐚𝐝𝐞𝐫𝐬:
Could an employee tell, without guessing, whether a customer document is safe to upload to an AI tool?
If the answer is unclear, that’s a gap worth addressing.
𝐒𝐚𝐟𝐞 𝐀𝐈 𝐚𝐝𝐨𝐩𝐭𝐢𝐨𝐧 𝐬𝐭𝐚𝐫𝐭𝐬 𝐰𝐢𝐭𝐡 𝐜𝐥𝐞𝐚𝐫 𝐠𝐮𝐢𝐝𝐚𝐧𝐜𝐞, 𝐧𝐨𝐭 𝐛𝐥𝐚𝐧𝐤𝐞𝐭 𝐰𝐚𝐫𝐧𝐢𝐧𝐠𝐬.
.
.
#TheEasyWayIn #CyberAwareness #CybersecurityAwarenessMonth #EventusSecurity
𝐓𝐇𝐄 𝐄𝐀𝐒𝐘 𝐖𝐀𝐘 𝐈𝐍 | 𝐒𝐢𝐭𝐮𝐚𝐭𝐢𝐨𝐧 𝟎𝟑: 𝐓𝐡𝐞 𝐫𝐞𝐯𝐞𝐚𝐥
A quick summary. An easy upload. But what information goes with it?
In Monday’s scenario, 𝐂 𝐰𝐚𝐬 𝐭𝐡𝐞 𝐫𝐢𝐠𝐡𝐭 𝐬𝐭𝐚𝐫𝐭𝐢𝐧𝐠 𝐩𝐨𝐢𝐧𝐭: check your organisation’s AI and data-sharing rules, then use an approved method.
Removing customer names may not be enough. Contact details, internal notes and other information can still identify a person or customer account, or reveal confidential business information.
AI can save time. Before using it, check 𝐰𝐡𝐚𝐭 𝐢𝐧𝐟𝐨𝐫𝐦𝐚𝐭𝐢𝐨𝐧 𝐲𝐨𝐮’𝐫𝐞 𝐬𝐡𝐚𝐫𝐢𝐧𝐠, 𝐡𝐨𝐰 𝐭𝐡𝐞 𝐭𝐨𝐨𝐥 𝐡𝐚𝐧𝐝𝐥𝐞𝐬 𝐢𝐭 𝐚𝐧𝐝 𝐰𝐡𝐞𝐭𝐡𝐞𝐫 𝐢𝐭’𝐬 𝐚𝐩𝐩𝐫𝐨𝐯𝐞𝐝 𝐟𝐨𝐫 𝐭𝐡𝐚𝐭 𝐢𝐧𝐟𝐨𝐫𝐦𝐚𝐭𝐢𝐨𝐧 𝐚𝐧𝐝 𝐭𝐚𝐬𝐤.
𝐓𝐡𝐞 𝐡𝐚𝐛𝐢𝐭:
Before you paste or upload, ask:
𝐀𝐦 𝐈 𝐚𝐥𝐥𝐨𝐰𝐞𝐝 𝐭𝐨 𝐬𝐡𝐚𝐫𝐞 𝐭𝐡𝐢𝐬 𝐢𝐧𝐟𝐨𝐫𝐦𝐚𝐭𝐢𝐨𝐧 𝐰𝐢𝐭𝐡 𝐭𝐡𝐢𝐬 𝐭𝐨𝐨𝐥?
If you’re unsure, check with the relevant team before proceeding.
On #Friday, we’ll look at how organisations can make safe AI use easier for everyone.
.
.
#TheEasyWayIn #DontMakeItEasyForThem #Cybersecurity #CybersecurityAwarenessMonth #EventusSecurity #SecureWithEventus
𝐖𝐞'𝐫𝐞 𝐡𝐞𝐚𝐝𝐢𝐧𝐠 𝐭𝐨 𝐁𝐥𝐚𝐜𝐤 𝐇𝐚𝐭 𝐈𝐧𝐝𝐢𝐚 𝟐𝟎𝟐𝟔!
Eventus Security is excited to be an 𝐄𝐱𝐡𝐢𝐛𝐢𝐭 𝐏𝐚𝐫𝐭𝐧𝐞𝐫 at Black Hat India 2026, bringing together cybersecurity professionals, industry leaders and innovators for three days of learning, networking and collaboration.
Our team will be there to exchange perspectives, share insights, and discuss how organisations can strengthen their security operations and cyber resilience.
📅 𝟮𝟴–𝟯𝟬 𝗢𝗰𝘁𝗼𝗯𝗲𝗿 𝟮𝟬𝟮𝟲
📍 𝗦𝗵𝗲𝗿𝗮𝘁𝗼𝗻 𝗚𝗿𝗮𝗻𝗱, 𝗕𝗲𝗻𝗴𝗮𝗹𝘂𝗿𝘂
📌 𝗕𝗼𝗼𝘁𝗵 #𝟮𝟮
Whether you're exploring Managed SOC, AI-driven security operations, Managed XDR or broader Cyber Resilience capabilities, we'd be delighted to connect.
𝐀𝐭𝐭𝐞𝐧𝐝𝐢𝐧𝐠 𝐁𝐥𝐚𝐜𝐤 𝐇𝐚𝐭 𝐈𝐧𝐝𝐢𝐚? 𝐒𝐭𝐨𝐩 𝐛𝐲 𝐁𝐨𝐨𝐭𝐡 #𝟐𝟐 𝐚𝐧𝐝 𝐬𝐚𝐲 𝐡𝐞𝐥𝐥𝐨. 𝐖𝐞 𝐥𝐨𝐨𝐤 𝐟𝐨𝐫𝐰𝐚𝐫𝐝 𝐭𝐨 𝐬𝐞𝐞𝐢𝐧𝐠 𝐲𝐨𝐮 𝐭𝐡𝐞𝐫𝐞!
.
.
#BlackHatIndia2026 #EventusSecurity #CyberSecurity #ManagedSOC #CyberResilience #ManagedXDR
Last week, we explored how a familiar-looking sign-in page can deceive us. In Week 3 of “The Easy Way In,” we look at another everyday decision: using AI to get work done faster.
𝐓𝐇𝐄 𝐄𝐀𝐒𝐘 𝐖𝐀𝐘 𝐈𝐍 | 𝐒𝐢𝐭𝐮𝐚𝐭𝐢𝐨𝐧 𝟎𝟑: 𝐓𝐡𝐞 𝐡𝐞𝐥𝐩𝐟𝐮𝐥 𝐀𝐈 𝐭𝐨𝐨𝐥
You have a long customer document to summarise before a meeting. An AI tool can do it in seconds.
The document contains customer names, contact details and internal notes. You haven’t checked whether the tool is approved for handling this information.
𝐖𝐡𝐚𝐭 𝐰𝐨𝐮𝐥𝐝 𝐲𝐨𝐮 𝐝𝐨?
𝐀. Upload it. The time saved is worth it.
𝐁. Remove the customer names and upload the rest.
𝐂. Check your organisation’s AI and data-sharing rules, then use an approved method.
𝐖𝐡𝐢𝐜𝐡 𝐨𝐩𝐭𝐢𝐨𝐧 𝐰𝐨𝐮𝐥𝐝 𝐲𝐨𝐮 𝐜𝐡𝐨𝐨𝐬𝐞, 𝐚𝐧𝐝 𝐰𝐡𝐲? Share your answer in the comments.
We’ll unpack the risk on Wednesday.
𝘍𝘪𝘤𝘵𝘪𝘰𝘯𝘢𝘭 𝘴𝘤𝘦𝘯𝘢𝘳𝘪𝘰 𝘣𝘢𝘴𝘦𝘥 𝘰𝘯 𝘢𝘯 𝘦𝘷𝘦𝘳𝘺𝘥𝘢𝘺 𝘸𝘰𝘳𝘬𝘱𝘭𝘢𝘤𝘦 𝘥𝘦𝘤𝘪𝘴𝘪𝘰𝘯.
.
.
#TheEasyWayIn #DontMakeItEasyForThem #CybersecurityAwarenessMonth #EventusSecurity
𝐓𝐇𝐄 𝐄𝐀𝐒𝐘 𝐖𝐀𝐘 𝐈𝐍 | 𝐒𝐢𝐭𝐮𝐚𝐭𝐢𝐨𝐧 𝟎𝟐: 𝐓𝐡𝐞 𝐨𝐫𝐠𝐚𝐧𝐢𝐬𝐚𝐭𝐢𝐨𝐧𝐚𝐥 𝐫𝐞𝐬𝐩𝐨𝐧𝐬𝐞
A stolen password shouldn’t be the end of the story.
In this week’s situation, the safest first step was simple: open the service through a known, trusted route rather than the link in the message.
But even careful people can be fooled by a convincing sign-in page. Organisations need to plan for that.
Strong authentication helps. So do:
🔹𝐕𝐢𝐬𝐢𝐛𝐢𝐥𝐢𝐭𝐲: spotting unusual sign-ins, access changes and activity outside a user’s normal pattern
🔹𝐄𝐚𝐬𝐲 𝐫𝐞𝐩𝐨𝐫𝐭𝐢𝐧𝐠: a simple way for employees to flag suspected credential theft, without fear of blame
🔹𝐑𝐚𝐩𝐢𝐝 𝐫𝐞𝐬𝐩𝐨𝐧𝐬𝐞: a clear process so security teams can investigate and act fast
𝐓𝐡𝐞 𝐪𝐮𝐞𝐬𝐭𝐢𝐨𝐧 𝐟𝐨𝐫 𝐬𝐞𝐜𝐮𝐫𝐢𝐭𝐲 𝐥𝐞𝐚𝐝𝐞𝐫𝐬:
If someone entered their credentials on a fake page today, how quickly would your team know, and how quickly could you respond?
Awareness, detection and response work best together.
👉𝐂𝐨𝐦𝐢𝐧𝐠 𝐌𝐨𝐧𝐝𝐚𝐲: 𝐒𝐢𝐭𝐮𝐚𝐭𝐢𝐨𝐧 𝟎𝟑 | 𝐓𝐡𝐞 𝐡𝐞𝐥𝐩𝐟𝐮𝐥 𝐀𝐈 𝐭𝐨𝐨𝐥
A document to summarise. A meeting to prepare for. An AI tool that can do it in seconds. Before you upload, what would you check?
.
.
#TheEasyWayIn #DontMakeItEasyForThem #CybersecurityAwarenessMonth #EventusSecurity
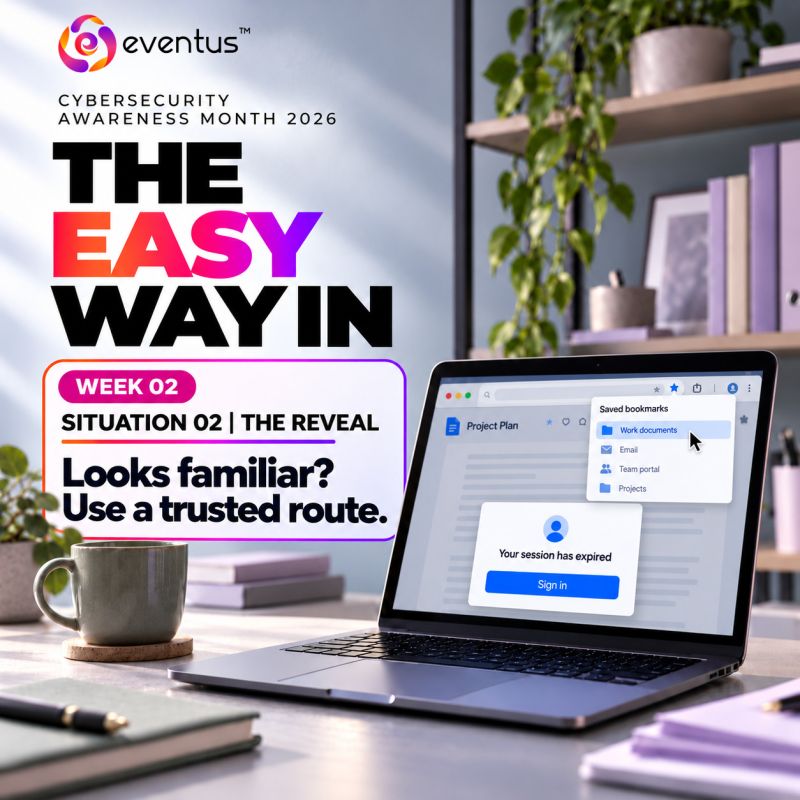
𝐓𝐇𝐄 𝐄𝐀𝐒𝐘 𝐖𝐀𝐘 𝐈𝐍 | 𝐒𝐢𝐭𝐮𝐚𝐭𝐢𝐨𝐧 𝟎𝟐: 𝐓𝐡𝐞 𝐫𝐞𝐯𝐞𝐚𝐥
For Monday’s unexpected sign-in page, 𝐁 𝐰𝐚𝐬 𝐭𝐡𝐞 𝐬𝐚𝐟𝐞𝐬𝐭 𝐟𝐢𝐫𝐬𝐭 𝐬𝐭𝐞𝐩: open the service through your usual app or saved bookmark.
A familiar logo is easy to copy. A “session expired” message can make a login request feel routine. Neither confirms that the page is genuine.
Rather than entering your credentials on the page that appeared, use your trusted route to check whether you need to sign in. If your session really has expired, you can sign in there.
𝐀𝐥𝐫𝐞𝐚𝐝𝐲 𝐞𝐧𝐭𝐞𝐫𝐞𝐝 𝐲𝐨𝐮𝐫 𝐜𝐫𝐞𝐝𝐞𝐧𝐭𝐢𝐚𝐥𝐬 𝐨𝐧 𝐚 𝐩𝐚𝐠𝐞 𝐲𝐨𝐮 𝐧𝐨𝐰 𝐬𝐮𝐬𝐩𝐞𝐜𝐭? Report it to your security team promptly. The sooner they know, the sooner they can act to protect the account.
𝐓𝐡𝐞 𝐡𝐚𝐛𝐢𝐭: An unexpected login prompt is a reason to verify, even when it looks familiar.
𝐖𝐡𝐚𝐭 𝐰𝐨𝐮𝐥𝐝 𝐲𝐨𝐮 𝐜𝐡𝐞𝐜𝐤 𝐟𝐢𝐫𝐬𝐭: 𝐭𝐡𝐞 𝐩𝐚𝐠𝐞’𝐬 𝐚𝐝𝐝𝐫𝐞𝐬𝐬, 𝐡𝐨𝐰 𝐲𝐨𝐮 𝐫𝐞𝐚𝐜𝐡𝐞𝐝 𝐢𝐭, 𝐨𝐫 𝐰𝐡𝐞𝐭𝐡𝐞𝐫 𝐭𝐡𝐞 𝐬𝐚𝐦𝐞 𝐩𝐫𝐨𝐦𝐩𝐭 𝐚𝐩𝐩𝐞𝐚𝐫𝐬 𝐭𝐡𝐫𝐨𝐮𝐠𝐡 𝐲𝐨𝐮𝐫 𝐮𝐬𝐮𝐚𝐥 𝐚𝐩𝐩?
On Friday, we’ll explore how organisations can make safer responses easier for everyone.
#TheEasyWayIn #DontMakeItEasyForThem #CybersecurityAwarenessMonth #EventusSecurity
𝐓𝐨𝐦𝐨𝐫𝐫𝐨𝐰, 𝐰𝐞 𝐬𝐭𝐨𝐩 𝐚𝐬𝐤𝐢𝐧𝐠 “𝐖𝐡𝐚𝐭 𝐝𝐨𝐞𝐬 𝐃𝐏𝐃𝐏𝐀 𝐬𝐚𝐲?”
𝐀𝐧𝐝 𝐬𝐭𝐚𝐫𝐭 𝐚𝐬𝐤𝐢𝐧𝐠:
“𝐀𝐫𝐞 𝐰𝐞 𝐚𝐜𝐭𝐮𝐚𝐥𝐥𝐲 𝐫𝐞𝐚𝐝𝐲?”
Because DPDPA readiness isn't just about having a policy on paper.
It is about being able to answer the practical questions:
• Where is personal data collected, stored, and processed?
• Who is accountable for it?
• How are privacy obligations being operationalised?
• What happens when something goes wrong?
• Can your organisation demonstrate that it is prepared?
𝐓𝐡𝐞𝐬𝐞 𝐚𝐫𝐞𝐧’𝐭 𝐭𝐡𝐞𝐨𝐫𝐞𝐭𝐢𝐜𝐚𝐥 𝐪𝐮𝐞𝐬𝐭𝐢𝐨𝐧𝐬.
They are the questions that came up repeatedly in conversations with 𝟐𝟎𝟎+ 𝐞𝐧𝐭𝐞𝐫𝐩𝐫𝐢𝐬𝐞𝐬.
Tomorrow, we unpack them.
𝐃𝐏𝐃𝐏 𝐀𝐜𝐭 𝟐𝟎𝟐𝟑: 𝐌𝐲𝐭𝐡 𝐯𝐬 𝐑𝐞𝐚𝐥𝐢𝐭𝐲 — 𝐖𝐡𝐚𝐭 𝟐𝟎𝟎+ 𝐄𝐧𝐭𝐞𝐫𝐩𝐫𝐢𝐬𝐞 𝐂𝐨𝐧𝐯𝐞𝐫𝐬𝐚𝐭𝐢𝐨𝐧𝐬 𝐓𝐚𝐮𝐠𝐡𝐭 𝐔𝐬
📅 𝐓𝐨𝐦𝐨𝐫𝐫𝐨𝐰 | 𝟏𝟒 𝐎𝐜𝐭𝐨𝐛𝐞𝐫
⏰ 𝟑:𝟎𝟎 𝐏𝐌 𝐈𝐒𝐓
Speaker: Shahroz Ali — Founder & CBO, PurpleCop
Co-host: Sudhanshu Dashora — Regional Account Manager, Eventus Security
💬 Live Q&A | 🎓 Certificate of DPDPA Attendance | ✅ CPE Credit Eligible
𝐇𝐚𝐯𝐞 𝐚 𝐃𝐏𝐃𝐏𝐀 𝐪𝐮𝐞𝐬𝐭𝐢𝐨𝐧 𝐲𝐨𝐮’𝐫𝐞 𝐬𝐭𝐢𝐥𝐥 𝐧𝐨𝐭 𝐬𝐮𝐫𝐞 𝐚𝐛𝐨𝐮𝐭?
𝐁𝐫𝐢𝐧𝐠 𝐢𝐭 𝐭𝐨 𝐭𝐡𝐞 𝐬𝐞𝐬𝐬𝐢𝐨𝐧.
👉 Register: https://t.co/lVlhbJLe3z
.
.
#DPDPA #DataPrivacy #DataProtection #PrivacyCompliance #Cybersecurity #EventusSecurity
Last week, we explored an urgent request from a senior leader. For Week 2 of “The Easy Way In,” we turn to something more routine: a familiar-looking sign-in page.
𝐓𝐇𝐄 𝐄𝐀𝐒𝐘 𝐖𝐀𝐘 𝐈𝐍 | 𝐒𝐢𝐭𝐮𝐚𝐭𝐢𝐨𝐧 𝟎𝟐: 𝐓𝐡𝐞 𝐫𝐨𝐮𝐭𝐢𝐧𝐞 𝐥𝐨𝐠𝐢𝐧
You’re reviewing a shared document when a sign-in page appears. It shows the familiar logo and says your session has expired.
You’ve signed in to this service many times. Everything looks normal, and you want to get back to work.
𝐖𝐡𝐚𝐭 𝐰𝐨𝐮𝐥𝐝 𝐲𝐨𝐮 𝐝𝐨 𝐟𝐢𝐫𝐬𝐭?
𝐀. Enter your credentials and continue.
𝐁. Open the service through your usual app or saved bookmark to check whether you need to sign in.
𝐂. Ask a colleague whether they’ve seen the same page.
𝐖𝐡𝐚𝐭’𝐬 𝐲𝐨𝐮𝐫 𝐜𝐡𝐨𝐢𝐜𝐞: 𝐀, 𝐁 𝐨𝐫 𝐂? Tell us in the comments.
On Wednesday, we’ll unpack the risk behind this routine-looking request.
𝘍𝘪𝘤𝘵𝘪𝘰𝘯𝘢𝘭 𝘴𝘤𝘦𝘯𝘢𝘳𝘪𝘰 𝘣𝘢𝘴𝘦𝘥 𝘰𝘯 𝘢 𝘤𝘰𝘮𝘮𝘰𝘯 𝘢𝘵𝘵𝘢𝘤𝘬 𝘱𝘢𝘵𝘵𝘦𝘳𝘯.
.
.
#TheEasyWayIn #CybersecurityAwarenessMonth #EventusSecurity #CyberHygiene #StayCyberSafe #CyberAwareness
𝐓𝐇𝐄 𝐄𝐀𝐒𝐘 𝐖𝐀𝐘 𝐈𝐍 | 𝐒𝐢𝐭𝐮𝐚𝐭𝐢𝐨𝐧 𝟎𝟏: 𝐓𝐡𝐞 𝐨𝐫𝐠𝐚𝐧𝐢𝐬𝐚𝐭𝐢𝐨𝐧𝐚𝐥 𝐫𝐞𝐬𝐩𝐨𝐧𝐬𝐞
𝐂𝐚𝐧 𝐩𝐞𝐨𝐩𝐥𝐞 𝐯𝐞𝐫𝐢𝐟𝐲 𝐰𝐢𝐭𝐡𝐨𝐮𝐭 𝐬𝐥𝐨𝐰𝐢𝐧𝐠 𝐞𝐯𝐞𝐫𝐲𝐭𝐡𝐢𝐧𝐠 𝐝𝐨𝐰𝐧?
In this week’s situation, the safest first step was to verify the request through a known, trusted channel.
But “check before you act” works only when employees know 𝐡𝐨𝐰 𝐭𝐨 𝐜𝐡𝐞𝐜𝐤 and feel comfortable doing it, even when the request appears to come from a senior leader.
Organisations can make that easier with:
🔹 A clear verification route using known contact details.
🔹 A second approval for high-risk requests where appropriate.
🔹 An easy way to report suspicious messages and get timely support.
Leaders also set the tone. 𝐀 𝐪𝐮𝐢𝐜𝐤 𝐜𝐡𝐞𝐜𝐤 𝐬𝐡𝐨𝐮𝐥𝐝 𝐛𝐞 𝐰𝐞𝐥𝐜𝐨𝐦𝐞, 𝐞𝐯𝐞𝐧 𝐰𝐡𝐞𝐧 𝐚 𝐫𝐞𝐪𝐮𝐞𝐬𝐭 𝐢𝐬 𝐮𝐫𝐠𝐞𝐧𝐭.
Ask your team one question today:
𝐈𝐟 𝐚𝐧 𝐮𝐫𝐠𝐞𝐧𝐭 𝐫𝐞𝐪𝐮𝐞𝐬𝐭 𝐚𝐩𝐩𝐞𝐚𝐫𝐞𝐝 𝐭𝐨 𝐜𝐨𝐦𝐞 𝐟𝐫𝐨𝐦 𝐚 𝐬𝐞𝐧𝐢𝐨𝐫 𝐥𝐞𝐚𝐝𝐞𝐫, 𝐰𝐨𝐮𝐥𝐝 𝐞𝐯𝐞𝐫𝐲𝐨𝐧𝐞 𝐤𝐧𝐨𝐰 𝐡𝐨𝐰 𝐭𝐨 𝐯𝐞𝐫𝐢𝐟𝐲 𝐢𝐭?
Make verification a normal part of work. A brief pause can make an attacker’s job much harder.
𝐒𝐭𝐚𝐲 𝐭𝐮𝐧𝐞𝐝 𝐟𝐨𝐫 𝐒𝐢𝐭𝐮𝐚𝐭𝐢𝐨𝐧 𝟎𝟐 𝐨𝐧 𝐌𝐨𝐧𝐝𝐚𝐲. 𝐀 𝐧𝐞𝐰 𝐬𝐜𝐞𝐧𝐚𝐫𝐢𝐨. 𝐖𝐡𝐚𝐭 𝐰𝐨𝐮𝐥𝐝 𝐲𝐨𝐮 𝐝𝐨?
.
.
#TheEasyWayIn #DontMakeItEasyForThem #SecureWithEventus #CybersecurityAwarenessMonth #EventusSecurity
𝐒𝐚𝐮𝐝𝐢 𝐞𝐧𝐭𝐞𝐫𝐩𝐫𝐢𝐬𝐞𝐬 𝐚𝐫𝐞 𝐭𝐫𝐚𝐧𝐬𝐟𝐨𝐫𝐦𝐢𝐧𝐠 𝐟𝐚𝐬𝐭. 𝐒𝐞𝐜𝐮𝐫𝐢𝐭𝐲 𝐨𝐩𝐞𝐫𝐚𝐭𝐢𝐨𝐧𝐬 𝐜𝐚𝐧'𝐭 𝐚𝐟𝐟𝐨𝐫𝐝 𝐭𝐨 𝐛𝐞𝐜𝐨𝐦𝐞 𝐭𝐡𝐞 𝐛𝐨𝐭𝐭𝐥𝐞𝐧𝐞𝐜𝐤.
• New cloud workloads.
• New digital services.
• New identities.
• New applications.
• New integrations.
As organisations across #SaudiArabia continue to scale their digital environments, the challenge for security teams isn't simply gaining more visibility.
It's maintaining 𝐞𝐟𝐟𝐞𝐜𝐭𝐢𝐯𝐞 𝐬𝐞𝐜𝐮𝐫𝐢𝐭𝐲 𝐨𝐩𝐞𝐫𝐚𝐭𝐢𝐨𝐧𝐬 𝐚𝐬 𝐭𝐡𝐞 𝐞𝐧𝐯𝐢𝐫𝐨𝐧𝐦𝐞𝐧𝐭 𝐜𝐡𝐚𝐧𝐠𝐞𝐬.
• Can new assets be brought under monitoring quickly?
• Can analysts maintain context as infrastructure expands?
• Can security teams identify which changes introduce meaningful risk?
• Can detection capabilities evolve alongside the environment they're protecting?
This is where the SOC needs to operate differently.
Not as a static monitoring function, but as a security capability that continuously adapts to the organisation.
𝐁𝐞𝐜𝐚𝐮𝐬𝐞 𝐰𝐡𝐞𝐧 𝐭𝐡𝐞 𝐛𝐮𝐬𝐢𝐧𝐞𝐬𝐬 𝐜𝐡𝐚𝐧𝐠𝐞𝐬 𝐟𝐚𝐬𝐭𝐞𝐫 𝐭𝐡𝐚𝐧 𝐬𝐞𝐜𝐮𝐫𝐢𝐭𝐲 𝐨𝐩𝐞𝐫𝐚𝐭𝐢𝐨𝐧𝐬, 𝐯𝐢𝐬𝐢𝐛𝐢𝐥𝐢𝐭𝐲 𝐠𝐚𝐩𝐬 𝐜𝐚𝐧 𝐟𝐨𝐥𝐥𝐨𝐰.
For Saudi security leaders, SOC maturity isn't only about what you can detect today.
𝐈𝐭'𝐬 𝐚𝐛𝐨𝐮𝐭 𝐰𝐡𝐞𝐭𝐡𝐞𝐫 𝐲𝐨𝐮𝐫 𝐬𝐞𝐜𝐮𝐫𝐢𝐭𝐲 𝐨𝐩𝐞𝐫𝐚𝐭𝐢𝐨𝐧𝐬 𝐜𝐚𝐧 𝐤𝐞𝐞𝐩 𝐩𝐚𝐜𝐞 𝐰𝐢𝐭𝐡 𝐰𝐡𝐚𝐭 𝐭𝐡𝐞 𝐛𝐮𝐬𝐢𝐧𝐞𝐬𝐬 𝐛𝐞𝐜𝐨𝐦𝐞𝐬 𝐭𝐨𝐦𝐨𝐫𝐫𝐨𝐰.
👉 Speak to our Expert. → https://t.co/yyoENbN5BC
.
.
#SaudiArabia #KSA #SaudiCyberSecurity #MiddleEastCyberSecurity #SOC #ManagedSOC #SOCaaS #SecurityOperations #CyberResilience #CISO #EventusSecurity #SecureWithEventus
𝐓𝐇𝐄 𝐄𝐀𝐒𝐘 𝐖𝐀𝐘 𝐈𝐍 | 𝐒𝐢𝐭𝐮𝐚𝐭𝐢𝐨𝐧 𝟎𝟏: 𝐓𝐡𝐞 𝐑𝐞𝐯𝐞𝐚𝐥
In Monday’s situation, 𝐂 𝐰𝐚𝐬 𝐭𝐡𝐞 𝐬𝐚𝐟𝐞𝐬𝐭 𝐟𝐢𝐫𝐬𝐭 𝐬𝐭𝐞𝐩: contact the person through a number or channel you already know and use.
An attacker can impersonate a senior leader, create urgency and discourage you from checking. Replying to the same suspicious message could leave you talking to the attacker.
𝐓𝐡𝐞 𝐡𝐚𝐛𝐢𝐭: Pause and verify unusual requests independently, especially when they involve money, sensitive files or a change in process.
A familiar name and an urgent request are reasons to check, rather than rush.
𝐖𝐡𝐚𝐭 𝐰𝐨𝐮𝐥𝐝 𝐡𝐚𝐯𝐞 𝐦𝐚𝐝𝐞 𝐲𝐨𝐮 𝐩𝐚𝐮𝐬𝐞: 𝐭𝐡𝐞 𝐮𝐫𝐠𝐞𝐧𝐜𝐲, 𝐭𝐡𝐞 𝐧𝐞𝐰 𝐚𝐝𝐝𝐫𝐞𝐬𝐬 𝐨𝐫 “𝐈’𝐥𝐥 𝐞𝐱𝐩𝐥𝐚𝐢𝐧 𝐥𝐚𝐭𝐞𝐫”?
On Friday, we’ll look at how organisations can make that check easier.
.
.
#TheEasyWayIn #CybersecurityAwarenessMonth #DontMakeItEasyForThem #EventusSecurity #SecureWithEventus
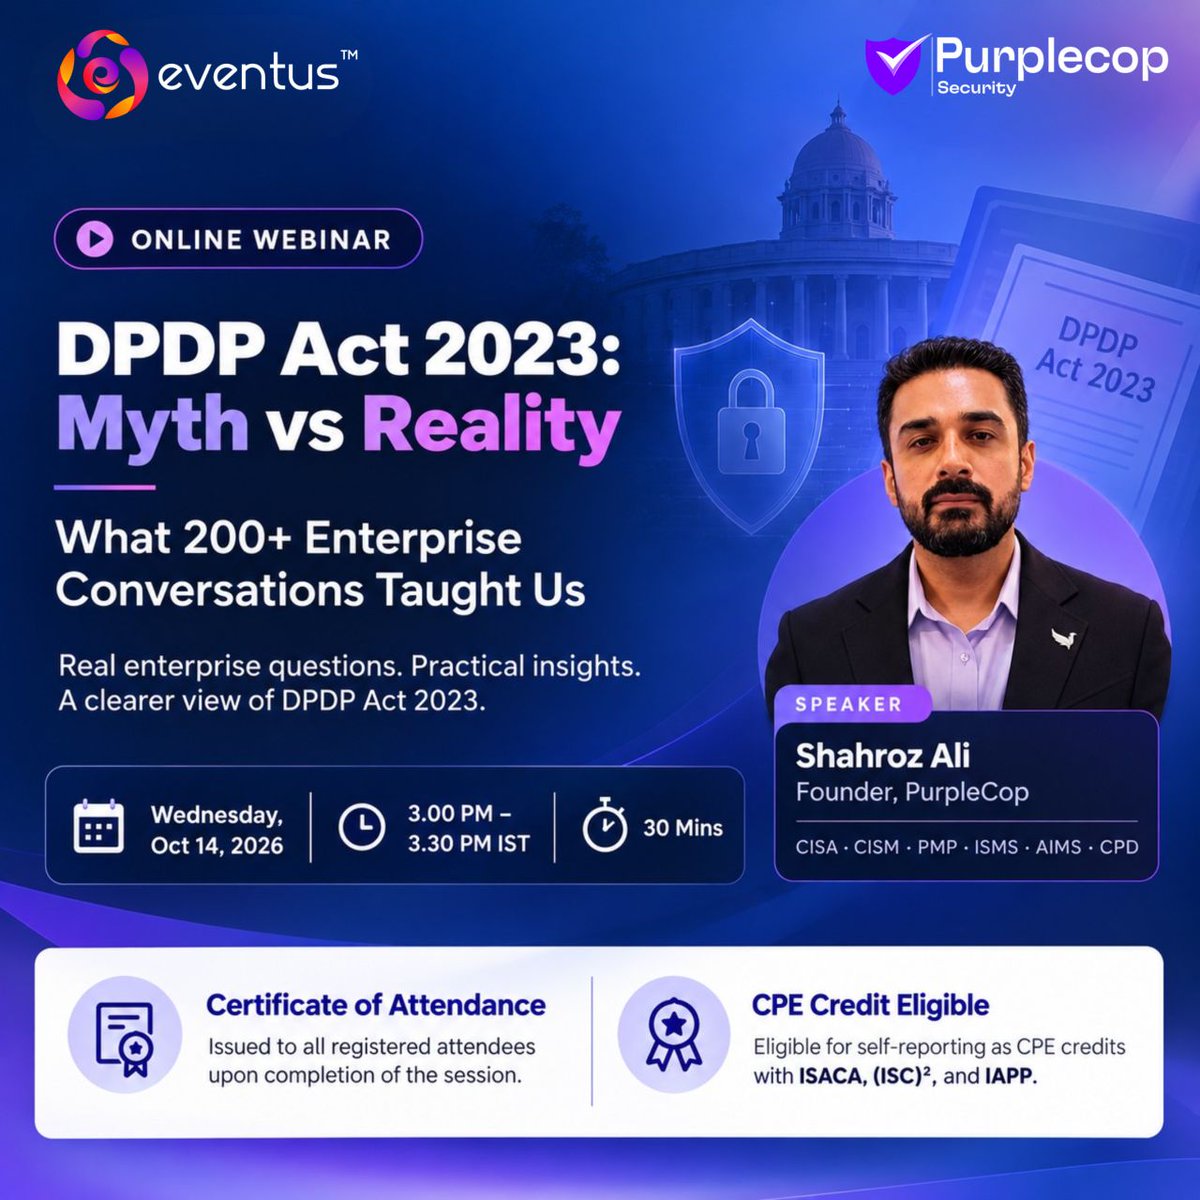
𝐃𝐏𝐃𝐏 𝐀𝐂𝐓 𝟐𝟎𝟐𝟑: 𝐌𝐘𝐓𝐇 𝐕𝐒 𝐑𝐄𝐀𝐋𝐈𝐓𝐘
“We have ISO 27001, so we’re covered.”
“DPDPA is mainly an IT responsibility.”
“We still have 18 months. Why the rush?”
“We’ll report the breach once the investigation is complete.”
These are some of the questions and assumptions we’ve heard in conversations with 𝟐𝟎𝟎+ 𝐞𝐧𝐭𝐞𝐫𝐩𝐫𝐢𝐬𝐞𝐬.
But what does the DPDP Act actually require?
Join us as we separate what’s assumed from what’s actually required.
𝐃𝐏𝐃𝐏 𝐀𝐜𝐭 𝟐𝟎𝟐𝟑: 𝐌𝐲𝐭𝐡 𝐯𝐬 𝐑𝐞𝐚𝐥𝐢𝐭𝐲 — 𝐖𝐡𝐚𝐭 𝟐𝟎𝟎+ 𝐄𝐧𝐭𝐞𝐫𝐩𝐫𝐢𝐬𝐞 𝐂𝐨𝐧𝐯𝐞𝐫𝐬𝐚𝐭𝐢𝐨𝐧𝐬 𝐓𝐚𝐮𝐠𝐡𝐭 𝐔𝐬
📅 𝐖𝐞𝐝𝐧𝐞𝐬𝐝𝐚𝐲, 𝟏𝟒 𝐎𝐜𝐭𝐨𝐛𝐞𝐫
⏰ 𝟑:𝟎𝟎 𝐏𝐌 𝐈𝐒𝐓
We’ll unpack the questions enterprises are actually asking around 𝐜𝐨𝐧𝐬𝐞𝐧𝐭, 𝐚𝐜𝐜𝐨𝐮𝐧𝐭𝐚𝐛𝐢𝐥𝐢𝐭𝐲, 𝐛𝐫𝐞𝐚𝐜𝐡 𝐫𝐞𝐩𝐨𝐫𝐭𝐢𝐧𝐠, 𝐒𝐢𝐠𝐧𝐢𝐟𝐢𝐜𝐚𝐧𝐭 𝐃𝐚𝐭𝐚 𝐅𝐢𝐝𝐮𝐜𝐢𝐚𝐫𝐢𝐞𝐬, 𝐭𝐢𝐦𝐞𝐥𝐢𝐧𝐞𝐬 𝐚𝐧𝐝 𝐩𝐞𝐧𝐚𝐥𝐭𝐢𝐞𝐬.
Speaker:
Shahroz Ali — Founder & CBO, PurpleCop
Co-host:
Sudhanshu Dashora — Regional Account Manager, Eventus Security
🎓 Certificate of DPDPA Attendance
✅ CPE Credit Eligible
💬 Live Q&A
𝐇𝐚𝐯𝐞 𝐚 𝐃𝐏𝐃𝐏𝐀 𝐪𝐮𝐞𝐬𝐭𝐢𝐨𝐧 𝐲𝐨𝐮’𝐫𝐞 𝐬𝐭𝐢𝐥𝐥 𝐮𝐧𝐬𝐮𝐫𝐞 𝐚𝐛𝐨𝐮𝐭? 𝐁𝐫𝐢𝐧𝐠 𝐢𝐭 𝐭𝐨 𝐭𝐡𝐞 𝐬𝐞𝐬𝐬𝐢𝐨𝐧.
👉 Register: https://t.co/lVlhbJLLT7
.
.
#DPDPA #DataPrivacy #DataProtection #PrivacyCompliance #Cybersecurity #EventusSecurity
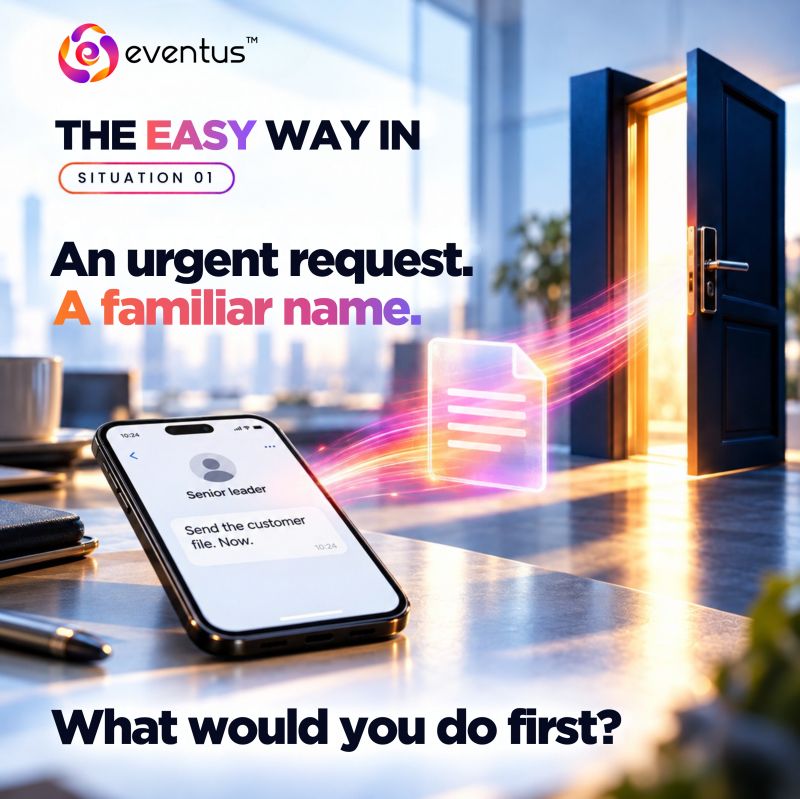
𝐓𝐇𝐄 𝐄𝐀𝐒𝐘 𝐖𝐀𝐘 𝐈𝐍 | 𝐒𝐢𝐭𝐮𝐚𝐭𝐢𝐨𝐧 𝟎𝟏
It’s late afternoon. You receive a message that appears to be from a senior leader:
“I’m in a meeting. Please send the customer file to this address now. I’ll explain later.”
The sender’s name looks right. The request sounds urgent. You’ve worked with this person before.
𝐖𝐡𝐚𝐭 𝐰𝐨𝐮𝐥𝐝 𝐲𝐨𝐮 𝐝𝐨 𝐟𝐢𝐫𝐬𝐭?
𝐀. Send the file. You can confirm afterwards.
𝐁. Reply to the same message asking if the request is genuine.
𝐂. Contact the person through a channel you already know and use.
𝐀, 𝐁 𝐨𝐫 𝐂? 𝐓𝐞𝐥𝐥 𝐮𝐬 𝐢𝐧 𝐜𝐨𝐦𝐦𝐞𝐧𝐭𝐬 𝐰𝐡𝐚𝐭 𝐲𝐨𝐮’𝐝 𝐝𝐨 𝐟𝐢𝐫𝐬𝐭, 𝐚𝐧𝐝 𝐰𝐡𝐲.
We’ll unpack the risk on Wednesday.
𝘍𝘪𝘤𝘵𝘪𝘰𝘯𝘢𝘭 𝘴𝘤𝘦𝘯𝘢𝘳𝘪𝘰 𝘣𝘢𝘴𝘦𝘥 𝘰𝘯 𝘢 𝘤𝘰𝘮𝘮𝘰𝘯 𝘢𝘵𝘵𝘢𝘤𝘬 𝘱𝘢𝘵𝘵𝘦𝘳𝘯..
.
#TheEasyWayIn #CybersecurityAwarenessMonth #EventusSecurity #SecurityAwareness #CyberSecurity
𝐓𝐡𝐞𝐲 𝐝𝐨𝐧’𝐭 𝐚𝐥𝐰𝐚𝐲𝐬 𝐧𝐞𝐞𝐝 𝐭𝐨 𝐛𝐫𝐞𝐚𝐤 𝐢𝐧. 𝐒𝐨𝐦𝐞𝐭𝐢𝐦𝐞𝐬, 𝐰𝐞 𝐥𝐞𝐭 𝐭𝐡𝐞𝐦 𝐢𝐧.
An urgent email. A familiar-looking login page. A voice that sounds like someone you know. A request to “just run this quick fix.”
That’s 𝐓𝐡𝐞 𝐄𝐚𝐬𝐲 𝐖𝐚𝐲 𝐈𝐧.
Cybercriminals count on those moments when we’re busy, distracted or acting out of habit.
This October, for Cybersecurity Awareness Month, Eventus Security is launching 𝐓𝐡𝐞 𝐄𝐚𝐬𝐲 𝐖𝐚𝐲 𝐈𝐧, a series built around the 2026 theme: “𝐃𝐨𝐧’𝐭 𝐌𝐚𝐤𝐞 𝐈𝐭 𝐄𝐚𝐬𝐲 𝐟𝐨𝐫 𝐓𝐡𝐞𝐦.”
Throughout the month, we’ll share realistic workplace scenarios, put your judgement to the test and explore simple actions that make an attacker’s job harder. We’ll also look at how organisations can make safer decisions easier through clear processes, practical safeguards and a culture that encourages reporting.
𝐌𝐨𝐧𝐝𝐚𝐲: What would you do?
𝐖𝐞𝐝𝐧𝐞𝐬𝐝𝐚𝐲: Where was the risk?
𝐅𝐫𝐢𝐝𝐚𝐲: How can organisations reduce it?
Four weeks. Four situations. Small habits that can make a big difference.
The first situation arrives on 𝐌𝐨𝐧𝐝𝐚𝐲, 𝟓 𝐎𝐜𝐭𝐨𝐛𝐞𝐫
Would you spot the easy way in?
.
.
#CybersecurityAwarenessMonth #DontMakeItEasyForThem #CyberAwareness #EventusSecurity #SecureWithEventus
𝐀𝐈 𝐫𝐢𝐬𝐤 𝐢𝐬 𝐧𝐨𝐰 𝐞𝐧𝐭𝐞𝐫𝐢𝐧𝐠 𝐭𝐡𝐞 𝐒𝐎𝐂'𝐬 𝐛𝐥𝐢𝐧𝐝 𝐬𝐩𝐨𝐭.
Most SOCs were built to monitor servers, endpoints, networks and applications.
But what happens when the risk sits inside the AI systems and automated decisions driving your business?
For security leaders, the challenge is no longer limited to detecting traditional threats.
The 𝐍𝐈𝐒𝐓 𝐀𝐈 𝐑𝐢𝐬𝐤 𝐌𝐚𝐧𝐚𝐠𝐞𝐦𝐞𝐧𝐭 𝐅𝐫𝐚𝐦𝐞𝐰𝐨𝐫𝐤 (𝐀𝐈 𝐑𝐌𝐅) provides a structured approach to understanding and managing these emerging risks through Govern, Map, Measure, and Manage.
In this blog, Dominic F., 𝐂𝐲𝐛𝐞𝐫𝐬𝐞𝐜𝐮𝐫𝐢𝐭𝐲, 𝐃𝐚𝐭𝐚 𝐏𝐫𝐢𝐯𝐚𝐜𝐲 & 𝐆𝐑𝐂 𝐂𝐨𝐧𝐬𝐮𝐥𝐭𝐚𝐧𝐭 at Eventus Security explores why traditional SOC visibility is no longer enough and what it takes to bring AI governance, threat monitoring and risk intelligence into modern security operations.
Because securing the infrastructure is only part of the job.
The future SOC must go beyond monitoring infrastructure, it must also understand the risks behind AI-driven decisions.
𝘐𝘧 𝘺𝘰𝘶'𝘳𝘦 𝘳𝘦𝘴𝘱𝘰𝘯𝘴𝘪𝘣𝘭𝘦 𝘧𝘰𝘳 𝘤𝘺𝘣𝘦𝘳𝘴𝘦𝘤𝘶𝘳𝘪𝘵𝘺, 𝘈𝘐 𝘳𝘪𝘴𝘬 𝘰𝘳 𝘨𝘰𝘷𝘦𝘳𝘯𝘢𝘯𝘤𝘦, 𝘵𝘩𝘪𝘴 𝘪𝘴 𝘢 𝘮𝘶𝘴𝘵-𝘳𝘦𝘢𝘥👇
🔗 𝐑𝐞𝐚𝐝 𝐭𝐡𝐞 𝐟𝐮𝐥𝐥 𝐛𝐥𝐨𝐠: https://t.co/4gn6f31FX3
.
.
#AIRisk #AIRiskManagement #NISTAIRMF #CyberSecurity #SOC #AIGovernance #ThreatIntelligence #CyberRisk #SecurityOperations #EventusSecurity #SecureWithEventus
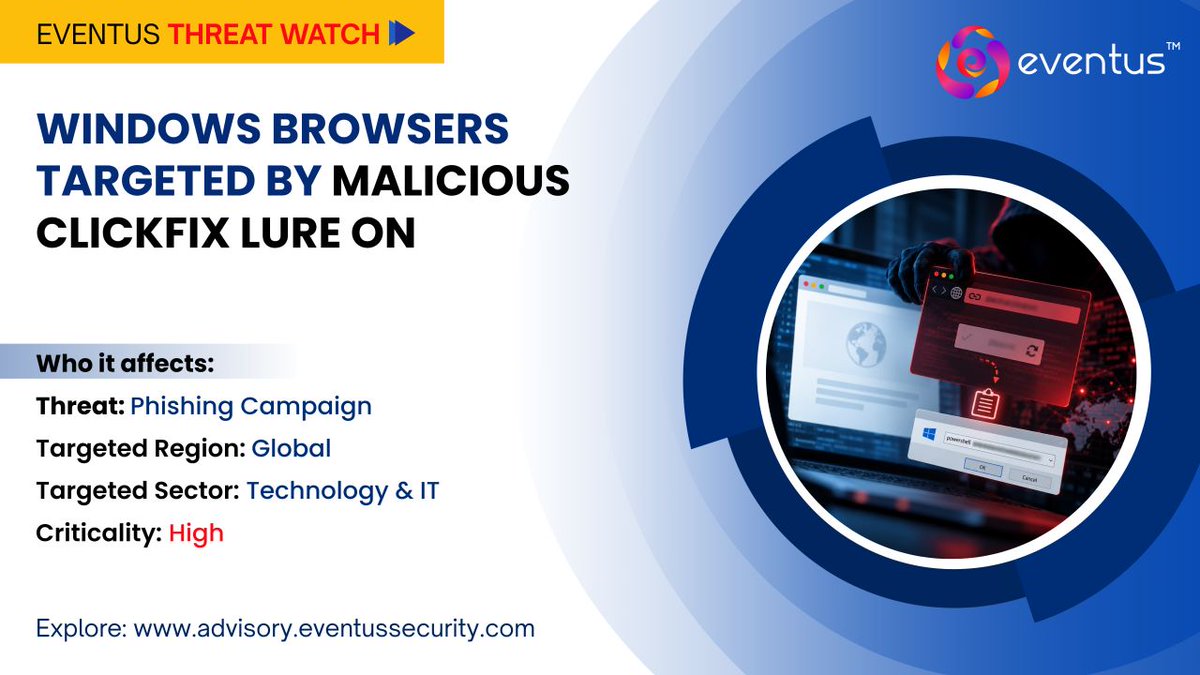
𝐄𝐯𝐞𝐧𝐭𝐮𝐬 𝐓𝐡𝐫𝐞𝐚𝐭 𝐖𝐚𝐭𝐜𝐡 | 𝐀𝐥𝐞𝐫𝐭 #𝟐𝟔
𝐓𝐇𝐄 𝐃𝐎𝐌𝐀𝐈𝐍 𝐋𝐎𝐎𝐊𝐄𝐃 𝐇𝐀𝐑𝐌𝐋𝐄𝐒𝐒. 𝐓𝐇𝐄 𝐑𝐔𝐍𝐓𝐈𝐌𝐄 𝐖𝐀𝐒𝐍’𝐓.
A domain used as a placeholder across public code repositories is now being used in a #ClickFix campaign targeting Windows users. Visitors on other systems may see an ordinary page, making the malicious behaviour easier to miss.
The broader concern goes beyond one domain: a reference that once seemed harmless can become a live security risk when the domain behind it changes hands.
For security and development teams, the question is worth asking: where do placeholder domains appear in your code, documentation and tools, and what happens when those references are accessed?
Our latest advisory examines how the lure works, why routine checks may miss it, and what teams should review.
👉 𝗥𝗲𝗮𝗱 𝘁𝗵𝗲 𝗳𝘂𝗹𝗹 𝗮𝗱𝘃𝗶𝘀𝗼𝗿𝘆 𝘁𝗼 𝘀𝗲𝗲 𝗵𝗼𝘄 𝘁𝗵𝗶𝘀 𝘄𝗼𝗿𝗸𝘀 𝗮𝗻𝗱 𝗵𝗼𝘄 𝘁𝗼 𝘀𝘁𝗮𝘆 𝗽𝗿𝗼𝘁𝗲𝗰𝘁𝗲𝗱. https://t.co/HULfrFxraX
Eventus Threat Watch tracks the threats that can quietly move from “𝘭𝘰𝘰𝘬𝘴 𝘴𝘢𝘧𝘦” to “𝘢𝘭𝘳𝘦𝘢𝘥𝘺 𝘦𝘹𝘱𝘭𝘰𝘪𝘵𝘦𝘥”.
.
.
#EventusThreatWatch #CyberSecurity #ThreatIntelligence #SupplyChainSecurity #PowerShell #CyberThreats #InformationSecurity #EventusSecurity #SecureWithEventus
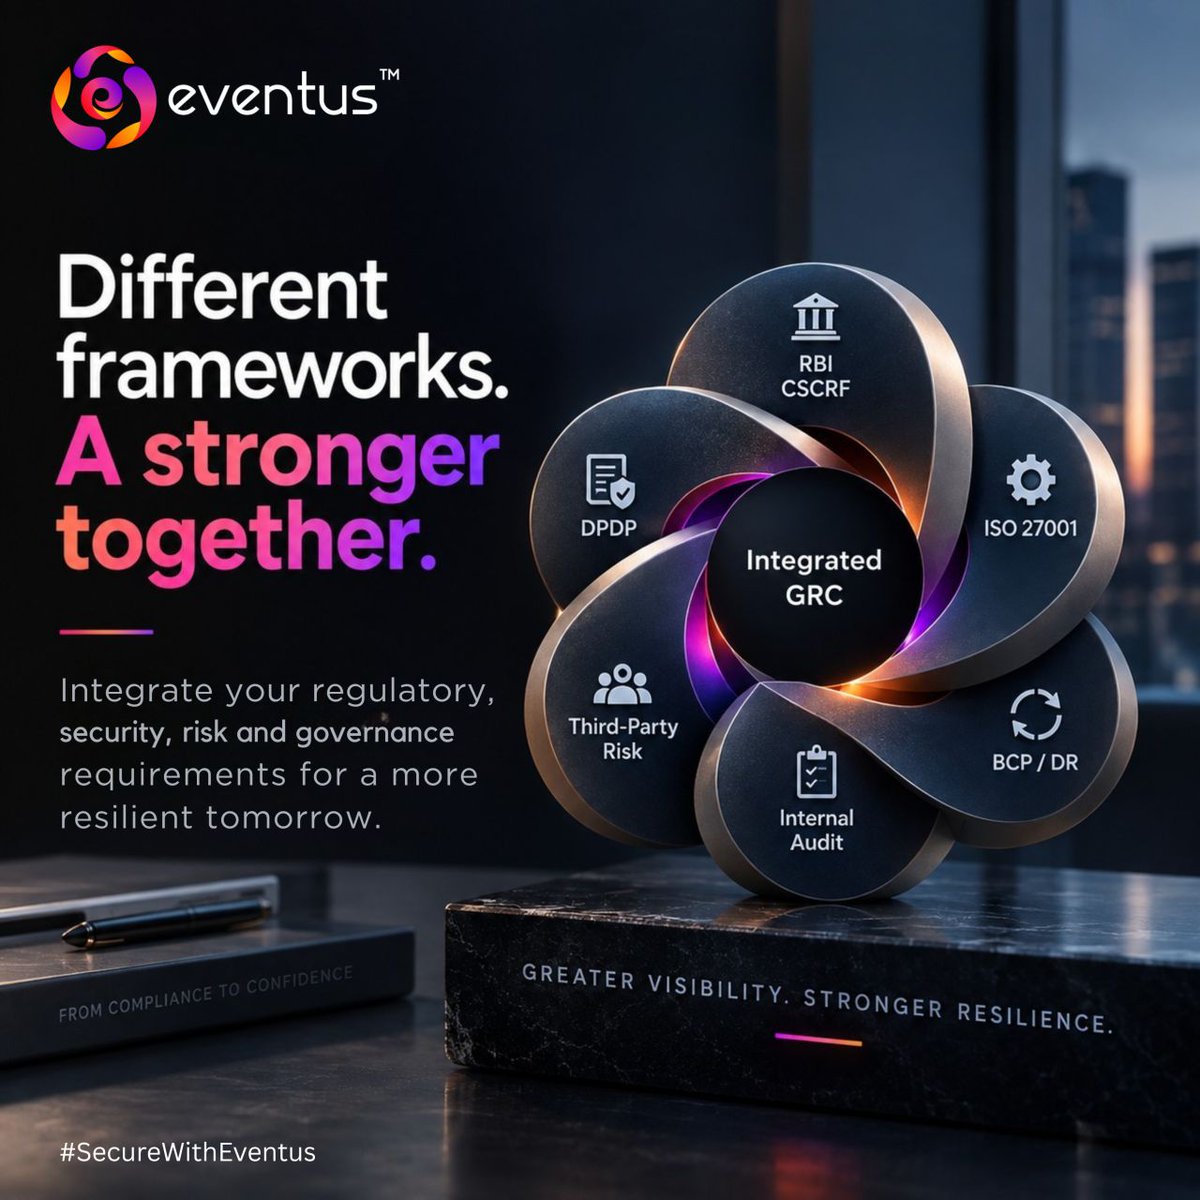
𝐁𝐅𝐒𝐈 𝐨𝐫𝐠𝐚𝐧𝐢𝐬𝐚𝐭𝐢𝐨𝐧𝐬 𝐝𝐨𝐧’𝐭 𝐡𝐚𝐯𝐞 𝐚 𝐬𝐡𝐨𝐫𝐭𝐚𝐠𝐞 𝐨𝐟 𝐜𝐨𝐦𝐩𝐥𝐢𝐚𝐧𝐜𝐞 𝐟𝐫𝐚𝐦𝐞𝐰𝐨𝐫𝐤𝐬. 𝐓𝐡𝐞𝐲 𝐡𝐚𝐯𝐞 𝐚 𝐜𝐨𝐨𝐫𝐝𝐢𝐧𝐚𝐭𝐢𝐨𝐧 𝐩𝐫𝐨𝐛𝐥𝐞𝐦.
Depending on the type of regulated entity, organisations may need to address requirements arising from RBI cybersecurity and IT governance directions, SEBI CSCRF, the DPDP Act and Rules, ISO 27001, Third-party risk management, Internal audit, and Business Continuity and Disaster Recovery requirements.
𝐄𝐚𝐜𝐡 𝐬𝐞𝐫𝐯𝐞𝐬 𝐚 𝐝𝐢𝐟𝐟𝐞𝐫𝐞𝐧𝐭 𝐩𝐮𝐫𝐩𝐨𝐬𝐞. 𝐁𝐮𝐭 𝐦𝐚𝐧𝐲 𝐨𝐟 𝐭𝐡𝐞 𝐮𝐧𝐝𝐞𝐫𝐥𝐲𝐢𝐧𝐠 𝐞𝐱𝐩𝐞𝐜𝐭𝐚𝐭𝐢𝐨𝐧𝐬 𝐫𝐞𝐩𝐞𝐚𝐭:
→ Access control
→ Data protection
→ Incident response
→ Third-party oversight
→ Business resilience
→ Control testing and evidence
When each framework is managed as a separate compliance exercise, different teams can end up reviewing the same controls, collecting similar evidence and maintaining parallel documentation.
This creates duplicated effort, fragmented ownership and the risk of control gaps becoming visible only during an audit or regulatory review.
The answer is not another compliance tracker.
𝐈𝐭 𝐢𝐬 𝐚 𝐜𝐨𝐦𝐦𝐨𝐧 𝐜𝐨𝐧𝐭𝐫𝐨𝐥 𝐟𝐫𝐚𝐦𝐞𝐰𝐨𝐫𝐤 𝐭𝐡𝐚𝐭 𝐦𝐚𝐩𝐬 𝐦𝐮𝐥𝐭𝐢𝐩𝐥𝐞 𝐨𝐛𝐥𝐢𝐠𝐚𝐭𝐢𝐨𝐧𝐬 𝐭𝐨:
→ One clearly defined control
→ One accountable owner
→ One reliable evidence source
→ One defined testing approach and frequency
→ One reporting view
This allows teams to reuse relevant evidence where appropriate, identify control gaps earlier and give leadership a clearer view of risk, control effectiveness and organisational resilience.
An integrated GRC and Security Program Advisory approach can help bring regulatory, security, privacy and governance requirements into one practical control and implementation roadmap.
Because compliance should not create more silos, it should help the organisation see and manage risk more clearly.
𝐀𝐫𝐞 𝐲𝐨𝐮𝐫 𝐭𝐞𝐚𝐦𝐬 𝐬𝐭𝐢𝐥𝐥 𝐦𝐚𝐧𝐚𝐠𝐢𝐧𝐠 𝐦𝐮𝐥𝐭𝐢𝐩𝐥𝐞 𝐟𝐫𝐚𝐦𝐞𝐰𝐨𝐫𝐤𝐬 𝐭𝐡𝐫𝐨𝐮𝐠𝐡 𝐬𝐞𝐩𝐚𝐫𝐚𝐭𝐞 𝐜𝐨𝐧𝐭𝐫𝐨𝐥 𝐬𝐞𝐭𝐬 𝐚𝐧𝐝 𝐞𝐯𝐢𝐝𝐞𝐧𝐜𝐞 𝐭𝐫𝐚𝐢𝐥𝐬?
👉 Connect with our GRC experts to explore a more integrated approach: https://t.co/yyoENbMxM4
.
.
#BFSI #GRC #Cybersecurity #RiskManagement #SecurityGovernance #EventusSecurity
𝐖𝐡𝐚𝐭 𝐎𝐮𝐫 𝐂𝐮𝐬𝐭𝐨𝐦𝐞𝐫𝐬 𝐒𝐚𝐲 | 𝐆𝐚𝐫𝐭𝐧𝐞𝐫 𝐏𝐞𝐞𝐫 𝐈𝐧𝐬𝐢𝐠𝐡𝐭𝐬™
Effective managed detection and response can help security teams strengthen visibility, improve threat detection, and respond to security incidents with greater confidence.
Chief Information Security Officer in the Consumer Goods Industry gives Eventus Managed Detection and Response Services 5/5 Rating in the Gartner Peer Insights™ Managed Detection and Response Market.
𝐑𝐞𝐚𝐝 𝐭𝐡𝐞 𝐟𝐮𝐥𝐥 𝐫𝐞𝐯𝐢𝐞𝐰 𝐡𝐞𝐫𝐞: https://t.co/rjIZ2Ztd27
.
.
#gartnerpeerinsights #manageddetectionandresponse #mdr #cybersecurity #eventussecurity