Finally beat the Ocarina of Time remake. I want to collect my thoughts on it for a bit, but I tried to savor every bit of this remake and it was honestly worth it.
OoT was the first game I ever beat as a young child, I would be happy if this was someone's first exposure to it.
PLEASE READ‼️
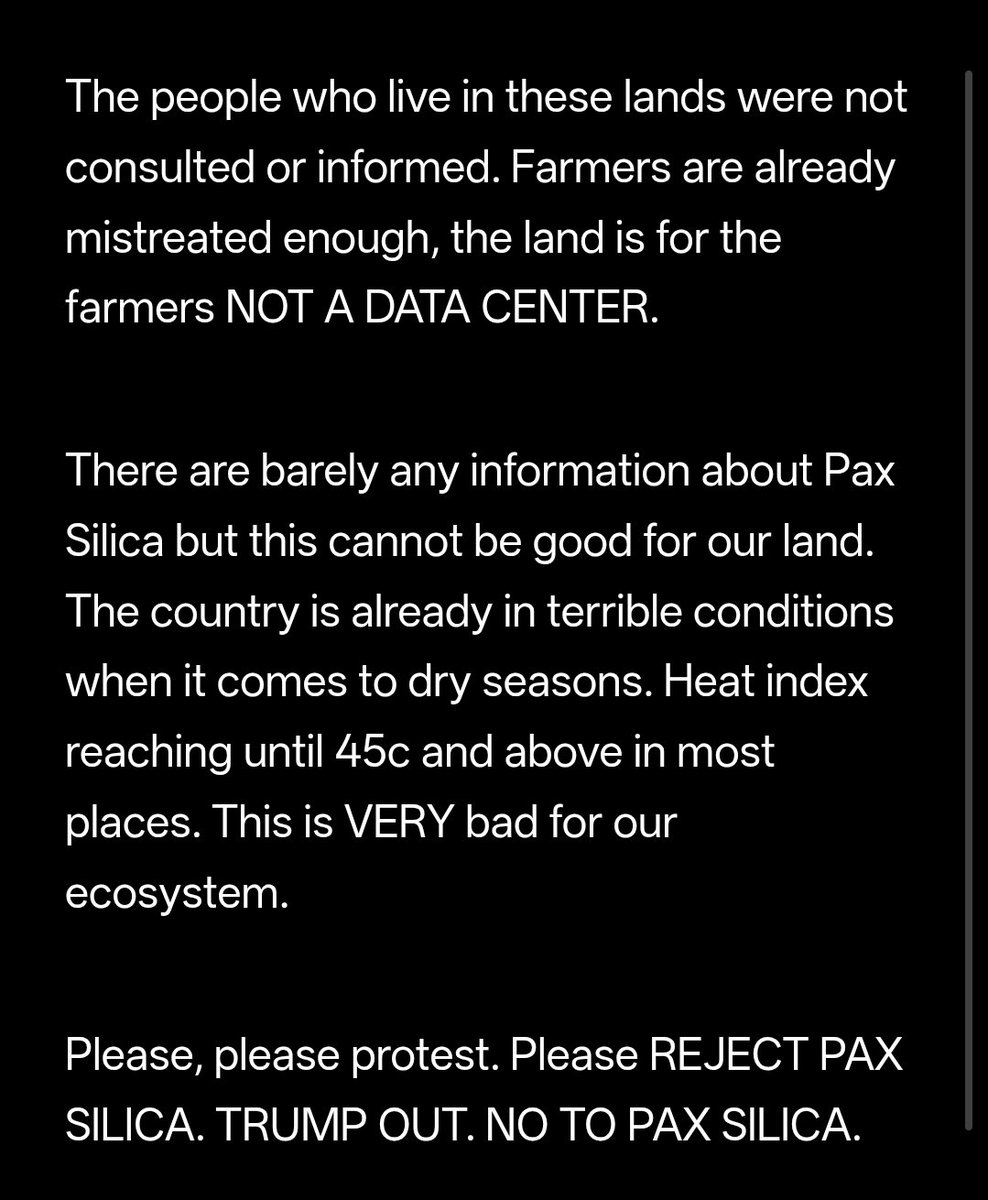
On November 16th Trump will be visiting the Philippines to finally sign Pax Silica. This is a data center that'll takeover 1,2620 hectares. That is a size of 38 mall of asias. It'll be built over agricultural and indigenous lands.
#RejectPaxSilica#TrumpOut
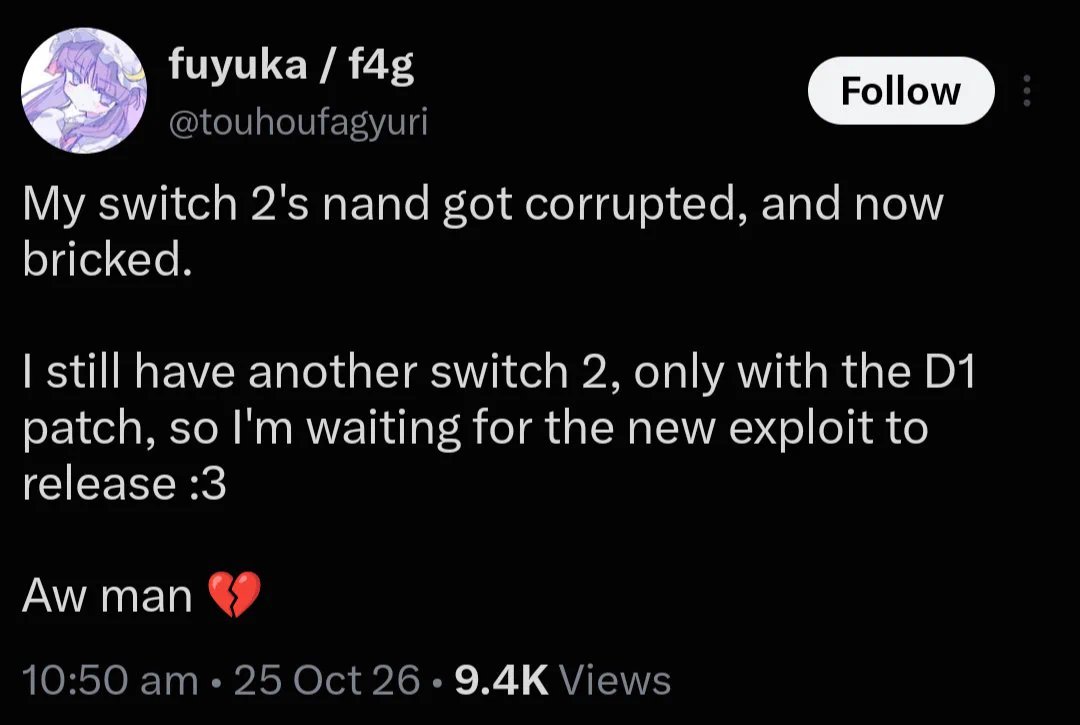
As excited as I was to hear Switch 2 got cracked; even if Switch 2 mods come out in the next few years I'm not risking my Switch 2 with vibecoded garbage lmao. Just look what happened to people's computers with Epic's shitty launcher.
As excited as I was to hear Switch 2 got cracked; even if Switch 2 mods come out in the next few years I'm not risking my Switch 2 with vibecoded garbage lmao. Just look what happened to people's computers with Epic's shitty launcher.
PUBLIC SERVICE ANNOUNCEMENT FROM YOUR LOCAL CYBER SECURITY SPECIALIST
For those who don’t know what this recent PHP security vulnerability means:
This affects most public facing websites.
These vulnerabilities can allow someone to gain access to most websites and their hosting server. That could give them access to sensitive information and/or creds. That is a serious problem.
Companies are working on patching this immediately. But if someone already got in, patching the vulnerability isn't enough. Backdoors could still be there and you can't take back already stolen data.
The part I am most concerned about. Do these companies have the knowledge, staff, and information needed to properly investigate whether someone got in before they applied the fix? Most don't.
You are going to hear things like "your data was encrypted" this does not automatically mean it was safe. If someone controls the service that can decrypt that information, or the attacker has plenty of time and resources on their hands, the information can be decrypted.
This can also affect apps and other services that rely on these connections. How far an attacker can get depends on what those servers can access and how well the company has separated its systems. From many years of experience, most companies don't have good security posture.
FOR THE REGULAR NONTECHNICAL PERSON:
Don’t assume every account you have was hacked. This is a REALLY good time to pay attention and get your account security in order.
SO:
Keep an eye out for breach notices and unusual login activity. If you get an unexpected message telling you to reset your password, go to the company’s website or app directly. Don’t blindly trust or click links in emails. Fake security warnings will ramp up to take advantage of peoples fear.
Stop reusing passwords, ESPECIALLY THE SAME PASSWORD OR A VARIATION OF IT. Use a different password for each account, and turn on multifactor authentication wherever possible. Start with your email. If a company tells you your password was exposed, change it there and anywhere else you used the same or a similar one.
Being a regular person does not mean you’ll be ignored. A lot of account attacks are automated. Someone doesn’t need to know who you are to try your and a thousand other peoples stolen login on a hundred other websites simultaneously.
If you have ANY questions or need any help what so ever please let me know.
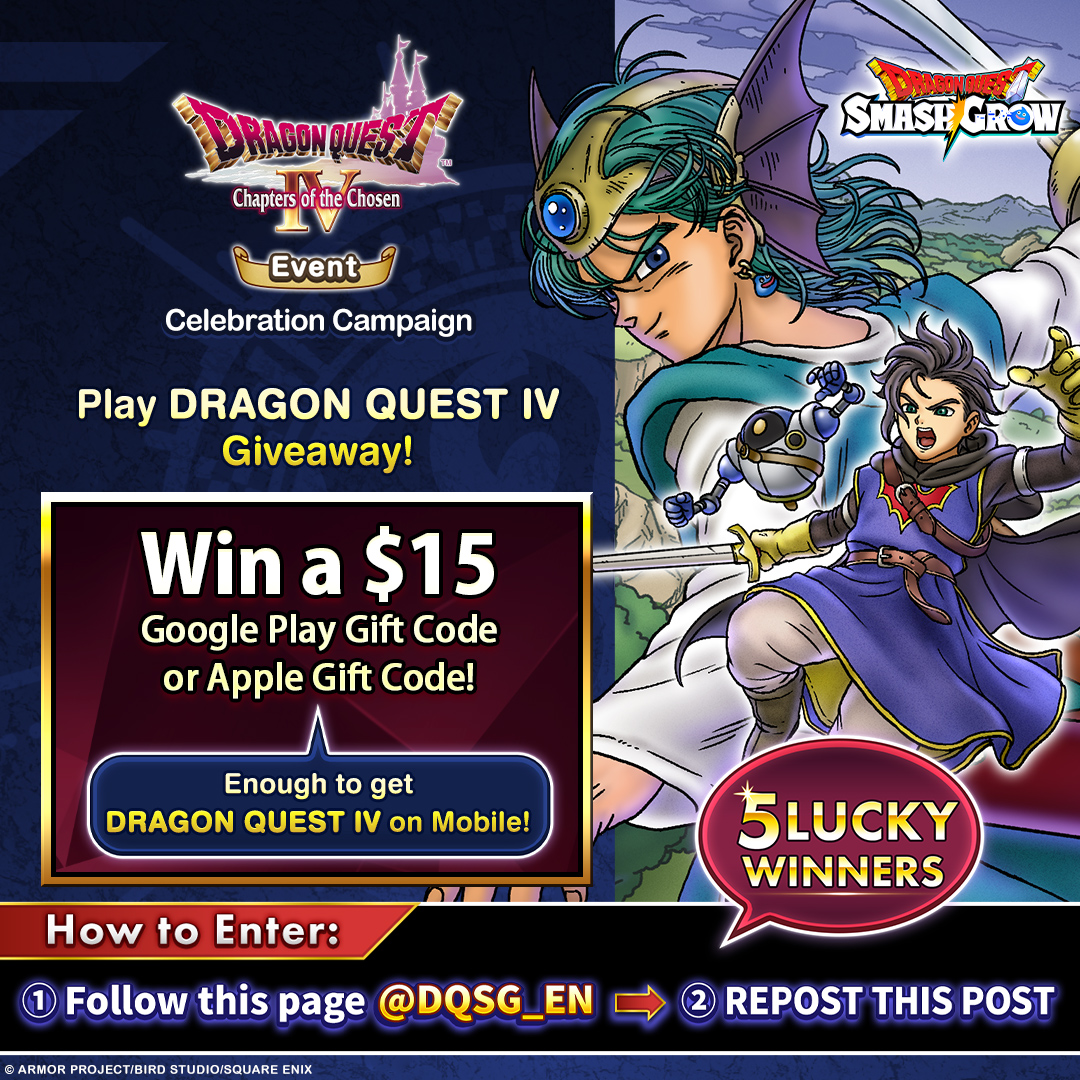
🎁Play #DragonQuest IV Giveaway!🎁
To celebrate the DQ IV event in DQSG, we’re giving away a $15 Google Play Gift Code or Apple Gift Code to 5 lucky winners—enough to pick up the mobile version of DRAGON QUEST IV!
Whether you’re discovering the adventure for the first time or returning to a cherished classic, step into the world of DQ IV and enjoy the collaboration event even more!
How to Enter👇
① Follow DQSG_EN
② Repost this post
See Terms and Conditions here: https://t.co/1B1zbFzj4B
*Entry ends on October 28 at 23:59 (UTC).
#DQSG #DQSmashGrow