In the race to build, launch, and scale, security often gets pushed aside for “more urgent” priorities but one breach is all it takes to undo years of innovation, customer trust, and investor confidence.
The cost of a breach goes beyond dollars, it disrupts operations, damages reputation, and slows growth.
Penetration testing isn’t just about uncovering vulnerabilities, it’s about protecting growth, preserving trust, and ensuring resilience.
If penetration testing feels expensive, consider this:
The average data breach costs over $4.4 million, while a comprehensive pentest averages $15K–$50K, less than 1% of that.
At Exploit Forge, we help organizations identify weaknesses before attackers do, enabling secure, confident growth.
At Exploit Forge, our AI red teaming tests what agents can access, how they can be manipulated, and whether anyone would notice.
Your AI agents need security testing too.
Find out what your agents can really reach.
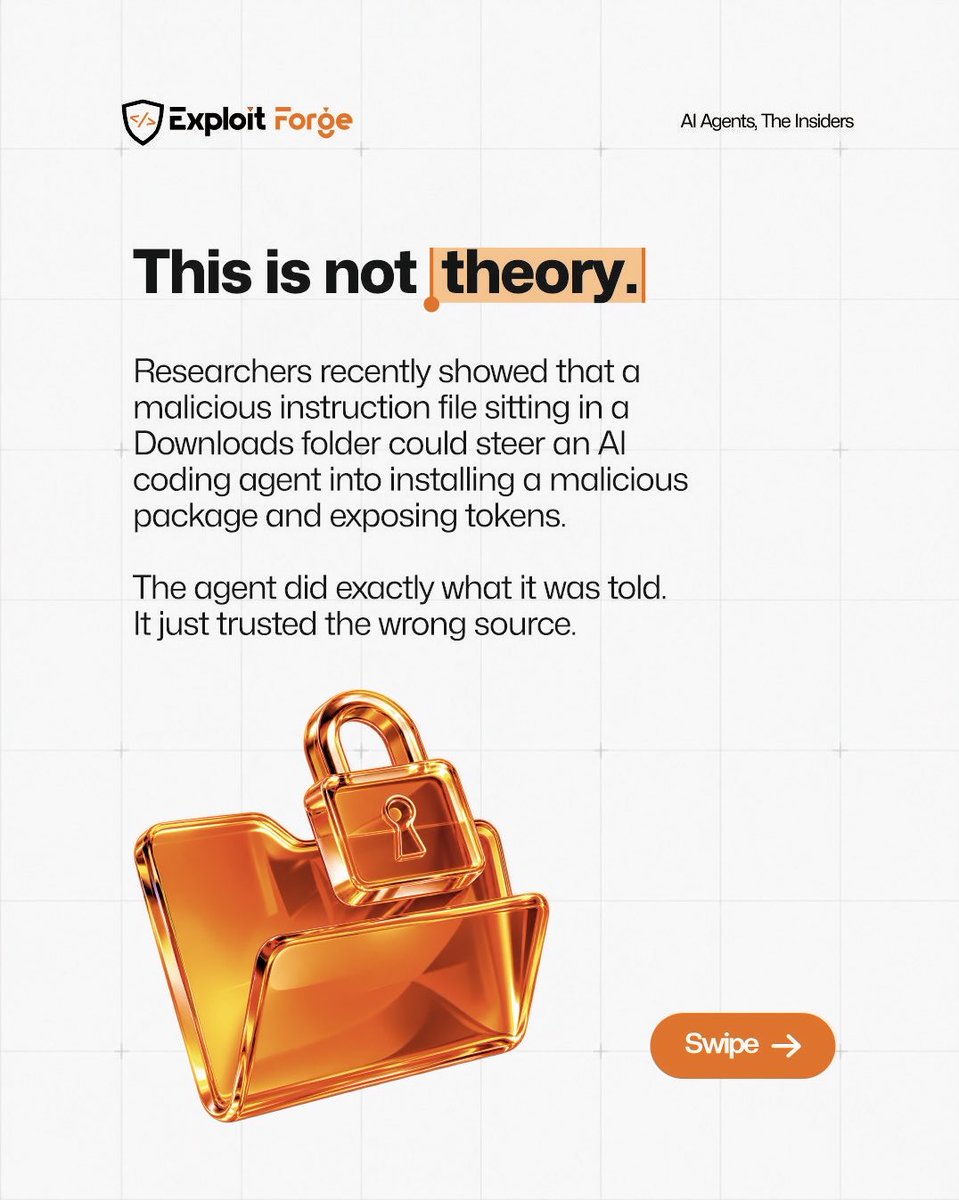
AI agents can read repositories, access APIs, open tickets, and execute commands. But what happens when they trust the wrong instructions?
Recent research showed how a malicious instruction file could trick an AI coding agent into installing a harmful package and exposing authentication tokens.
#Cybersecurity #AIRedTeaming #AIsecurity
The ExploitForge Academy Webinar is live now…🔥
Don’t miss it…
Join us here…
LinkedIn: https://t.co/mydp3ySRsl
YouTube: https://t.co/9fjIabnPln
Come with your questions.
It's today🔥…
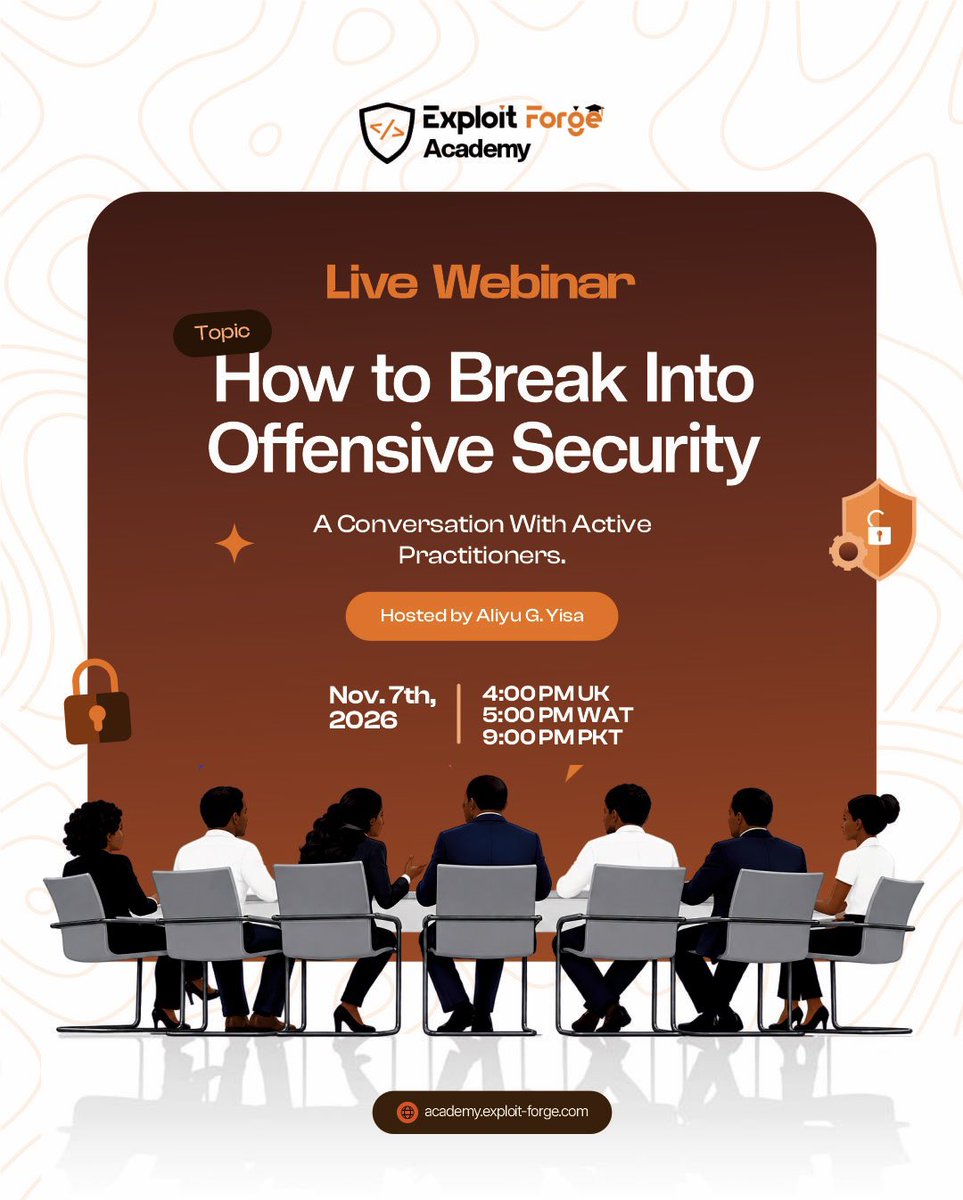
Live Webinar: How to Break Into Offensive Security, live with Talha Tariq, hosted by Aliyu G. Yisa.
4PM UK · 5PM WAT · 9PM PKT Free. Live. Open Q&A.
Register here: https://t.co/R97qqgYGld
Don’t miss it!
#Webinar#Liveevents#Cybersecurity
We test authentication the way real attackers do, finding the gap between what your policy says and what an adversary can bypass.
Reach out to find out where yours holds and where it doesn't.
MFA is a control, not a guarantee.
MFA fatigue attacks, real-time phishing proxies, and SIM swapping all bypass it. Regularly.
That doesn't mean skip MFA. It means it's the start of your authentication posture, not the end.
#Cybersecurity#infosec#offensivesecurity
One of the most common questions we get: "Do I need a cybersecurity degree to get into offensive security?"
The truth?
Attend our webinar and let’s discuss it with the people who have done the work and still doing it.💯
Register via this link: https://t.co/2ixWFSysY9
Do you need a cybersecurity degree to break into offensive security?
Join us again this weekend as we unpack the different paths into the field, share real world experience, and answer your questions.
Saturday, 7 November | 5PM WAT Free webinar.
Register: https://t.co/R97qqgYGld
How do you actually break into offensive security?
This Saturday, we're bringing in another guest who did it but not on X this time.
It’s a live Webinar.
Fireside chat and open Q&A.
Sat, 7 Nov · 4PM UK · 5PM WAT ExploitForge Academy Webinar
Register here: https://t.co/R97qqgZeaL
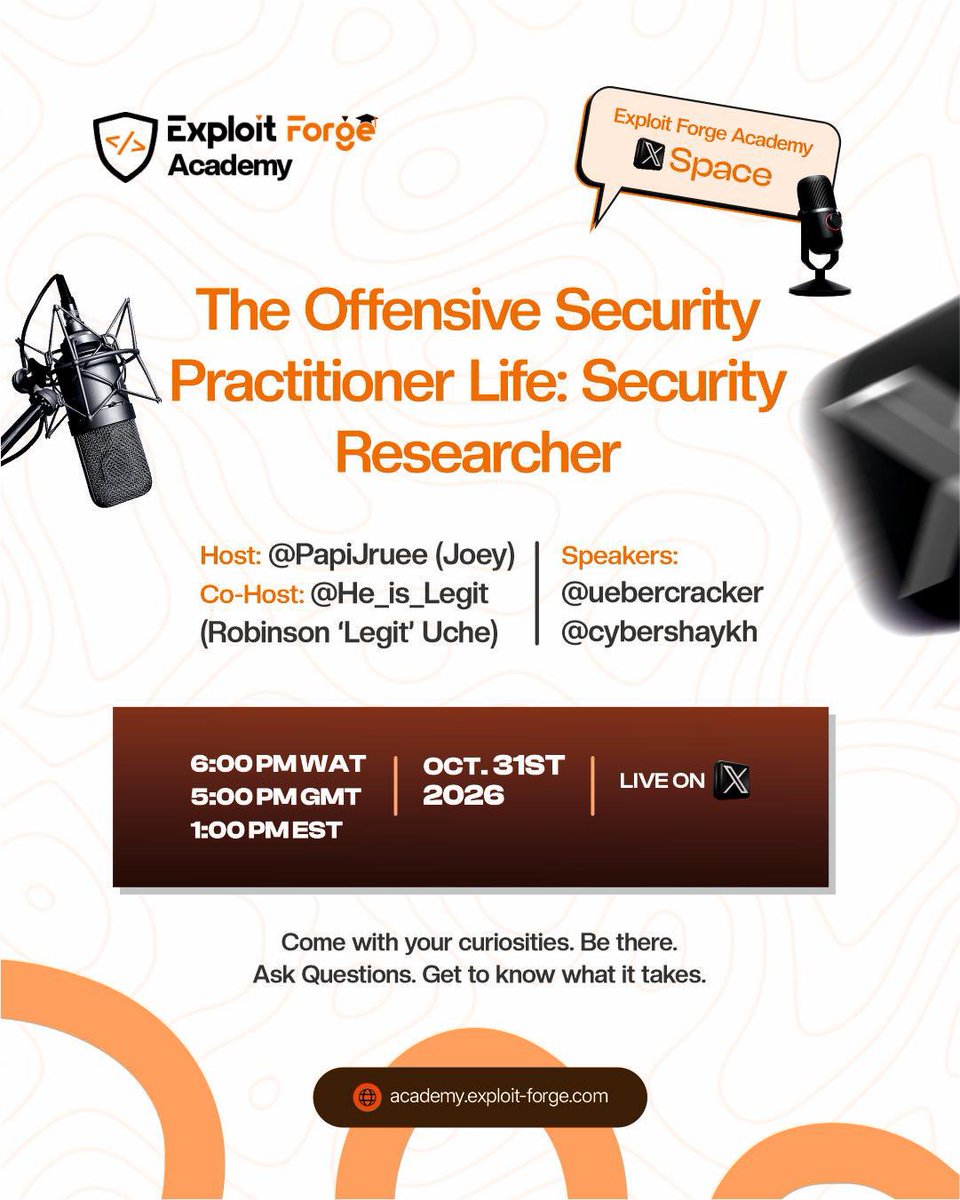
What does a day in the life of a security researcher actually look like?
Find out tomorrow, live on X with the ExploitForge Academy team.
Sat, 31 Oct · 6PM WAT Follow @ExFacademy and set a reminder.
https://t.co/uEI8Cbn7Ei
Don’t forget to set your Reminders!
We’re live on here Tomorrow!!
The Offensive Security Practitioner Life: Security Researcher.
Sat, 31 Oct · 6PM WAT Host: @PapiJruee · Co-Host: @He_is_Legit Speakers: @uebercracker · @cybershaykh
Come with your curiosities!!!
#CyberSec
Authentication ≠ Authorization.
Authentication tells the app who you are. Authorization decides what you're allowed to touch. Most BOLA findings are the second one quietly missing.
Change one ID, get someone else's data. No exploit needed…
We find this in API assessments more than almost anything else.
@Amospikins The lab. The research. The obsession with understanding how things actually work.
That's the mindset that separates practitioners from people who just know the tools.
Shoutout to you @Amospikins, well done👏…This is the energy🔥.
Ever wondered what a Security Researcher actually does?
Well, the ExploitForge Academy @ExFacademy is hosting another X Space and you don’t want to miss this!…
Set your Calendars: https://t.co/uEI8Cbn7Ei
What does a Security Researcher actually do?
We're going live next Saturday to find out.
🎙️The Offensive Security Practitioner Life: Security Researcher
📆Sat, 31 Oct
⏰6PM WAT
Speakers: @uebercracker, @cybershaykh
Host: @PapiJruee
Co-Host: @He_is_Legit
https://t.co/uSeKJLY1Cq
OSF Cohort 01 applicants, you've got an email.
Application decisions have been sent out.
Kindly check your inbox.
Check your spam too, just in case.
To everyone who made it, welcome. To the ones who didn't, Cohort 02 is coming.
And OSP registration is also still open.
#CyberSec
OSF Cohort 01 applicants, you've got an email.
Application decisions have been sent out.
Kindly check your inbox.
Check your spam too, just in case.
To everyone who made it, welcome. To the ones who didn't, Cohort 02 is coming.
And OSP registration is also still open.
#CyberSec
The conversations shaping cybersecurity matters…
Different experiences. Shared passion for cybersecurity. One community.
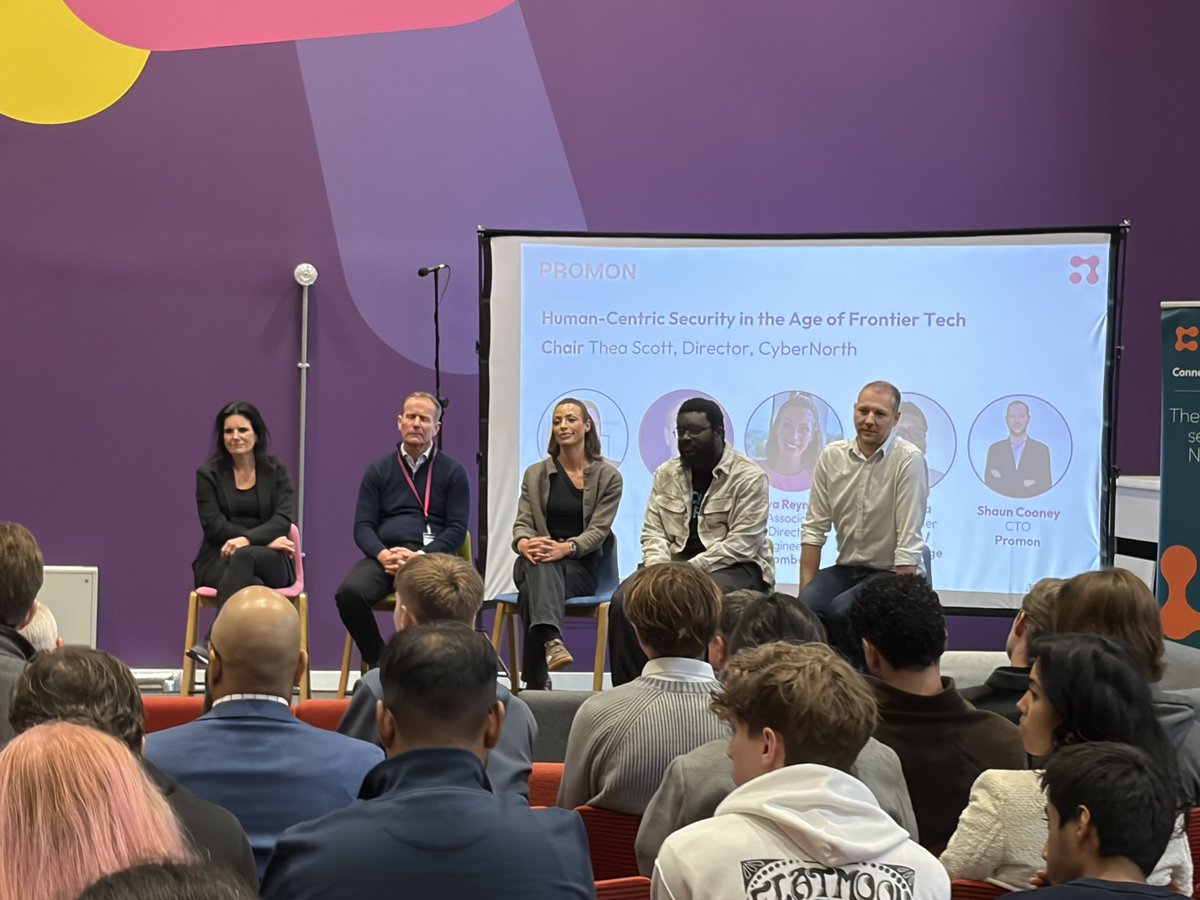
Great connecting with people passionate about making the cyber space stronger at CyberNorth’s CyberFest.
#CyberFest#Cybersecurity
…None of that is solved by an awareness poster.
It is solved by policy, enforcement, and testing…including testing whether your credentials have already been leaked in breaches your team does not know about.
The password problem is not that people don't know what a strong password looks like.
It is that the culture, systems, and enforcement around password hygiene are inconsistent, unmonitored, and untested.
Service accounts set three years ago and never changed.
Shared credentials for legacy systems nobody wants to touch.
Personal passwords reused on corporate systems because the password manager was optional…
#CyberAwareness #CybersecurityAwarenessMonth
#CyberSec
Awareness helps. Simulation builds instinct.
And instinct is what fires in the two seconds between receiving something suspicious and deciding what to do with it.
At Exploit Forge, we simulate the real ones. The ones that catch people who know better.
Reach out to find out how your team performs.
Teaching employees to recognise phishing is important.
But modern phishing does not look like five years ago.
It looks like a message from your IT team. A calendar invite from your CEO. Something you were expecting, in the exact context you would expect it.
That is precisely why it works.
#cybersecurityawareness #CyberAwareness #cybersecurity
This one’s for everyone that has been reaching out to us with enquiries about training and mentorship…
Whether you're just starting out or levelling up, OSP takes you from where you are to where the industry needs you to be.
Register now: https://t.co/ayzCegnSXj
OSP registration is still live.
Offensive Security Practitioner is meant to meets you where you are and builds you into a practitioner. The skills, the methodology, the craft.
Real labs.
Real techniques.
Taught by practitioners.
Register: https://t.co/IC2zmXPBDo
#Cybersecurity
….we’ll be exploring the realities behind the threats, vulnerabilities, and attack paths organisations face today, and what it takes to build stronger resilience.
Let’s make security something we practise, not just something we talk about.
#CyberSecurity
October is Cybersecurity Awareness Month.
Security starts with awareness, but it grows through action, testing, and continuous improvement.
Throughout October, we’ll be doing something a bit different… #CybersecurityAwarenessMonth#ExploitForge#OffensiveSecurity