We got new research from @cybershaykh!
A single unclaimed npm package name is all it takes for client-side RCE... Read more about it below! (=
https://t.co/boz5xNq9ry
Last year, I found a way to disclose what apps organisations were building on Apple Developer before they were ever released to the public.
Here’s how I did it -:
https://t.co/EDbOIY1P8s
Last year, I found a way to disclose what apps organisations were building on Apple Developer before they were ever released to the public.
Here’s how I did it -:
https://t.co/EDbOIY1P8s
I Intend to drop some of my paid out bug from @apple.
So many easy findings with crazy impact, but nothing very complicated.
And yes you can still find easy impactful vulnerabilities on company like Apple.
All It takes is finding that unique attack surfaces.
Blog post about From header smuggling in Apple iCloud just dropped.
Sending emails as [email protected], exotic parsing, and a $15,000 bounty.
https://t.co/IzPrUbDw5Q
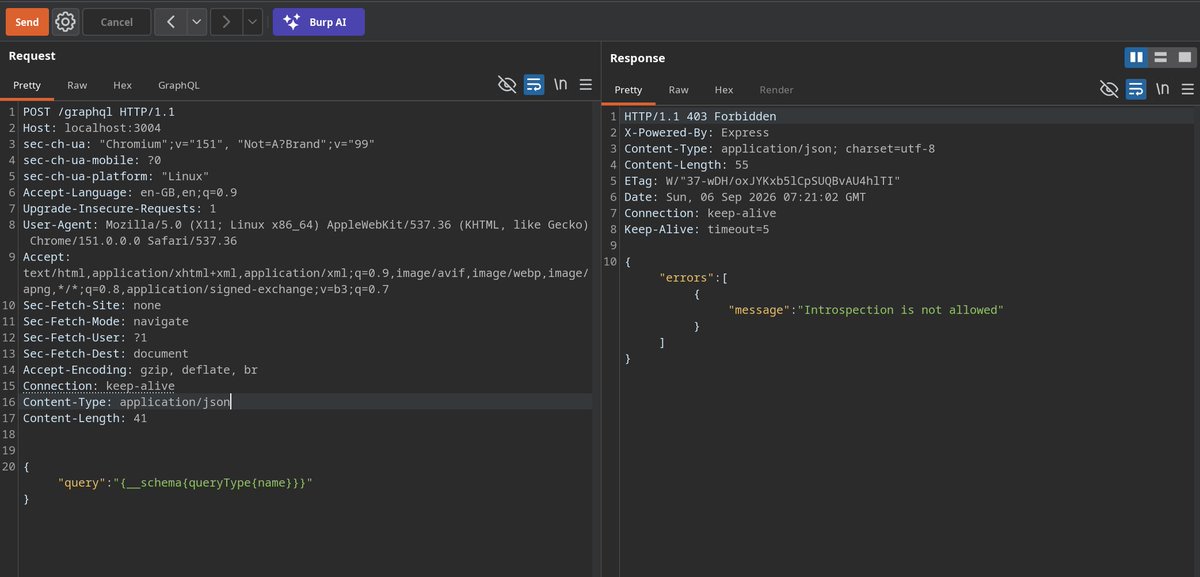
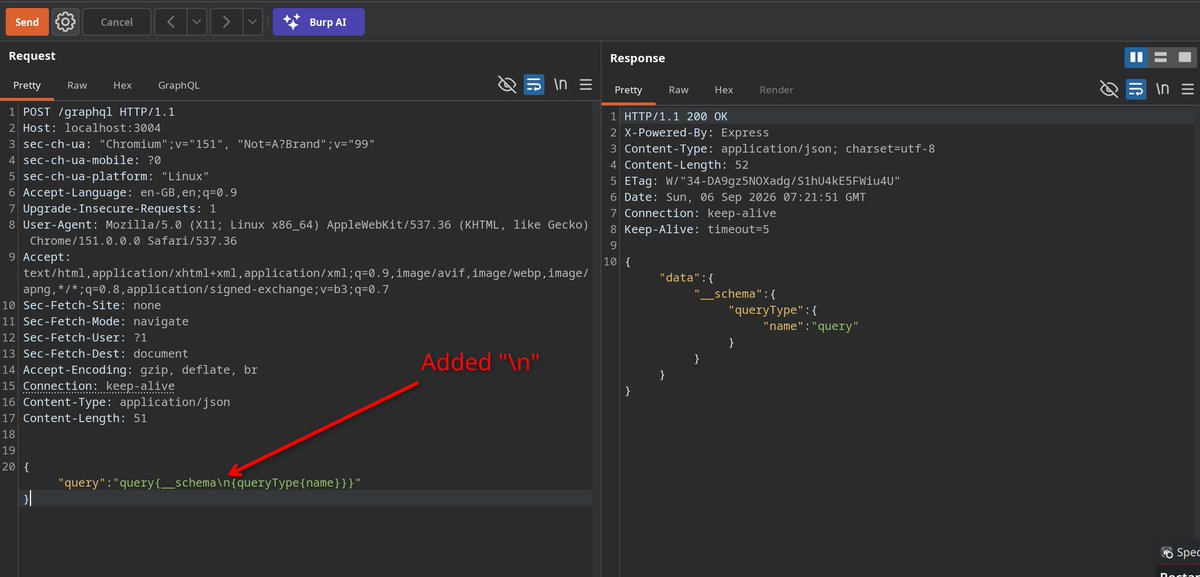
Sometimes, disabling the introspection is implemented as a regex against __schema keyword.
A simple newline character can be enough to create a discrepancy between the filter and the parser.
For GraphQL, whitespace is insignificant, but the regex will stop matching after that!
Try it out in the lab 👇
https://t.co/Tp50mK7qNl
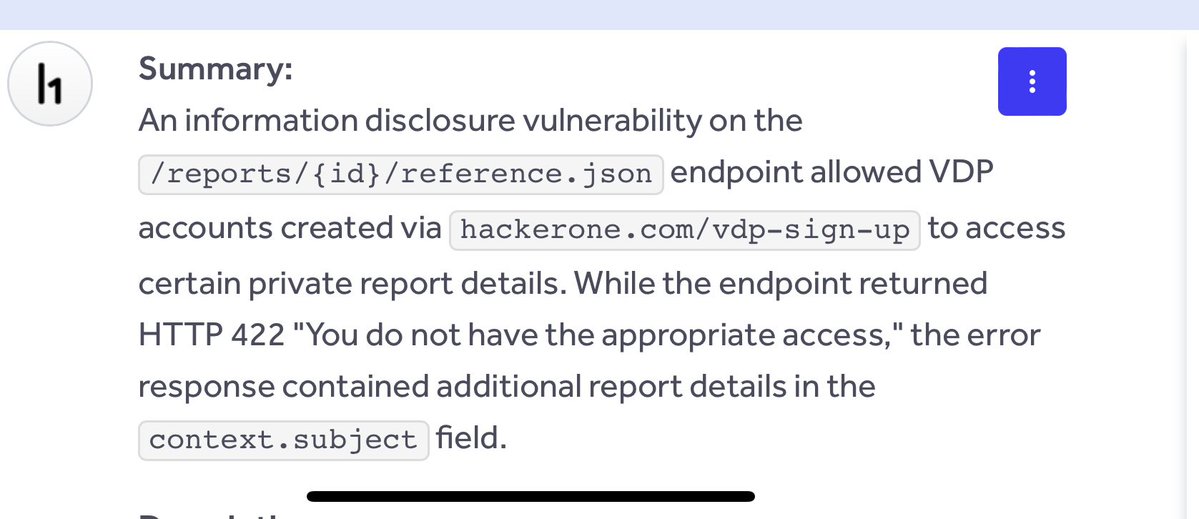
vulnerability disclosure programs are a mess right now.
companies are flooded with slop reports, ai bots are triaging them, platform triagers are triaging the bots, then eventually it reaches the company. the whole process can take a ridiculous amount of time.
and if you actually do serious vulnerability research, it reaches them after a week, then a huge amount of the work is arguing back and forth about impact, proving exploitability, explaining why something isn’t merely theoretical, and dealing with people constantly trying to downplay the finding.
do vulnerability research and submit through vdps for a while, then we can have a more useful conversation about how disclosure actually works.
@yeswehack Good platform tho, I enjoy hacking on it, I’m still top 10 on yeswehack program itself even after this years away.
But yo we need MEDIATION.
I would be back once you all hear US.
lol i said and fought for this back in 2024 I lost over 25k to lack of remediation, till today im yet to get back on @yeswehack cause of that one reason.
@Yeswehack CEO at that time believe I have no point.
Program said 20k for critics
This is driving me crazy.
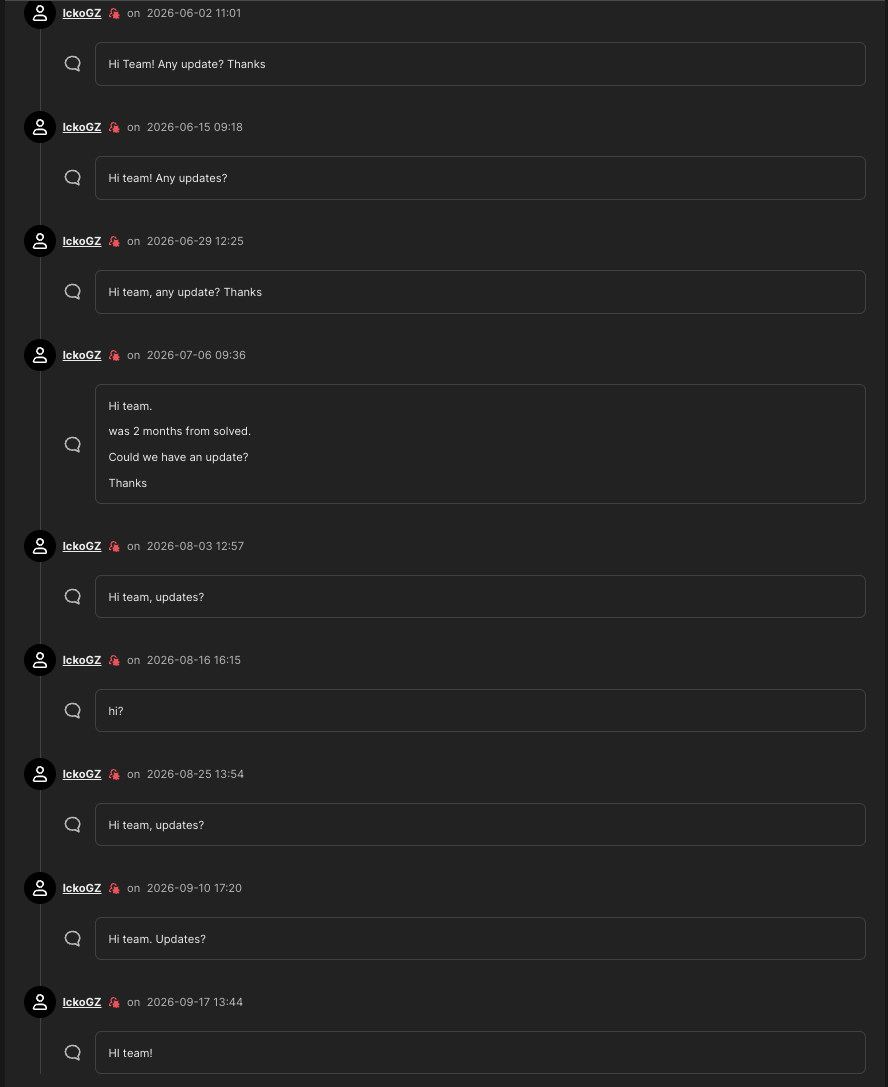
A CRIT10.0 with leaked AWS & internal github admin tokens, solved in 4 days, and no response EVER.
@yeswehack, I'm happy with the platform but after all this years we should have a mediation option.
@yeswehack It’s been over 2yrs why I’m I sharing cause I said I would at some point, it’s a no brainer at this point they just don’t care.
Mediation is a must to have, enough of all those fancy features give us MEDIATION.
@Icko_GZ@yeswehack lol i said and fought for this back in 24 I lost over 25k to lack of remediation, till today im yet to get back on yeswehack cause of that one reason.
Yeswehack CEO at that time believe I have no point.