Today, we announced that we crossed $7B in revenue run-rate, growing over 80% year over year in Q2.
We also shared:
🚀 $100M+ revenue run-rate for Lakebase
🚀 $1.5B+ revenue run-rate for Lakehouse, growing over 100% year over year
🚀 Continued positive adjusted free cash flow
And we raised $5B in our latest fundraise.
We’ll use this capital to invest in:
1️⃣ Lakebase, our serverless Postgres database built for AI agents
2️⃣ Genie, our AI coworkers that actually understand your business data
3️⃣ Unity AI Gateway, our multi-AI governance solution that helps control costs
@iamVictorDey shares more in @Forbes:
https://t.co/y2LdxysBNi
SQLi despite 'secure' Prepared Statements! Known to affect mysql and mysql2, nice write-up from @xoreipeip (and with due credit to previous work by other researchers)
2 instances this week of OAuth SaaS integrations where the setup guide says "login as admin". Even with scopes, the connections are overprivileged. Getting flashbacks of software that "needs" to be installed as admin (translation: cos then it just works).
As a #Salesforce admin or security pro, does it frustrate you that it's impossible to configure an account to have full access to the config of a Salesforce Org as read-only? Upvote https://t.co/cx9b5zVYRy
All I want for Christmas is U(RL handlers not vulnerable to RCE)...
AmberWolf has published information about CVE-2024-12908, a Remote Code Execution vulnerability in the Delinea Secret Server Protocol Handler.
You can read our blog & PoC here:
https://t.co/oW4E5V4KFT
Today, AmberWolf released two blog posts and our tool "NachoVPN" to target vulnerabilities in major VPNs, including CVE-2024-29014 (SonicWall NetExtender SYSTEM RCE) and CVE-2024-5921 (Palo Alto GlobalProtect RCE and Priv Esc), after our SANS HackFest presentation.🧵
New @Sonos app - yuk. Key features missing. Maybe I've just not found things like how to edit the queue. Best case, unintuitive UI; worst case, something that worked (mostly - has definitely got buggier and slower recently) is undeniably worse. Trust that updates are coming...
The @Yourallypally steward in this story should be congratulated - he followed protocol under pressure. So important for 'first line' staff to have a robust process to follow and to be confident sticking with it.
https://t.co/tHUu6Krej5
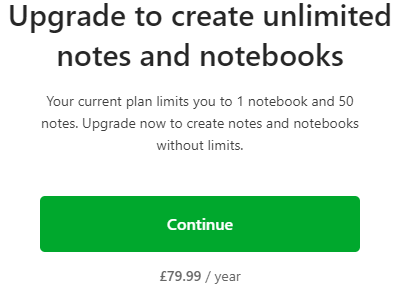
A lot of people will be forgetting @evernote now. I only store text (more or less). I appreciate they have costs and I'd be prepared to bung them a few quid but this drastic change without warning will push many to find an alternative.
Poor show @evernote - used to be able to export all notebooks at once for back-up, now it seems I have to export each notebook in turn. Why make something so important harder to do?
@AppOmniSecurity Interesting stuff but I'm unclear if the core vulnerability and analysis was done by someone else. Can't see a source credited so maybe it is original. Could you clarify?
We've just published 'Smashing the state machine: the true potential of web race conditions' by @albinowax! Dive in to arm yourself with novel techniques & tooling, and help reshape this attack class:
https://t.co/GJOOn4Wmab
First round of BSides Cambridge tickets are live! We've got some great talks lined up. Get your tickets now.
If you're a student, message us or @secmum and we'll sort something out.
#bsides#bsidescambs#infosec#cybereast
https://t.co/v0XQO8SOP1