🚨ExVul Security Incident Analysis Update
We are officially engaged in the comprehensive joint investigation and on-chain tracing for the recent security incident involving the @cysic_xyz cross-chain bridge on BNB Smart Chain.
🔍 Current Investigation Focus:
• Attack Path Analysis:
Deep-diving into the database access vector and message processing logic vulnerability.
• Fund Tracing & Monitoring:
Tracking fund flows and monitoring the blacklisted recipient address
(0xA4e1827Fe2664fD0797a55e442b2e2639449C255), which currently holds ~2.8M CYS.
• Security Remediation:
Assisting in risk validation and security hardening before bridge reopening.
We are working closely with the Cysic team to uncover the full picture. Detailed technical findings and tracing results will be published in our upcoming joint report.
Stay tuned for official updates. 🛡️
#ExVul #Web3Security #Cysic #IncidentResponse #SmartContractSecurity
🚨 ALERT — Exploit on Ethereum
Unifund's legacy trading-group core lost 4.9941 WETH across five exploit transactions. The original EOA netted 4.7555 ETH after gas across its three transactions.
Root cause:
Unifund's swapExactTokensForTokens accepts a cyclic path with the same input and output token, then accounts the input-side and output-side balance deltas separately.
For WETH→A→B→WETH, both updates hit the same WETH ledger key, so each real swap gain is credited twice. In the flagged tx, the group physically held 5.628136547 WETH but its ledger recorded 10.256273095 WETH;
finish()+withdraw() paid the exact 4.628136547 WETH phantom difference from other groups' funds.
Attack tx: https://t.co/eUHOGkf0pq
Attacker: 0x6ee1702ca602ddab66f984aaebaac0451068f881
Victim (Unifund trading-group core): 0x152ad66bd57da8d539abaaf98d7c378621c36227
Vulnerable swap facet: 0x489176b37cb9da4149940707ce39135adc41cec5
Subscribe to our TG bot for real-time attack alerts 👉 https://t.co/XXmb8rT3VA
🚨 ALERT — Exploit on BNB Smart Chain
GDC's Pancake V2 GDC/WBNB pair lost 51.225527 WBNB. The attacker EOA realized +50.008850 BNB after gas, while consuming 41,047.699285 pre-existing GDC. Using >806k BNB/WBNB of atomic capital, two EIP-7702 delegated referral accounts turned GDC's mid-sell reward callbacks into a reserve-manipulation window.
Root cause:
GDCToken._transfer checked the 10% sell limit and froze reserveFloorMode while the pair held 21M GDC, then GDCMain.
onSellRewards called untrusted referral recipients before pair settlement.
Those callbacks pushed 804,812 WBNB into the pair and swapped its GDC side down to the gross sell amount.
GDCToken._applyReserveFloorDistribution then removed that full gross amount from the pair and sync()ed before the outer transfer credited only 30%, leaving 66 wei GDC against 806,382 WBNB;
the 30% credit became apparent AMM input and almost all WBNB was withdrawn.
Attack tx: https://t.co/7Fn0smDPQ9
Attacker: 0x09343312e8a2fd4f8c8ee130a7715587ab21125f
Victim (GDC): 0x39a90d082e19bd2ac30da6964d3d2fda50077777
Vulnerable GDC/WBNB pair: 0xe3349ca6ac1656e02b20b8d5a4c095e28255eb0a
Vulnerable GDCMain callback: 0x8955be303f033a837f7c3c407e0b2b3f9bc4fd5c
Subscribe to our TG bot for real-time attack alerts 👉 https://t.co/XXmb8rT3VA
🚨 ALERT — Exploit on BSC
TENDRIL's Pancake V2 pool lost 550k USDT. The final exploit transaction paid 30K USDT to a hard-coded beneficiary after temporary liquidity was fully repaid; campaign profit is at most ~181,910.34 USDT after directly observed token purchases and gas, before an unpriced LP-position basis.
Root cause:
Every ordinary TENDRIL sell calls PoolControl.sellToken(A).
PoolControl then invokes the sender-restricted TENDRIL.controlburn(2A), which debits the V2 pair itself, and calls pair.sync() before the seller's outer 70% transfer arrives.
The msg.sender checks only authenticate the immediate Token and PoolControl contracts;
an unprivileged seller controls the full Token -> PoolControl -> Token -> Pair path. The burn drove the synchronized token reserve to 6,678 wei, so the delayed outer swap withdrew essentially all USDT.
Attack tx: https://t.co/77aLp4w5hK
Attacker / profit beneficiary: 0xb87cf5ab84d0ab9545358cd30229627305331373
Operator / exploit deployer: 0xb81e4aafa347b27112b7f6f5de6cf7cd516021ff
Exploit contract: 0xc8cb6a2aa825a576e1470479046056fe414ee0f8
Victim (TENDRIL/USDT pair): 0x5de082471f2a9f01a61e467a32837dee830d99e0
Vulnerable TENDRIL token: 0xb1afdfd850da168f2cc9f742e11cdda5273973d2
Subscribe to our TG bot for real-time attack alerts 👉 https://t.co/XXmb8rSw62
🚨 ALERT — Exploit on BNB Smart Chain
The OSK CoreVault system suffered ~251.23 BNB (~$175K) in net exploit loss.
The attacker retained ~152.26 BNB after seeding an 8-BNB position and flash-borrowing 207,358.41 WBNB. The flagged deploy tx contains the full cash-out, not an unrelated whole-block balance delta.
Root cause:
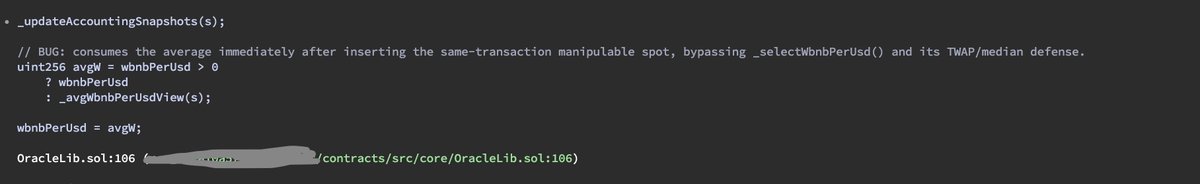
CoreVaultFarming._redeemPrincipalCore() settles through OracleLib.getAccountingPrices().
That function first pushes the same-transaction Pancake WBNB/USDT spot into a 3-sample window, then immediately returns the raw average. It never calls the library’s spot/TWAP/average median selector.
Attack tx: https://t.co/b4I50xXxwd
Attacker: 0xd3565b191b28b49cc517189b984dacdb1ff05304
Victim (InsurancePool): 0xf40e0d525003fb6c6a9a7d79734a87a465053df1
Vulnerable CoreVault: 0x302f5084ba0e4a2d4de5e6bc5dd5247028f5d674
The InsurancePool owner should sever the vulnerable Treasury and evacuate remaining reserves.
Subscribe to our TG bot for real-time attack alerts 👉 https://t.co/XXmb8rT3VA
Security is a continuous commitment, not a checkbox. Proud to have partnered with the @0xHedgehood team to thoroughly review Stock Yield v2 and the share lending oracle. Rigorous testing ensures safer DeFi for everyone. 🛡️📉
Read the full audit in here 👇
security first 🦔
our smart contract audit with @EXVULSEC is complete
result: passed
critical findings: 0
covers stock yield v2 and the share lending oracle. use hedgehood with confidence
full report:
https://t.co/jO2ODgR0lX
🚨 ALERT — Exploit on Ethereum
zkLink Nova (@zkLink_Official) lost roughly $0.8M from its L1 escrows. An attacker installed a forged L2 logs root for batch 116409, then finalized 12 fake withdrawals with no corresponding L2 burn.
Root cause:
The allowlisted SyncL2TxHashRelayer was callable by anyone. In Arbitrator.claimMessage(), a valid Linea claim primed transient finalizeMessageHash;
a second call reused that stale hash and named zkLink’s own EthereumGateway as the “message service.”
Because the Arbitrator made the call, it satisfied onlyArbitrator and installed attacker-chosen root 0x1934…15ea8. The stale hash let validation pass without a fresh callback, after which finalizeEthWithdrawal plus 11 L1ERC20Bridge.finalizeWithdrawal calls accepted fabricated leaves against the forged root.
Flow (1 exploit tx): valid claim primes transient hash → reuse stale hash to call EthereumGateway.sendMessage(syncBatchRoot) → forge batch 116409 root → finalize ETH leaf + 11 ERC-20 leaves → 22.4313 ETH + 245.7379 pufETH + 10 other tokens released.
The attacker paid 1.00116 ETH gas across the exploit and a same-block zero-value self-transaction, leaving +21.4301 ETH net native plus the tokens. The USD total is price-dependent: ~$779K at contemporaneous marks and ~$805K using later marks.
Attack tx: https://t.co/xS9DWt6WSe
Attacker: 0xaCA0655a11200a80d33d0e48786317304cDE5718
Victim (ETH escrow): 0x5fD9F73286b7E8683baB45019c94553B93E015Cf
Victim (L1ERC20Bridge): 0xAd16EDCF7Deb7e90096a259C81269d811544B6b6
Vulnerable Arbitrator: 0x1eE09a2CaA0813a5183f90f5A6D0e4871F4c6002
Public allowed relayer: 0x0fdC28E64772A70109D10fd068f859Cfa7dEA2c6
Status at 13:26 CST on Oct. 29: the relayer remained enabled and ZkLink was unpaused. The drained token balances were empty, but refills or other assets may remain at risk until the path is disabled or upgraded.
Subscribe to our TG bot for real-time attack alerts 👉 https://t.co/XXmb8rT3VA
🚨 ALERT — Exploit on Ethereum
X100 (@x100global) Freezer/DexTreasury lost 361,799.999998 X in a one-transaction, flash-loan-funded Senate takeover. The attacker realized 4.75M USDT.
Root cause:
applyForSenate() lets anyone join immediately for a 100-X fee, while the three Senate seats are chosen from current frozen balances—with no voting-power snapshot, stake-age delay, or execution timelock.
Two helpers froze 19,000.000001 X each, beating the 19,000-X incumbent by one raw unit and taking 2/3 seats.
Proposal #7 auto-voted for its proposer; the second helper voted, and execute() immediately self-called v3Swap(PancakeV3, X→USDT, fee=100, amountIn=400,000 X, minOut=0).
The attacker-seeded pool paid the treasury only 35.675313 USDT for 400K X.
Attack tx: https://t.co/fVbk50AbKJ
Attacker: 0x7ec2afdf3ec5964899894f8d58afa95cbb8ffd63
Victim (X100 Freezer / DexTreasury): 0x79f35a33fe2813414851c4ae8daeacd14d822a46
Exploit coordinator: 0x37541fc4a6f1ec86889ba506f51dc39f2bedd10a
Subscribe to our TG bot for real-time attack alerts 👉 https://t.co/XXmb8rT3VA
Kudos to our partner @Cysic_XYZ for taking swift and decisive action. Burning 7.2M CYS from Foundation Reserves directly protects holders and realigns tokenomics. True resilience is built on accountability and transparent execution. Proud to support Cysic moving forward.
Cysic Bridge Security Incident Update:
We plan to burn 7.2M CYS from Foundation Reserves by the end of October to offset the unauthorized minting and realign the token supply with our tokenomics.
The on-chain burn records will be published once confirmed.
A message from Cysic to the party responsible for the exploit:
In the interest of reaching an amicable resolution, we are offering a recovery bounty of approximately 10% for your cooperation in returning approximately 90% of the identified ETH proceeds from the unauthorized minting of 10,000,000 CYS.
Specifically, return 275.872 ETH in native ETH on Ethereum mainnet to the following address controlled by the Cysic Foundation:
0xe3e8E1147a47dCf42fa73892D74928544fe5a6A9
The return window is 72 hours from the on-chain publication of this message on Ethereum mainnet.
Upon verification that 275.872 ETH was received at the designated address by the deadline, you may retain the remaining identified ETH proceeds, approximately 30.652 ETH, as the recovery bounty. This bounty is excluded from the 275.872 ETH repayment amount and does not need to be returned. We will publicly acknowledge your cooperation and consider Cysic’s ETH recovery claim under this offer resolved.
We have reconstructed the key stages of the attack and preserved the supporting technical and on-chain evidence. If the funds have not been returned by the deadline, the matter will be escalated with law enforcement to pursue a full criminal investigation.
BSC on-chain message: https://t.co/4sVLZbtggc
ETH on-chain message: https://t.co/93Rkj9okBT
Always a pleasure working with great teams that take security seriously! 🛡️
Our team is completing another thorough smart contract audit to ensure maximum protection for user funds. Full audit report coming soon. Stay tuned! 🦔🔍
🚨 ALERT — Exploit on BSC
AlpsCon AI Trade Hub lost 152,809.3575 USDC; the attacker received 152,295.3625 USDC before gas. A 1,027,990 USDC Aave flash loan was converted into temporary ALPS service credits, which were credited with prior historical rewards across V7/V8/V9.
Root cause:
V7–V9 recursively import balances from the preceding version, then multiply those newly visible balances by each version's already accumulated profitPerShare while the new account's entryProfitPerShare remains zero.
This lets a fresh V6 deposit claim distributions made before the deposit existed.
The onlyVerified gate also trusted 0xf39f…2266, the canonical Hardhat test account with a public private key;
EIP-7702 let the attacker run exploit code in that whitelisted account context.
Attack tx: https://t.co/Mj5VGXGhH4
Attacker: 0x3d9df7d20d8296286383ffe475aa7b9e548946b2
Whitelisted delegated account: 0xf39fd6e51aad88f6f4ce6ab8827279cfffb92266
Victim (AI Trade Hub V9): 0x9b210da482217afc24074e57f6f8337fe07f0124
The hack decompiled contract:
https://t.co/oIDEFQ7fVI
Subscribe to our TG bot for real-time attack alerts 👉 https://t.co/XXmb8rT3VA
🚨 ALERT — Exploit on Ethereum
@kolan_protocol Uniswap v4 Hook was exploited for 1.279453 ETH net. The attacker flash-borrowed 6.7 WETH, manipulated the KLN spot price, permissionlessly closed two expired windows holding 2.309861 ETH, and sold back through the liquidity those closes injected.
Root cause:
KolanHook.accept(id) allows any caller after expiry, while _closeWindow() trusts the same pool's instantaneous _sqrtPrice() to restore/reposition escrowed ETH liquidity and runs an unbounded buyback.
The attacker moved that price first, forced two settlements at the manipulated state, then reversed the trade through the newly placed ETH liquidity.
Attack tx: https://t.co/V9R5vFbhdl
Attacker: 0x8df735014eab81905e76b87ef0c069bd8e0ae382
Victim (KolanHook): 0x0136fecf49e0217bfd2d9551e8e7b05f174ba8ec Attack helper: 0x4d6a41f2b80fe75facf27f9d0b3dc8bd0ebc835f.
Subscribe to our TG bot for real-time attack alerts 👉 https://t.co/XXmb8rT3VA
🚨 ALERT — Exploit on Ethereum
@UNCX_token Smart Token Vesting was drained of five ERC-20s worth ≈$87.7K at parent-block spot prices.
The exploit contract retained ≈$85.6K in EDGEN, ZC, PEPECOIN, LO0P and PAAL; after 0.5624 ETH in fees/gas, estimated mark-to-market profit was ≈$84.2K.
Root cause:
VestingManager.release() subtracts claimed shares from global _totalTokenShares but leaves them in the position's _depositedShares.
After release → topUpVesting(), cancel() calculates sharesToRemove from the full lifetime _depositedShares without subtracting schedule released,
so already-released shares are removed from the global total a second time.
The attacker used a direct donation to magnify this stale-share debit,
corrupted the denominator, then released a second attacker-owned vesting to take tokens backing unrelated users.
Attack tx: https://t.co/3hU55YM0od
Attacker: 0x78c9b11853e4f183a34c63ffd1924d2319a2f5b3
Exploit contract: 0xf6d072254eb8a9b06e0ba21221b498332c1bc35e
Victim (UNCX Smart Token Vesting): 0xa98f06312b7614523d0f5e725e15fd20fb1b99f5
The same accounting path remained live at the latest checked block; other token balances may still be exposed.
Subscribe to our TG bot for real-time attack alerts 👉 https://t.co/XXmb8rT3VA
🚨 ALERT — EIP-7702 Wallet Drain on Ethereum
sven.eth was drained for 9.1231 ETH net (~$22.77K) plus 1.69271471 TAPEETH.
No flash loan or AMM manipulation was involved: the attacker sponsored a type-4 transaction carrying the victim's valid EIP-7702 authorization, then swept the account in one call.
Root cause:
This is not a TAPEETH / PodMining bug.
The authorization signed by sven.eth delegated its EOA to attacker-deployed code at 0x0366b55f948a688888ca6e029ad0831f6ec260d1.
EIP-7702 then made calls to sven.eth execute that code in the victim account's context, allowing the hard-coded controller 0x9208097c007be15e28b20e94e66870a3f9f820bc to call PodMining.claim(), transfer the freshly minted reward, and send out the victim's entire ETH balance.
Attack tx: https://t.co/pdjkfGevd6
Attacker: 0x9208097c007be15e28b20e94e66870a3f9f820bc
Victim (sven.eth): 0xd8ba9e5886b7000bace2c9dbdd0be98ac77d4a28
Malicious EIP-7702 delegate: 0x0366b55f948a688888ca6e029ad0831f6ec260d1
The malicious delegation was still active at block 26,188,153. Do not send funds to the victim address; clear/replace the delegation and migrate assets immediately.
Subscribe to our TG bot for real-time attack alerts 👉 https://t.co/XXmb8rT3VA
Security and transparency are the foundation of fast-moving markets.
🛡️ It was a pleasure working with the @bibodottrade team to review and secure their smart contracts.
Glad to see them live and building right! Check out the full report below 👇
Bibo has completed a smart contract audit with @exvulsec 🔐
Market move fast
We keep building with security and transparency in mind
Thanks to the ExVul team for the review
Read the full audit report 👉
https://t.co/vtbprWrDJv
🚨 ALERT — Exploit on Ethereum
Legacy Set Protocol’s ETHMACOAPY lost ~8.11 WETH across two transactions from different EOAs.
Root cause:
actualizeFee() rounds redemption backing UP, even when no fee is payable. The attacker donated collateral, triggered recalculation, then redeemed temporary tokens for more collateral than they contributed—consuming existing holders’ backing.
Attack tx: https://t.co/NhSIg6BtQI
Attacker: 0x3a15cf422307e922645d671cb247e76e8b1ec50d Victim (ETHMACOAPY): 0xb647a1d7633c6c4d434e22ee9756b36f2b219525
A second transaction two blocks later removed another ~4.062 WETH, effectively exhausting this Set’s recorded backing.
Subscribe to our TG bot for real-time attack alerts 👉 https://t.co/XXmb8rT3VA