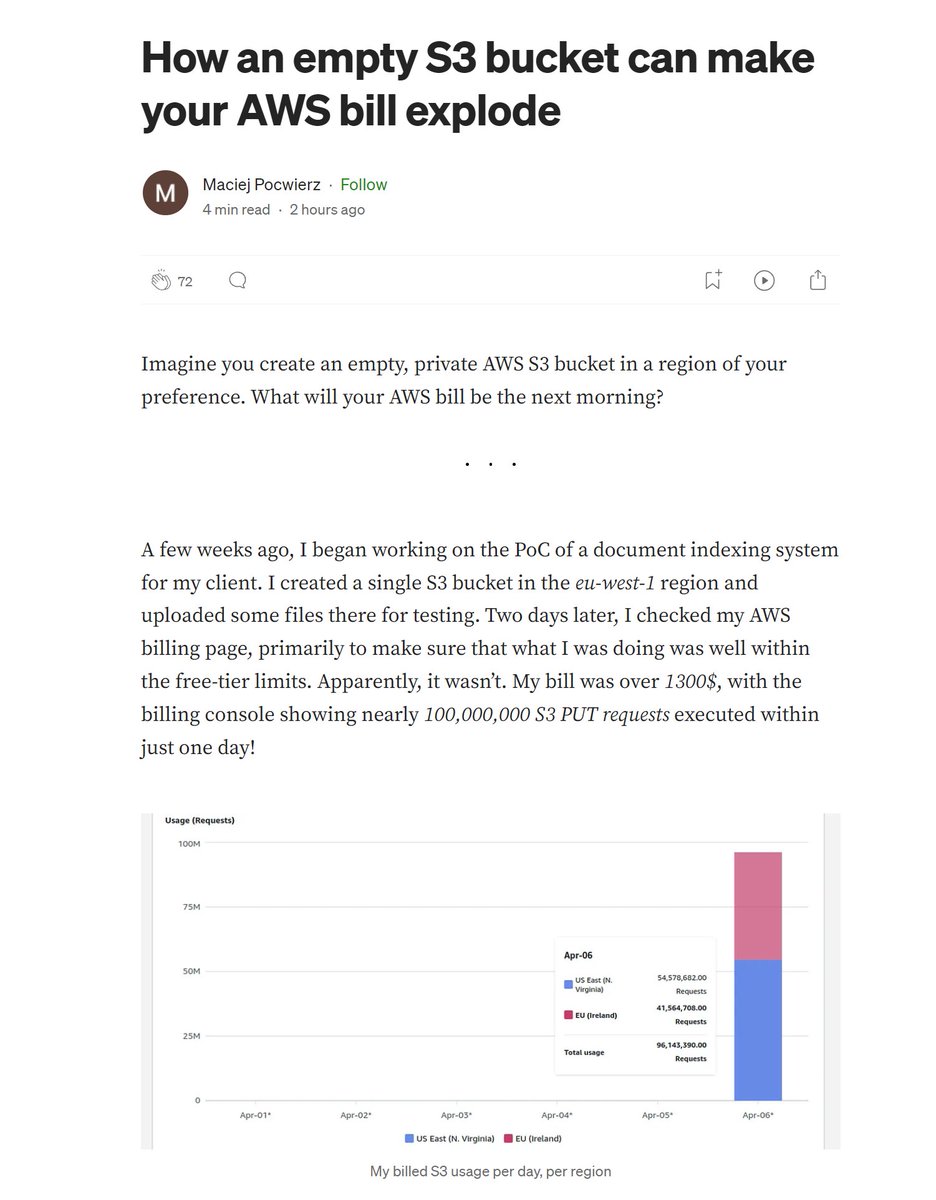
So apparently if someone knows / guesses the name of your S3 bucket - even if it's private (!) - they can just bankrupt you by sending infinite PUT requests and there is nothing you can do about it.
> requests get rejected
> but AWS still counts it as a write operation against your account for which you have to pay at a rate of $0.005 per 1000 requests
This seems insane to me. Especially because a lot of services rely on presigned URLs for uploads / downloads which exposes your bucket name to the client. In this case the author got their bill waved, but AWS support made it clear it's an exception not the rule.
People seem to be imagining this is worse than it probably is, so I've written a piece that hopefully explains it in clear language what the problem is and what's at stake. https://t.co/ubAbQAD679
Fabriqué un aparato para detectar Reggaeton en el parlante del vecino y atacarle el bluetooth. Mañana seguramente publico la demo y el código. 🔧🔇https://t.co/RGGpA5hUQd #reggaetonbegone
@kaepora Hi Nadim. How about...
1. Encrypted notes/reminders
(Saved locally, and uploaded for backup to drive of choice if required)
2. A search/library to find on which platform you can buy or stream a movie/series/content and the price.
3. Detect rogue cell towers.
@happy_pao Es buena idea, aunque no todos los tweets son tan profundos 😅 De todas formas, te recomiendo probar mastodon a mí me encuentras acá: https://t.co/c7A2dSU2X1