@zyron_tech10 Hi Web Developers😊
You don’t have to tell your clients you don't do SEO.
Let's work together, you handle the website development, I do SEO and set up analytics.
No one as to know😊
Security Groups to secure the virtual machines deployed within the subnets
Network Access Control Lists (NACLs) to provide security at the subnet level
Route Tables connected to an Internet Gateway to enable internet access for resources that need it
VPC Flow Logs to capture and monitor network traffic within the VPC
I'm slowly beginning to appreciate why cloud engineers don't just jump into deployments.
Planning the architecture first makes the actual deployment much easier to understand.
Before deploying anything, I started with an architectural drawing to map out the entire infrastructure.
Here's what I designed:
An AWS Cloud environment containing a VPC
Three subnets for a typical 3-tier architecture
Day 21 of my Zero to Cloud Journey ☁
Since I deployed a Virtual Network (VNet) on Azure, I figured it was only fair to do the AWS version too. 😁
While many of the concepts are similar, I'm beginning to notice the subtle differences between Azure and AWS.
Sometimes you learn by building. Then you deepen your understanding by asking why.
I also attached my architectural drawing alongside a video of the deployment so you can see exactly what I built today.
Day 21 tomorrow ☁️
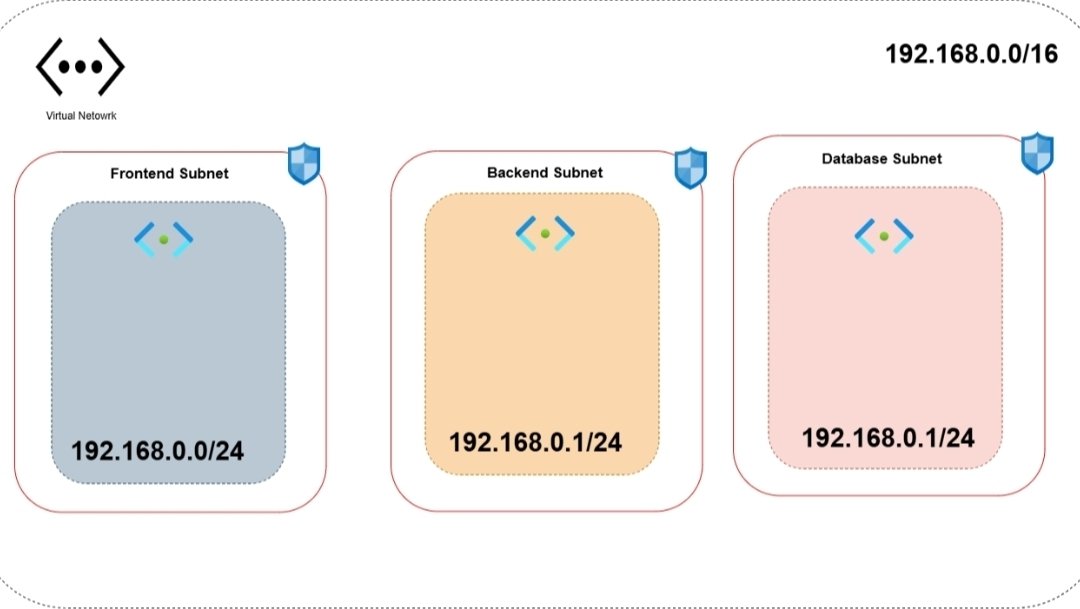
Day 20 of my Zero to Cloud Journey ☁️
Yo! I finally deployed my first Virtual Network (VNet) on Azure! 🥹
I created a VNet, attached 3 subnets to it, and secured each subnet with its own Network Security Group (NSG).
In my case, I created separate subnets for the frontend, backend, and database.
This reinforced something a good friend (chatgpt) once told me:
"Waiting until you fully understand every concept before doing often leads to action paralysis."