🚨 BREAKING: An Israeli ad firm called Discover-Tech used targeted ads to infect Al Jazeera devices with Candiru spyware. It also targeted NATO and European Parliament networks.
Investigations show the ad firm facilitates multiple mercenary spyware partners.
#ESETresearch has analyzed the evolution of #MATCHBOIL, a C# downloader used by the 🇷🇺 Russia-aligned APT group UAC-0099 to download, install, and persist another payload. @reib3n1 https://t.co/hdWz0uqbQC 1/7
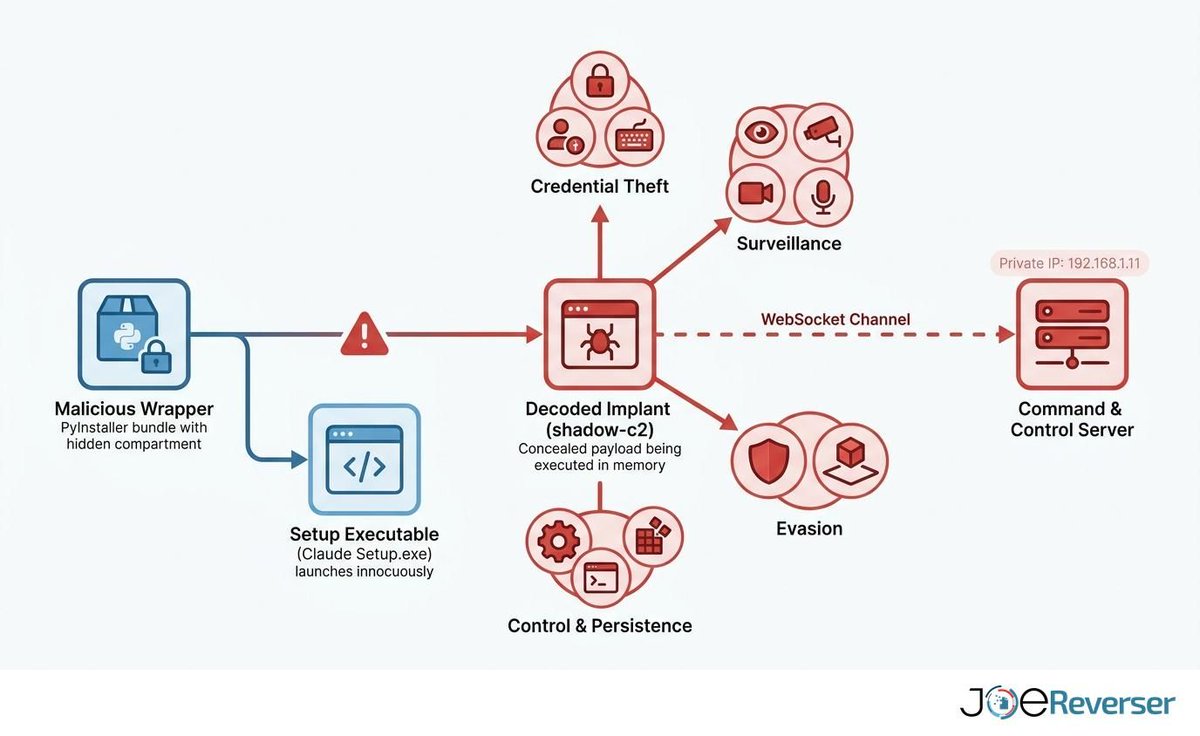
We found an AI-themed malware lure delivering the shadow-c2 implant through a malicious PyInstaller wrapper, using Claude Setup.exe as the visible decoy 🔎
🎭 The PyInstaller wrapper launches Claude Setup.exe while decoding and executing the hidden shadow-c2 Python implant in memory
🔓 shadow-c2 supports browser and Discord credential theft, keylogging, clipboard monitoring, screen capture, webcam/microphone access, remote shell, and process control
🛡️ It includes VM, sandbox, debugger, and sleep-evasion checks, plus multiple persistence mechanisms
🔐 C2 communication uses WebSockets with RSA-OAEP key exchange and AES-GCM encryption
🌐 The configured C2 is 192.168.1.11:5000/ws, a private/local address — potentially consistent with the sample being one component of a broader intrusion set
Joe Reverser analysis: https://t.co/QN54mooHEf
Joe Sandbox analysis: https://t.co/VrjiHNRzWd
#CyberSecurity #Malware #ThreatIntel #InfoSec #ReverseEngineering #AI
Oh, boy ... this seems to be serious
"Imminent Zero-Day Attack: #KiteWorks Urges Customers to Shut Down Servers"
fixed version
"the company has fixed all known vulnerabilities in its latest software release, 9.5.1, which it recommends all customers use"
"Large companies and corporations worldwide use KiteWorks products for secure file transfer but also for communication via webmail. In Germany, several state banks and insurance companies, a media group, consulting firms, and well-known automotive suppliers are among the company’s customers."
https://t.co/RcTwXo2tEM
https://t.co/H7S4Mw0sX0
Italian zero-day maker Dataflow Security generated €63 million in revenue in three years, and the company also has strong ties with former Israeli intelligence veterans, according to an investigation by @RositaRijtano.
https://t.co/BfTlKkos40
‼️ OnePlus confirmed a stock phone could be rooted by an installed app. Then it warned the researcher not to publish.
The app needs no special permissions. OnePlus confirmed the two flaws in May, but no fix was available when the researcher disclosed them. No real-world exploitation is known.
How the root chain works → https://t.co/0WRNLlTvyd
🛡️ wifit3: auditor Wi‑Fi multiplataforma para Linux, Windows y macOS, funcionando directamente con adaptadores USB compatibles
📡 Escanea redes y permite auditar WPA/WPA2, PMKID, WPS y WEP desde una TUI en Python
https://t.co/LqUhhNQruj
The switch to SparroWocky happened shortly after FamousSparrow started targeting Latin America almost exclusively, going mainly after governmental entities. This is most probably part of 🇨🇳 China’s reaction to the increased 🇺🇸 US interest in the region. 2/6
🚨 Great research from @Unit42_Intel on ZionSiphon - an OT-focused threat targeting industrial environments.
We took a deeper look at the sample with Joe Reverser 🔬⚙️
🔗 Unit 42:
https://t.co/NTNArdpUNn
🔗 Joe Reverser analysis:
https://t.co/QJKC5BMms6
Interesting capabilities include SCADA/OT discovery, configuration manipulation, PLC/Modbus activity, USB propagation and anti-forensic behavior. 🏭🛡️
Drawing on ESET’s investigations of 10+ 🇷🇺 Sandworm-linked incidents in 2025, we’ll unpack the group’s latest TTPs and a rarely documented collaboration between Sandworm and UAC-0099 during a destructive attack against a 🇺🇦 Ukrainian grain logistics company. 2/4
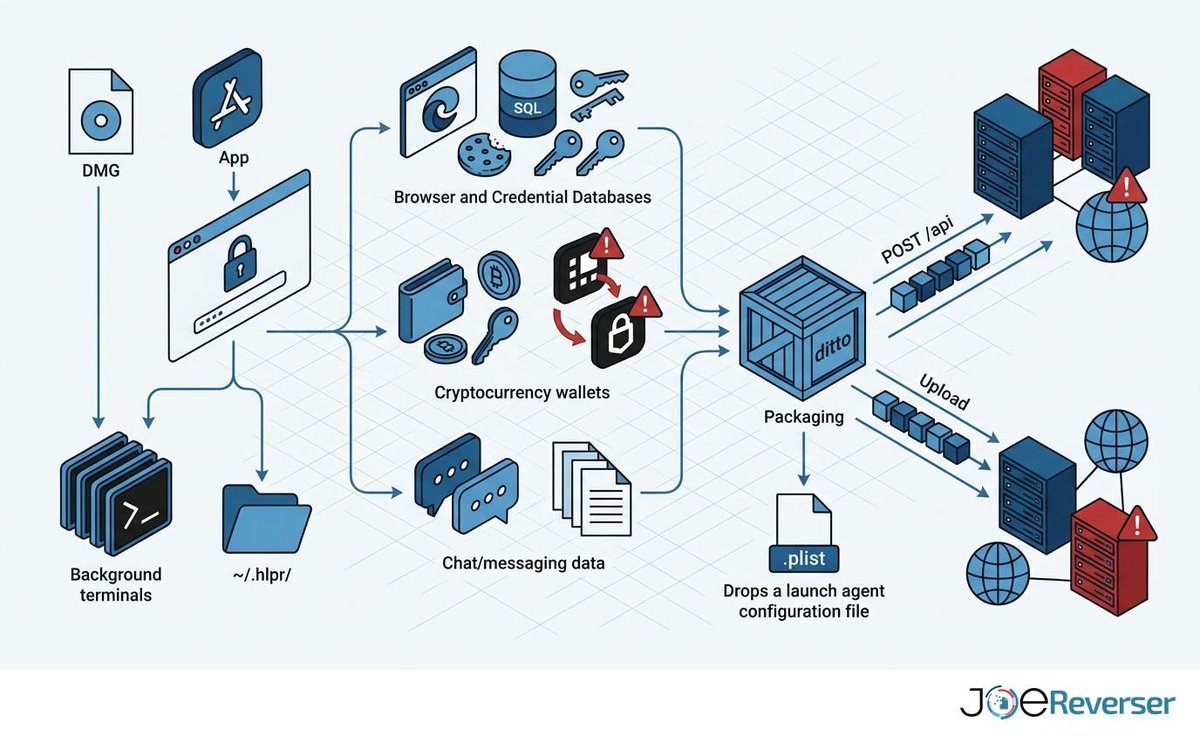
We stumbled upon this pretty little dropper on Mac abusing #Polygon smart contracts as a dead-drop C&C resolver. Upon decoding the server address, it pipes the second stage payload directly to osascript.
Contract: 0xA3a603F8a454a9c905b4c579Bb72628F7C15C2A0
Selector: 0x2686ecea
SHA-256: 7fc061fa6a4ae18c140bfb22c0f9d9080aa6bb4a302e6b32e38ecaca2d8ab196
Blockchain: Polygon
#macOS #AppleScript #malware
🚨 From compromised VPN credentials to MQTT and Matrix C2, three threat groups are targeting Russian enterprises.
NightEagle uses GhostContainer, Toy Ghouls now fields a custom backdoor, and Kaspersky links Hacking Cat to Gorilla RAT and destructive malware.
Read: https://t.co/9SxDUgC4Pj