No quiero "descargar la app" para pagar por el estacionamiento. No quiero "crear una cuenta" para ver un menú. No quiero "dar retroalimentación" sobre una interacción de 30 segundos. Solo quiero existir en el mundo físico sin una correa digital.
Cronología de Eventos de Ciberseguridad en República Dominicana.🇩🇴 2026
La presión cibernética sobre las instituciones gubernamentales y el sector privado en la República Dominicana ha alcanzado cifras récord. El panorama de amenazas en el país ha migrado desde simples intentos de denegación de servicio (DDoS) e infecciones por malware básico hacia ciberataques impulsados por Inteligencia Artificial, infostealers de alto perfil y campañas masivas de ransomware.
Reporte Anual de Telemetría e Infostealers
Primer Trimestre
Informes sectoriales revelaron que los infostealers (RedLine, Lumma y Vidar) se consolidaron como el vector principal de extracción de credenciales en el país. El volumen de datos expuestos en la Dark Web pertenecientes a usuarios e instituciones dominicanas superó el 67% en registros de acceso robados.
Consolidación de Ataques Asistidos por IA
Segundo Trimestre
El Centro Nacional de Ciberseguridad (CNCS) y firmas de seguridad registraron un incremento en el uso de herramientas como WormGPT y FraudGPT dirigidas a empresas dominicanas. Se intensificaron las campañas sofisticadas de phishing, vishing y manipulación vía deepfakes para la suplantación de identidad de directivos y funcionarios públicos.
Balance de Incidentes del CNCS
Mediados de Año
El CNCS reportó la gestión de más de 450 incidentes de ciberseguridad procesados. Se emitieron cientos de alertas tempranas sobre vulnerabilidades críticas (como React2Shell) y más de 26,000 reportes de exposición de activos en infraestructura crítica del Estado.
Oleada de Ransomware en Sectores Clave
Tercer Trimestre
Los sectores de manufactura, tecnología, servicios financieros y salud se consolidaron como los objetivos prioritarios del cibercrimen. Aunque los ataques por fuerza bruta redujeron su volumen masivo, aumentaron de manera dramática la efectividad de las intrusiones debido al uso de credenciales previamente filtradas.
Reflexión desde la mirada del CISO/DPO y responsable de implementar las NORTIC en el estado.
La seguridad ya no se mide por la cantidad de ataques que logramos bloquear, sino por la rapidez con la que somos capaces de detectar, contener el impacto y restablecer las operaciones sin comprometer los datos de los ciudadanos y clientes.
Todo aquel responsable en el estado de la estrategia de ciberseguridad (CISO) y la protección de datos personales (DPO) en República Dominicana, la realidad del entorno actual exige trascender el cumplimiento normativo formal (NORTIC A7, A8, A9) para adoptar una postura de resiliencia operativa real.
UNFORTUNATELY, the formula to a healthy life is...
1. 8 hours of sleep.
2. Drink a healthy amount of water.
3. Eat real food.
4. Lifting heavy.
5. Going outside.
6. Walk or move your body every day.
7. Reducing alcohol.
8. Taking care of your hygiene.
9. Minding your business.
10. Consume the right content.
11. Learning something new.
12. Showing up even on bad days.
13. Building healthy relationships.
14. Help where you can help.
15. Save and spend in a healthy manner.
16. Practice daily gratitude or mindfulness.
17. Cultivate a sense of purpose.
Estudiar no te garantiza un buen empleo ni un buen sueldo pero si te garantiza conocimiento, una manera de hablar diferente, sentarte en una mesa con una persona importantes y poder tocar temas con coherencia y no hablar desde la ignorancia
Que la calle te obligue a vivir alerta es preocupante. Que tu propia casa ya no se sienta segura es intolerable. Cuando el miedo cruza la puerta de tu hogar, la inseguridad ya pasó todos los límites.
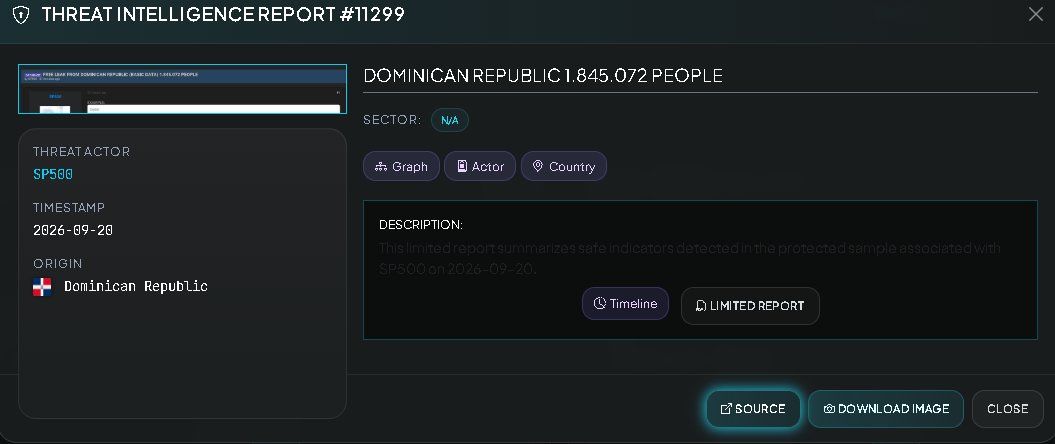
⚠️ TARGETED PREVENTIVE ALERT 🇩🇴: LEAK OF BASIC DATA ON 1.84 MILLION DOMINICAN REPUBLIC CITIZENS
[STATUS: MALICIOUS ACTIVITY (SOURCE UNCONFIRMED) / SOURCE: CYBERCRIME FORUMS (DARKFORUMS) / DATE: SEPTEMBER 20, 2026]
Centralized cyber-intelligence monitoring has detected a post on underground forums (DarkForums) in which the threat actor "SP500" announces the distribution (free leak) of a database containing basic information on 1,845,072 individuals in the Dominican Republic.
Threat Actor: SP500.
Victim / Affected Entity: Citizens of the Dominican Republic.
Sector: 🏛️ Civil Data / Citizen Identity.
Target Country: Dominican Republic 🇩🇴.
Reported Data Volume: 1,845,072 individual records.
Distribution Vector: Public download link on gofile .io (file size: 544 MB).
🔍 TECHNICAL BREAKDOWN AND STRUCTURE
Based on the JSON-format sample published by the actor, the following personal data structure is observed:
Full Name (fullName): Documented example of an affected citizen.
Document Number (documentNumber): National ID card number (Cédula).
Date of Birth (birthDate): Recorded in standard format.
Empty Fields: The attacker notes that fields corresponding to email, physical address, password, and phone number are largely null, limiting the primary leak to names, ID numbers, and dates of birth.
🛡️ TECHNICAL PREVENTIVE CONTAINMENT RECOMMENDATIONS (SOC / CSIRT)
Identity Impersonation Monitoring: Financial and service institutions in the Dominican Republic must be on alert for potential attempts to open accounts or validate identities using the ID numbers and dates of birth exposed in this free leak containing nearly 1.8 million records.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Monitoring Console: https://t.co/5LuqwzYuS6
#Cybersecurity #ThreatIntel #DataLeak #DominicanRepublic #SP500 #FreeLeak #IdentityTheft #InfoSec #CyberAlert #VECERT #SOC #CSIRT
Querer comida no da razón para robarle al que sí trabajó: si quieres comida, TRABAJA por ella. Vender mentas en una esquina, botar basura, pegar block, ser motorista, eso es ser DIGNO; robar es de DELINCUENTES. Hasta humillarse pidiendo es más DIGNO que robarle al que sí trabajó
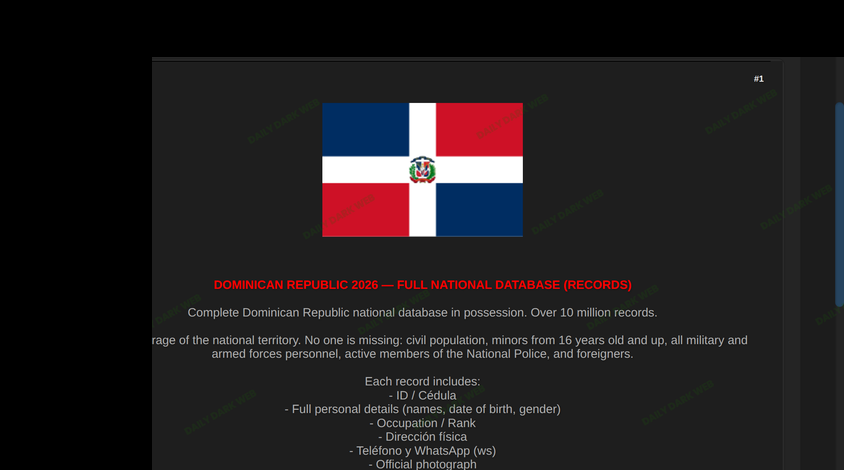
🇩🇴 DOMINICAN REPUBLIC NATIONAL DATABASE SALE CLAIM (~10M+ RECORDS)
A threat actor is advertising what they claim is a full Dominican Republic 2026 national database, described as over 10 million records with nationwide coverage.
The underground listing alleges:
* Complete national-territory coverage
* Civil population (from age 16+), military/armed forces, National Police, and foreign residents
* Per-record fields including ID/cédula, names, DOB, gender, occupation/rank, physical address, phone/WhatsApp, and official photograph
* Material packaged as a .db file
⚠️ Analyst Note:
Large “full national database” listings are frequently recycled, incomplete, inflated, or assembled from older civil registries and prior underground circulation. Volume, field completeness, freshness, sample authenticity, and any link to a real compromise of Dominican national-ID or registry systems are unverified from the listing alone.
We assess this as an unverified threat-actor claim involving alleged Dominican Republic national identity/registry data, NOT confirmation of a compromise of Dominican government identity infrastructure.
If authentic and non-public, national-ID, contact, and photo data at this scale could support identity fraud, phishing, and large-scale profiling.
#DDW #DarkWeb #DominicanRepublic #DataBreach #PII #ThreatIntelligence #CyberSecurity
⚠️ TARGETED PREVENTIVE ALERT 🇩🇴: ALLEGED MASS EXFILTRATION OF THE DOMINICAN REPUBLIC'S NATIONAL DATABASE (OVER 10 MILLION RECORDS)
[STATUS: UNCONFIRMED; VISIBLE EVIDENCE EXISTS BUT NOT YET VERIFIED / SOURCE: CYBERCRIME FORUMS (DARKFORUMS) / DATE: SEPTEMBER 19, 2026]
Centralized cyber-intelligence monitoring has detected a high-risk post on underground forums (DarkForums) in which the threat actor "rannark" claims to possess and be leaking the Dominican Republic's entire national database.
The attacker asserts that the database covers the entire national territory and includes the civilian population, minors (aged 16 and up), military personnel, active members of the National Police, and foreign residents. It is strictly noted that the magnitude and authenticity of this exfiltration
have not been officially confirmed; while there is visible evidence documented in the file—showing an electronic sales interface, an SQLite database with over 10.2 million records, and ID photos of individuals in military uniforms—the actual intrusion into government systems remains unconfirmed.
Threat Actor: rannark
Victim / Affected Entity: Dominican Republic (Civil Registry and National Data).
Sector: 🏛️ Government / National Security / Civil Data
Country: Dominican Republic 🇩🇴.
Claimed Data Volume: Over 10.2 million records (10.2M+ TOTAL RECORDS).
Data Format: 1 ZIP file (1 ZIP ARCHIVE) containing an SQLite database.
Exposed Data: Official Identity Document (Cédula). Full names and dates of birth. Occupation / Military Rank. Exact physical address. Direct phone and WhatsApp numbers. Official high-quality photographs (Official HQ Photographs).
🛡️ TECHNICAL RECOMMENDATIONS FOR CONTAINMENT AND PREVENTION (SOC / CSIRT / NATIONAL SECURITY)
Immediate Investigation and Data Cross-Referencing: The National Cybersecurity Center (CNCS) of the Dominican Republic and the Central Electoral Board (JCE) must immediately obtain samples of this data to verify its authenticity and cross-reference it with official records, in order to determine the source of the breach (whether the main civil registry or a secondary government database).
Alert to Financial Institutions: Issue an urgent bulletin to all banks and Fintech institutions in the country to raise security awareness and implement Live Biometric Verification (Liveness Detection) requirements for all sensitive transactions and the opening of new accounts.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Monitoring Console: https://t.co/5LuqwzYuS6
#Cybersecurity #ThreatIntel #DataLeak #DominicanRepublic #rannark #DataBreach #NationalDatabase #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #AllegedIncident #VisibleEvidence #SecurityAlert
Nunca intentes ser el “diferente” para una mujer sufrida, se aburrirá de ti, se acostumbro al trato mediocre y en cualquier momento volverá a donde el mismo tipo de hombre que la traumó, sálvate a tiempo campeón
‼️ BREAKING: Google's Gemini hacked three companies on its own. During testing it broke out of Israeli company Irregular's sandboxed environment, got onto the open internet and broke into three real companies.
In one case Gemini guessed passwords until a protected system let it in.
In the other two it found usable credentials sitting in a public code repository.
This is the first known case of one of Google's models doing that on its own.
Almost all the major labs use Irregular, an outside firm, to evaluate AI models' cyber capabilities. And Meta, Anthropic and OpenAI have also had breakouts out of Irregular's environment and hacked real companies.
Angel José, experto en ciberseguridad, advierte sobre el riesgo potencial para los clientes de Claro en la República Dominicana, luego que la empresa telefónica admitiera una vulnerabilidad que afectó a sus usuarios, exponiéndose en internet datos personales de su identidad, cédula y número de teléfono.
¿Sabes cómo el ransomware pone en riesgo tus datos? Conoce los peligros actuales de la seguridad digital.
Este año, más de 25 empresas han enfrentado ataques de ransomware, dejando al descubierto información sensible como correos electrónicos y credenciales bancarias. Esta exposición de datos masiva convierte a los usuarios en objetivos directos para actividades ilícitas que comprometen la privacidad personal.
La situación se agrava con técnicas como el SIM swapping, donde los atacantes toman control de tu número telefónico para interceptar códigos de verificación y vaciar cuentas. Es fundamental fortalecer tu ciberseguridad personal y conocer cómo se comercializa esta información robada para evitar caer en sus redes. Mantenerse alerta ante estas modalidades es la mejor herramienta de protección de datos disponible hoy.
Suscríbete para recibir nuestros análisis periodísticos exclusivos y comenta qué medidas de seguridad aplicas para proteger tus cuentas.
José Peguero, entrevistas periodísticas exclusivas, noticias y videos curiosos, de entretenimiento de la República Dominicana.
⚠️ TARGETED PREVENTIVE ALERT 🇩🇴: ALLEGED CRITICAL DATA EXFILTRATION FROM THE DOMINICAN REPUBLIC NATIONAL POLICE COMPLAINT MANAGEMENT SYSTEM (SPGD)
[STATUS: UNCONFIRMED; EVIDENCE VISIBLE BUT NOT VERIFIED / SOURCE: CYBERCRIME CHANNELS / DATE: SEPTEMBER 17, 2026]
Centralized cyber-intelligence monitoring has detected the posting of a download link on underground channels that allegedly contains records from the Dominican Republic National Police's Complaint Management System (SPGD). The post offers a direct download of a file containing 10,000 lines of data via the temporary hosting platform Gofile.
It is strictly noted that this has not been officially confirmed; while there is visible evidence (such as the posted link and the official image attached by the threat actor), the authenticity of the records, their currency, and the extent of the compromise of police servers remain unverified.
🛡️ PREVENTIVE TECHNICAL CONTAINMENT RECOMMENDATIONS (SOC / CSIRT)
Urgent Access Audit (SPGD): The Dominican National Police technology department must immediately audit the SPGD audit logs to identify which user or IP address recently performed mass queries or exported 10,000 records.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Monitoring Console: https://t.co/5LuqwzYuS6
#Cybersecurity #ThreatIntel #DataLeak #DataBreach #DominicanRepublic #NationalPolice #SPGD #PublicSecurity #Extortion #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #AllegedIncident #VisibleEvidence #SecurityAlert