Building fast is great, but shipping with broken auth is a nightmare. 🚨
We review dozens of AI apps. The most common flaw? Exposed API keys in the frontend.
Quick checklist before you deploy:
✅ No .env files in GitHub
✅ Rate-limit your auth endpoints
✅ Check CORS policie
Shipping fast? 🚀 Don't leave your API keys or auth endpoints exposed.
We audit AI & SaaS apps at findhyde to catch flaws before hackers do.
Need a quick security tip for your stack? DMs open! 🛡️
#CyberSecurity#SaaS
Your SaaS has a beautiful UI.
But your backend is leaking user data. 🤫
At findhyde, we don't just run automated scanners. We hunt for the deep logic flaws (Auth bypass, IDOR, API leaks) that tools miss.
Need an external set of eyes before your next launch?
Drop a " " below or DM me.
@Ankita_05_@findhyde
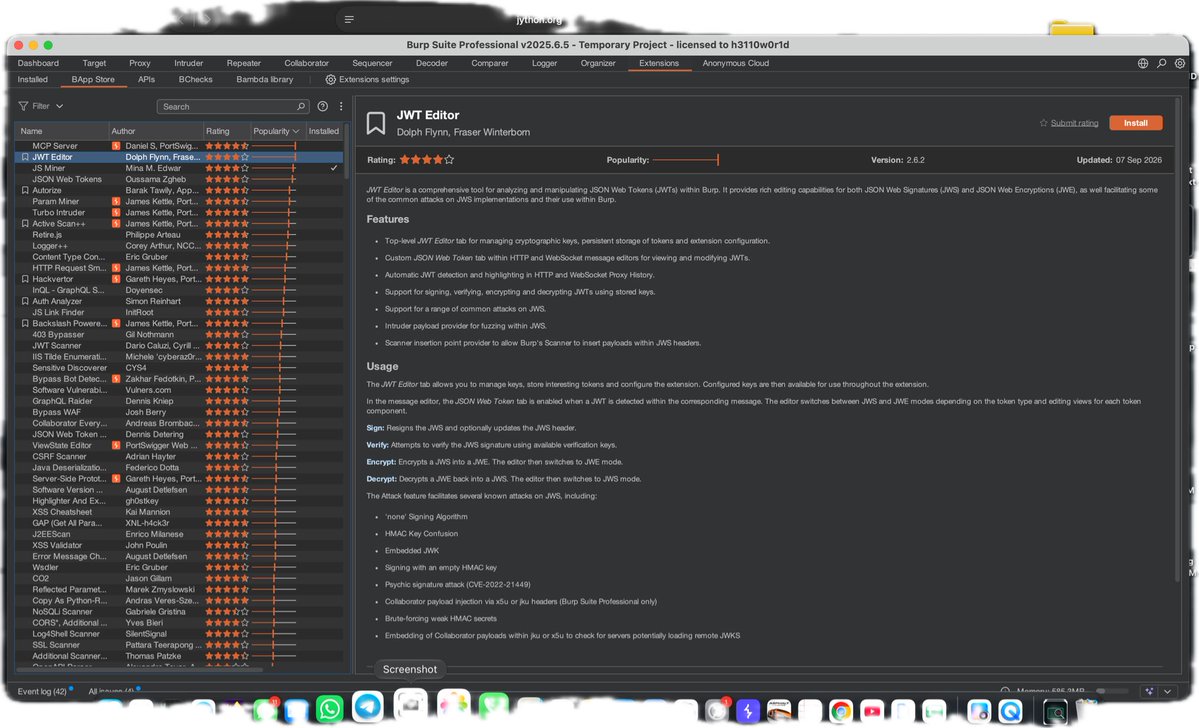
If you're into AppSec, save this list:
🔍 JS Miner: Finds hardcoded secrets & endpoints in JS files.
☁️ Anonymous Cloud: Spots public S3 buckets & subdomain takeovers.
🚪 403 Bypasser: Fuzzes paths/headers to bypass forbidden errors.
🔐 Authorize: Finds broken access control (IDOR) by replaying low-priv requests.
🕸️ InQL: Maps hidden GraphQL queries and mutations.
📡 Collaborator Everywhere: Injects OOB payloads into headers for blind callbacks.
🧬 Hackvertor: Builds nested encoding chains right inside Repeater.
Automation finds the clues. A hacker's brain connects the dots. 🧠
Which one is your favorite?
Found this old gem in my archive. 💎 The 'Comet' badge for 10 valid reports on a single target... except I actually submitted 22.
Finding one bug is luck. Finding 22 in the same app is deep understanding. This is the level of persistence we bring to every client at @findhyde.
Secure your app
This is how we test at .Need this level of deep security testing for your SaaS? Let's connect
@yeswehack
🚨 The #1 mistake I see in modern SaaS apps?
Exposing backend API keys in frontend code. 💀
🔐 Never trust the client side.
Keep sensitive keys on the backend.
Want to know if your app is leaking secrets?
DM me.
Let’s secure your app before attackers find the weakness.
I'm Ankita, Co-founder of @findhyde. We help startups secure their Web Apps & APIs.
🛡️
Sharing my journey of building a cyber-security startup at 20, along with tips on API security.
👇
Let's connect! What are you building today ?
# BuildlnPublic #WomenIn Tech
Most startups ignore API security until it's too late 🚨
3 quick checks before launching your SaaS.
1️⃣ Exposed API keys in code ?
2️⃣Rate limiting enabled ?
3️⃣ Strong Authentication?
Which one are you guilty of skipping? Be honest 👇
# Saas #CyberSecurity.
The #1 mistake I see in modern SaaS apps?
Exposing your backend API keys in the frontend code. 💀
Never trust the client side. Always secure your backend.
Want to know if your keys are exposed? Drop a '👀' below or DM me. Let's secure your app.
💻 Working on a client security assessment—testing web apps, finding vulnerabilities, and helping strengthen defenses.
My goal: help businesses discover security gaps before attackers do.
Let’s connect.
🌐 https://t.co/Ep2pcqYotE
#CyberSecurity#Pentesting#findhyde#hack
Building a SaaS product? Don’t wait for a security incident to test your application.
FindHyde helps teams identify security weaknesses in:
🔐 Web applications
🔐 APIs
🔐 Authentication & authorization
Planning a security assessment? Let’s connect.
🌐 https://t.co/zGpLMV0sXq
Team findhyde is growing! 🚀
Huge congrats to our researcher Mohd Mukammil for this Certificate of Appreciation from @INDmoneyApp's Bug Bounty program.
We help SaaS & fintech startups secure their APIs (100+ valid bugs).
Let's chat: https://t.co/zGpLMV0sXq