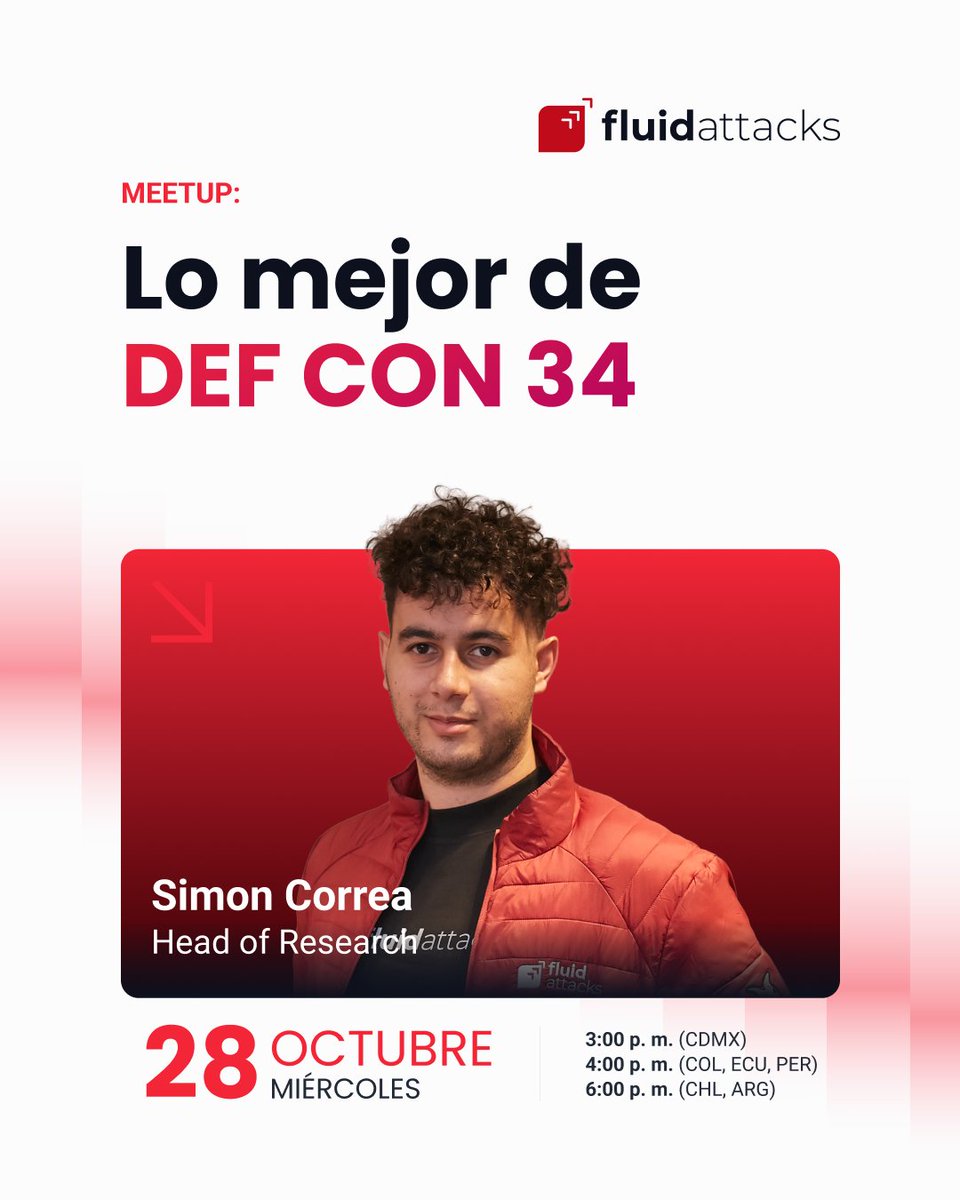
En el meetup de octubre, Simón Correa (Head of Research @fluidattacks) comparte lo mejor de #DEFCON34: cómo la IA ya hace descubrimientos propios en seguridad y el riesgo que abren los agentes de IA con acceso a repos, terminal y credenciales.
Regístrate: https://t.co/ArvB5LIDrs
Este 23 de octubre nuestro CTO Juan Restrepo estará en la tarima en #DevOpsDaysBogotá con su charla “Trilema moderno: IA, software y seguridad”, a las 3:26 p.m. Si aún no tienes tu entrada, ingresa a nuestra página de eventos y obtén un 20% de descuento 👉 https://t.co/xThXNPUzJa
Fluid Attacks' research team found a zero-day vulnerability in NoSleep. As a #CNA, we assigned the ID CVE-2026-19755. Details here: 🔗 https://t.co/0aYIS9CMbd. We have disclosed 280 #CVE to this date: 🔗https://t.co/fgMrQcycLm.
#News | For the third consecutive year, Fluid Attacks has achieved SOC 2 compliance! 🔐
Our clients rely on us to protect their software and data. Honoring that trust starts with securing our own house.
Explore the updated report: https://t.co/zJYddM6s7U
@Jiler830219 ¡Te esperamos el 28 de octubre en el meetup! Si aún no te registras, aquí está el enlace para que vayas a hacerlo y no te pierdas el evento virtual https://t.co/ArvB5LJbh0
En el meetup de octubre, Simón Correa (Head of Research @fluidattacks) comparte lo mejor de #DEFCON34: cómo la IA ya hace descubrimientos propios en seguridad y el riesgo que abren los agentes de IA con acceso a repos, terminal y credenciales.
Regístrate: https://t.co/ArvB5LJbh0
🚀 El 23 de octubre estaremos en DevOpsDays Bogotá como patrocinadores Diamante. Si vas a estar, pásate por nuestro stand. ¿Aún no tienes tu entrada? Obtén un 20% OFF 👉 https://t.co/xThXNPU1TC.
Part 1 of our security horror stories is out, just in time for Halloween. Early readers call it "the reason I rotated every API key at midnight."
What should we add to part 2? Share your scariest story below. 👀
En el meetup de octubre, Simón Correa (Head of Research @fluidattacks) comparte lo mejor de #DEFCON34: cómo la IA ya hace descubrimientos propios en seguridad y el riesgo que abren los agentes de IA con acceso a repos, terminal y credenciales.
Regístrate: https://t.co/ArvB5LJbh0
Spotting fraud risk is half the job. Getting it to the people who can fix it is the other half.
Our Fraud risk center lets you escalate a system or an entire fraud category, notifying responsible contacts with the context to act.
See how 🔗 https://t.co/ZPbdh8qaDP
A zero-day vulnerability in Akaunting was discovered by an external pentester, then reviewed and documented by Fluid Attacks: ID CVE-2026-19198. You can find the full details here: 🔗 https://t.co/tK4ef4T8Kt. We have disclosed 279 #CVE to this date: 🔗https://t.co/1Hys9Co85I.
A full vulnerability backlog won't give fraud teams priorities.
Our Fraud risk center filters for vulnerabilities that:
→ Map to fraud categories
→ Are open, with nonzero risk
→ Are internet-reachable
→ Affect confidentiality or integrity
Highest-risk category first. 👇
@Jiler830219 Buen punto 👏 Esa relación entre lo que un agente puede hacer y los accesos que le damos es uno de los temas que abordará Simón en el meetup, a partir de lo que vio en DEF CON 34. ¡Te esperamos! Regístrate aquí: https://t.co/ArvB5LIDrs
En el meetup de octubre, Simón Correa (Head of Research @fluidattacks) comparte lo mejor de #DEFCON34: cómo la IA ya hace descubrimientos propios en seguridad y el riesgo que abren los agentes de IA con acceso a repos, terminal y credenciales.
Regístrate: https://t.co/ArvB5LIDrs
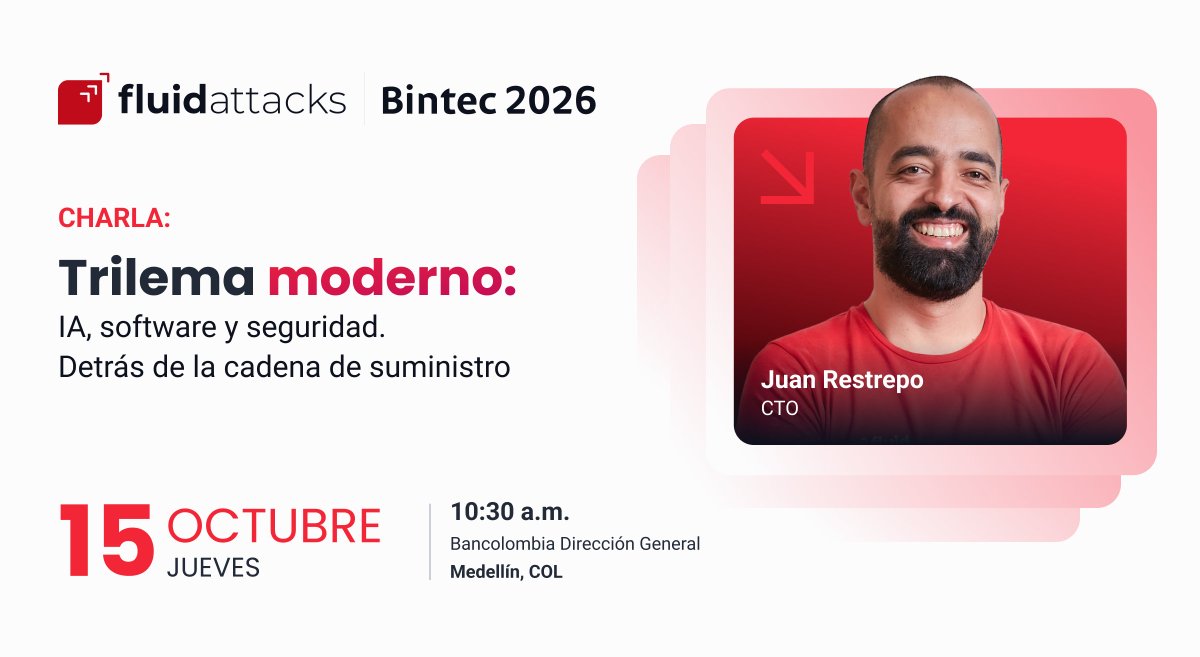
Si estarás en #Bintec, agéndate este jueves 15 de octubre a las 10:30 a. m., Juan Restrepo presenta su charla "Trilema moderno: IA, software y seguridad. Detrás de la cadena de suministro". Una mirada clara a los riesgos de la cadena de suministro y cómo abordarlos 🔐.
En el meetup de octubre, Simón Correa (Head of Research @fluidattacks) comparte lo mejor de #DEFCON34: cómo la IA ya hace descubrimientos propios en seguridad y el riesgo que abren los agentes de IA con acceso a repos, terminal y credenciales.
Regístrate: https://t.co/ArvB5LJbh0
An old staging server hides logs from last night, an API key nobody created, and a webhook sending data to a URL you've never seen.
These are the monsters no developer wants to find, and most have been there far too long.
Let's hunt them down together 🔦 https://t.co/IVaK5nSkA1
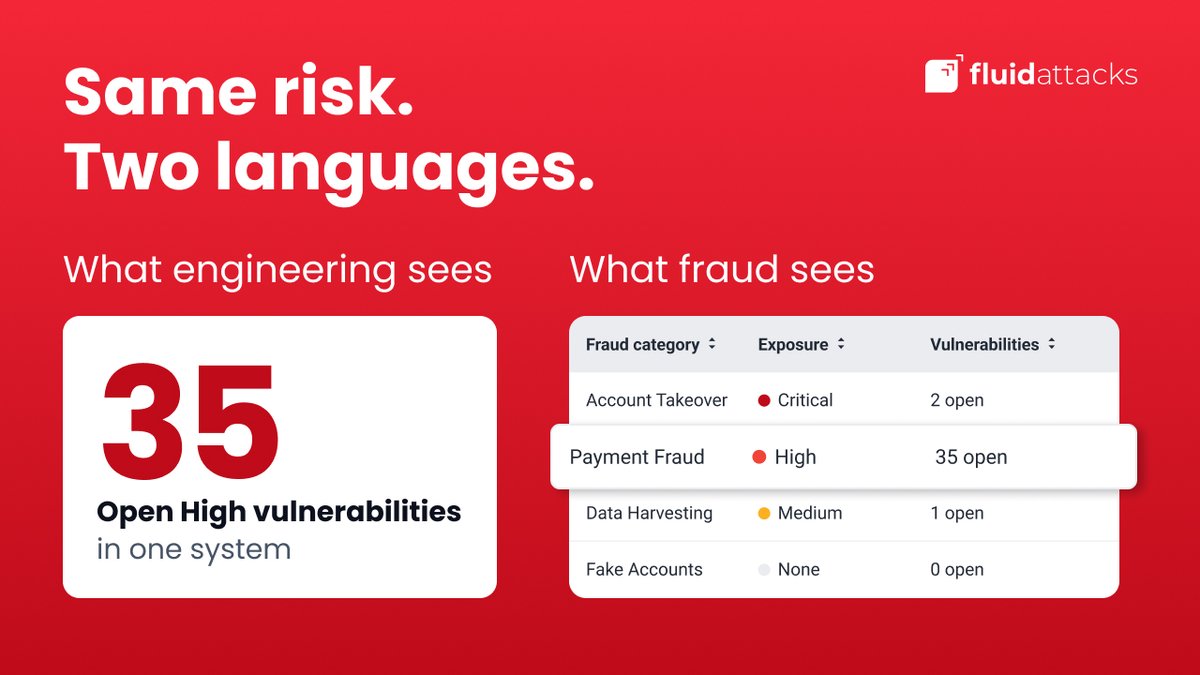
Your fraud and engineering teams may be looking at the same risk, they just call it different things. Our Fraud Risk Center turns vulnerabilities into fraud outcomes like Account Takeover and Payment Fraud.
Same data. Shared priorities. One conversation 🔗https://t.co/ZPbdh8qItn
En el meetup de octubre, Simón Correa (Head of Research @fluidattacks) comparte lo mejor de #DEFCON34: cómo la IA ya hace descubrimientos propios en seguridad y el riesgo que abren los agentes de IA con acceso a repos, terminal y credenciales.
Regístrate: https://t.co/ArvB5LJbh0
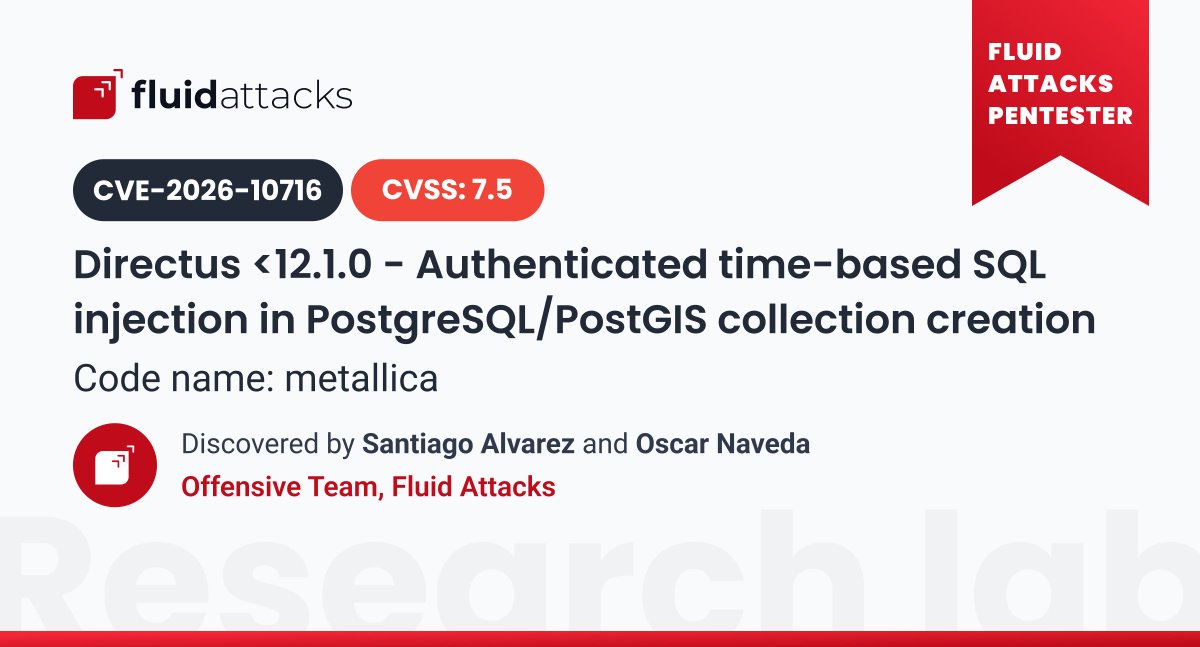
Fluid Attacks' research team found a zero-day vulnerability in Directus. As a #CNA, we assigned the ID CVE-2026-10716. Details here: 🔗 https://t.co/ATmvW1d8r1. We have disclosed 278 #CVE to this date: 🔗https://t.co/fgMrQcyKAU.