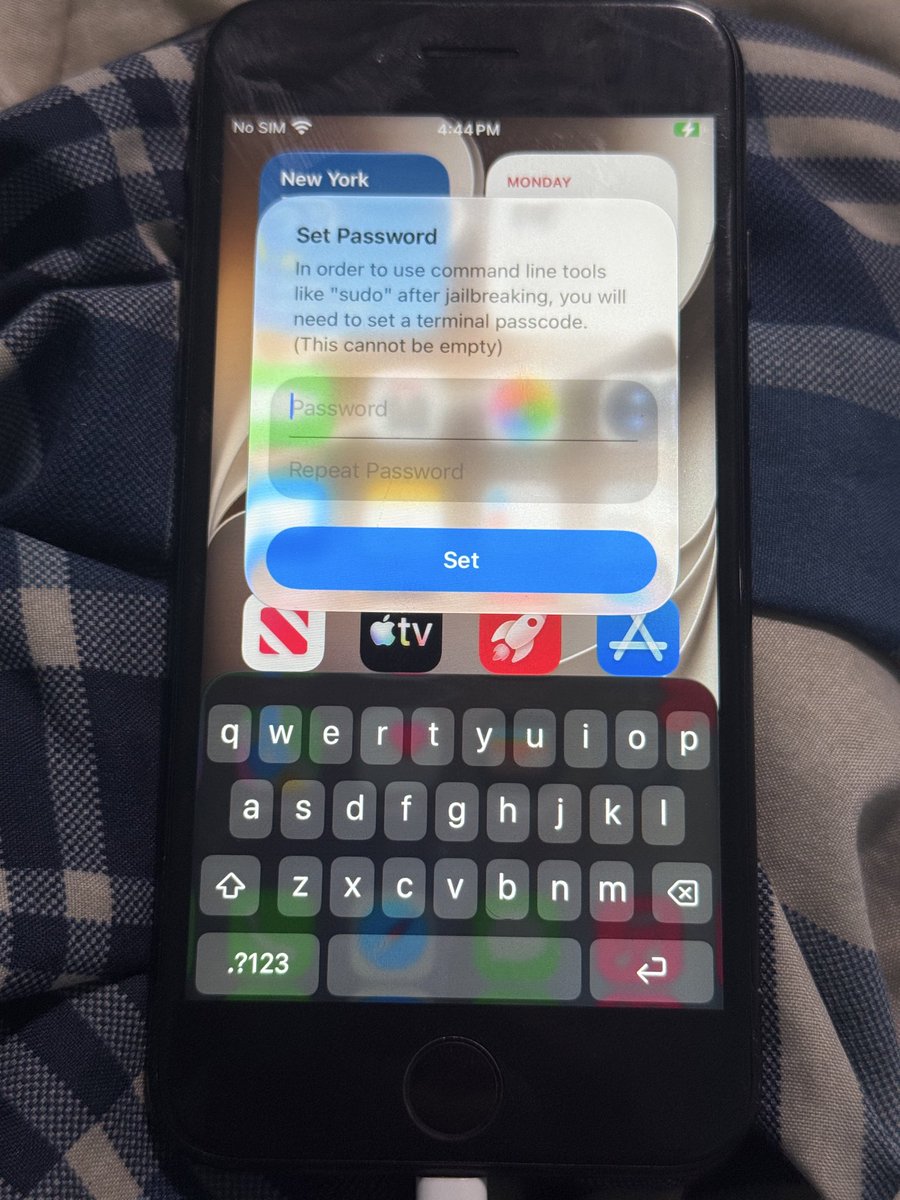
Introducing bad_query, a zero-day sandbox escape PoC for iOS 26 and 27.
This bug has been patched earlier today in iOS 27.0 beta 5, but not 26.6.1. Be careful out there, and use this for good.
Coordinated release with @0xjohnny and @rooootdev :p
https://t.co/UYYpqH37w6
@nitzukai 1) Developing for watchOS is a legitimate pain in the ass.
2) watchOS isn't really an app-focused platform nowadays (it's more about health tracking than it was in, say, 2015.)
3) The novelty is gone, compared to when it was new.
Rest in peace to maybe the most insane bug ever. This was bound to happen…
I barely did anything with it, so I don’t have much to show unfortunately LOL
@Ka_nek1@0xjohnny The bug is patched and Lycorine’s public repo doesn’t even have the actual TSS communication included, you can’t compile it anyways
Not to mention it’s an Xcode project, what do you need a build script for
@Burn48668749736 I didn’t report it to Apple, someone actually *did*, but Apple said it wasn’t a security issue (maybe due to the report being bad, or Apple legitimately just not thinking it was a security flaw)
It also isn’t my bug to share or report, if it was mine, I would have released it.
@nairiz12 I detailed a little bit about it here, but to answer your question yes, it is server-side. It can no longer be used on devices that don't already have it.
https://t.co/5lANt8AeB2
@kcFive12 tldr:
Generic Cryptexes were signed by TSS the same way they would if the device was an SRD.
There’s supposed to be an ECID whitelist for SRDs, so either the whitelist never existed, or it was never actually functional.
@zemabinks If it was released publicly, it would've probably been patched sooner. Developers needed time to get a sane environment (tweak injection and jailbreak apps) out of it.
There was more than enough information shared publicly to recreate it yourself, if you cared that much.
@OMGItsRealMark@haxi0sm Devices that already have a Cryptex signed for them can continue to reuse it (as long as the Cryptex nonce doesn’t change, which only happens on updates anyways)
This can’t be set up on new devices though
@N104AP It’s not the same kind of Cryptex as a DeveloperDiskImage or a Rapid Security Response / Background Security Improvement
The entire bug was that TSS signed a Cryptex for a device the same way it would for a Security Research Device. Which can then be installed to the device…
@kcFive12 tldr:
Generic Cryptexes were signed by TSS the same way they would if the device was an SRD.
There’s supposed to be an ECID whitelist for SRDs, so either the whitelist never existed, or it was never actually functional.
Heads up: Apple patched my iOS sandbox escape, Airlift, in iOS 27.2 beta 3.
Confusingly, as of now, Airlift works on 27.0, 27.0.1, 27.2b1, and 27.2b2. I'm assuming 27.1 public will have it patched as well.
Remember, there are always more bugs...