@maro254 📊 There are significant distinctions between "forecasting profitability" and "forecasting gameplay enhancement."
In any case: it's your game, your rules, your decisions –
we'll adapt as usual. #WoCPlayer
@ItaloTreno in 1 week 2 delay of 30 min each 😞 I could have spent my time in a different way than in a train station walking up and down...
Anyway just the train i booked are late, so it's not about you it's about me 💔 we need a break
The Exchange team has created a solution to address the problem of messages stuck in transport queues on Exchange Server 2016 & Exchange Server 2019 due to a latent date issue in a signature file used by the malware scanning engine within Exchange Server. https://t.co/vTHzGUfbVP
How to test your apps for #log4shell vulnerability
1. Generate a DNS token https://t.co/vCzVG0O03i
2. Wrap that token in
Prefix: ${jndi:ldap://
Suffix: /a}
3. Use that value in search forms, profile data, settings etc. of your apps
4. Get notified when you triggered a reaction
Following the Jupiter Rockets walkthrough range @ #SANSHackFest the 1 challenge we couldn't walkthrough, so here it is, J1bh4t's PCAP challenge:
https://t.co/eq71UbnVgE : game code: cagey-ray
Good Luck!
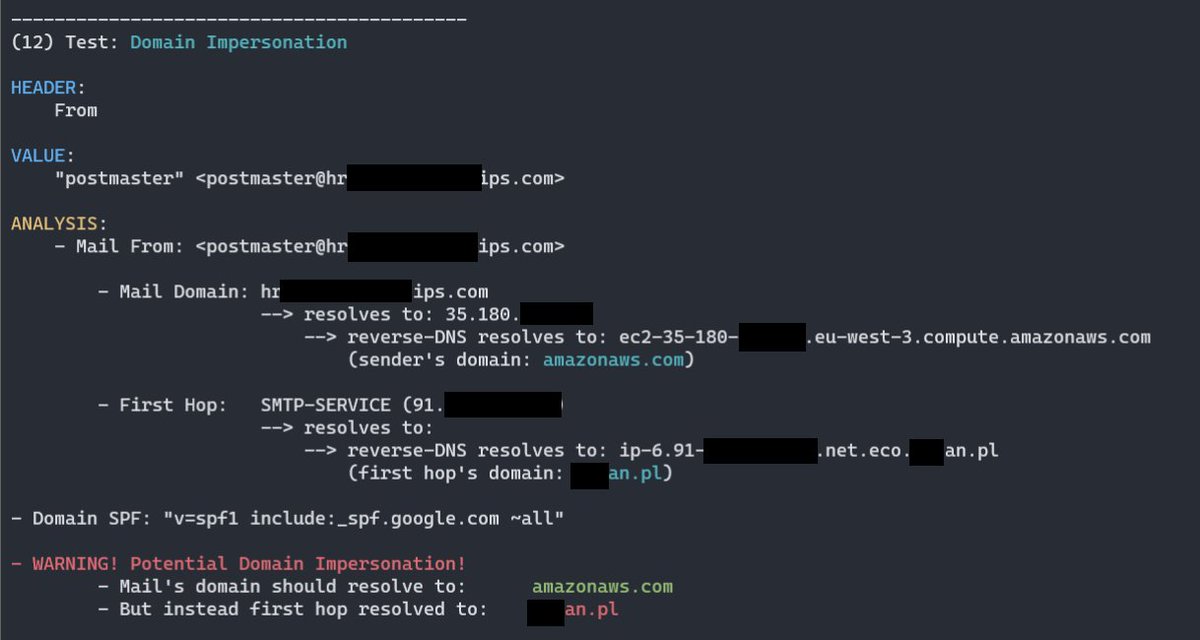
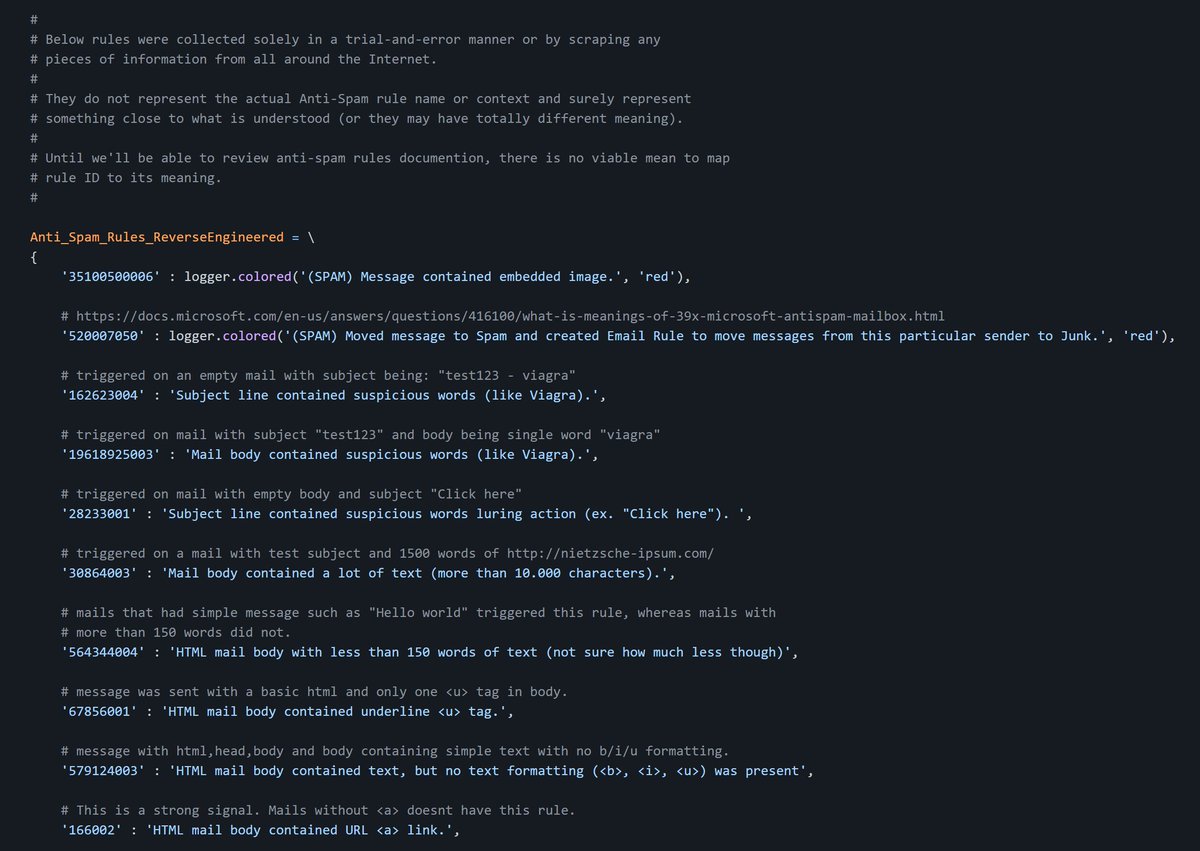
Recently I started digging into Office365 Anti-Spam & spent a lot of time decoding and comprehending SMTP headers.
Results are already satisfying: 10+ SFS/ENG rules "reverse-engineered"!
You're on a phishing now? Give my https://t.co/XTnM8g3dsi a ride!
https://t.co/3IiSpCrIFU
It feels too nice to take a break and analyze some silly ransomware after destroying my mental with LockBit 🥲.
Check out my analysis of #AtomSilo#Ransomware here! 👾🥳
https://t.co/nYJ09r3eeT
h/t to @Arkbird_SOLG for the sample
RE tip of the day: Malware can escape a debugging session by implementing TLS callbacks that will be executed before the entry point. Their addresses are pointed by the PE header's data directory IMAGE_DIRECTORY_ENTRY_TLS
#infosec#cybersecurity#malware#reverseengineering
Reverse Engineer's Toolkit : This is a collection of tools you may like if you are interested on reverse engineering and/or malware analysis on x86 and x64 Windows systems : https://t.co/M8WZ7UQScB
@GossiTheDog This is even more severe. The RCE is the simplest RCE you can ever imagine. Simply remove the auth header and you are root. remotely. on all machines. Is this really 2021?
Mass exploitation of Atlassian Confluence CVE-2021-26084 is ongoing and expected to accelerate. Please patch immediately if you haven’t already— this cannot wait until after the weekend.