with Mastercard & MoonPay people,businesses to pay, be paid using stablecoins across global markets ..MoonPay’s existing services, which include buying & selling crypto using credit cards,bank transfers,Apple Google Pay more ..
(https://t.co/SgaZuaAlfh)
(https://t.co/MCxduiNlJJ)
I stopped using third-party adblock VPNs after discovering Android's built-in Private DNS toggle
How to set up a Private DNS on your Android phone
Android makes switching to an ad-blocking DNS surprisingly easy
( https://t.co/dunGNG5eKC )
🚨🇪🇺EU launches a full-scale war on internet anonymity!
The European Union is preparing to roll out the so-called EU Kids Act, which will force every social media user to surrender their anonymity by handing over personal data.
Ursula von der Leyen and the rest claim this is about protecting children but the real reason is completely different.
Once anonymity is gone, social media users become fully visible to government agencies - and therefore easy targets for repression and censorship that is already exploding across the EU.
The Brussels political elite knows their dictatorship is running out of time.
On top of mass migration that has been proven to be used for electoral purposes, censorship, repression, and intimidation are now becoming standard tools in their political campaigns.
I bypassed streaming site VPN blocks by changing one hidden DNS setting on Android
Why I chose a smart DNS over a VPN
Targeting one specific problem Smart DNS can unlock multiple streaming services
( https://t.co/qbOlDwu5Ot)
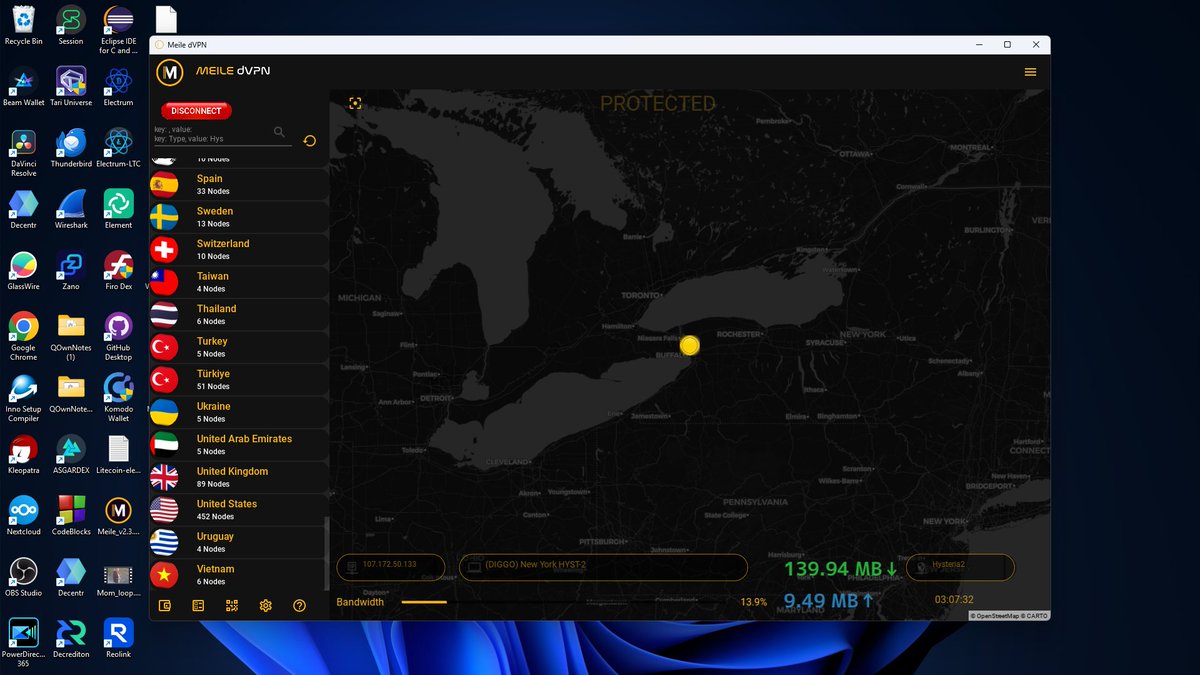
We just issued a pre-release for version 2.7.0 for Windows and MacOS.
This version includes the three new protocols introduced to Sentinel a month ago: Hysteria2, Xray, AmneziaWG. Also, a teaser not yet active but will be appearing in the v2.7.x series
You can test it out yourself by downloading it at: https://t.co/f8OE2qKPvG
Prediction markets. Now with leverage.
Perp lets you go long or short on real-world event probabilities, with no expiry.
Same predictions, more firepower.
Google just made the Pixel 11 a bad buy for GrapheneOS users.
The reason isn't the camera.
It's one missing security feature.
Pixel 11 launched without ARM Memory Tagging Extension (MTE), and GrapheneOS says that's a deal-breaker.
Why it matters:
• MTE blocks entire classes of memory exploits
• Pixel 8, 9, and 10 all had it
• GrapheneOS uses it across nearly the entire OS
• Stock Android barely uses it by default
GrapheneOS even says it may skip the entire Pixel 11 generation and focus on future Motorola flagships instead.
If you're buying a phone for GrapheneOS today, they recommend Pixel 8, 9, or 10 instead.
Would this change which Pixel you'd buy?
Android 17 can hide the sites you visit from network providers
Google is bringing ECH across the OS, obscuring destination domain names for supported sites and apps. Android 17 also adds local-network permission prompts
How the new privacy protections work https://t.co/GIezIZVobN
How to Enable Encrypted Client Hello (ECH) in Your Browser
(https://t.co/U7qfg7ceM7)
(https://t.co/djqBiXI5yI)
(https://t.co/8CBDPkzM1w)
Use a fallback DoH provider: Enabled
In Automatic DoH mode, use a fallback DoH provider
( chrome://flags/#fallback-dns-over-https )
The EU is introducing stricter security requirements for VPN services under its Cyber Resilience Act.
The new European standard covers VPN apps, servers and gateways, requiring encryption, authentication, key management and vulnerability handling.
VPN companies must provide stronger evidence that their security measures work and follow rules for actively exploited vulnerabilities.
Companies including NordVPN, Surfshark, Google, Cisco and Airbus developed the standard.
Revolut's "Security" Theatre: Banning the Most Secure Android on the Market While Coddling Eight-Year-Old Junk.
Revolut has decided your phone is dangerous. Not because it's unpatched. Not because it's rooted. But because you chose an operating system Google didn't rubber-stamp.
GrapheneOS users are being locked out of the app again. The project says Revolut is presenting the restriction as a security measure while actually enforcing Google Play licensing and device-certification requirements. Users already signed in are mostly fine, which points at checks fired during authentication or device verification. And the app has the nerve to tell you it's because Revolut is serious about keeping your data secure.
Here's the part that should make anyone's blood boil: Revolut's app still supports Android 9, a release that hasn't seen a security update in years. Sit with that. A device riddled with publicly documented, unpatched, actively exploited kernel bugs gets waved straight through. A locked-bootloader Pixel running verified boot, a hardened allocator, a hardened sandbox and the fastest patch cadence in the Android world gets shown the door.
That is not a security policy. That is a compliance checkbox wearing a security policy's clothes.
GrapheneOS previously found Revolut fingerprinting the build machine hostname and username, and worked around it by renaming them. They also found Revolut rejecting a verified boot state of yellow, which means a locked device running an aftermarket OS that the firmware is cryptographically verifying. Revolut looked at proof of cryptographic integrity and read it as a threat.
The tooling to do this properly exists. The Hardware Attestation API verifies actual device integrity, and Revolut was handed a compatibility guide long before any of this. They didn't want correctness. They wanted the cheap option, bolted on via third-party closed-source libraries that GrapheneOS calls a major security risk in their own right.
So the shape of it is clear. An outsourced dependency, wired to a Google monopoly gate, deciding which hardware you're allowed to hold your own money on. Meanwhile the genuinely vulnerable phones stay logged in, because they came with the right sticker.
If you're stuck, the current workaround is signing in with a disposable Google account to clear basic integrity, then installing Revolut through the sandboxed Play Store to satisfy the installer check. But a workaround is not a fix, and it should not be the user's job to engineer around a bank's laziness.
@Revolut, you don't get to sell security as a virtue while enforcing a vendor lock-in as one. Fix the check, or drop the pretence.
@TutaPrivacy Some android apps require Play Integrity API. This bannes operating systems like GrapheneOS that is Google independent.
I am really afraid that for future EU apps like the digital euro app will be using Play Integrity API that ties even more EU to Google
https://t.co/y9V763WlKK
Revolut recently banned using GrapheneOS without any justification. They're falsely claiming to do be doing it for security reasons. In reality, they're enforcing licensing Google Play. Revolut doesn't enforce security standards. It runs on Android 9 with no patches since 2018.
If you are looking to cash out crypto without a (neo-)bank account, check out the privacy crypto card by @AgoraCards, with minimal data requirements and higher limits than most competitors.
In order to get access, you will need my referral code during sign-up:
AGORA3078
Or directly visit through this link: https://t.co/pZ63dd9asl
Brave blocks this btw.
When you try to visit a page with a known tracking parameter in the URL (like ?si for YouTube), Brave removes the value from the URL before your browser makes the request.
This means the site still loads normally but without the tracking.