Thank you for your support.
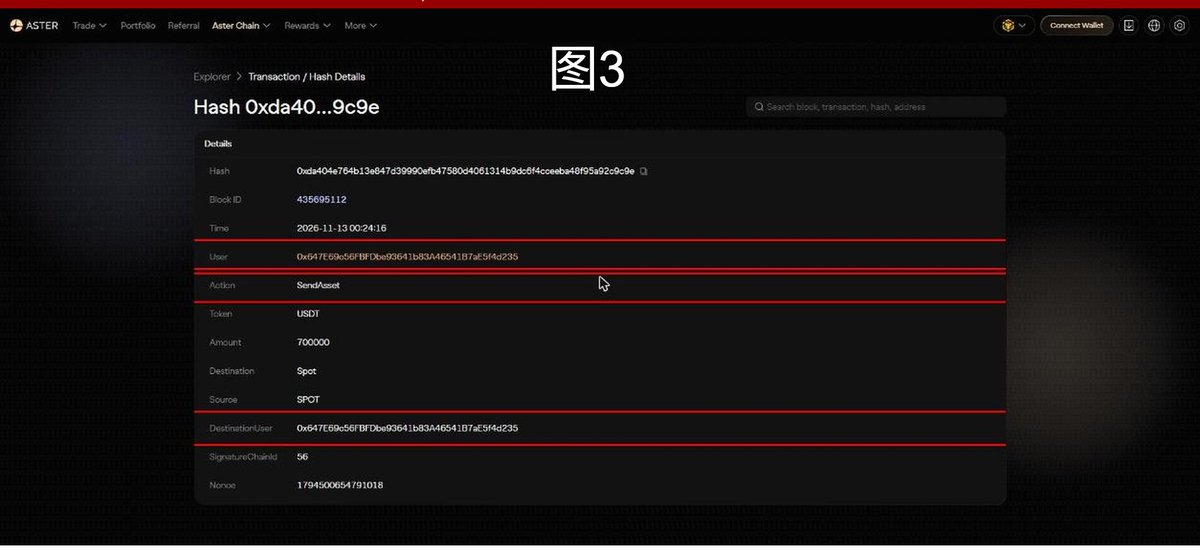
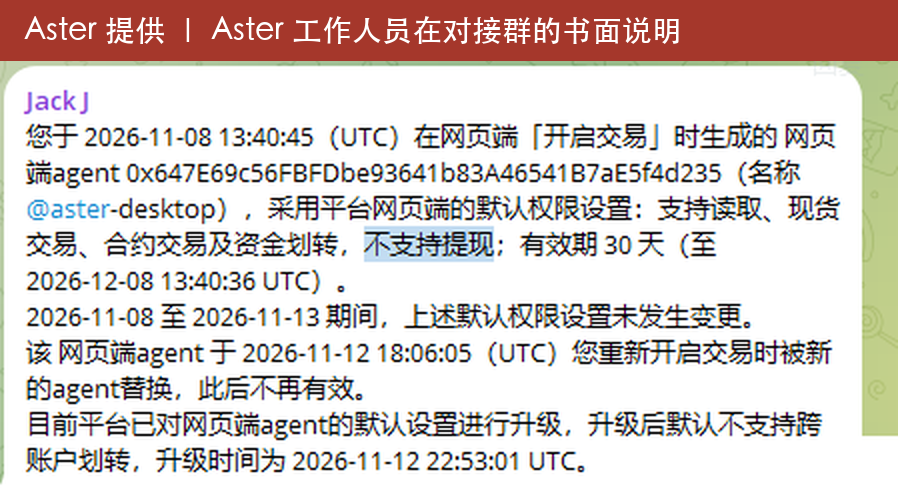
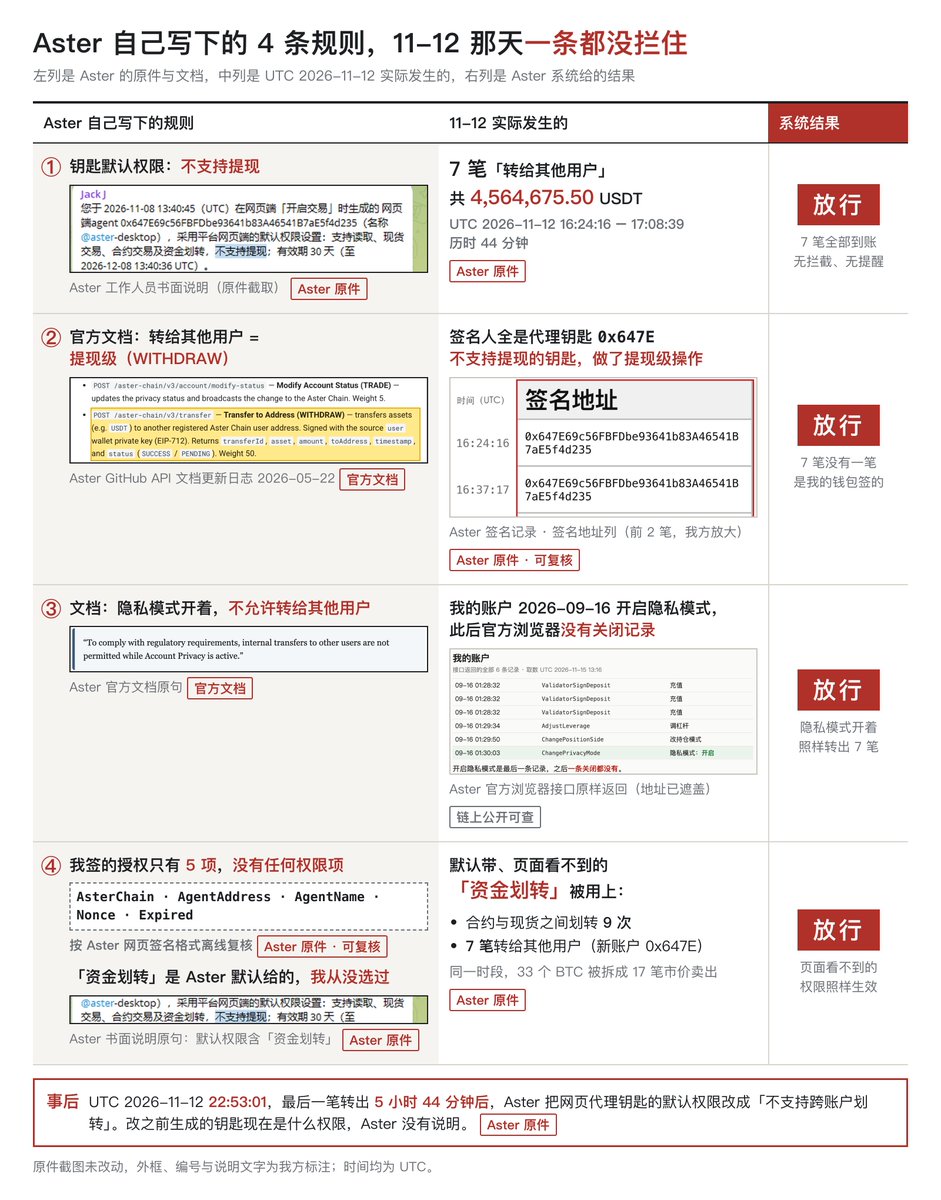
The records currently available show that the disputed transfers were signed by the web-generated agent key. However, this does not establish how the key was obtained or rule out a broader compromise. We are preserving the device and browser evidence and asking Aster to provide the original login, key-access, API, permission, signature, and risk-control logs. We will follow the evidence.