#WTS
Camera Action - Insta360 Ace Pro 2 (Dual-Battery) Fullset lengkap.
6juta aja, kalo ga nego bakal gw kasih semua aksesorisnya: tas, tambahan battery 2 biji lagi (total 4), charger battery yg bisa cas 3 battery sekaligus (KingMa), mount clamp buat mobil, dada, dll.
@sunnyirumekhai yg pasti data request, data request bagi mereka itu sangat beharga utk improve produk infrastruktur dan security mereka.
makanya mereka beraniin gratisin utk individu/company yg baru mulai nebeng di infra mereka.
kalo perusahaan lu kecil, Cloudflare nembokin infrastruktur lu secara gratis.
kalo perusahaan lu udh skala enterprise, harganya sangat2 worth it utk tembok perlindungan sekelas Cloudflare.
saya cinta Cloudflare, saya siap locked in sama Cloudflare ❤️
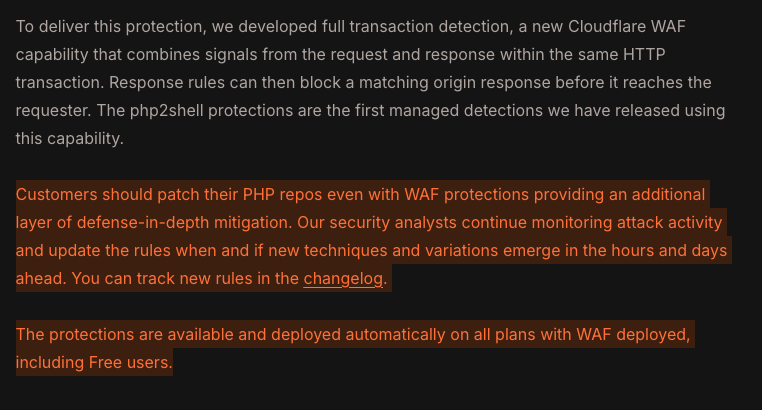
Cloudflare has deployed default web application firewall (WAF) protections for newly disclosed PHP vulnerabilities before public disclosure. The rules use request and response signals to stop exploit attempts and prevent exposed data from reaching attackers. https://t.co/OQG4x6x858
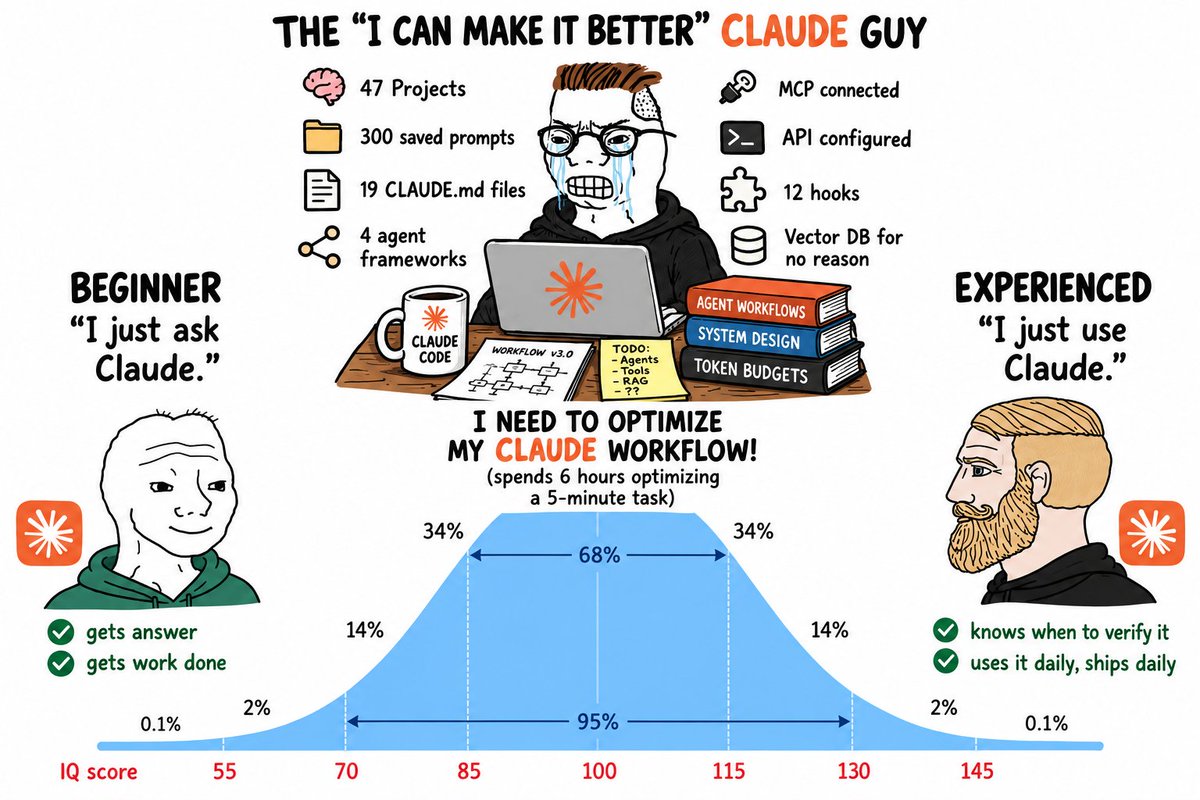
@ImBIOS_Dev yeah then money also doesnt care about your over-engineer agent workflow, mcp this mcp that, hook this hook that.
it's all about the result, right?
gw 0 MCP, 0 hooks, 0 plugins ala2.
most of the time cuma 5 skills, 2-5 kalimat AGENTS.md files, dan pake CLI.
sejauh ini maintain 350k LoC enak2 aja, malah justru tergolong disiplin.
gw ga ngerti sama orang byk bgt hook dan plugin di workflownya hahaha
@baddi44755 kalo webmu udah kamu daftarin ke Cloudflare (udah cloudflare proxy) bahkan harusnya udah aman even belum update patch phpnya.
tapi ya disaranin tetep diupdate.
@SofaValentinus iya, orang pake managed software/infra salah satu alasannya ini.
ga sempat update, ga ada waktu utk maintenance, atau skill issue buat ngurusin beginian.
kalo pake managed setidaknya udh ditembokin duluan, yg penting duitnya siap haha.
With all the recent vulnerabilities in PHP, Node.js, and other parts of the ecosystem
this is a good time to try Cloudflare’s Security Audit Skill
It uses multiple agents to find vulnerabilities, independently validate findings, and reduce false positives
One interesting detail… Cloudflare found that a single audit run discovered only about half the vulnerabilities found across multiple runs
A good reminder that running an AI security audit once doesn’t mean your code is secure
https://t.co/MMX4mfBlHd
Pahlawan terbesar recent krisis cybersecurity adalah Cloudflare. Cloudflare inisiatif deploy firewall buat melindungi services yang lamban / tidak ngeh dan belum update PHP. Cloudflare melaporkan JUTAAN percobaan serangan
Iya, Cloudflare yang mau diban Komdigi tolol.
ga perlu infra ribet, siapin homelab/vps.
- install harness kesayanganmu
- connect apps github, attlasian, etc
udah, mulai kerja dan tanya2 aja apa yg bisa diintegrasiin, gmn cara automate x, automate y. baca github issue, dll.
nanti ketemu insightnya dr AI nya itu sendiri.
@tengklengklewer ga ada, karena bener2 personalized dan tergantung project sih, paling kalo sempet gw buatin aja templatenya.
sbnrnya tinggal disesuain aja workflow contributing kamu gmn (tasknya kmn, pake cli apa, dll), testingnya (pake cli apa), trs design, build rules, dicatat semua di skills
@godofsleepy justru skills + cli mostly bisa untuk semua model dan harness, gampang migrasinya, karena basically ga attached ke spesific harness, ganti harness ya tinggal ganti.
kalo pake mcp, plugins gitu2 malah susah pas ganti harness, harus setup harnessnya lagi supaya connect ke mcpnya.
@fajaranz iya apalagi mcp itu sbnrnya bisa digantikan sama CLI + Skills, lebih hemat context.
soalnya MCP kebanyakan boros, tools langsung diload semua ke konteks.
@azamuddin91 haha yes mas, kalo MCP memang kondisional. tp aku prefer CLI dulu, kalo misal ga ada CLI nya yaudah terpaksa MCP.
tp most of time karena sebagian besar tool yg aku pake itu "ada" CLI nya, jadi makanya ga perlu MCP lagi.