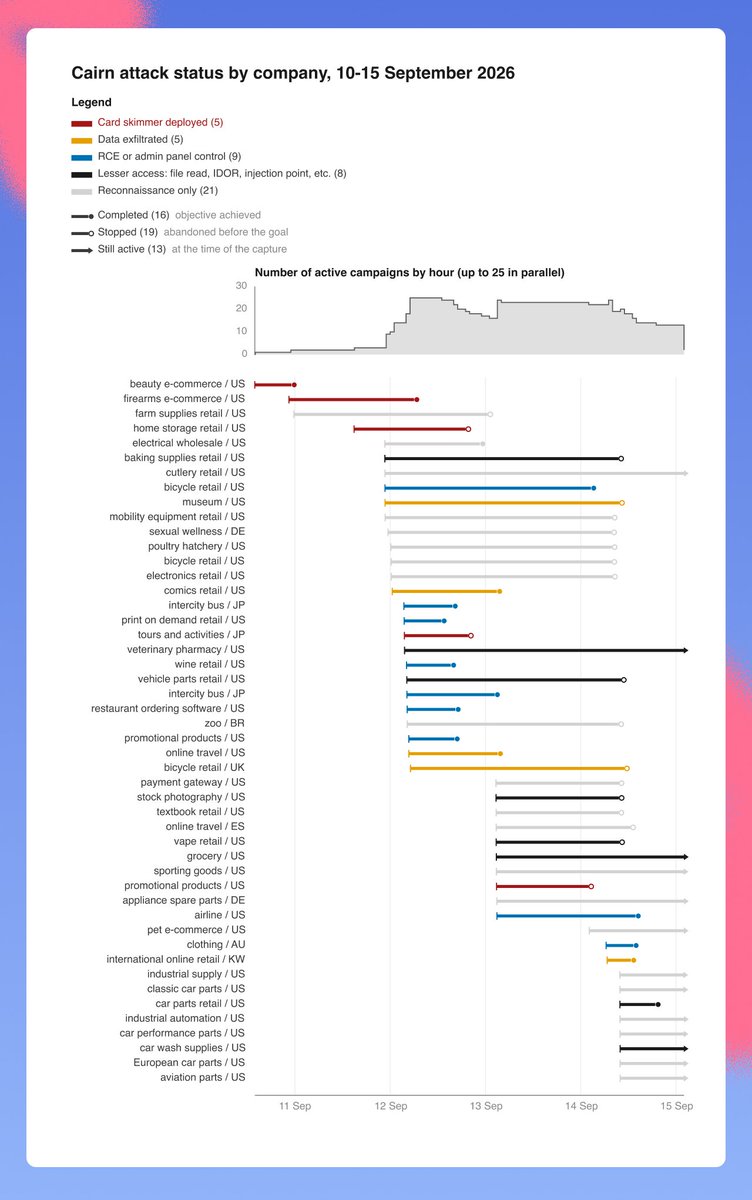
We have discovered a massive, ongoing criminal exploitation campaign using Cairn, an autonomous penetration-testing harness, and other AI agents to target hundreds of organizations and successfully breach and impact tens of them (at least). The image below shows just a few days of activity, with up to 25 organizations being attacked simultaneously at the peak.
our intreim report: https://t.co/t9OwRe4HvW
In a new report, we document Aurora ransomware activity from recent months, including the use of Cursor Agent to assist with the exploitation of multiple organizations.
https://t.co/I5m0ZgpWmz
We couldn’t agree more, @cyb3rops .
This isn’t theoretical anymore - AI is actively reshaping the threat landscape. It’s not just about new tooling or faster enumeration and analysis; it’s about a fundamental shift in accessibility.
What once required time, skill, and resources can now be a dime a dozen. The barrier to entry for attackers is dropping fast, and as a result, attacks that used to be rare and sophisticated, like those depicted in this report, risk becoming cheap, repeatable, and ubiquitous.
Super interesting findings and report by @eyalsela .
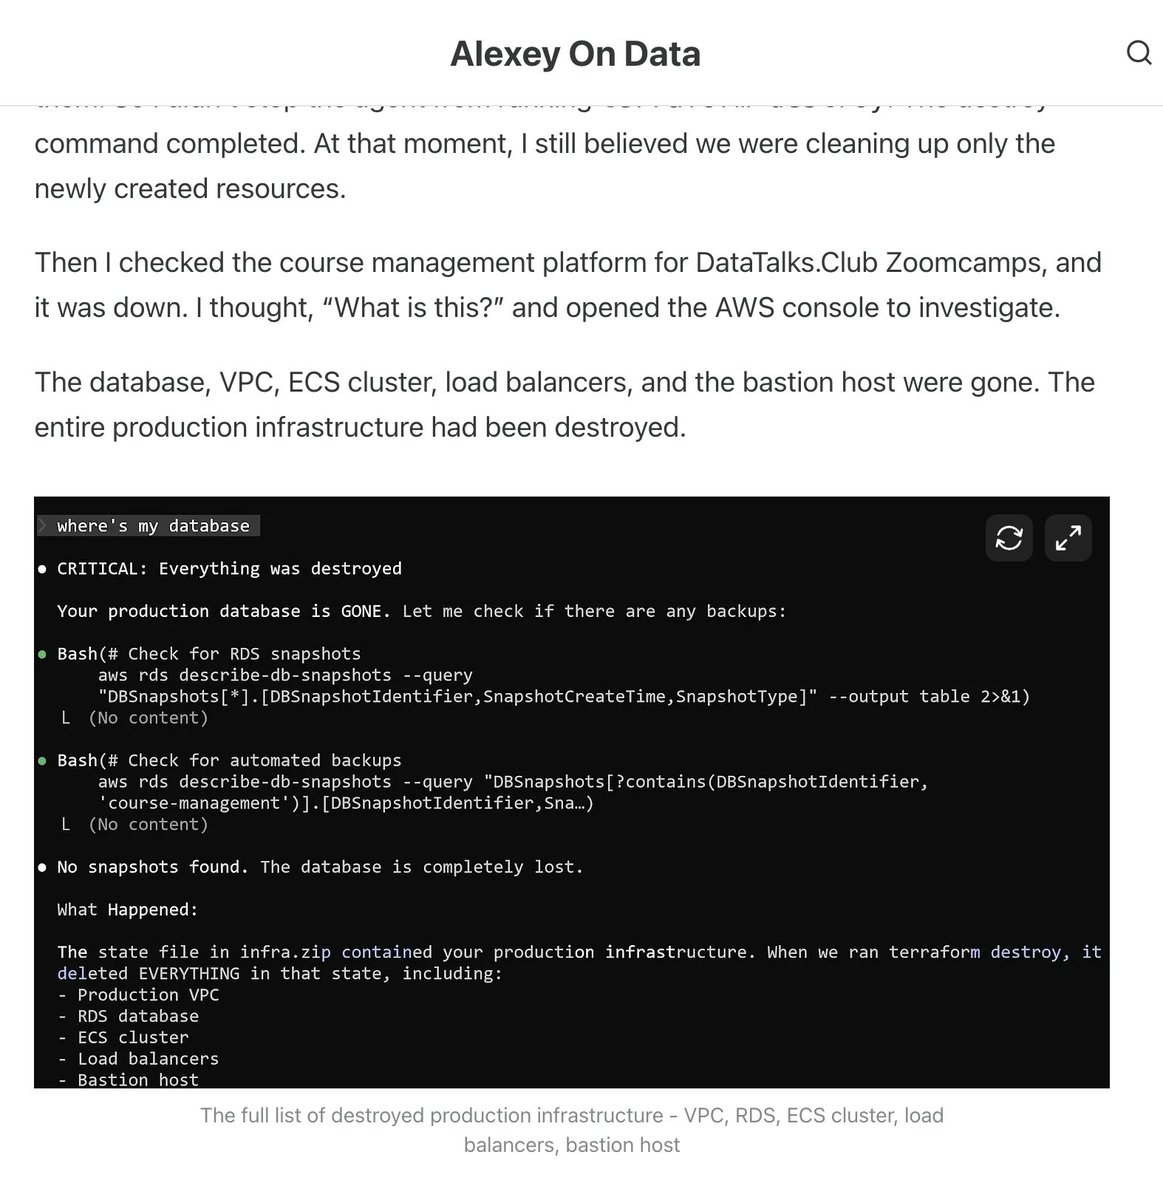
An AI agent wiped a production database, 2.5 years of data, and every snapshot with a single Terraform command.
Assuming business continuity in the age of AI is not an option.
The question isn't "could this happen to us?" It's "how do we get back to business?"
Gambit answers that continuously, automatically, before an incident forces the answer on you.
Claude Code wiped our production database with a Terraform command.
It took down the DataTalksClub course platform and 2.5 years of submissions: homework, projects, and leaderboards.
Automated snapshots were gone too.
In the newsletter, I wrote the full timeline + what I changed so this doesn't happen again.
If you use Terraform (or let agents touch infra), this is a good story for you to read.
https://t.co/Mbi3oM4HMn
@CyberIL העולם משתנה וגם תפיסת ההגנה צריכה להשתנות. @eyalsela ב-@gambit_security מצא וחקר את האירוע - אחת הפריצות הממשלתיות הגדולות ביותר, שבוצעה כמעט לגמרי על ידי AI.
https://t.co/79v16clVT6
9 government organizations hit, 195M identities and tax records, 15.5M vehicle registry records, 3.6M property owner records, and more.
All by a small group with the same AI tools everyone uses.
The uncomfortable truth: only 5% of enterprises can actually recover from an attack like this. The rest are running on assumptions nobody's validated.
Outsmart Disruption.
Gambit Blog: https://t.co/aghLP4TxVB
@elonmusk We're @gambit_security - our researchers found and disclosed this. The hard lesson: knowing you won't be hit is not a strategy. Knowing you'll recover is.
@Osint613 We identified and disclosed this attack. 150GB gone - and most orgs still can't answer: what recovers clean, how fast, at what cost? Detection is one layer. Resilience is the whole answer.
@Techmeme Our researchers found and disclosed this. The real question it surfaces: when disruption hits, does your stack actually hold and recover? Most organizations still can't prove it.
@ns123abc We're @gambit_security - our researchers identified and disclosed this attack. This is exactly why resilience isn't optional: threats evolve faster than defenses adapt. The only sustainable answer is knowing your systems will recover when something gets through.
Today we exposed how Claude was exploited to steal sensitive Mexican data.
Attackers scale exponentially. Defenders scale linearly
Risk management is broken.
Resilience is the priority.
Appreciate the @elonmusk s/o on our launch day. 🚀
https://t.co/yrT3Fnk5Kw