Here is the borehole water meter reading
1247m³. Monday morning, 8 days ago, we were at 1161m³.
That's a total of 86m³ consumed by our community, some kitchen gardens, hospitals, restaurants, finerals and schools. It's a lot of water!
We are almost at 1.25 million litres pumped!
Guess who is very happy?
After a long dry season, when it starts raining, you don't run home. You continue doing whatever you were doing otherwise you'll chase away rain.
I got rained for a good 30 mins. I am not even gonna change my clothes.
Sacrifices we make for the community!
Informe completo sobre el ataque del 19 de septiembre y una recompensa del 50% —hasta 3.3 BTC— sobre los fondos robados: https://t.co/z8ProW5fus
Términos de la recompensa: https://t.co/aF8d2L29Kv
El sábado 19 de septiembre un atacante usó una falla en nuestras herramientas administrativas para tomar el control de 35 cuentas de Blink y retirar unos 6.61 BTC de 24 de ellas. A las 11:39 UTC un cliente llamó a uno de nuestros ingenieros. Quince minutos después todo el servicio custodial estaba apagado. Esa misma noche la falla estaba cerrada y el servicio había vuelto. El jueves 24 de septiembre, cada cliente afectado tenía de vuelta su saldo exacto, en bitcoin y en dólares, pagado por los accionistas de Blink. Ningún cliente asume pérdida alguna.
La culpa fue nuestra. No de Bitcoin, no de nuestros usuarios. A los 22 clientes a quienes les robaron bitcoin, y a las 3,817 personas cuyos datos de cuenta fueron consultados: lo sentimos.
Cómo pasó:
Desde octubre de 2023 hasta ese sábado, cualquier persona con una cuenta gratuita de Blink y un navegador podía darse a sí misma los poderes de nuestro equipo de soporte: cambiar el correo o el teléfono de cualquier cuenta, iniciar sesión como ese cliente y subir sus límites. Tres errores comunes en cómo nuestras herramientas administrativas revisaban permisos, uno encima del otro, en código que heredamos.
Todo el equipo estaba ocupado migrando a decenas de miles de usuarios a la autocustodia bajo una nueva regulación. Un monitoreo pensado para detectar caídas del servicio no detectó a un administrador haciendo lo que ningún administrador debería hacer.
Lo que no tocó:
El dinero salió de nuestra billetera operativa. La mayoría de los fondos de los clientes está en almacenamiento en frío con firma múltiple, que nada en nuestras herramientas administrativas puede alcanzar. Las cuentas no custodiales nunca estuvieron en juego: no tenemos esas llaves.
Lo que vio el atacante:
También consultó datos de otras 3,817 cuentas; en algunos casos, un número de teléfono o un correo electrónico. No vio nombres, documentos de identidad, direcciones, contraseñas ni frases semilla. Escribimos a cada titular que pudimos contactar con el detalle exacto de lo que se vio.
Lo que lo frenó:
La autenticación de dos factores. El atacante inició sesión en nueve cuentas que la tenían activada e intentó dieciocho veces mover dinero. Cero pérdidas. Ninguna de las 24 cuentas vaciadas la tenía activada. Si haces una sola cosa después de leer esto: Configuración → Seguridad y privacidad → Autenticación de dos factores. Y actívala también en tu correo electrónico.
Lo que cambiamos:
La falla se cerró el mismo día y dos días después se agregó una tercera capa de protección. Las herramientas administrativas ya no están expuestas a internet. Las funciones que cambian el correo o el teléfono de un cliente están desactivadas para todos mientras las rediseñamos. Se revocaron todas las claves de API de los clientes.
La billetera operativa guarda ahora una fracción de lo que guardaba. Las correcciones de seguridad se desarrollan en privado y se publican una vez desplegadas; el código sigue siendo abierto. Ya funciona un canal permanente para reportar problemas de seguridad, con recompensas de hasta 0.1 BTC por hallazgos críticos.
Dónde está el dinero:
Una parte sigue donde se retiró. Unos 5 BTC pasaron por un servicio de intercambio entre cadenas; una cantidad pequeña llegó a un exchange que está colaborando. Hay denuncias penales presentadas en El Salvador y en Próspera, los reguladores están notificados y hemos rastreado los fondos sin interrupción. No esperamos recuperar el dinero.
Cont...
Full post-mortem of the September 19 attack, and a 50% bounty — up to 3.3 BTC — on the stolen funds:
https://t.co/8iRFY7Q13G
Bounty terms:
https://t.co/aF8d2L29Kv
On Saturday September 19 an attacker used a flaw in our admin tools to take over 35 Blink accounts and withdraw about 6.61 BTC from 24 of them. A customer called one of our engineers at 11:39 UTC. Fifteen minutes later the whole custodial service was off. By that evening the hole was closed and the service was back. By Thursday September 24 every affected customer had their exact balance back, in bitcoin and in dollars, paid for by Blink's shareholders. No customer bears any loss.
This was our fault. Not Bitcoin's, not our users'. To the 22 customers whose bitcoin was taken, and to the 3,817 people whose account details were looked up: we are sorry.
How it happened:
From October 2023 until that Saturday, anyone with a free Blink account and a web browser could give themselves the powers of our support staff: change the email or phone on any account, log in as that customer, raise their limits. Three unremarkable mistakes in how our admin tools checked permissions, stacked on top of each other, in code we inherited.
The whole team was busy moving tens of thousands of users to self-custody under new regulation. Monitoring built to catch outages didn't catch an administrator doing things no administrator should.
What it didn't touch:
The money came out of our hot wallet. Most customer funds sit in multi-signature cold storage that nothing in our admin tools can reach. Non-custodial accounts were never in play: we don't hold those keys.
What the attacker saw:
They also read the details of 3,817 other accounts, in some cases a phone number or email address. Not names, not IDs, not addresses, not passwords, not seed phrases. We wrote to every holder we could reach, saying exactly what was seen.
What stopped them:
Two-factor authentication. The attacker logged in to nine accounts that had it on and tried eighteen times to move money. Zero loss.
None of the 24 drained accounts had it on. If you take one thing from this post: Settings → Security and Privacy → Two-factor authentication. Then turn it on for your email too.
What we changed:
The flaw was fixed the same day and a third layer added two days later. The admin tools are off the public internet. The functions that change a customer's email or phone are switched off for everyone while we redesign them. All customer API keys were revoked.
The hot wallet now holds a fraction of what it did. Security fixes are developed privately and published once deployed; the code stays open source. A standing security reporting channel is live, with rewards of up to 0.1 BTC for critical findings.
Where the money is:
Some still sits where it was withdrawn to. About 5 BTC has gone through a cross-chain swap service; a small amount reached an exchange that is cooperating.
Criminal complaints are filed in El Salvador and Próspera, the regulators are notified, and we have traced the funds continuously. We are not expecting the money back.
So we are putting a 50% bounty on it.
Whoever provides the information that leads to a recovery gets 25% of what is recovered. Another 25% of anything recovered goes to Bitcoin Beach, Bitcoin Ekasi, Afribit Kibera and the circular economies they choose. No cap, no end date, paid only out of funds that actually come back. Write to [email protected].
We would far rather have spent this money on grassroots Bitcoin adoption than lost it to a thief. Shame on the attacker.
One more thing:
Ignore any email or SMS about this incident that contains a link: we contacted affected users only through messages in the Blink app. We will never ask for your PIN, password, seed phrase or a login code.
The full post-mortem has the timeline, the technical detail for anyone running code derived from ours, and the bounty terms (links at the top).
We still provide clean water to our community but closer to their homes.
The community fetches water on Mondays, Wednesdays and Fridays. We didn't have electricity throughout the day because of rationing from the drought. We do not have it today.
#JustStopToil
Get this. 🤣
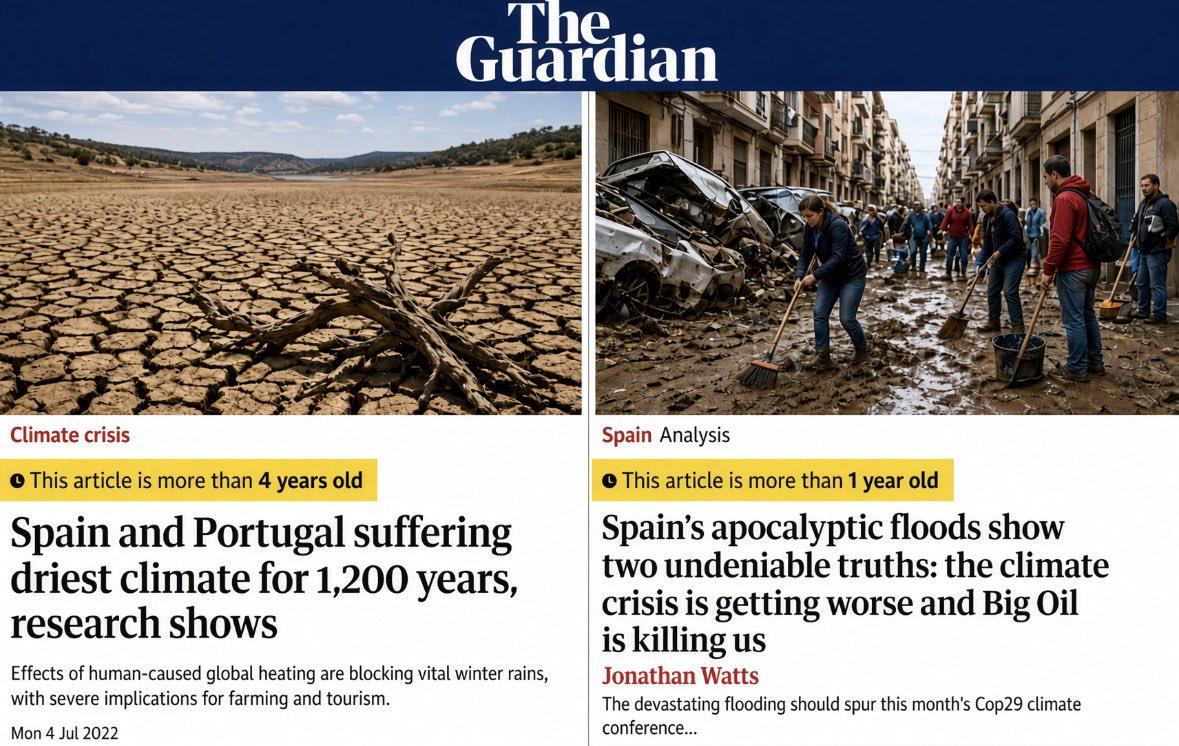
Four years ago, The Guardian claimed that Spain and Portugal are becoming too dry thanks to anthropogenic climate change.
However, after the devastating floods in fall 2024, The Guardian said that Spain is becoming too wet because of climate change.
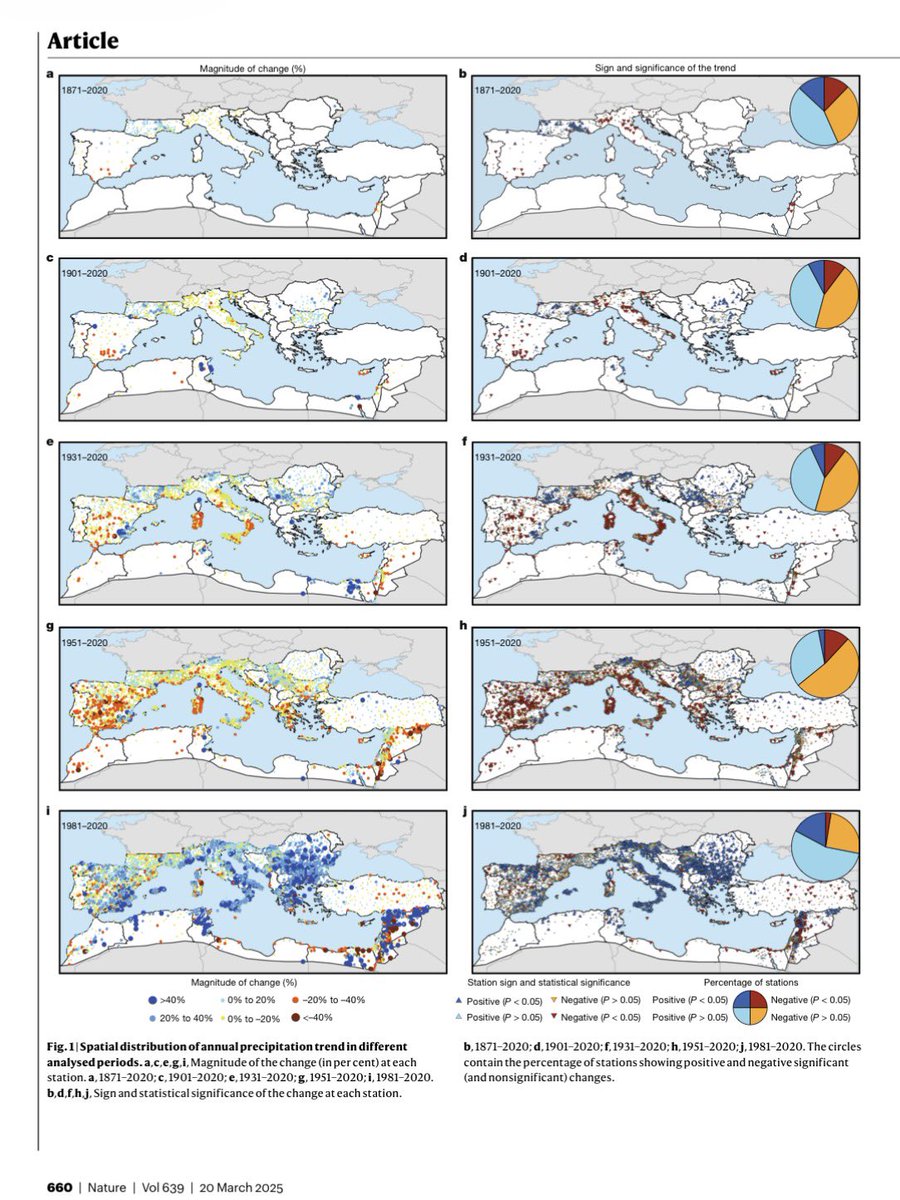
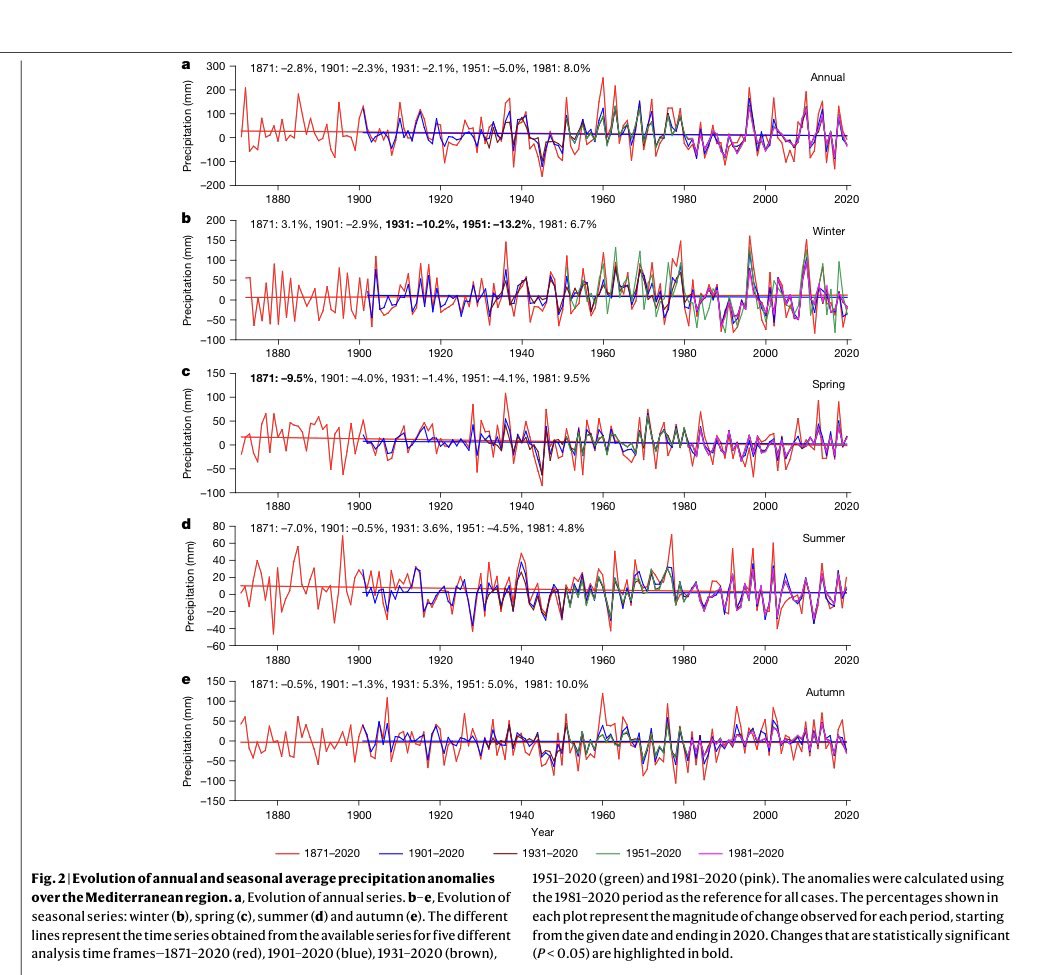
The observational data, however, tell a different story. A recent study published in Nature in March 2025 analyzed long-term rainfall data in the Mediterranean and found that no statistically significant long-term trends exist in the whole.
🗨️ “𝐻𝑒𝑟𝑒 𝑤𝑒 𝑠ℎ𝑜𝑤 ����ℎ𝑎𝑡 𝑀𝑒𝑑𝑖𝑡𝑒𝑟𝑟𝑎𝑛𝑒𝑎𝑛 𝑝𝑟𝑒𝑐𝑖𝑝𝑖𝑡𝑎𝑡𝑖𝑜𝑛 ℎ𝑎𝑠 𝑙𝑎𝑟𝑔𝑒𝑙𝑦 𝑟𝑒𝑚𝑎𝑖𝑛𝑒𝑑 𝑠𝑡𝑎𝑡𝑖𝑜𝑛𝑎𝑟𝑦 𝑓𝑟𝑜𝑚 1871 𝑡𝑜 2020, 𝑎𝑙𝑏𝑒𝑖𝑡 𝑤𝑖𝑡ℎ 𝑠𝑖𝑔𝑛𝑖𝑓𝑖𝑐𝑎𝑛𝑡 𝑚𝑢𝑙𝑡𝑖-𝑑𝑒𝑐𝑎𝑑𝑎𝑙 𝑎𝑛𝑑 𝑖𝑛𝑡𝑒𝑟𝑎𝑛𝑛𝑢𝑎𝑙 𝑣𝑎𝑟𝑖𝑎𝑏𝑖𝑙𝑖𝑡𝑦… 𝑊ℎ𝑖𝑙𝑒 𝑡𝑟𝑒𝑛𝑑𝑠 𝑐𝑎𝑛 𝑏𝑒 𝑖𝑑𝑒𝑛𝑡𝑖𝑓𝑖𝑒𝑑 𝑓𝑜𝑟 𝑠𝑜𝑚𝑒 𝑝𝑒𝑟𝑖𝑜𝑑𝑠 𝑎𝑛𝑑 𝑠𝑢𝑏𝑟𝑒𝑔𝑖𝑜𝑛𝑠, 𝑜𝑢𝑟 𝑓𝑖𝑛𝑑𝑖𝑛𝑔𝑠 𝑎𝑡𝑡𝑟𝑖𝑏𝑢𝑡𝑒 𝑡ℎ𝑒𝑠𝑒 𝑡𝑟𝑒𝑛𝑑𝑠 𝑝𝑟𝑖𝑚𝑎𝑟𝑖𝑙𝑦 𝑡𝑜 𝑎𝑡𝑚𝑜𝑠𝑝ℎ𝑒𝑟𝑖𝑐 𝑑𝑦𝑛𝑎𝑚𝑖𝑐𝑠, 𝑤ℎ𝑖𝑐ℎ 𝑤𝑜𝑢𝑙𝑑 𝑏𝑒 𝑚𝑜𝑠𝑡𝑙𝑦 𝑙𝑖𝑛𝑘𝑒𝑑 𝑡𝑜 𝑖𝑛𝑡𝑒𝑟𝑛𝑎𝑙 𝑣𝑎𝑟𝑖𝑎𝑏𝑖𝑙𝑖𝑡𝑦.”
🔗 https://t.co/yvnXcLz0qy
Interestingly, in Spain, there has been little trend in rainfall since 1871. However, if the analysis starts in 1951, there is a significant decrease (p <0.05), while starting in 1981 yields a statistically significant increase (p <0.05).
This just goes to show that people (like the writers at The Guardian) can manipulate data to get a desired trend to suit a specific narrative.
25 cubic meter of water or 25000 litres or 6600 gallons of water pumped from our borehole in a 24 hour duration. Our community is thirsty. Yesterday we had our taps running from 12 midday to 9 in the evening.
Tea is drying. Maizeand finger millet look terrible without rain.
I would never take this dude serious. Alarmism is what pays their bills and some fame. In my home right now, temperatures range from 14C at night to 30+C during the day. That's a difference of 15C and yet, we don't even realize it.
There is no climate crisis or emergency.
BBC again just reported “a warming atmosphere caused by human activity, including the burning of fossil fuels like coal, oil and gas.” They don’t offer prove - they can’t since it’s a total lie. Nature runs our climate. Idiots run our media
Tomatoes aren’t just found in stores. They’re planted, watered by hand, grown through drought, harvested, and sold for sats. Working for Bitcoin, not waiting for Bitcoin. HOPE looks like this.
Two months without rain.
We watched the sky and kept working anyway.
We watered by hand. We lost some. We saved most.
Today, we harvested our first tomatoes. 🍅
And I want you to understand what that really means.
It means a mother in our community can now sell these tomatoes for sats. It means her children eat tonight. It means she saves a little in Bitcoin for a future that does not vanish with inflation.
From soil to sats. From toil to hope. Together.
This is what a self-reliant Bitcoin community looks like. Not a chart. A farm. A harvest. A family.
We are not asking for pity. We are asking for partners.
Help us scale. Help us plant more. Help us reach more families who just need a chance to earn in money that respects their work.
And if you ever want to see it for yourself come. Walk the farm with us. Harvest with us. Stay in our cabins. Spend your sats in our shops. Let the soil tell you the story better than I ever could.
Every sat grows something real.
Support our campaign on geyser : https://t.co/iBHCmiK0zz
#Bitcoinkwawote
Everywhere is dry. We are not used to Yemen-like conditions- dust, hot sun, dying crops, poor to zero germination, etc.
This year has just been different.
We are in a CO2 famine. More CO2 is good for life on earth and at 420 ppm of CO2, plants are starving. That die at 150ppm and thrive at 1000-1200 ppm.
CO2 is not a temperature control knob.
I love CO2, you should too.
#SPEDN
Zap merchant: [email protected]
BTCMap location : https://t.co/xWeAYqmFy1
Bitcoin is money and we use it as so in our community.
We are building a self reliant Bitcoin circular economy so that's it's easier to earn, save and spend in Bitcoin in our community.
Jusper( our incoming MCA) recently paid for nails to go and help construct a needy person a toilet and paid for them with Bitcoin. And documented for you to see.
How amazing is that? This are the kind of leaders we need.
To support our campaign: https://t.co/iBHCmiK0zz
#Bitcoinkwawote
We've paused Blink services while we investigate a security incident.
An attacker accessed a limited number of custodial accounts and withdrew funds.
The large majority of funds are secure.
Non-custodial wallets are not affected.
This is getting pretty insane,
look at this,
You pay a plumber $100.
After tax, the plumber keeps $70.
The plumber pays a house cleaner $70.
After tax, the cleaner keeps $49.
The cleaner pays a delivery driver $49.
After tax, the driver keeps about $34.
The driver pays a mechanic $34.
After tax, the mechanic keeps about $24.
The mechanic pays a server $24.
After tax, the server keeps about $17.
Keep repeating the process.
Each time the money moves, more gets taxed until the gov has collected nearly the whole original $100.
oh and now introduce money printing / inflation...
we are getting close to another tea party if you ask me